

HimitsuShell
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
anti-botbinary-analysiscryptography+6
70
himitsushell/himitsushellshell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
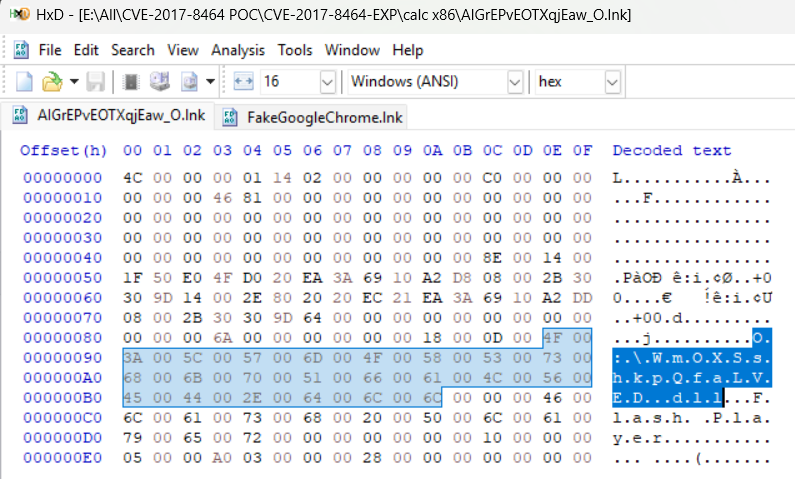 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 nodiuus/nocturne
A bin2bin code virtualizer for x86-64 PE's
 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 sizeable-bingus/massdriver
Proxies sensitive API calls from shellcode to artifacts for CET-compatible clean call stacks, enabling stealthy payload execution and call stack…
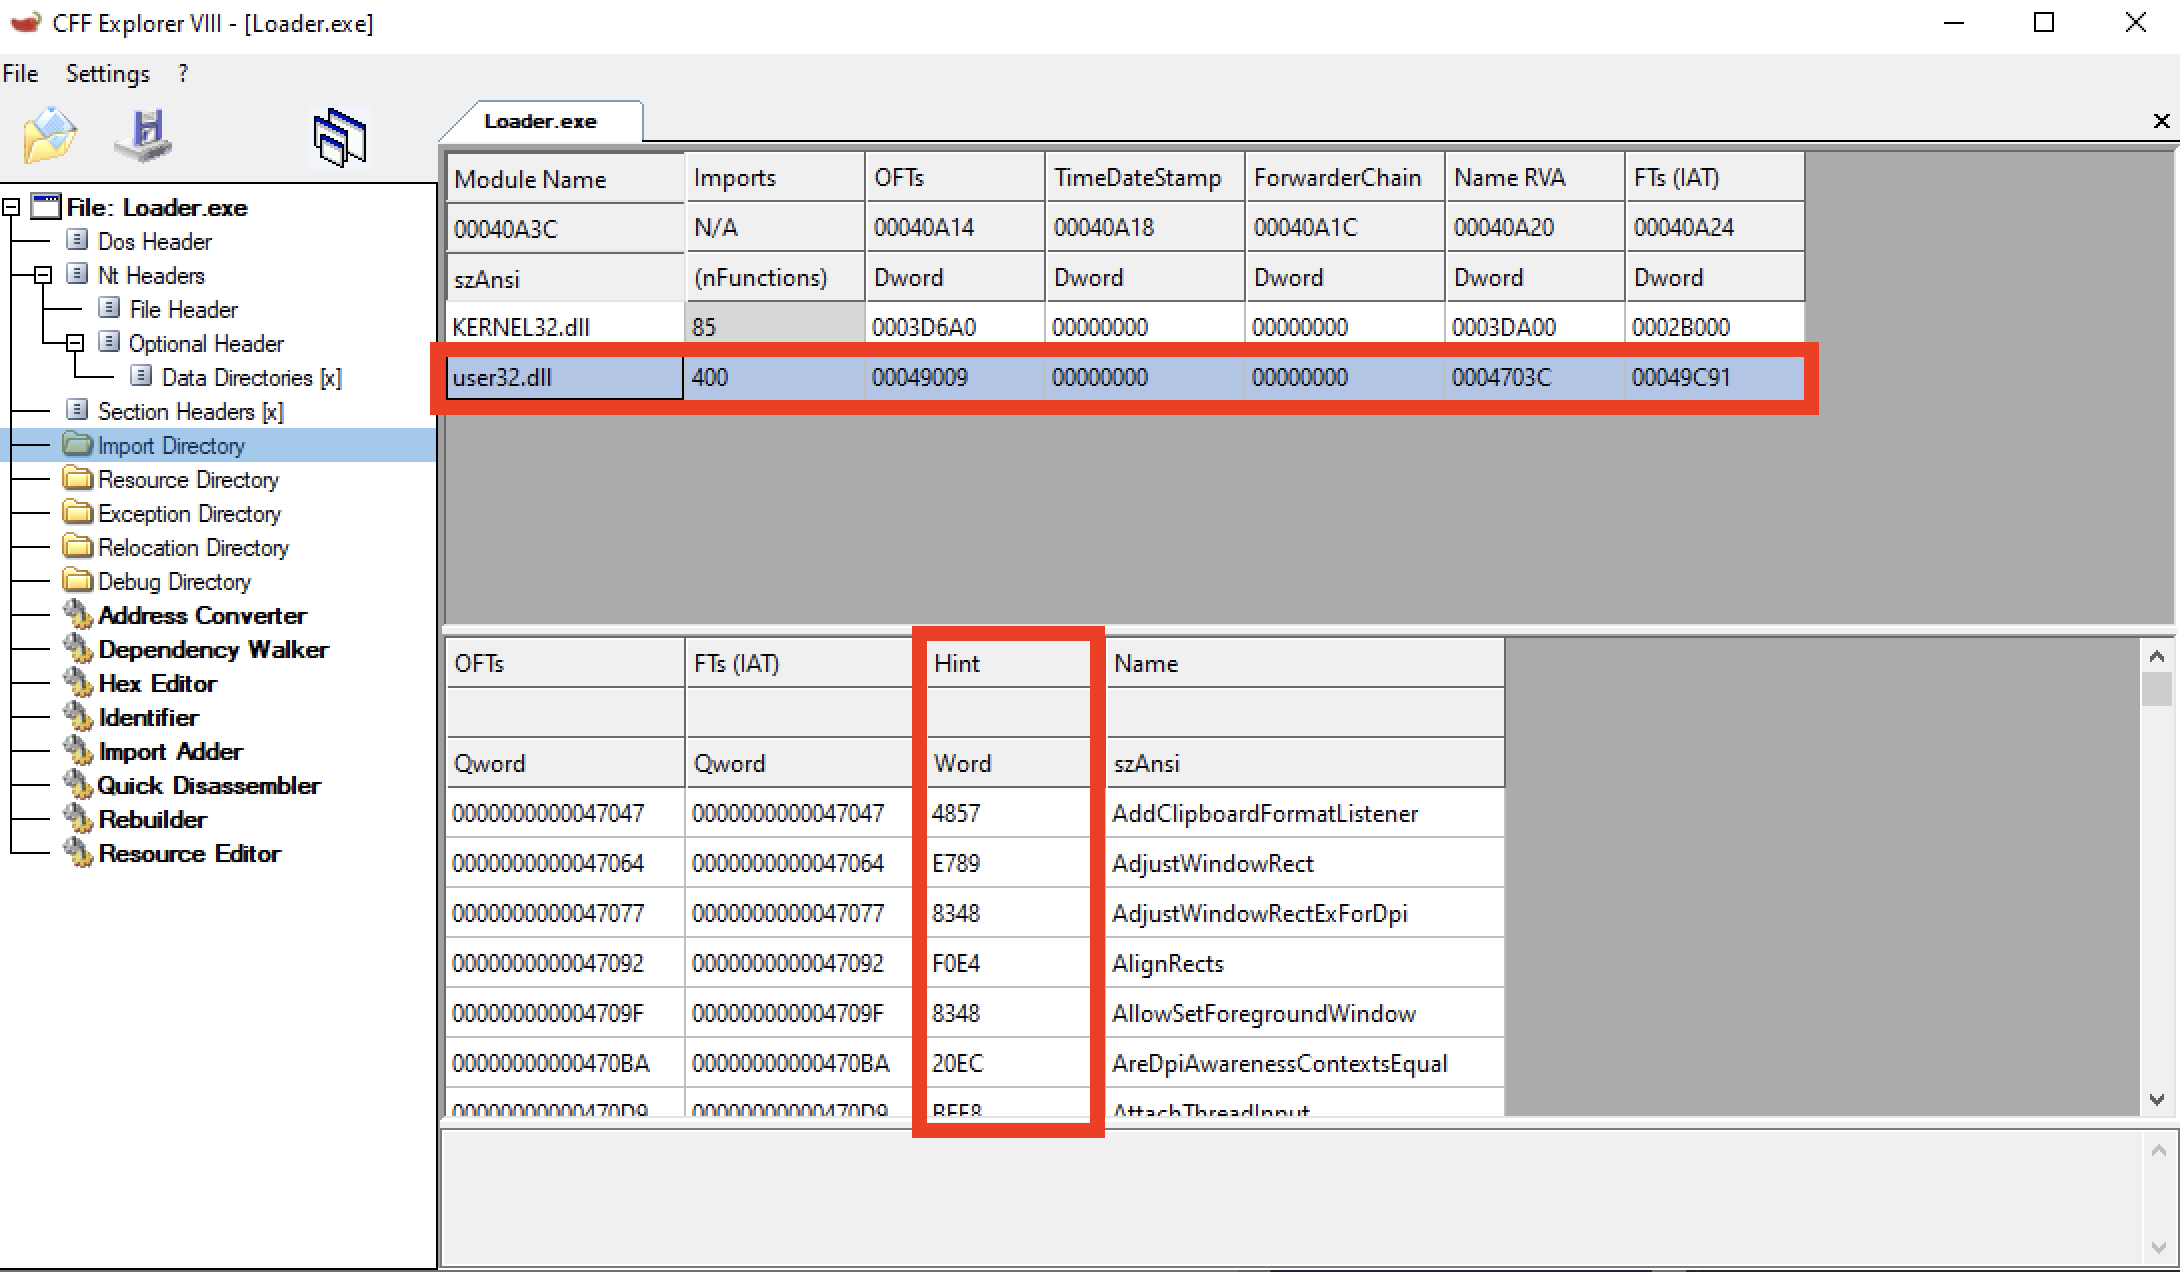 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 iss4cf0ng/dotnetpeloader
A C# PE loader for x64 and x86 PE files.
 hackinglz/cve-2025-27237
CVE 2025 27237 Zabbix LPE proof of concept.
 lepotekil/msfmania
Python AV Evasion Tools
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
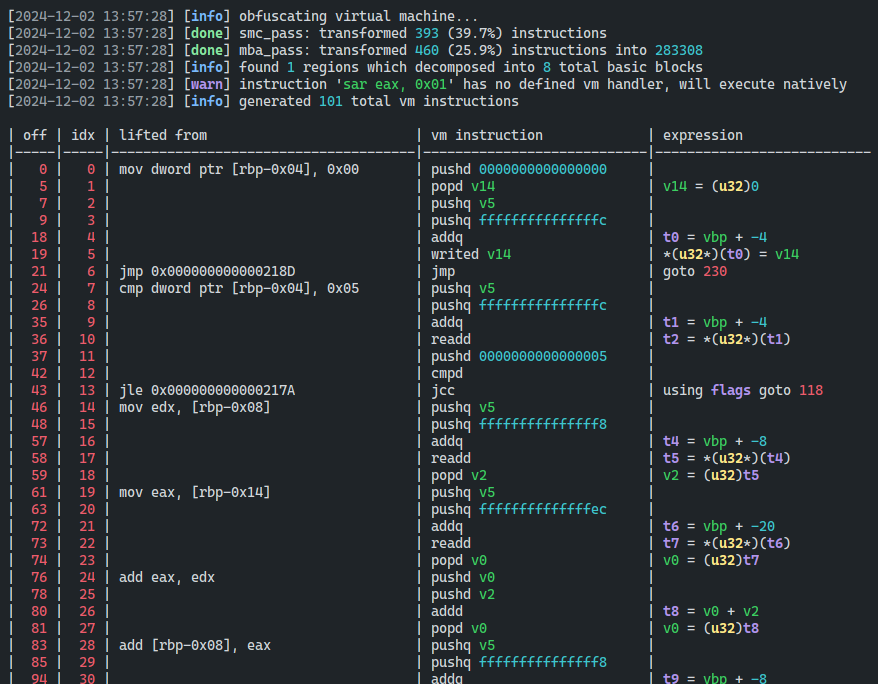 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 gmh5225/awesome-mba
List of mixed boolean-arithmetic resources
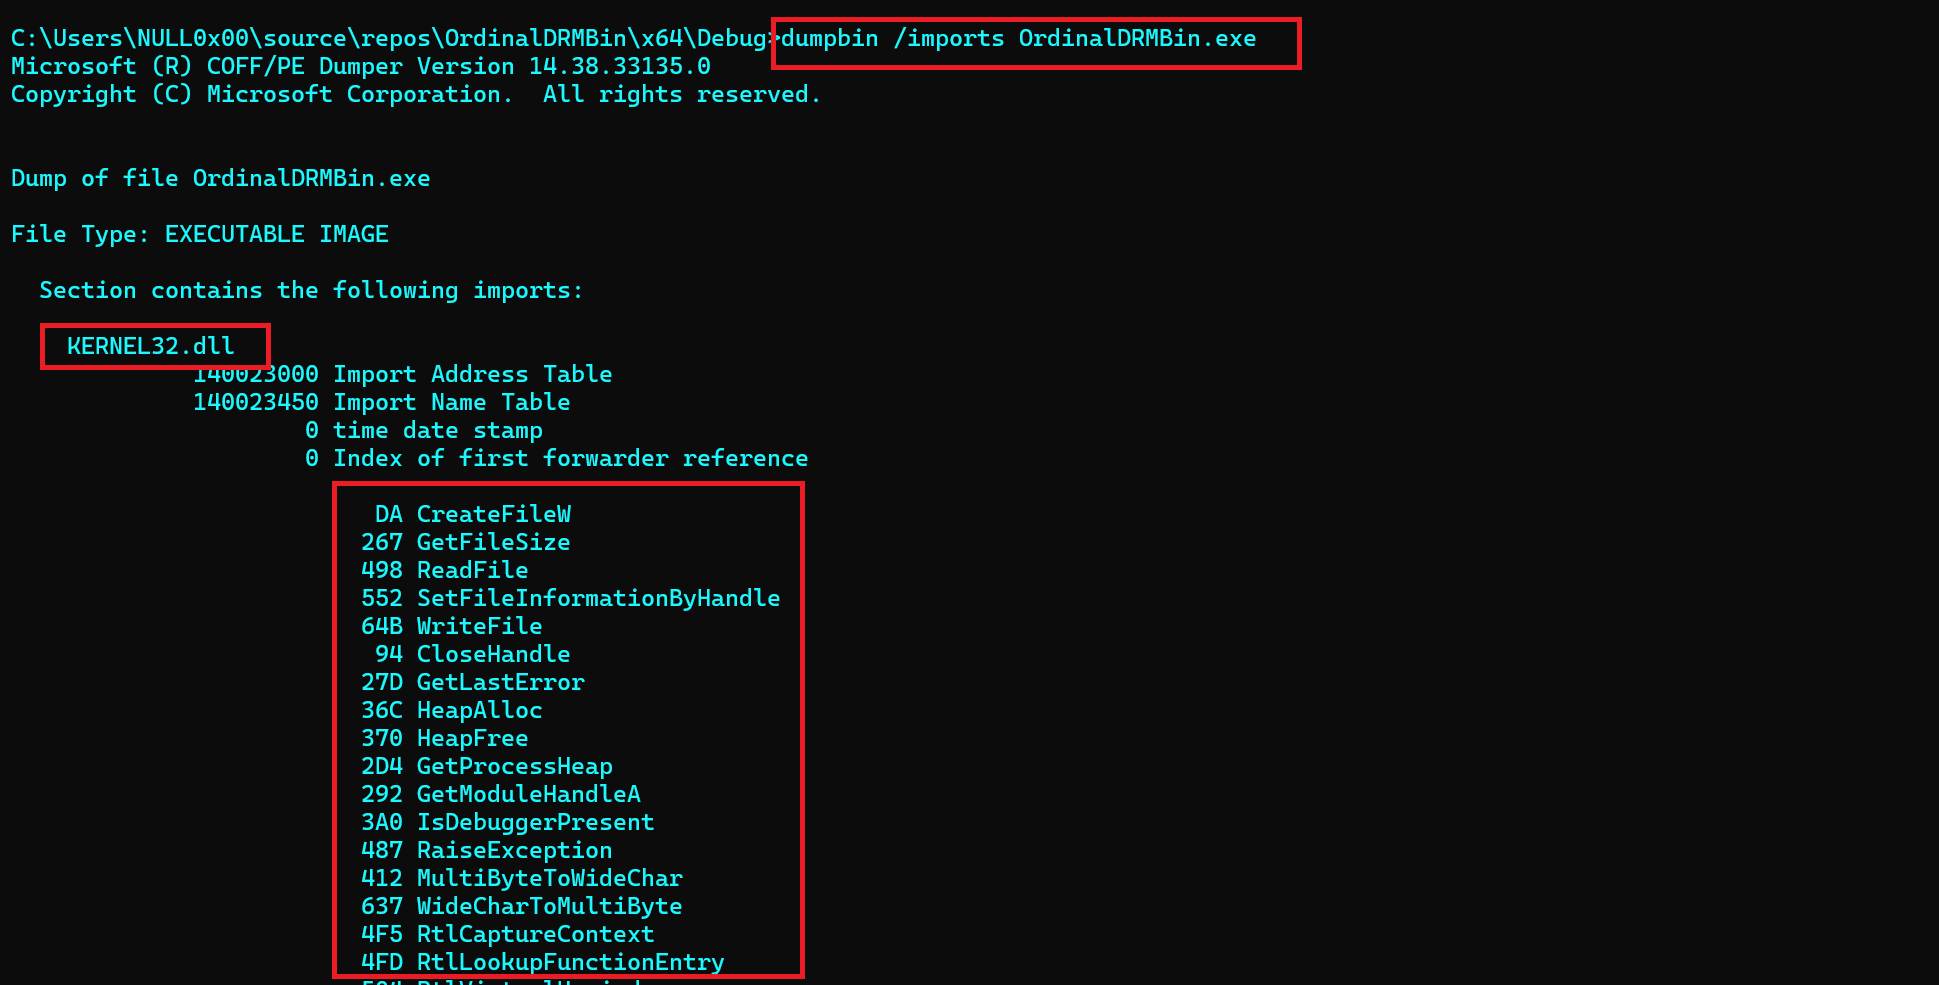 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware