
Crassus
 vu-ls/crassus
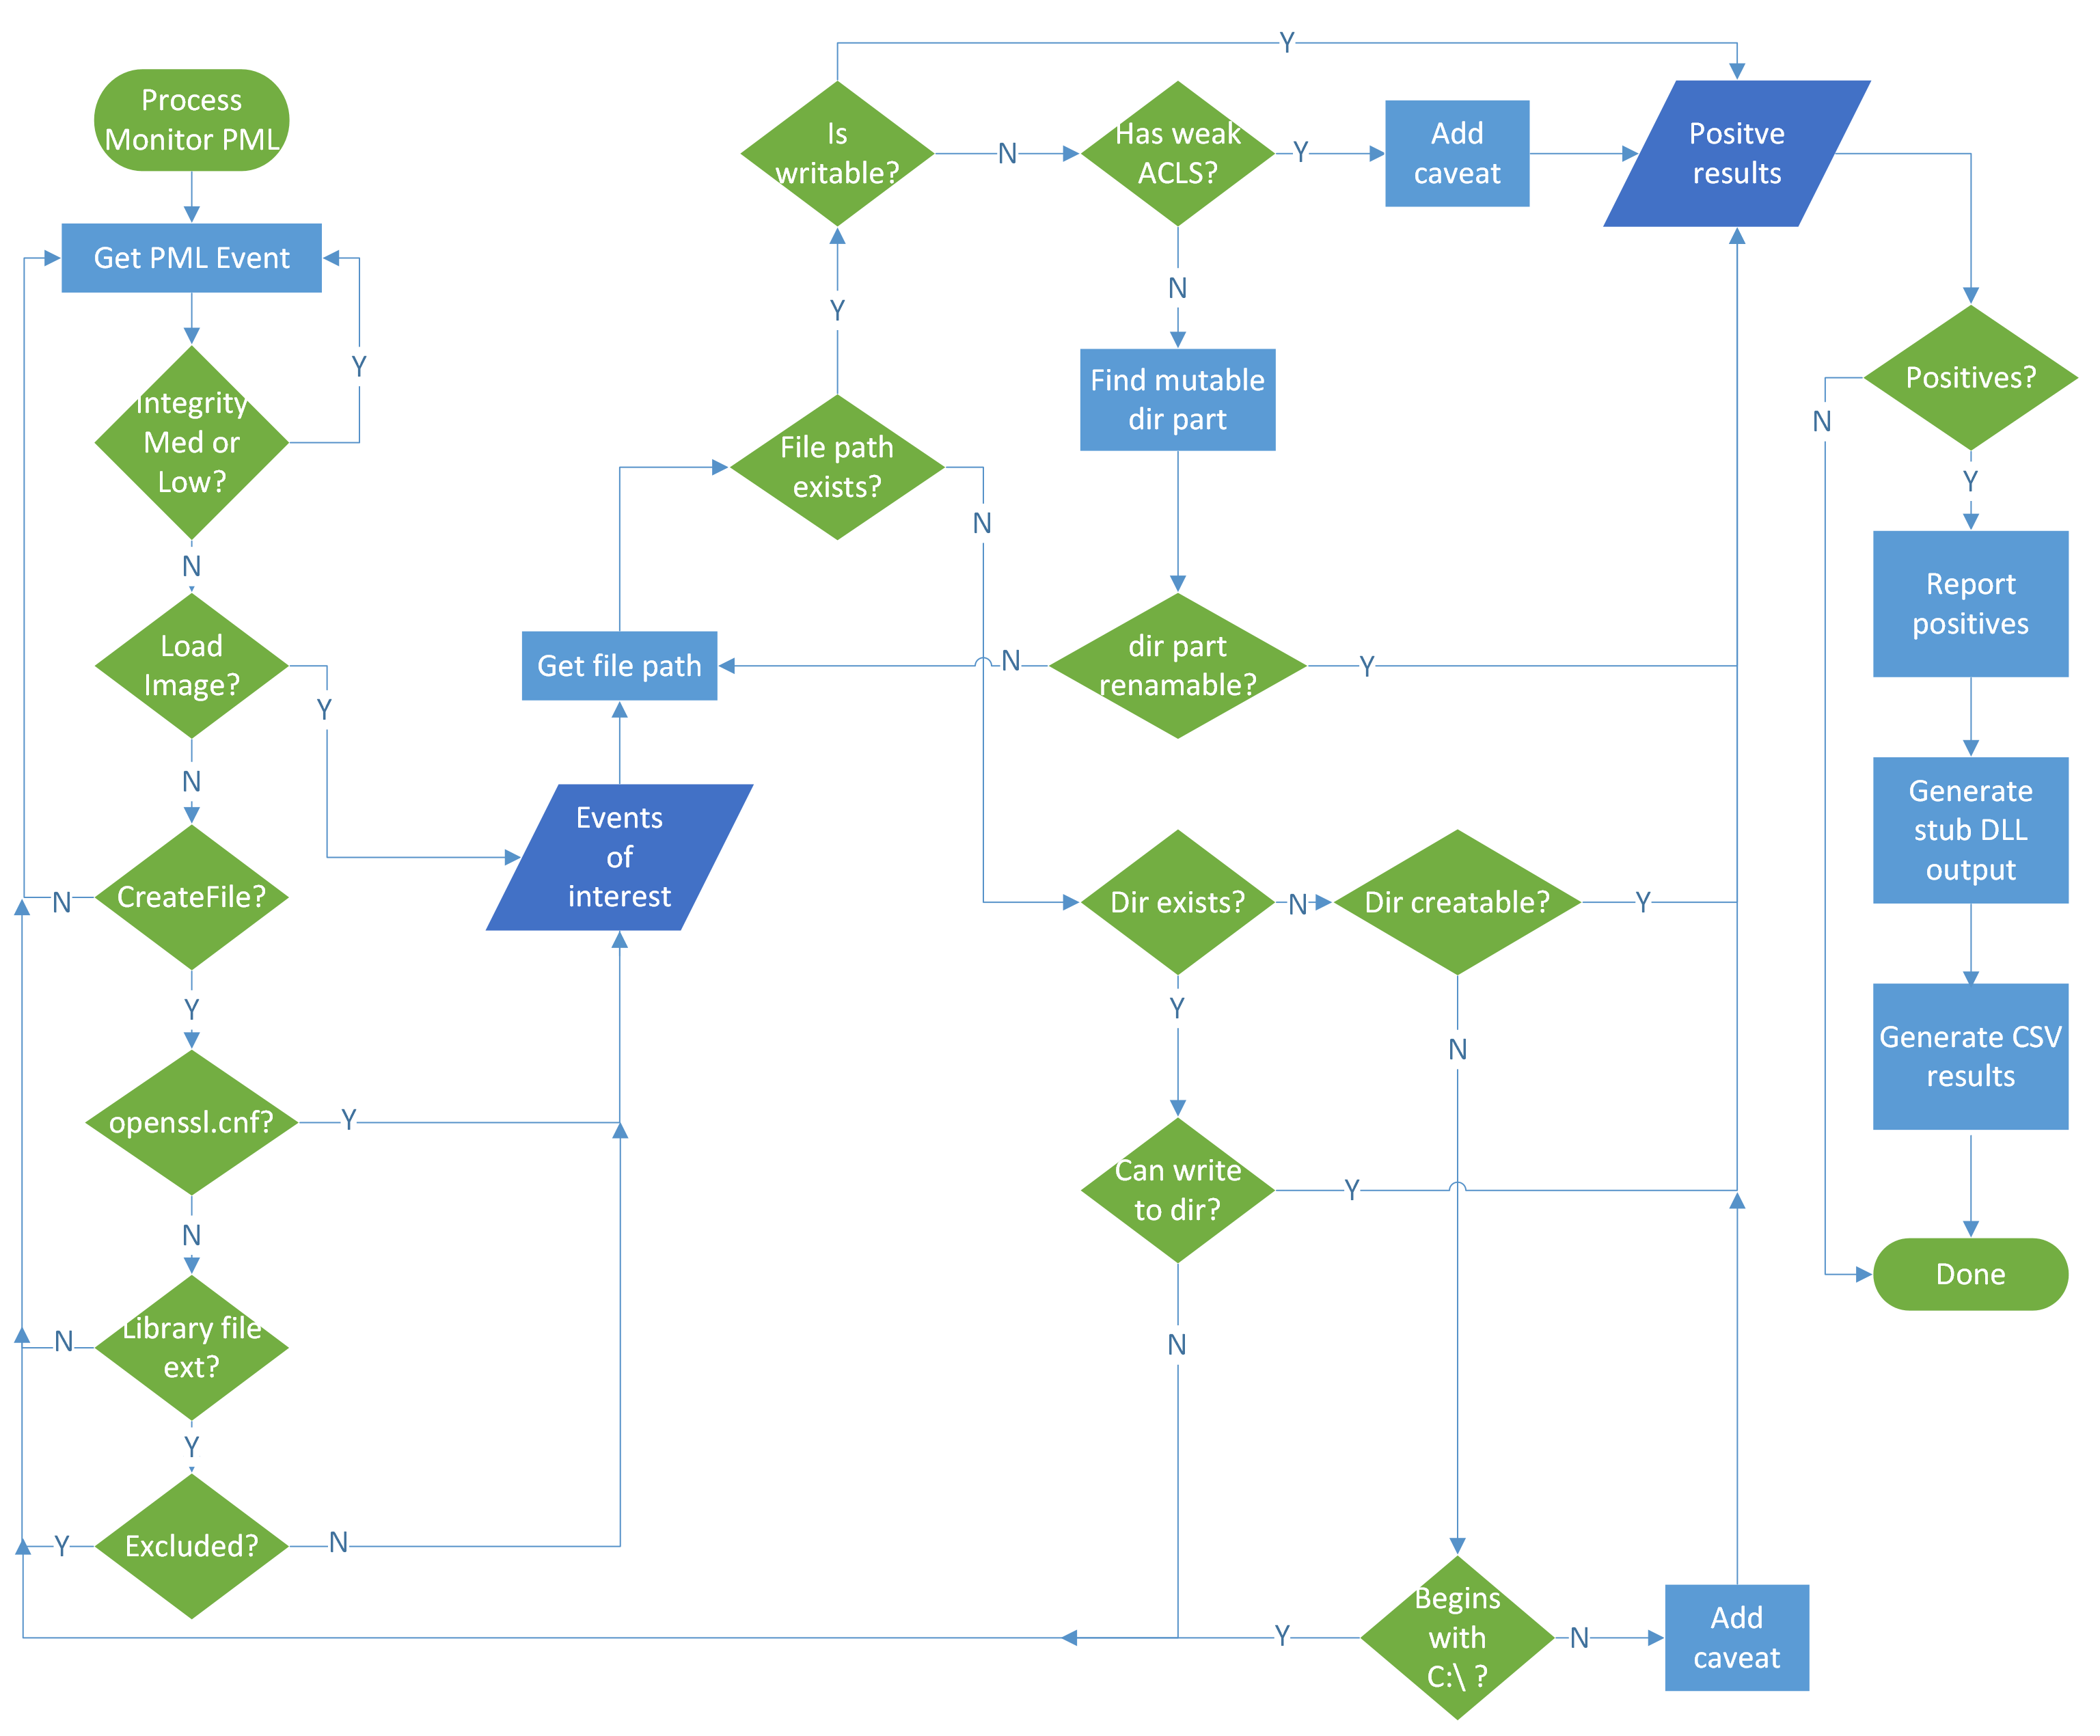
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
631
vu-ls/crassusWindows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 lab52io/leakedhandlesfinder
Leaked Windows processes handles identification tool
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…