
windiff
 ergrelet/windiff
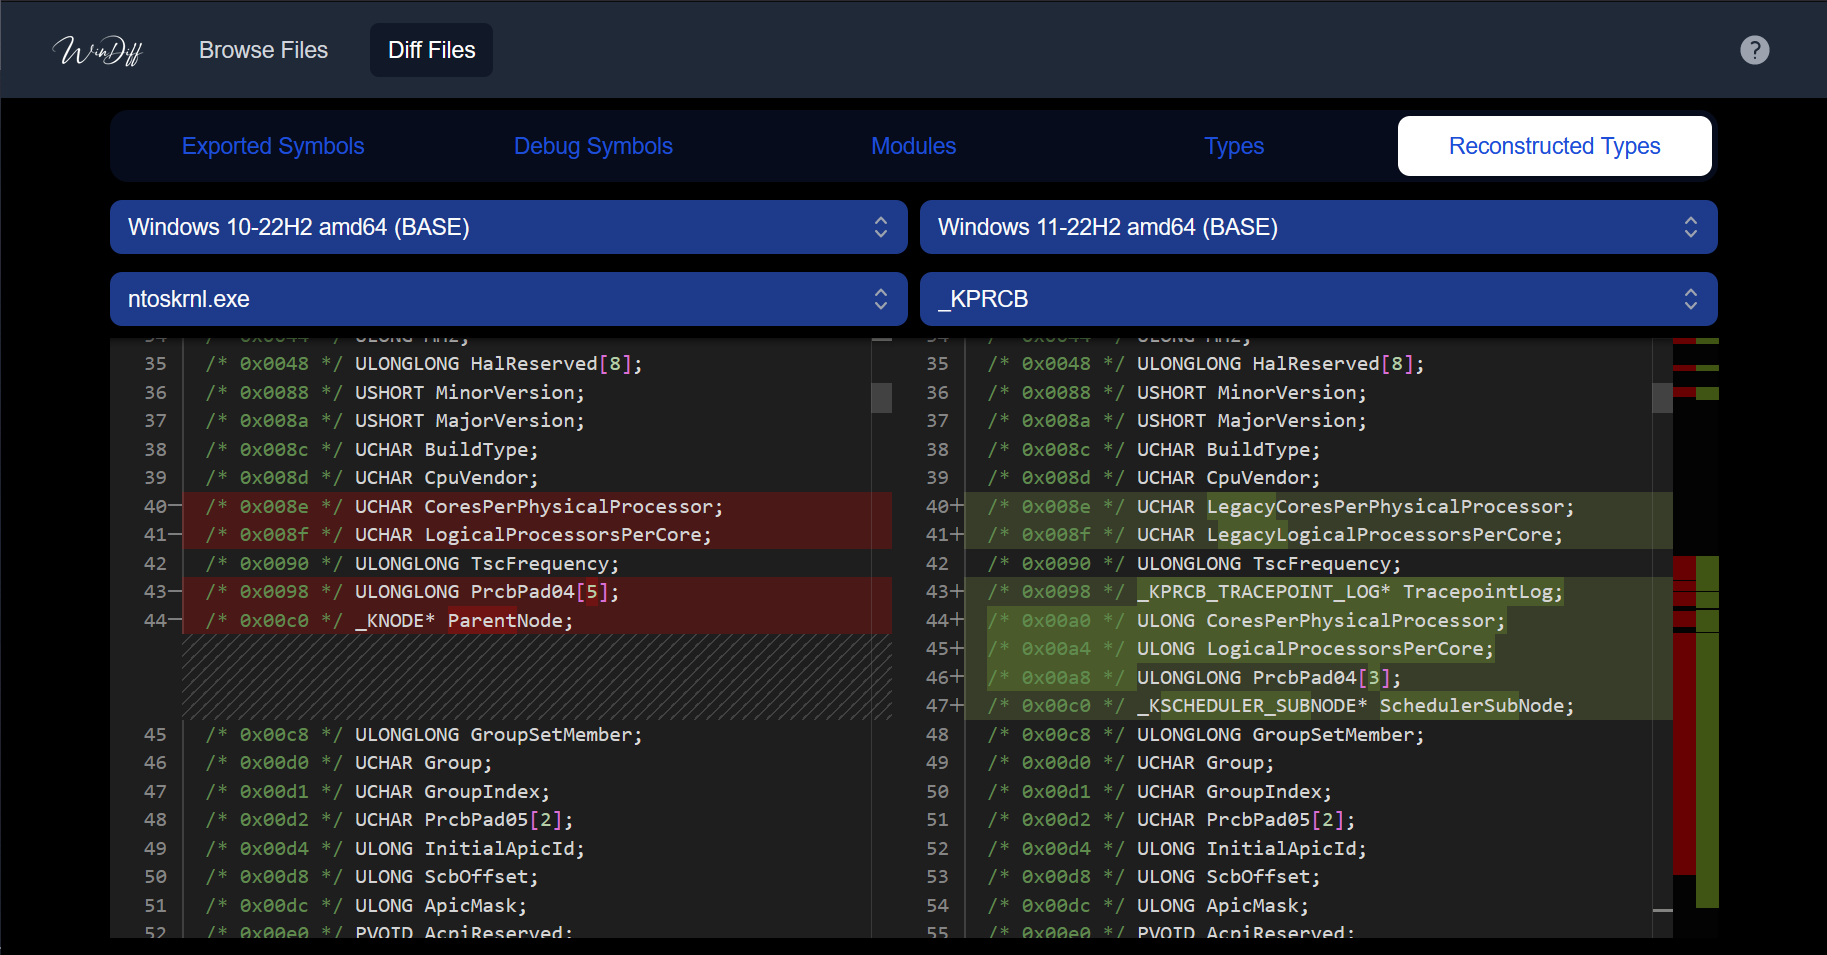
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
390
ergrelet/windiffTool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…