

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 ridhinva/linux-kernel-algif-aead-checker
Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
 jihwan77/linux-kernel-copy-fail-cve-2026-31431-
Analysis and mitigation of Linux kernel Copy Fail (CVE-2026-31431) vulnerability exploiting AF_ALG/splice page cache mutation, with PoC checker,…
 onhexgroup/tabpe
A monthly Windows PE baseline dataset for Cyber security researchers
 abdelkabirouadoukou/cve-2026-31431-analysis-and-fix
In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…
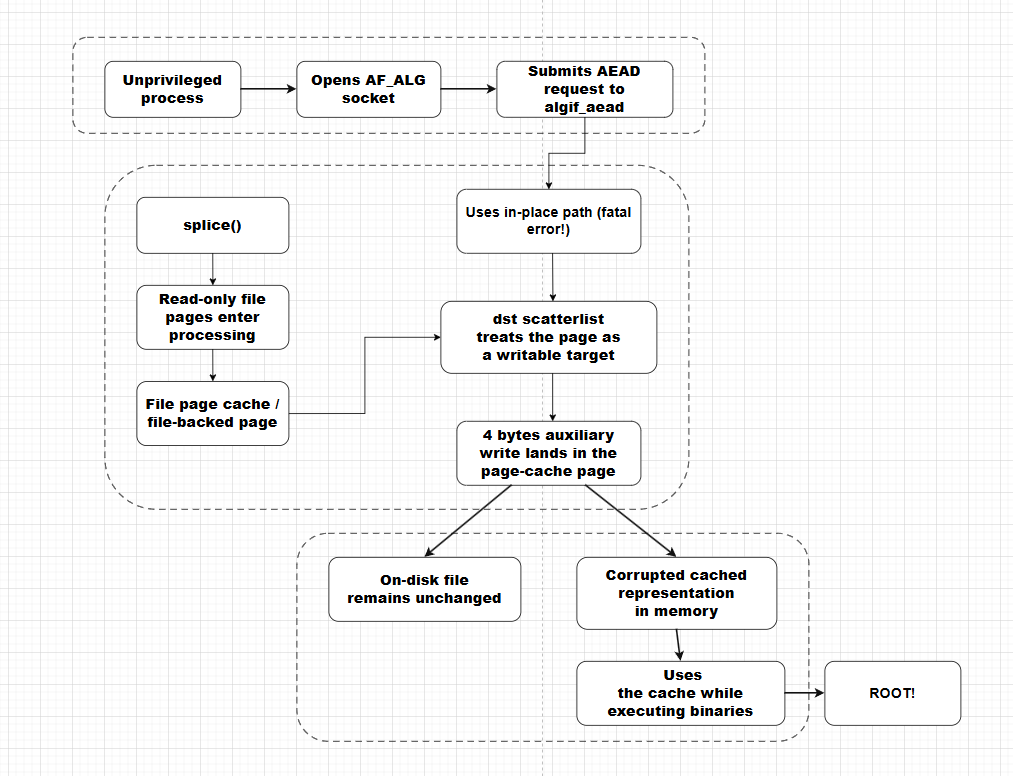 chernstepanov/copyfail-for-dummies
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
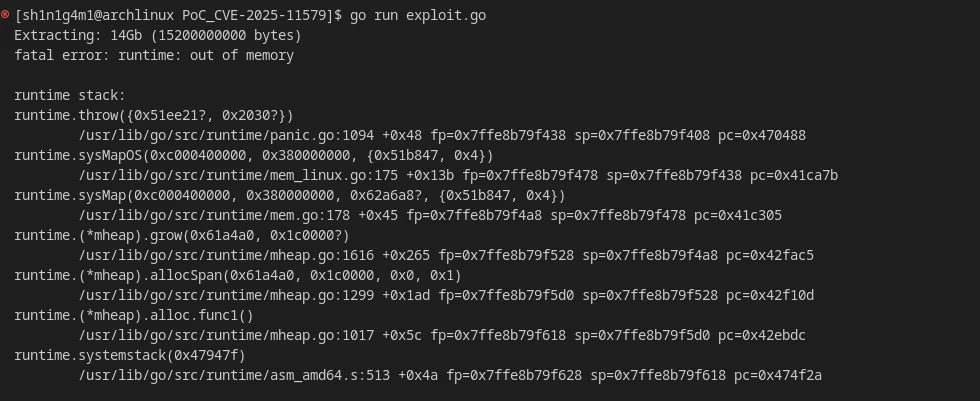 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 ffri/shadebios
PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025
 ant4g0nist/lisa.py
LLDB MCP Integration + other helpful commands
 revng/revng-c
Core binary-lifting library that translates executable code to LLVM IR and reconstructs C-like source for reverse engineering and automated binary…
 denuvosoftwaresolutions/gamba
Simplification of General Mixed Boolean-Arithmetic Expressions: GAMBA