


 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 m10ust/machscope
macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
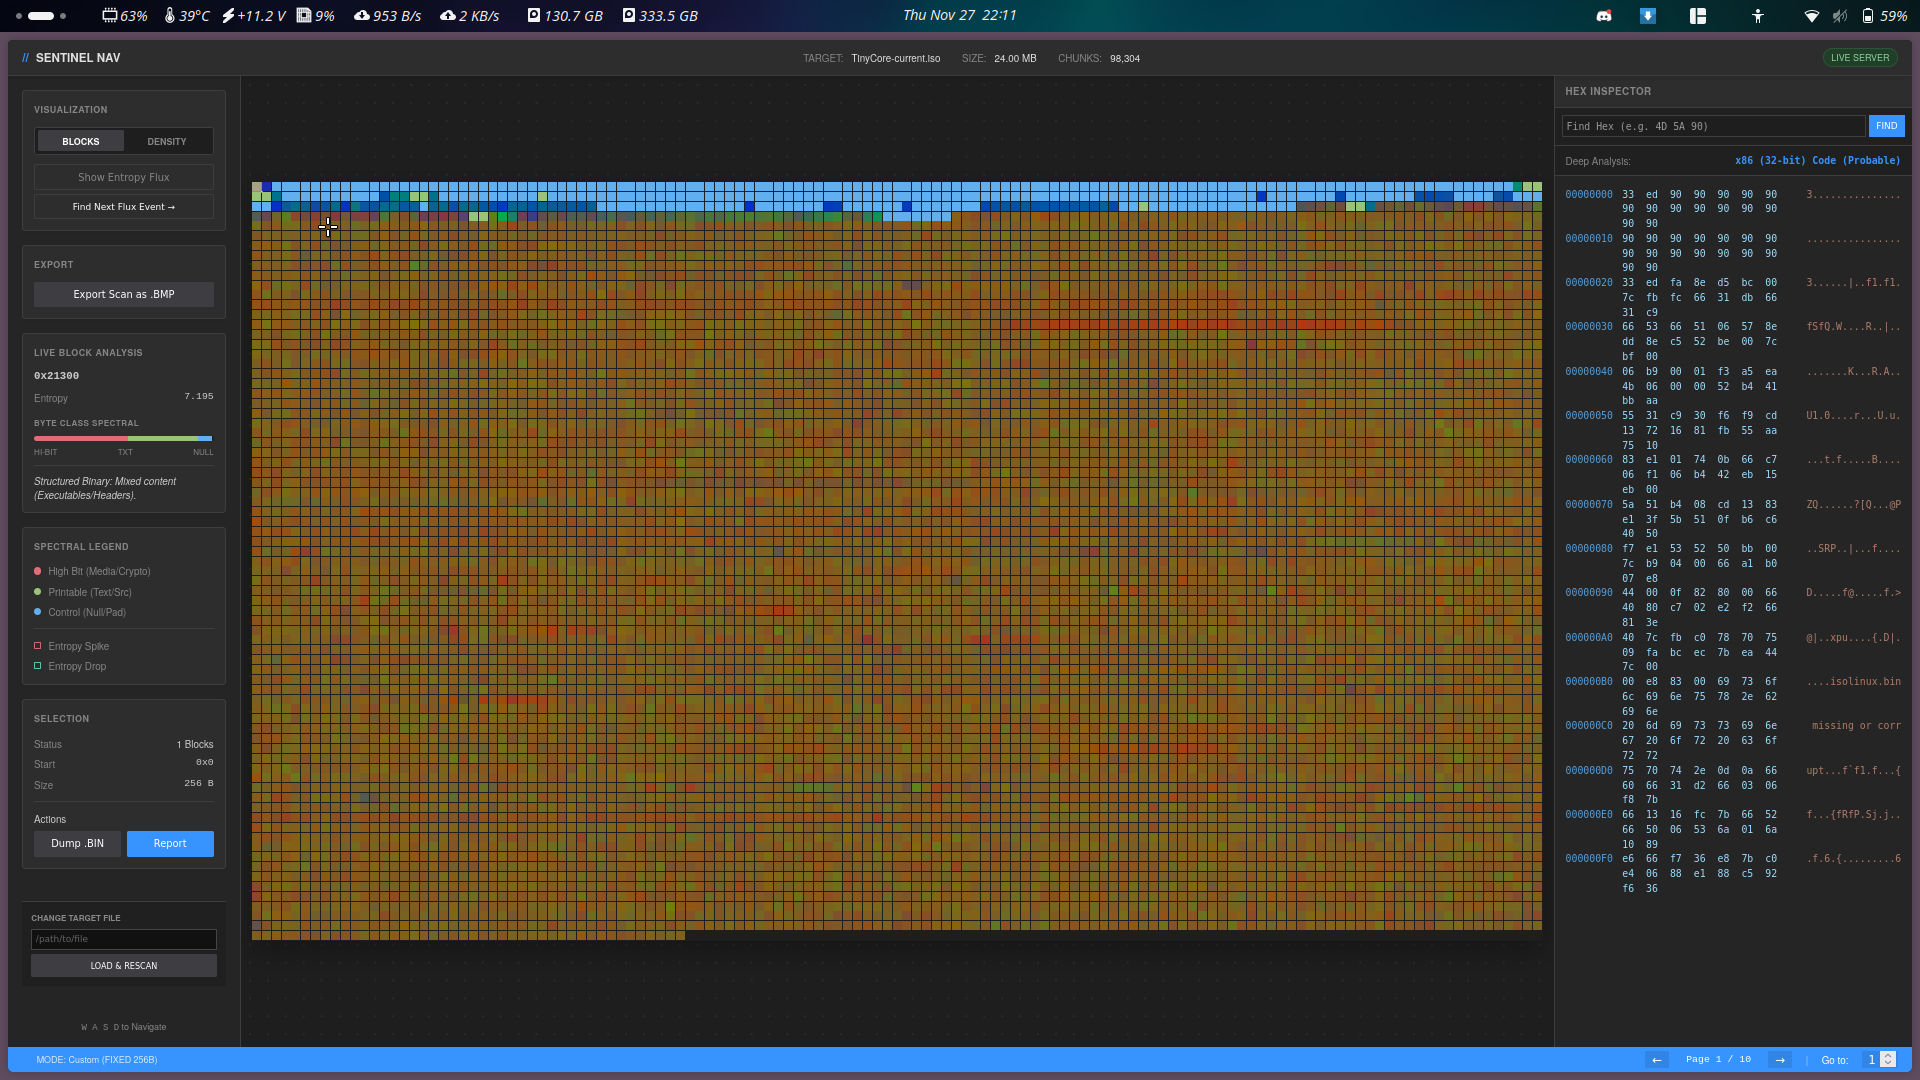 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 m31r0n/sniprecover-cli
Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303
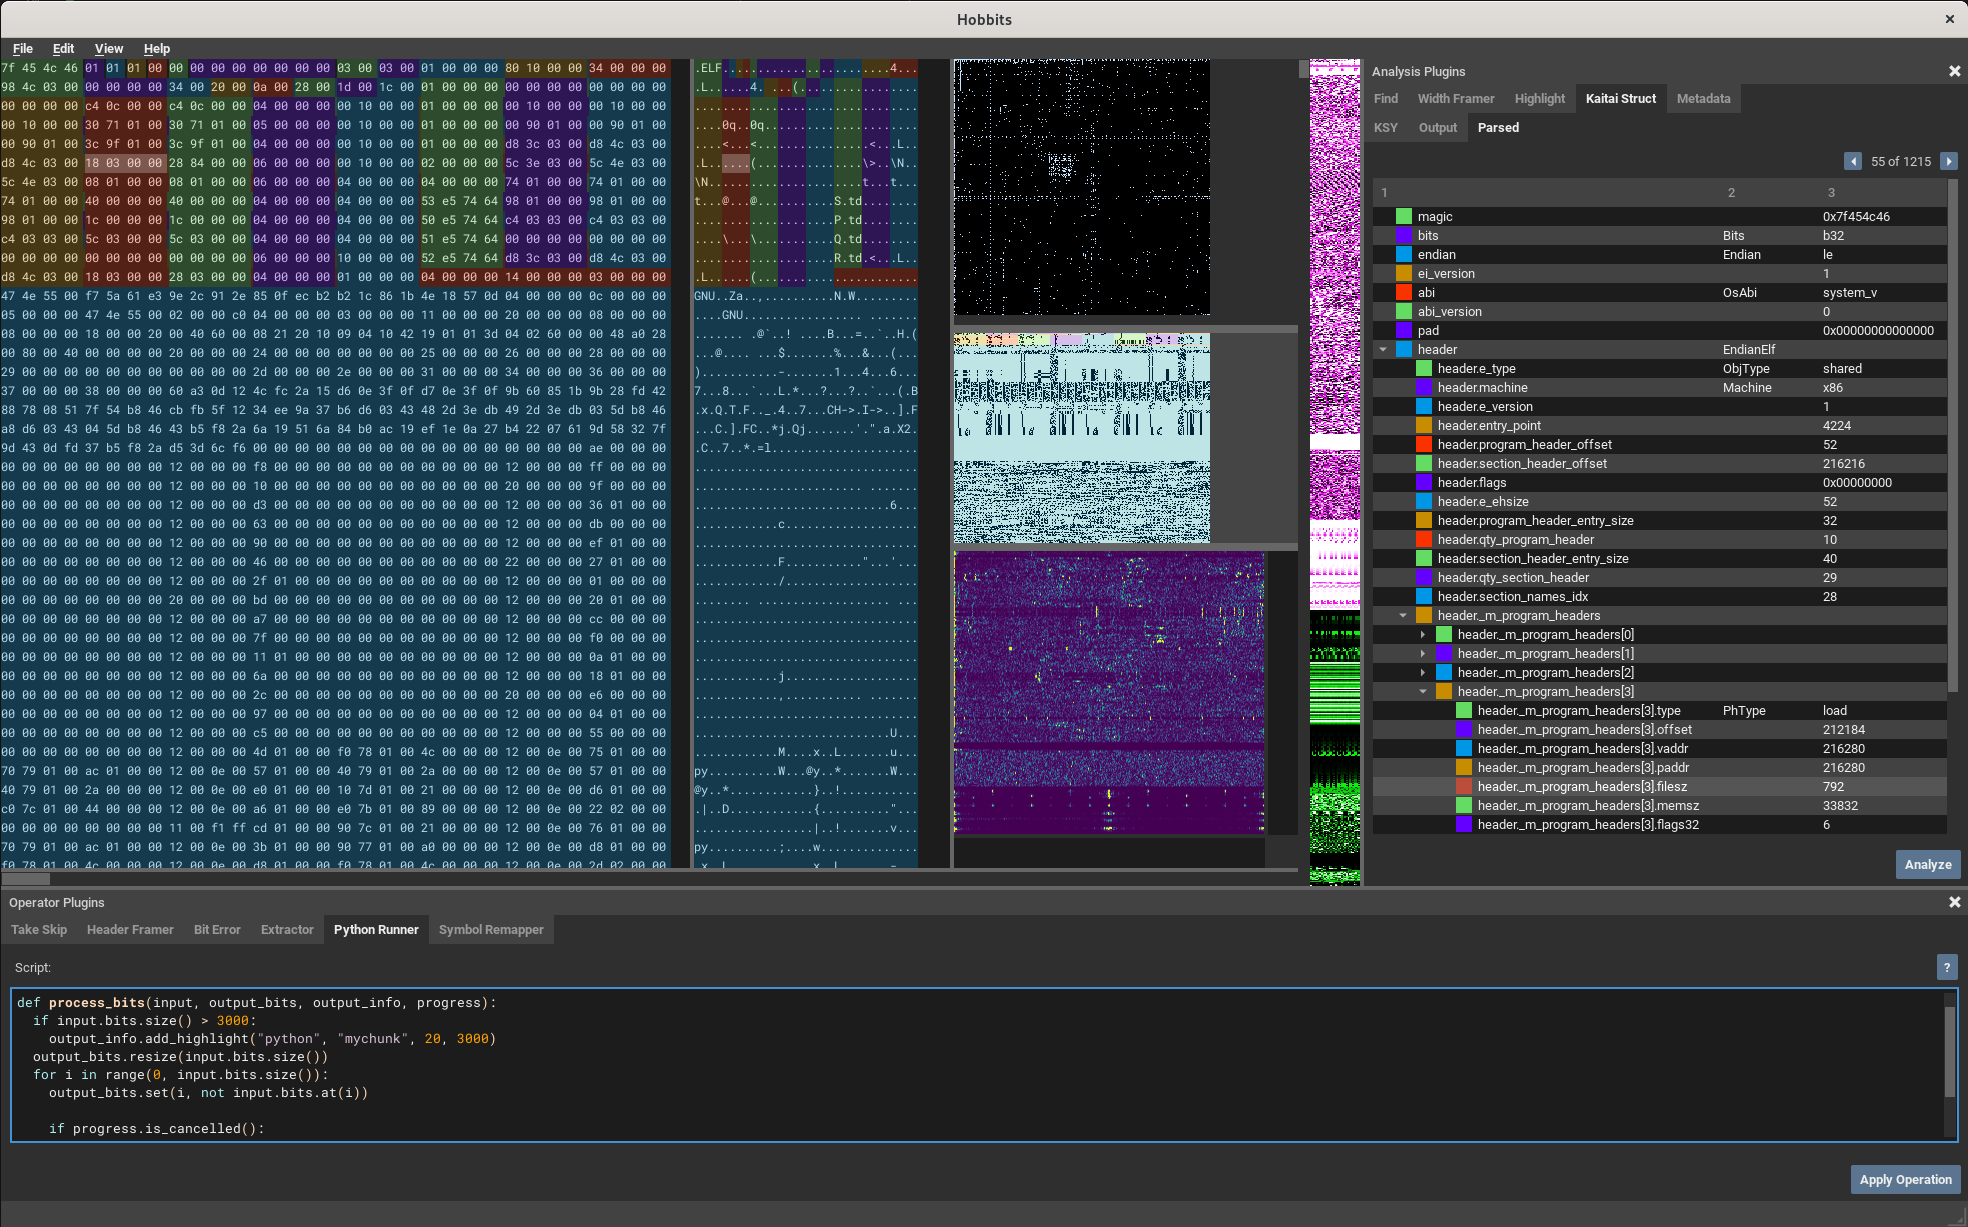 mahlet-inc/hobbits
A multi-platform GUI for bit-based analysis, processing, and visualization
 paul-tew/lifer
Windows link file (shortcuts) examiner
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing