
sandsifter
 battelle/sandsifter
The x86 processor fuzzer
vulnerability-analysisreverse-engineeringfuzzing+4
battelle/sandsifterThe x86 processor fuzzer
 xoreaxeaxeax/sandsifter
The x86 processor fuzzer
 nccgroup/binja_arch_ref
A simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
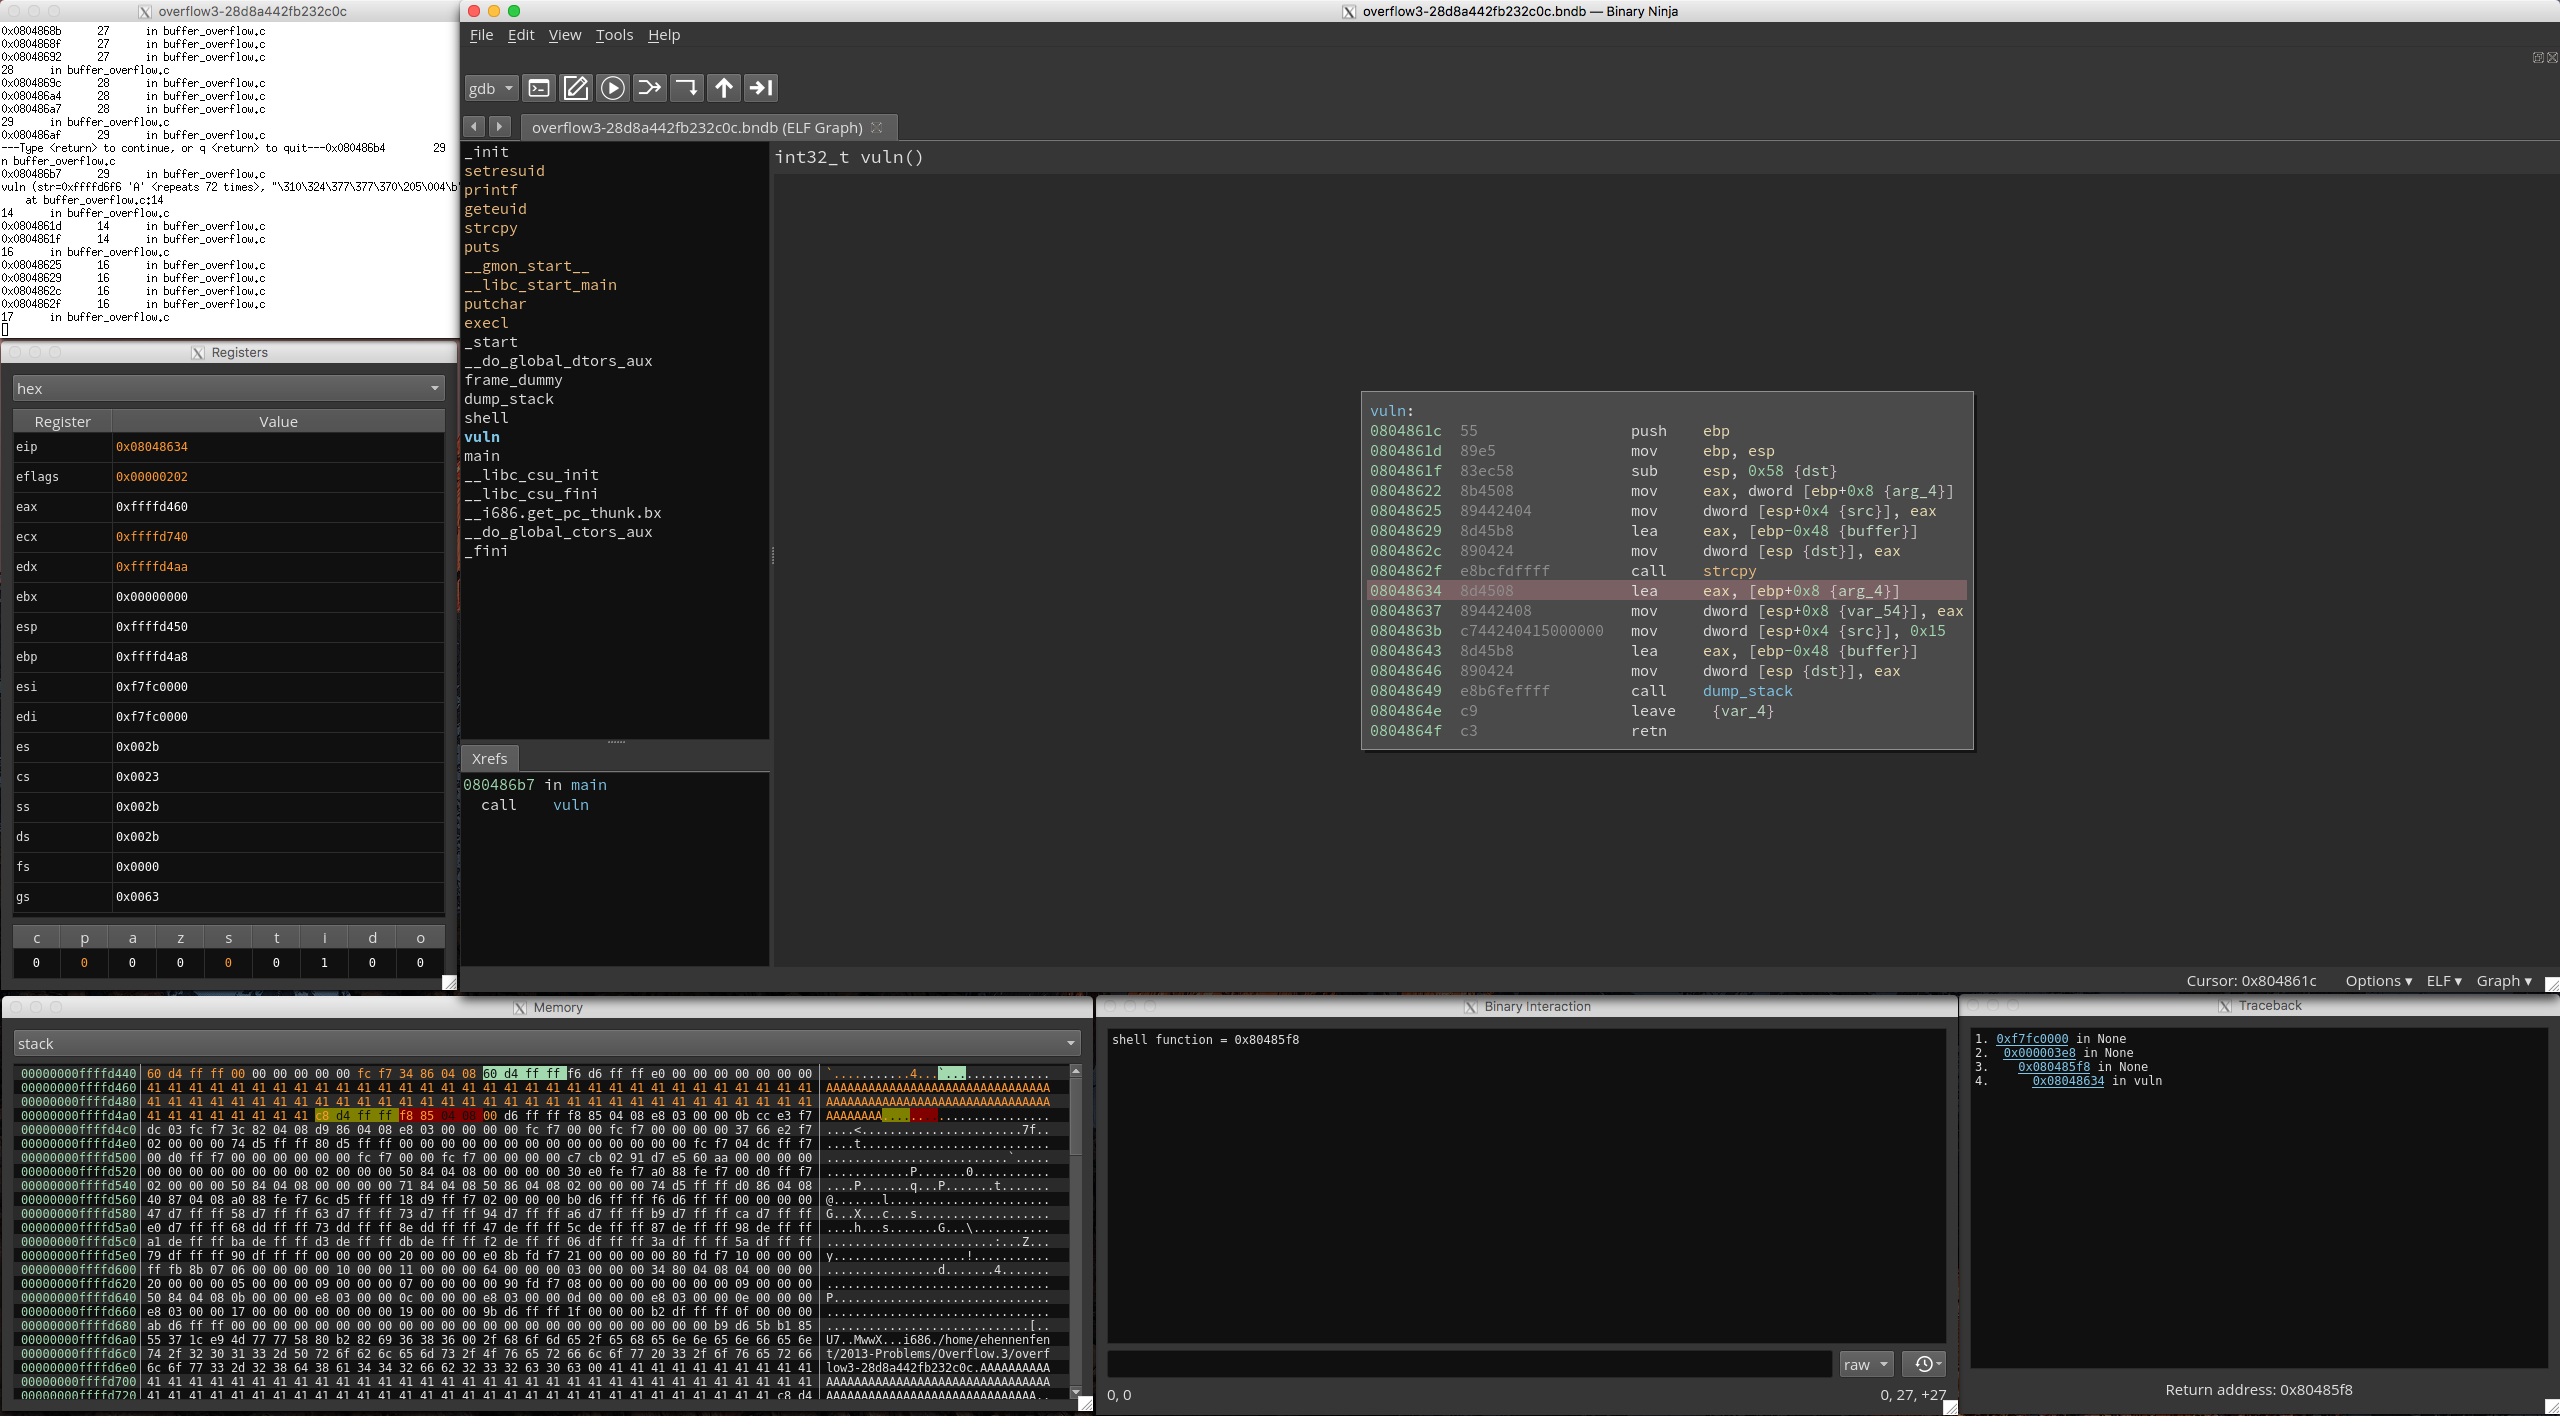 nccgroup/binja_dynamics
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
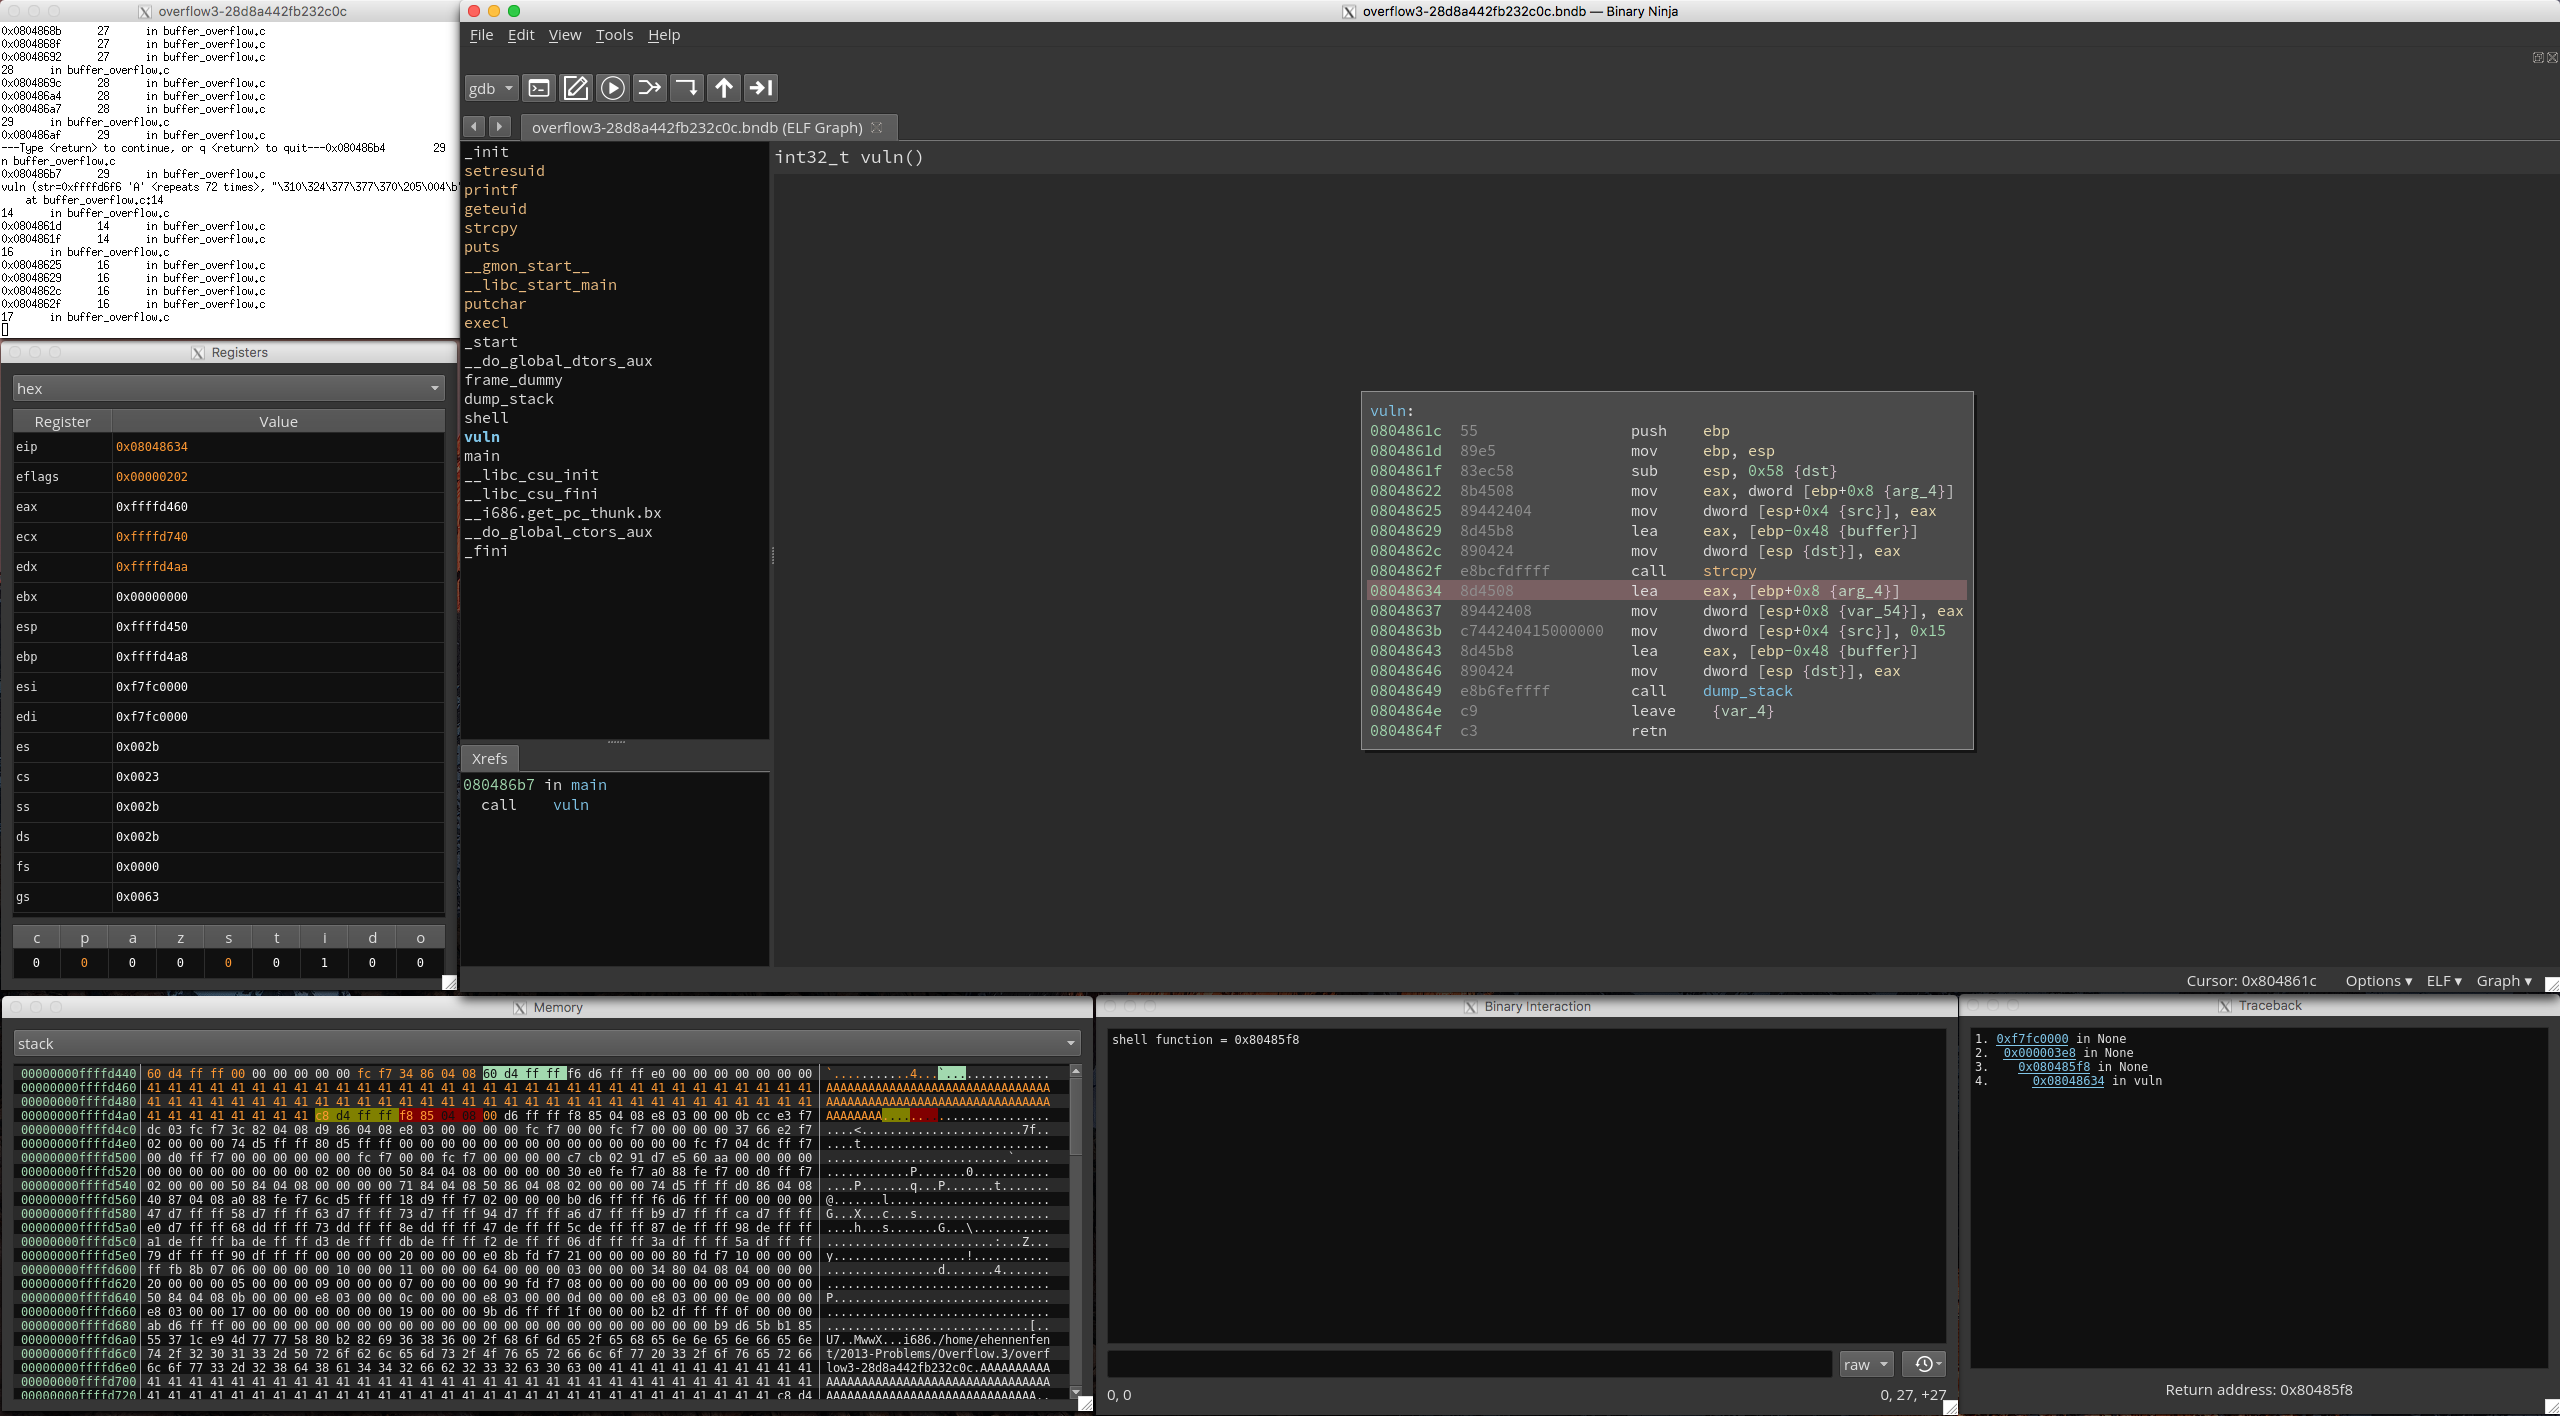 nccgroup/binja_sensei
A plugin that provides resources for beginners to learn reverse engineering using Binary Ninja. It automatically installs several other plugins, and…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 gdbinit/efiswissknife
IDA plugin to enhance (U)EFI binary reversing with batch analysis, GUID database, and service usage statistics for firmware security research.
 nccgroup/triforceafl
AFL/QEMU fuzzing with full-system emulation.
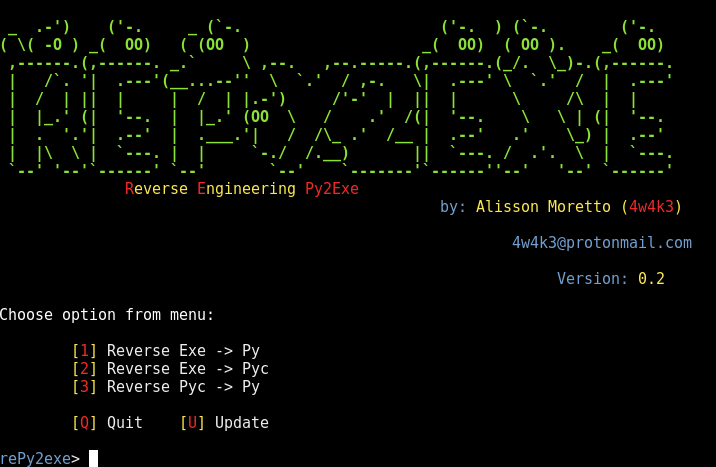 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 oalabs/frida-extract
Frida.re based RunPE (and MapViewOfSection) extraction tool
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 mmozeiko/aes-finder
Utility to find AES keys in running processes
 ehabhussein/ollydbg-binary-execution-visualizer
reverse engineering, visual binary analysis
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 census/choronzon
An evolutionary knowledge-based fuzzer