
icicle-python
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
43
icicle-emu/icicle-pythonPython bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
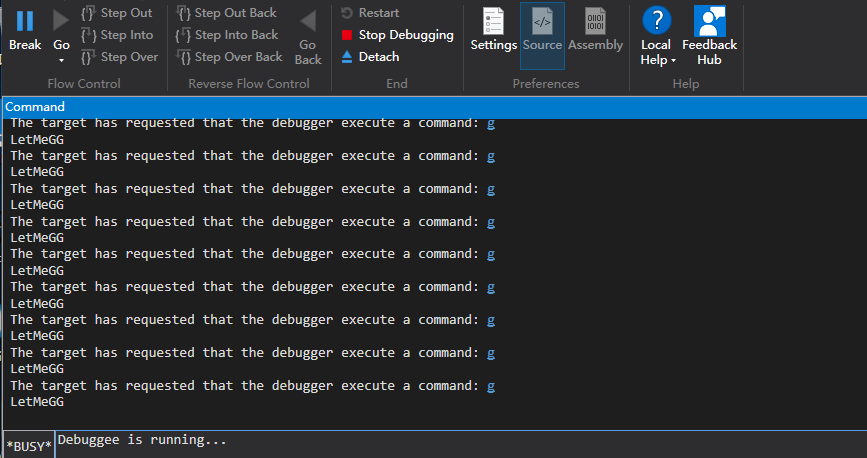 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
 gmh5225/linux-kernel-debugger
Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.
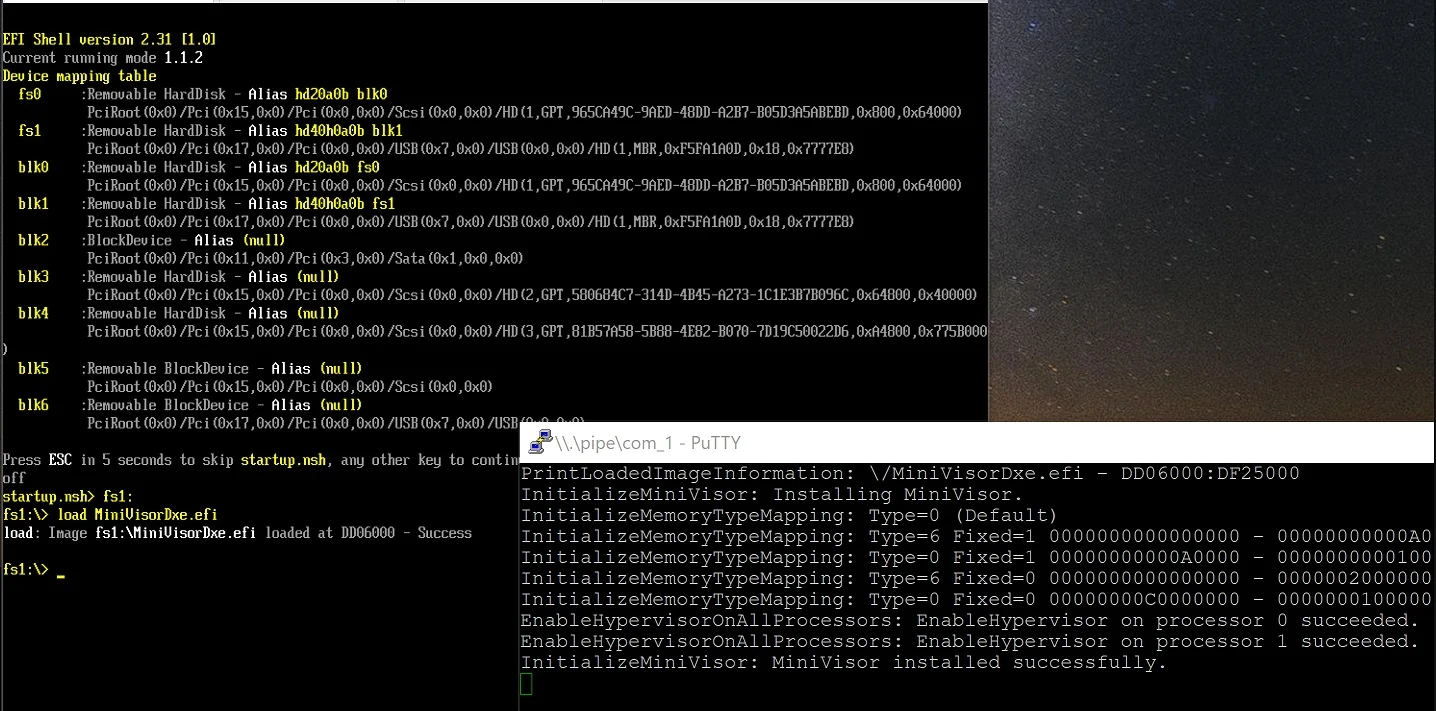 tandasat/minivisorpkg
The research UEFI hypervisor that supports booting an operating system.
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
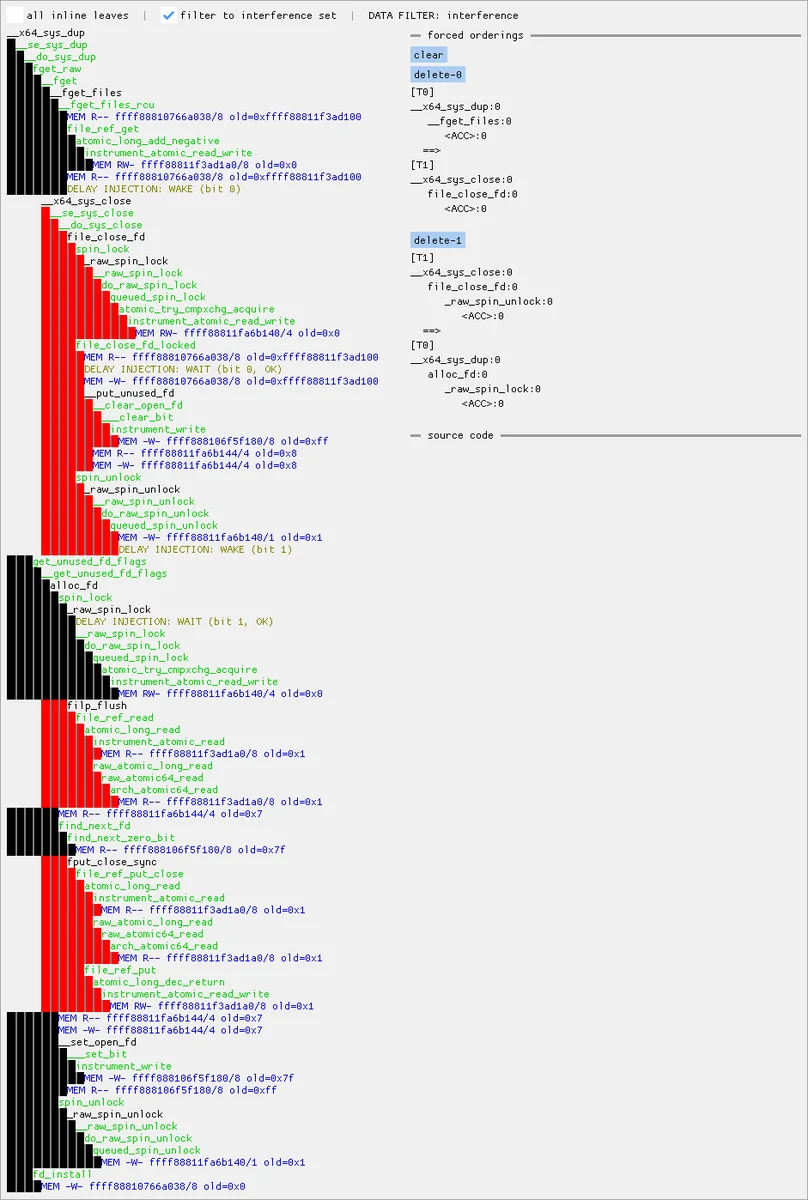 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
 werew/qsynth-artifacts
Benchmark datasets and synthesis artifacts for QSynth, containing Tigress-obfuscated C functions, x86_64 binaries, execution traces, ground truth,…
 darthton/hyperbone
Minimalistic VT-x hypervisor for Windows x64 providing syscall, MSR, IDT, and kernel inline hooks plus EPT-based page substitution and TLB splitting.
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 qmonnet/rbpf
Rust virtual machine and JIT compiler for eBPF programs
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
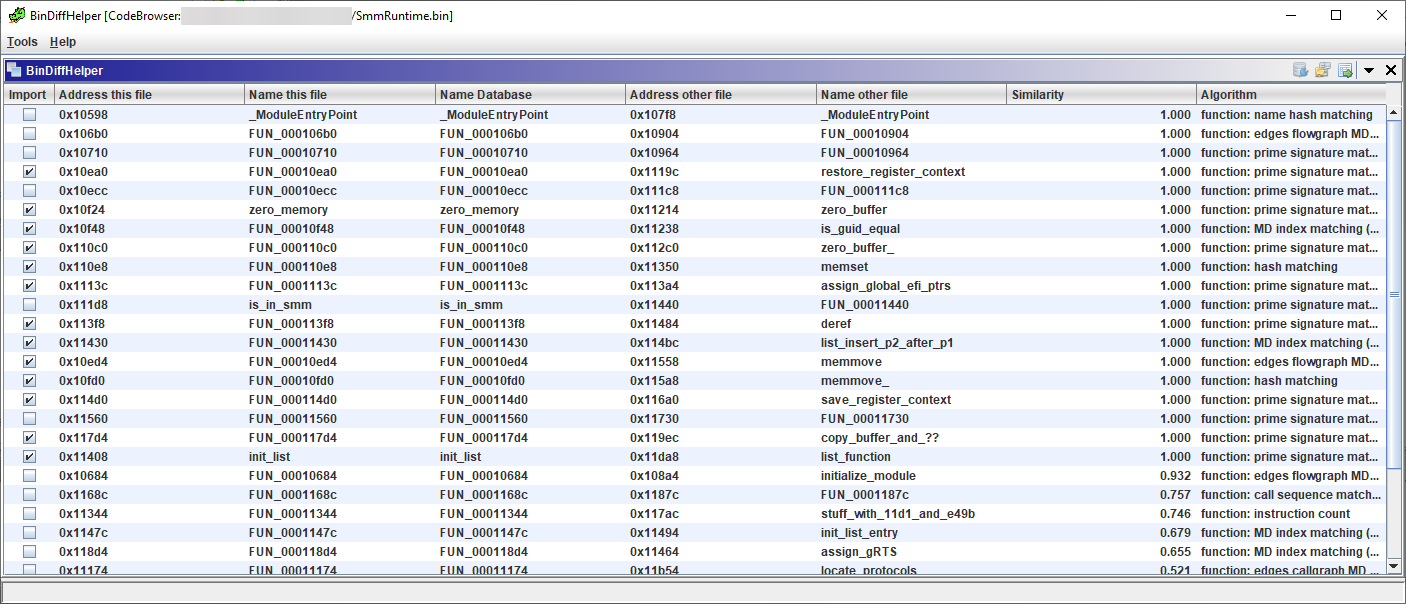 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching