
cve-2020-35498-flag
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
binary-analysisexploitationnetwork-security+2
freddierice/cve-2020-35498-flagC-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
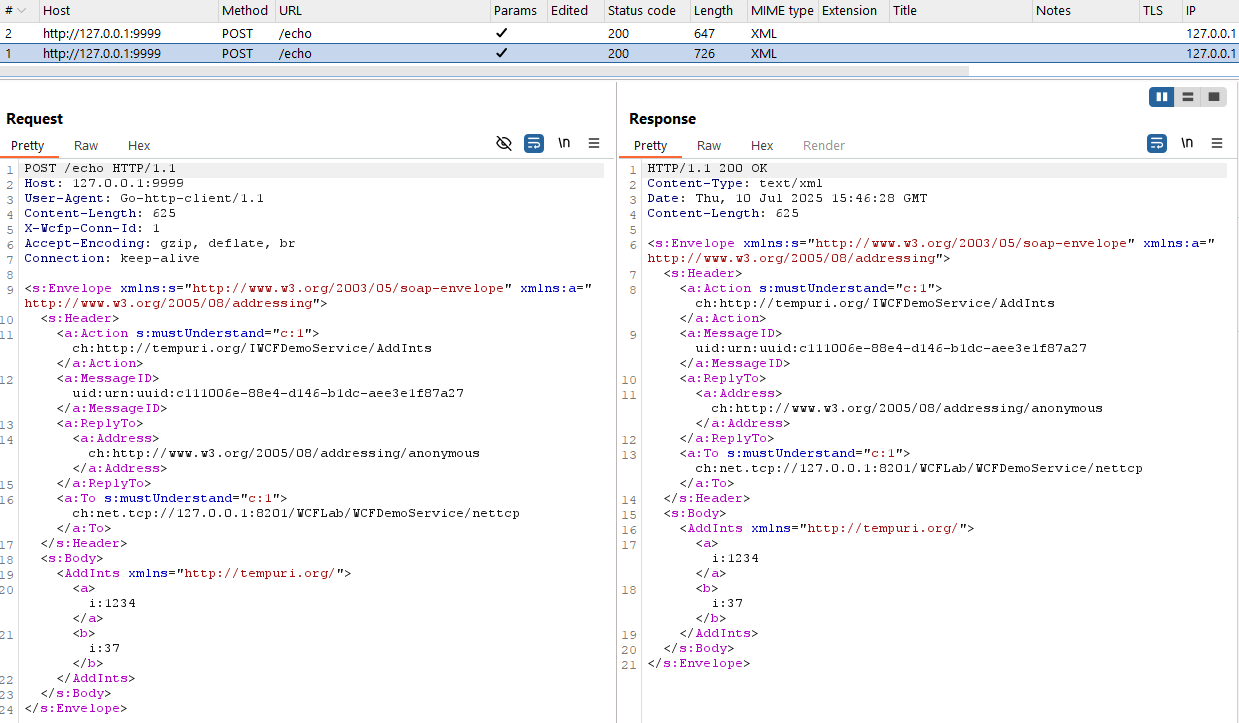 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 federicodotta/brida
The new bridge between Burp Suite and Frida!