EAC-Kernel-Packet-Fucker

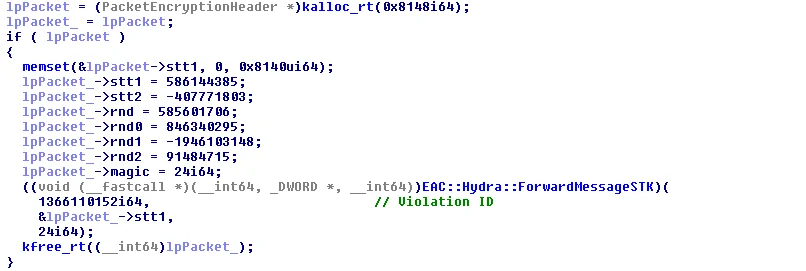
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.

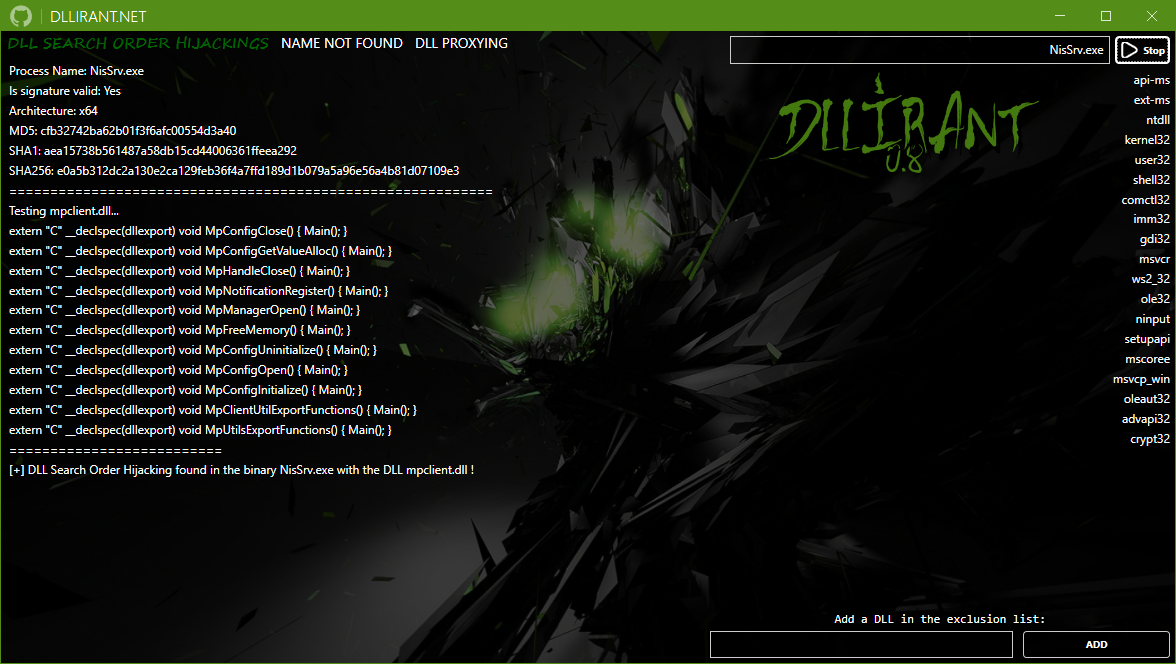
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

Pishi is a code coverage tool like kcov for macOS.

A tool for effective testing the binding layer of scripting languages

Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…

Automated defect verification tool for 6 dnsmasq CVEs (CVE-2026-2291, 4890, 4891, 4892, 4893, 5172)

Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…

A Runtime Crypter in C for Linux ELF binaries.

N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…

Automated static analysis tools for binary programs

Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…

Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…

Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…

Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…

Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…

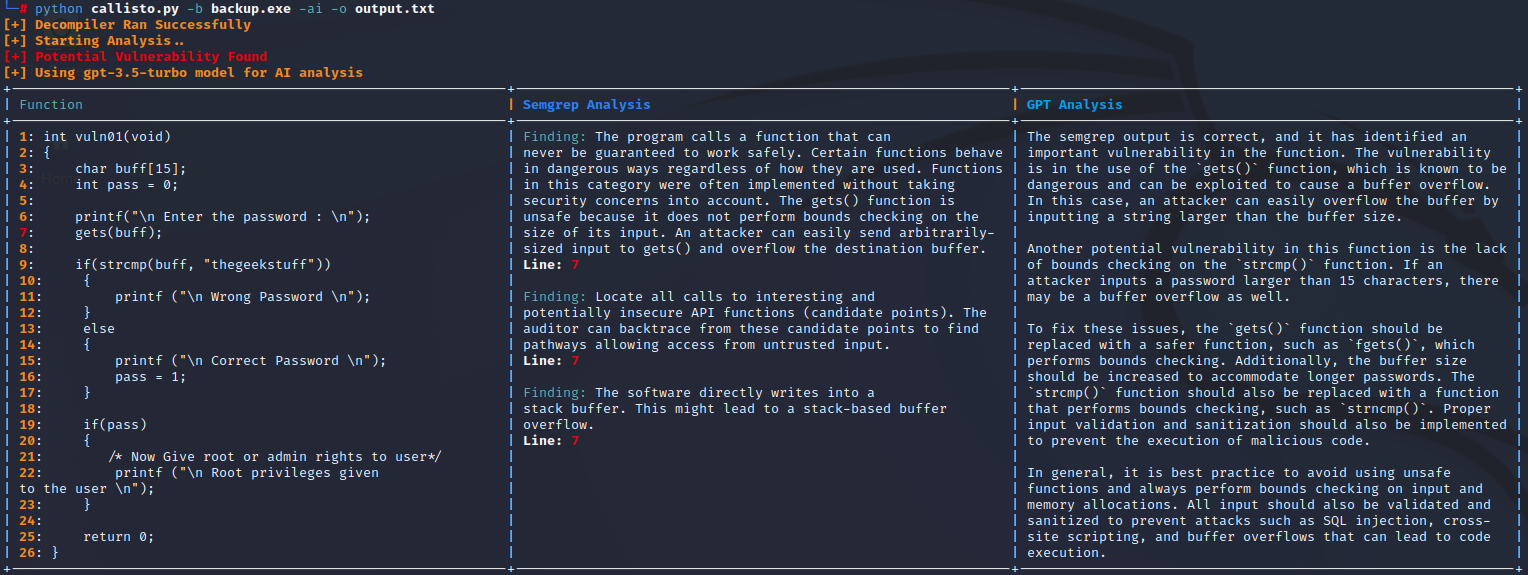
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…