
CVE-2017-12561
 parapapinho/cve-2017-12561
Reverse-engineering write-up and proof of concept for CVE-2017-12561, a use-after-free in HPE iMC dbman, covering binary diffing, ASN.1 decoding, and…
binary-analysisexploitationmemory-forensics+3
parapapinho/cve-2017-12561Reverse-engineering write-up and proof of concept for CVE-2017-12561, a use-after-free in HPE iMC dbman, covering binary diffing, ASN.1 decoding, and…
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 0x0oz/cve-2026-7482-poc
Proof-of-concept exploit for CVE-2026-7482, an unauthenticated heap out-of-bounds read in Ollama's GGUF loader, demonstrating memory exfiltration via…
 jaf0rk/cve-2026-3909
Proof-of-concept exploit for CVE-2026-3909, a Chromium Skia out-of-bounds vulnerability, with patches and crash analysis for reliable triggering in…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
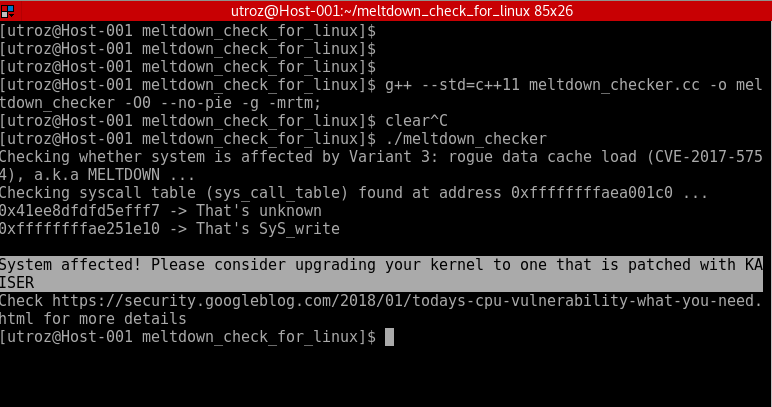 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.