

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
77 results
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
0xCr0ssCrush preview

0xCr0ssCrush

GitHubdeathshotxd/0xcr0sscrush

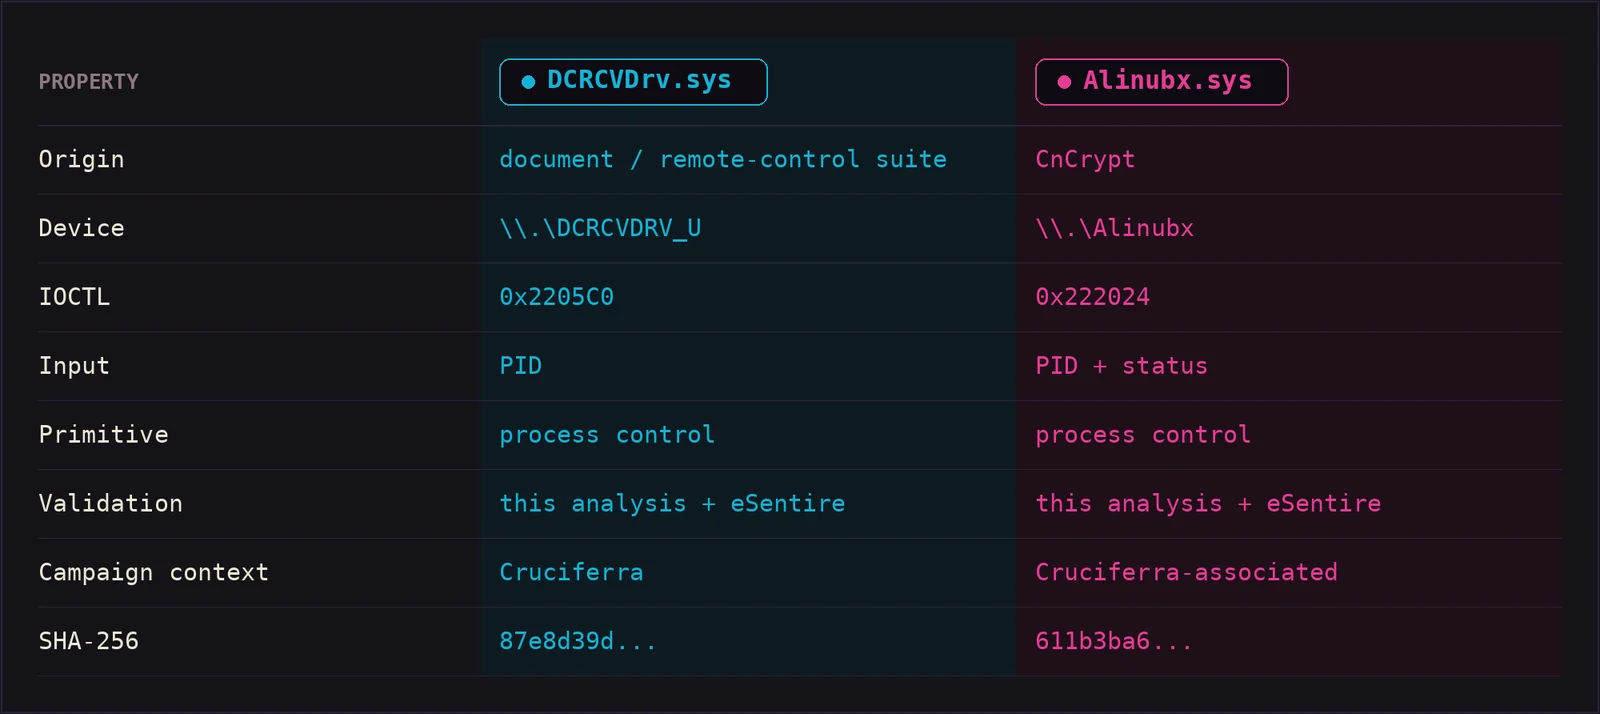
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
binary-analysisdefensive-toolsexploitation+4
3111 days ago
CVE-2022-2869-detector preview

CVE-2022-2869-detector

GitHubhalahajyahia/cve-2022-2869-detector

CodeQL detector for CVE-2022-2869 root cause (CWE-191 unsigned underflow) using control-flow/range analysis to identify vulnerable patterns without…
binary-analysiscode-analysisstatic-analysis+1
18 days ago
idamcp preview

idamcp

GitHubidamcp/idamcp

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
ai-assisted-reversingbinary-analysisdebuggers+3
1191 day ago
OWN-Defender preview

OWN-Defender

GitHubnirvanaon/own-defender

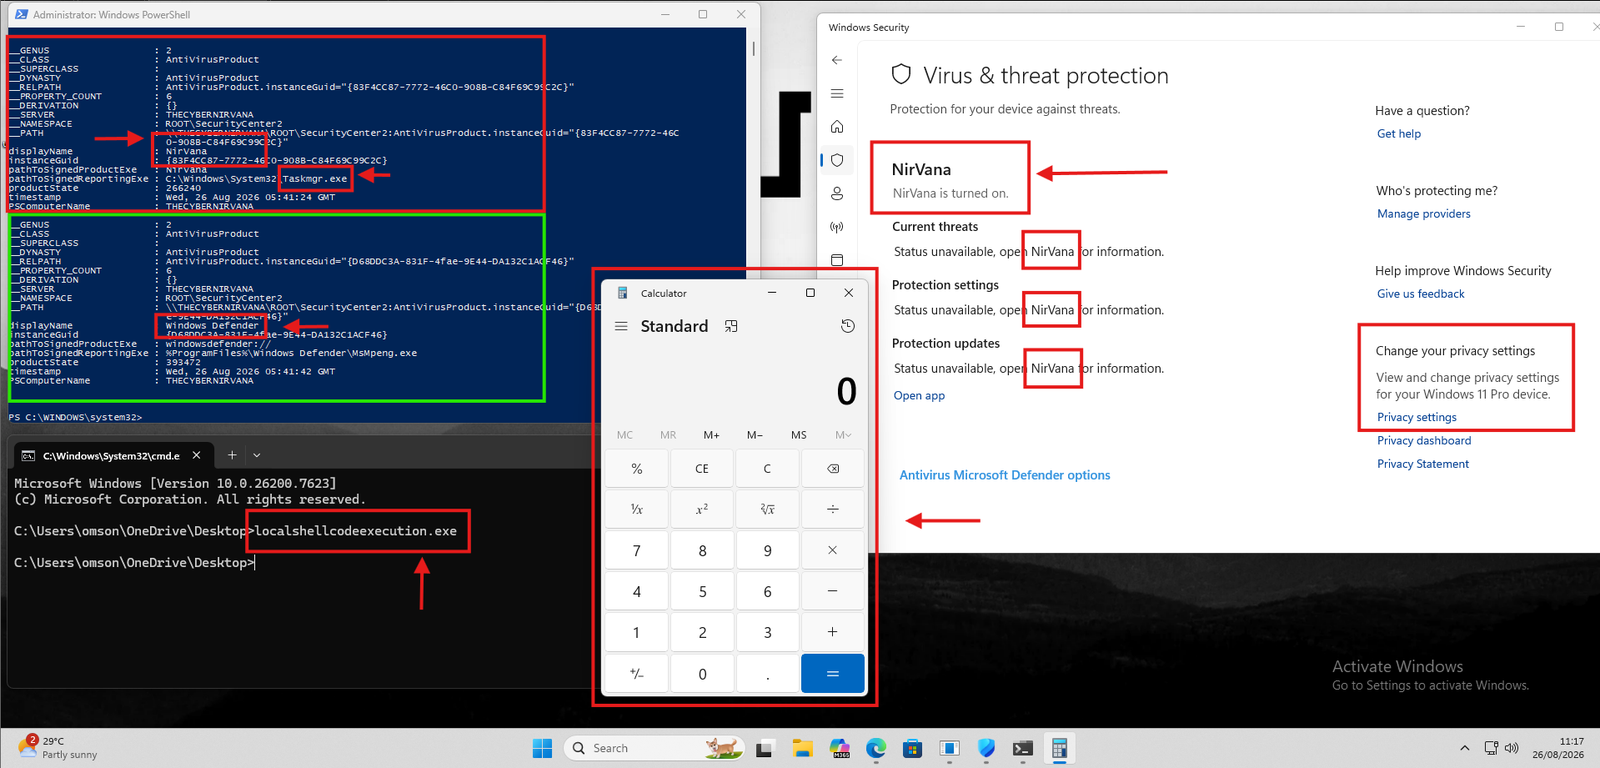
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…
binary-analysisdefensive-toolseducation+2
361 month ago
heaplens preview

heaplens

GitHubypl6/heaplens

CMPT733 Cybersecurity Lab II Project: GDB plugin for heap exploits inspired by CVE-2021-3156
binary-analysisdebuggerseducation+2
24 years ago
grandstream-cve-2026-2329-analysis preview

grandstream-cve-2026-2329-analysis

GitHubvivianuba/grandstream-cve-2026-2329-analysis

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
binary-analysiseducationfirmware-analysis+4
1 month ago
hexcymatix preview

hexcymatix

GitHubxoreaxeaxeax/hexcymatix

Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
binary-analysisreverse-engineeringstatic-analysis
191 month ago
mwcfg preview

mwcfg

GitHubc3rb3ru5d3d53c/mwcfg

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
1342 years ago
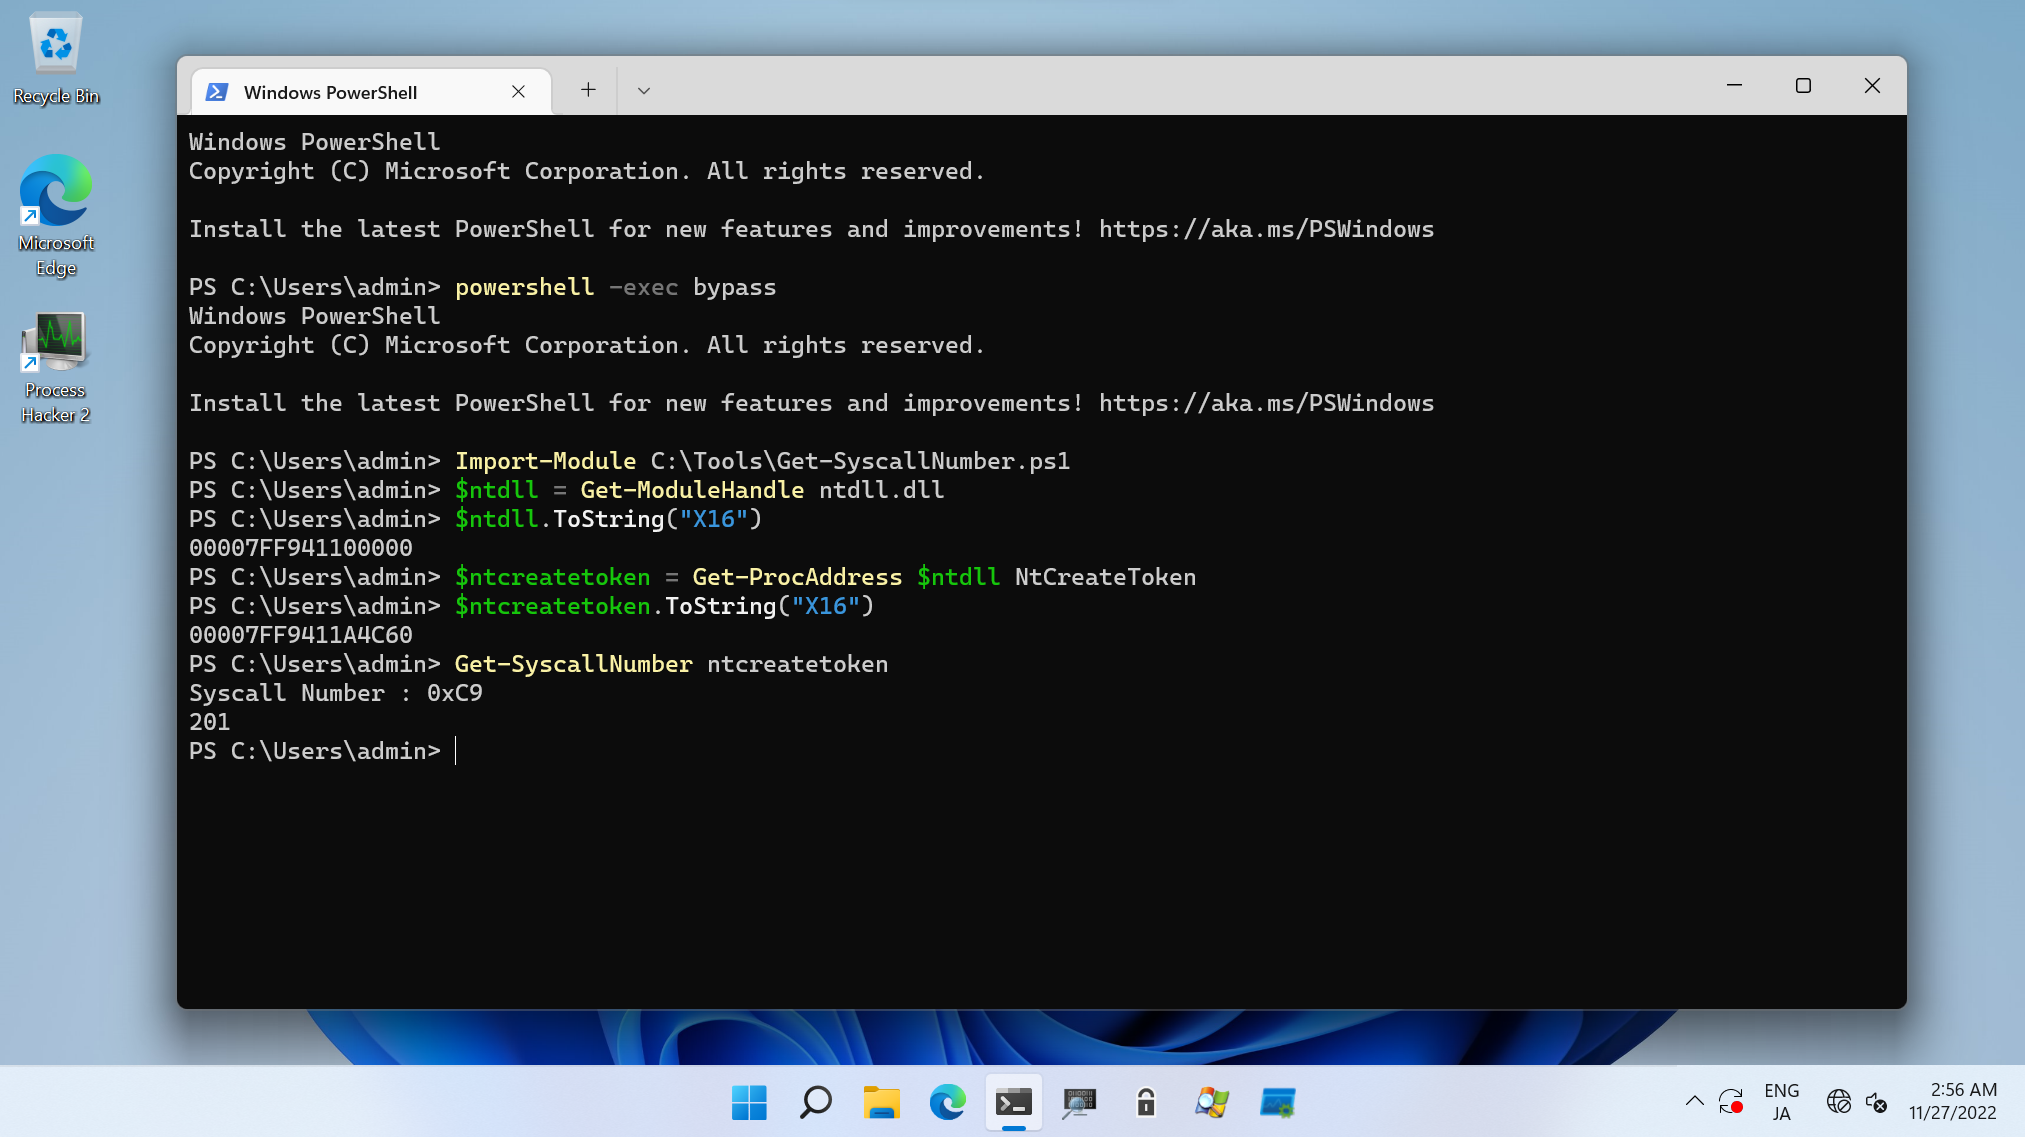
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.

adversarial-attackbinary-analysiseducation+3
3649 months ago
smoke_conf_extract preview

smoke_conf_extract

GitHubmyrtus0x0/smoke_conf_extract

Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.

binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
133 years ago
IDARustDemangler preview

IDARustDemangler

GitHubtimetravelthree/idarustdemangler

Rust Demangler & Normalizer plugin for IDA
binary-analysiscode-analysisreverse-engineering
3563 years ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve
binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.

binary-analysiseducationlabs-practice+6
1581 year ago
tp-link-decrypt preview

tp-link-decrypt

GitHubwatchfulip/tp-link-decrypt

Decrypt TP-Link Firmware
binary-analysiscryptographyembedded-systems-security+4
8311 months ago
VMUnprotect.Dumper preview

VMUnprotect.Dumper

GitHubvoid-stack/vmunprotect.dumper

VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.

binary-analysisdynamic-code-analysismalware-analysis+1
4614 years ago
memaddressanalysis preview

memaddressanalysis

GitHubnccgroup/memaddressanalysis

Research project related to memory address analysis

binary-analysismemory-forensicspapers-research+1
1412 years ago
Previous12345Next