Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
miniDumpReader preview

miniDumpReader

GitHubgmh5225/minidumpreader

Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…

binary-analysisdigital-forensicsforensics+3
3 years ago
entropystrip preview

entropystrip

GitHubdwexi/entropystrip

Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine

binary-analysisdefensive-toolsdigital-forensics+6
84 days ago
IPA preview

IPA

GitHubseekbytes/ipa

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

binary-analysisdefensive-toolsdigital-forensics+6
8832 years ago
refinery preview

refinery

GitHubbinref/refinery

High Octane Triage Analysis

binary-analysiscryptographyforensics+4
8779 days ago
dotnetfile preview

dotnetfile

GitHubpan-unit42/dotnetfile

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

binary-analysisforensicshash-analysis+4
1188 months ago
dissect.cobaltstrike preview

dissect.cobaltstrike

GitHubfox-it/dissect.cobaltstrike

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
binary-analysiscommand-and-controldigital-forensics+4
2125 days ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files
binary-analysisforensicsmalware-analysis+2
998 months ago
BiBi-Windows-Wiper-Analysis preview

BiBi-Windows-Wiper-Analysis

GitHubknight0x07/bibi-windows-wiper-analysis

Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
binary-analysisdigital-forensicsincident-response+3
92 years ago
NtWarden preview

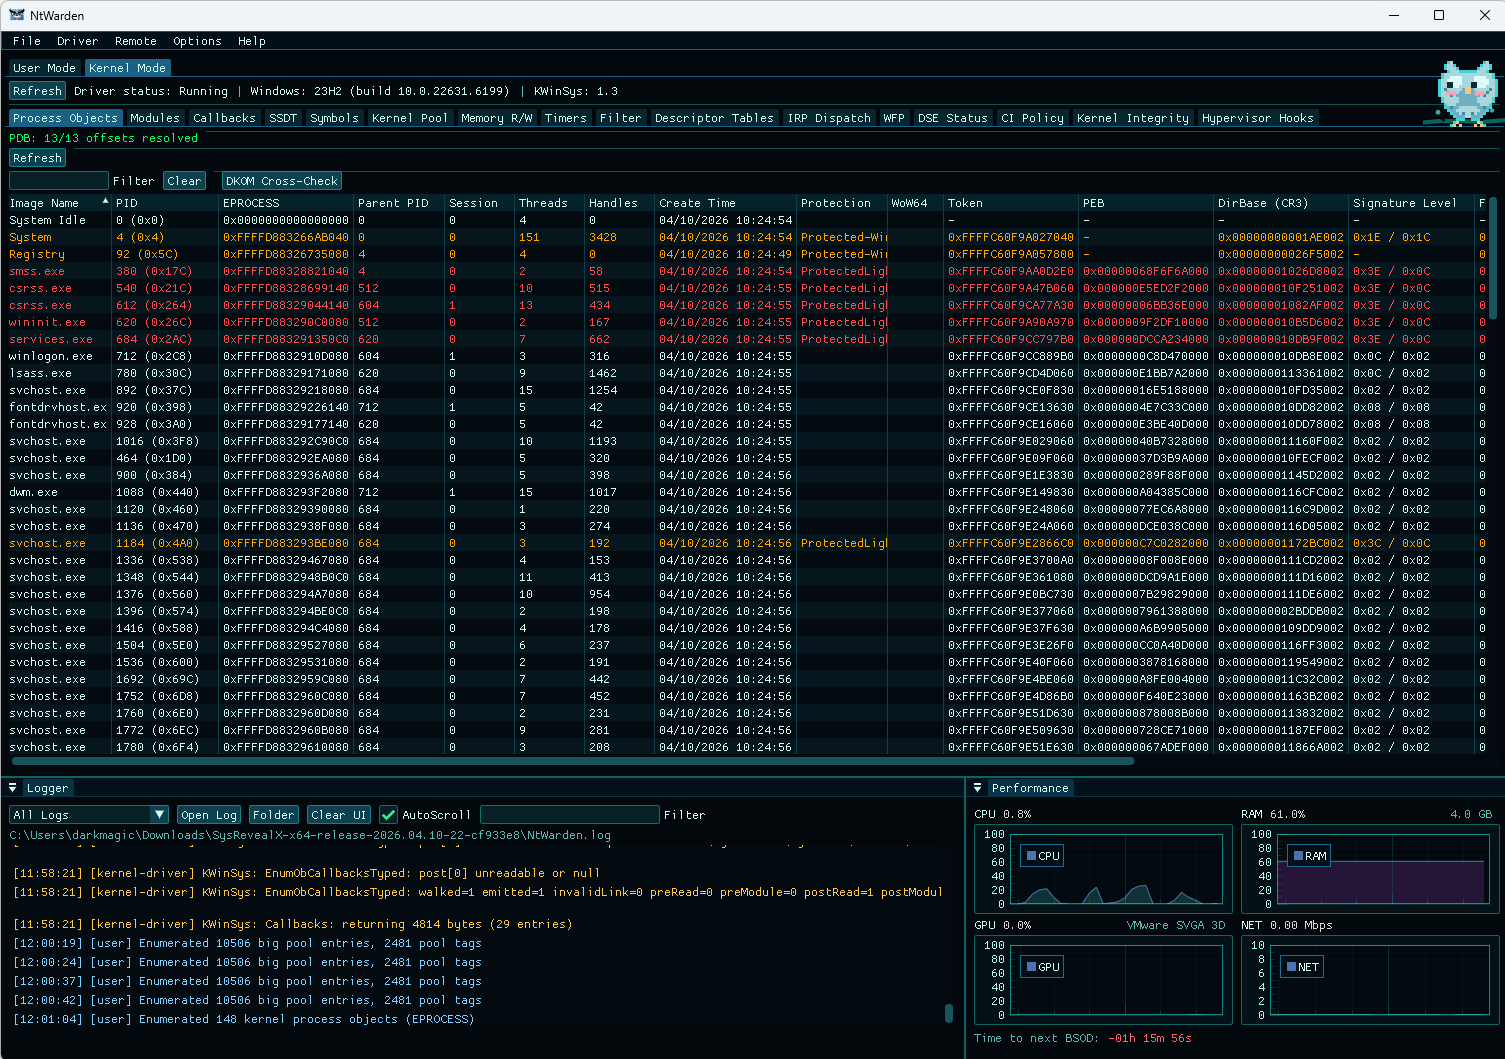
NtWarden

GitHubmrt4ntr4/ntwarden

Windows Analysis and Research Toolkit
binary-analysisdefensive-toolsdigital-forensics+4
7015 months ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
WindowsPatchDetector preview

WindowsPatchDetector

GitHubnccgroup/windowspatchdetector

Experimental Windows .text section Patch Detector
binary-analysisdefensive-toolsdigital-forensics+3
2311 years ago
libfwsi preview

libfwsi

GitHublibyal/libfwsi

Library to access the Windows Shell Item format
binary-analysisdata-recoverydigital-forensics+1
7511 days ago
binwally preview

binwally

GitHubbmaia/binwally

Binary and Directory tree comparison tool using Fuzzy Hashing
binary-analysisdata-recoverydigital-forensics+3
8411 years ago
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis
binary-analysiscryptographyforensics+3
908 years ago
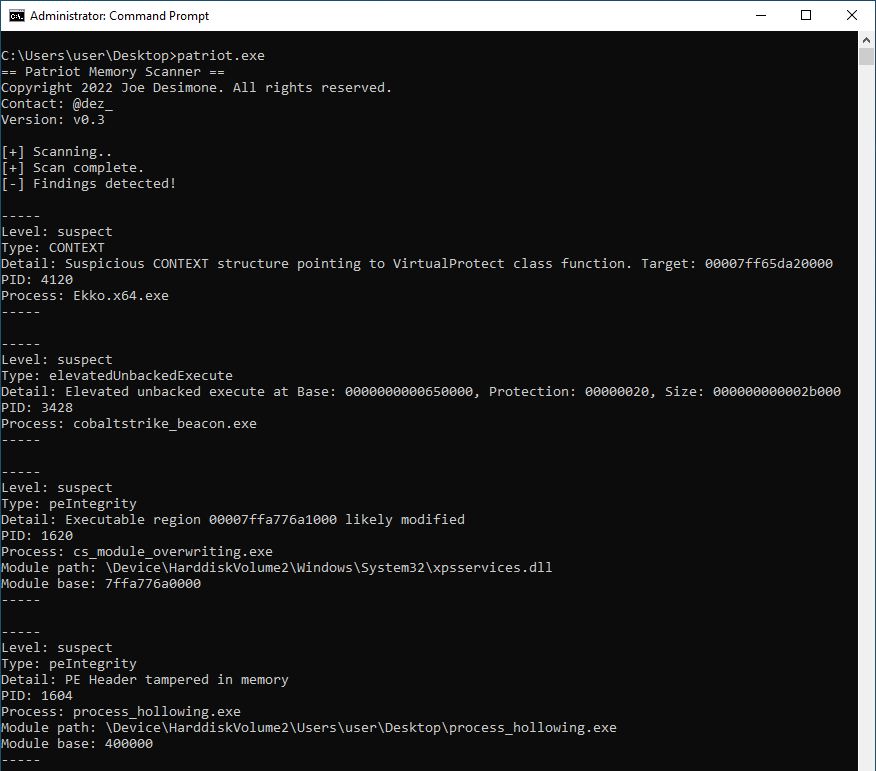
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
1654 years ago
xz-backdoor-scan preview

xz-backdoor-scan

GitHubjuul/xz-backdoor-scan

Scan for files containing the signature from the `xz` backdoor (CVE-2024-3094)

binary-analysisforensicsgeneral-purpose-utilities+3
2 years ago
rtf_exploit_extractor preview

rtf_exploit_extractor

GitHubcyberclues/rtf_exploit_extractor

Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents
binary-analysisexploitationforensics+2
239 years ago
Log4JShell-Bytecode-Detector preview

Log4JShell-Bytecode-Detector

GitHubcodeshield-security/log4jshell-bytecode-detector

Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)

binary-analysiscode-analysisincident-response+3
494 years ago
Previous1234Next