CVE-2025-0324-axis-vapix-privesc

Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…

Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)

Python Command-Line Ghidra Decompiler

The FLARE team's open-source library to disassemble Common Intermediate Language (CIL) instructions.

Scans an executable and determines if it was wrapped in an Electron version vulnerable to the Chromium vulnerability CVE-2023-4863/ CVE-2023-5129

Demonstration of CVE-2025-62518: a critical PAX extended header size override bug in tokio-tar and async Rust tar libraries, with reproduction tools…

Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding

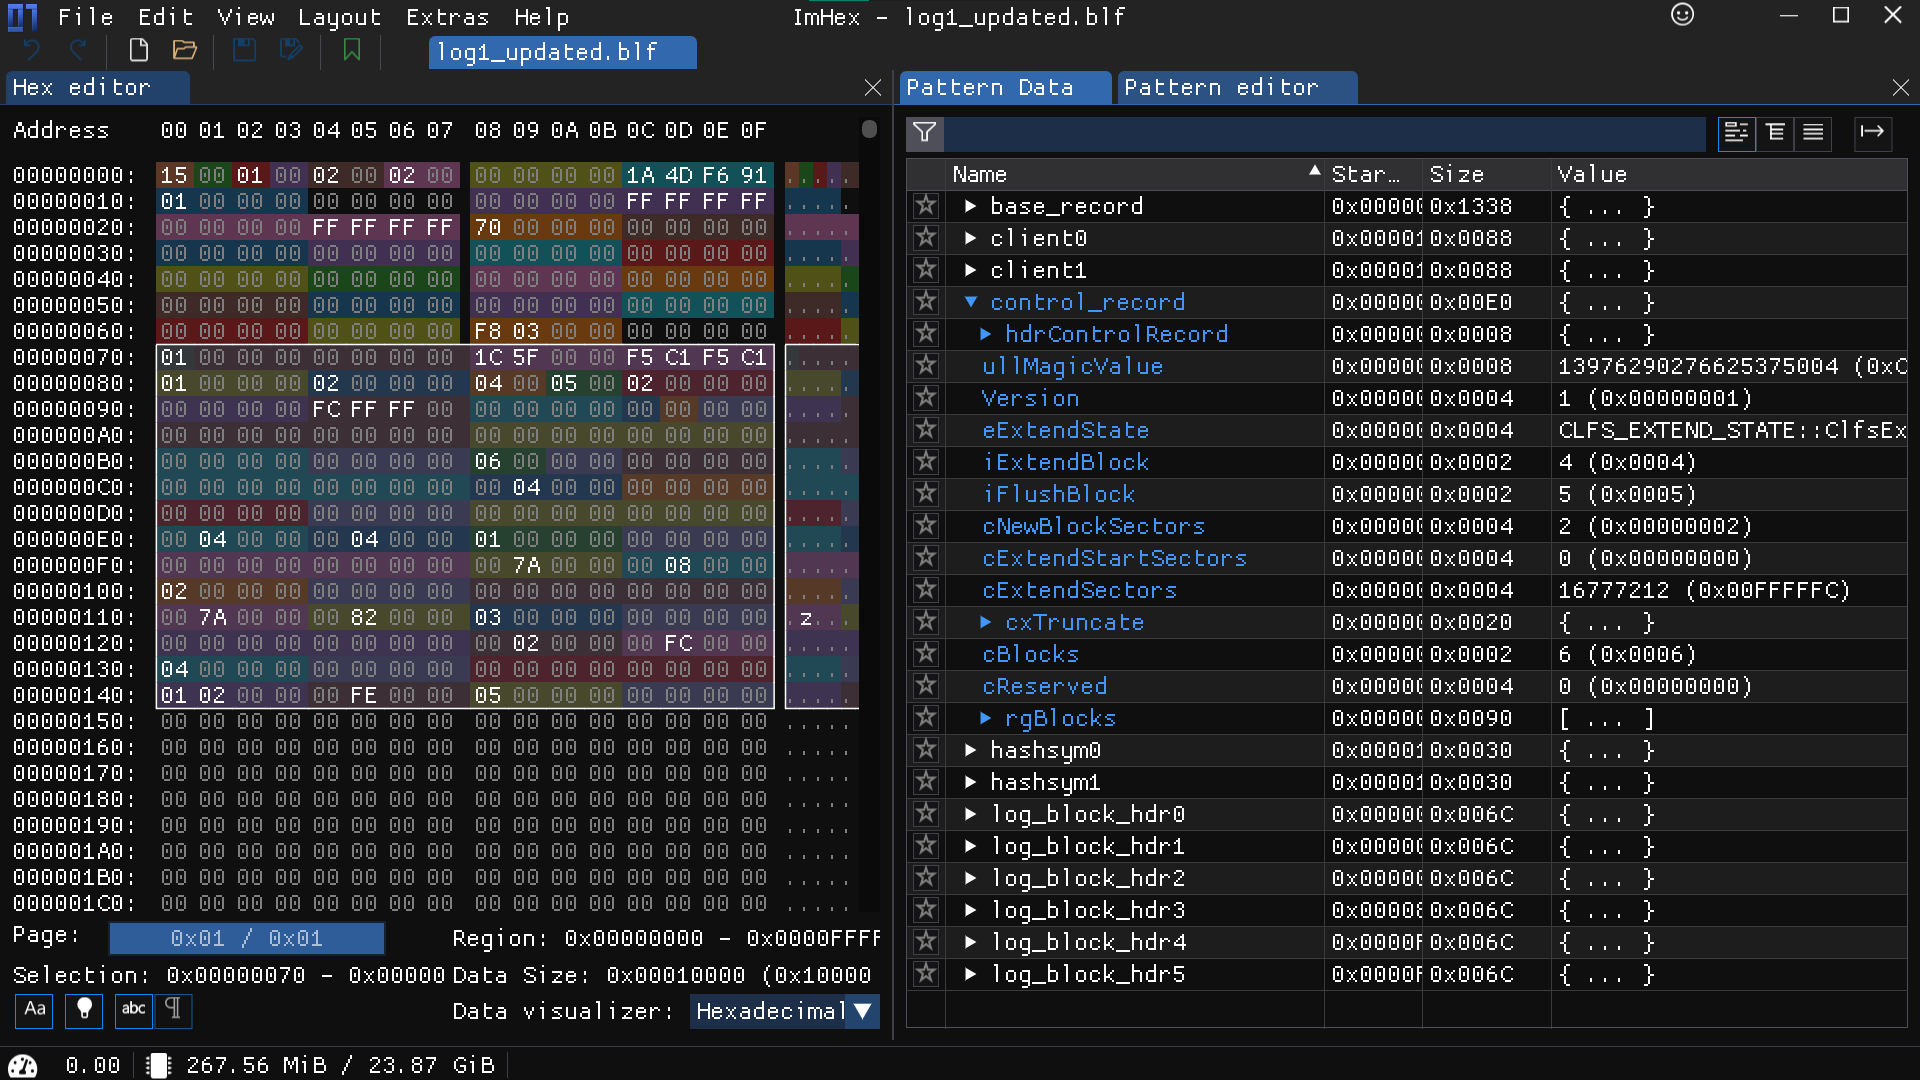
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension

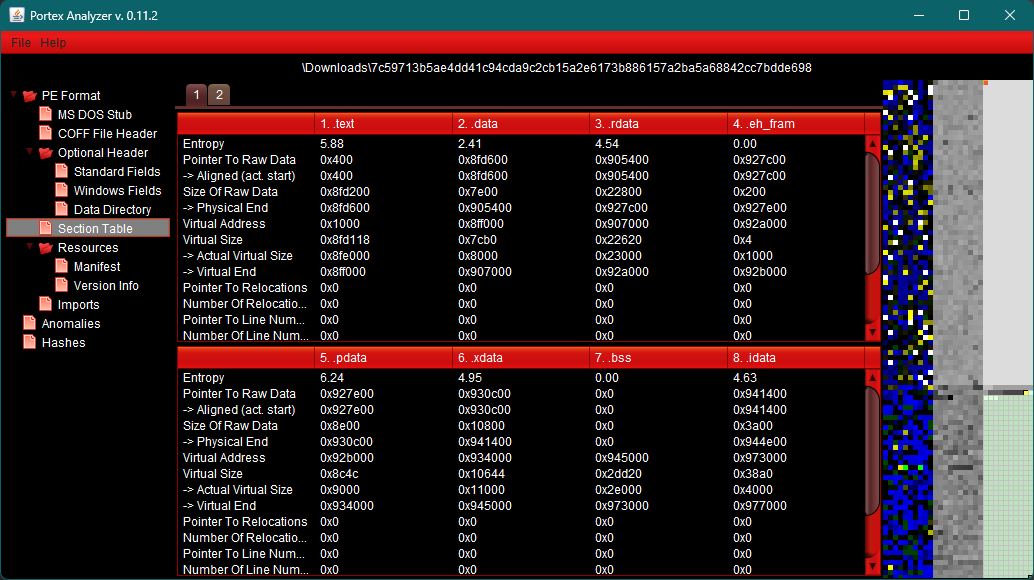
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library

ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…

:detective: Analyse binaries for missing security features, information disclosure and more...