
qvm-tool
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
binary-analysiscode-analysisdynamic-analysis-sandboxing+5
2
neurosaki987/qvm-toolStatic analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 nmatt0/moria
IoT firmware identification and extraction
 decalage2/collisions
Hash collisions and their exploitations
 jas502n/010-editor-template
Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
 rishvic/xpdf-docker
Docker images of Xpdf 4.04, vulnerable to CVE-2022-30524
 pazhanivelmani/webp_android10_r33_cve-2023-1999
Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…
 pazhanivelmani/libexif_android10_r33_cve-2016-6328
C-based library for parsing, editing, and saving EXIF metadata from JPEG images, with a focus on exploiting CVE-2016-6328 for Android 10.
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268
 huiwen-yayaya/cve-2023-4863
Reproduction and exploitation of CVE-2023-4863, a heap-buffer-overflow in libwebp's Huffman table builder, with crafted WebP images and ASAN-verified…
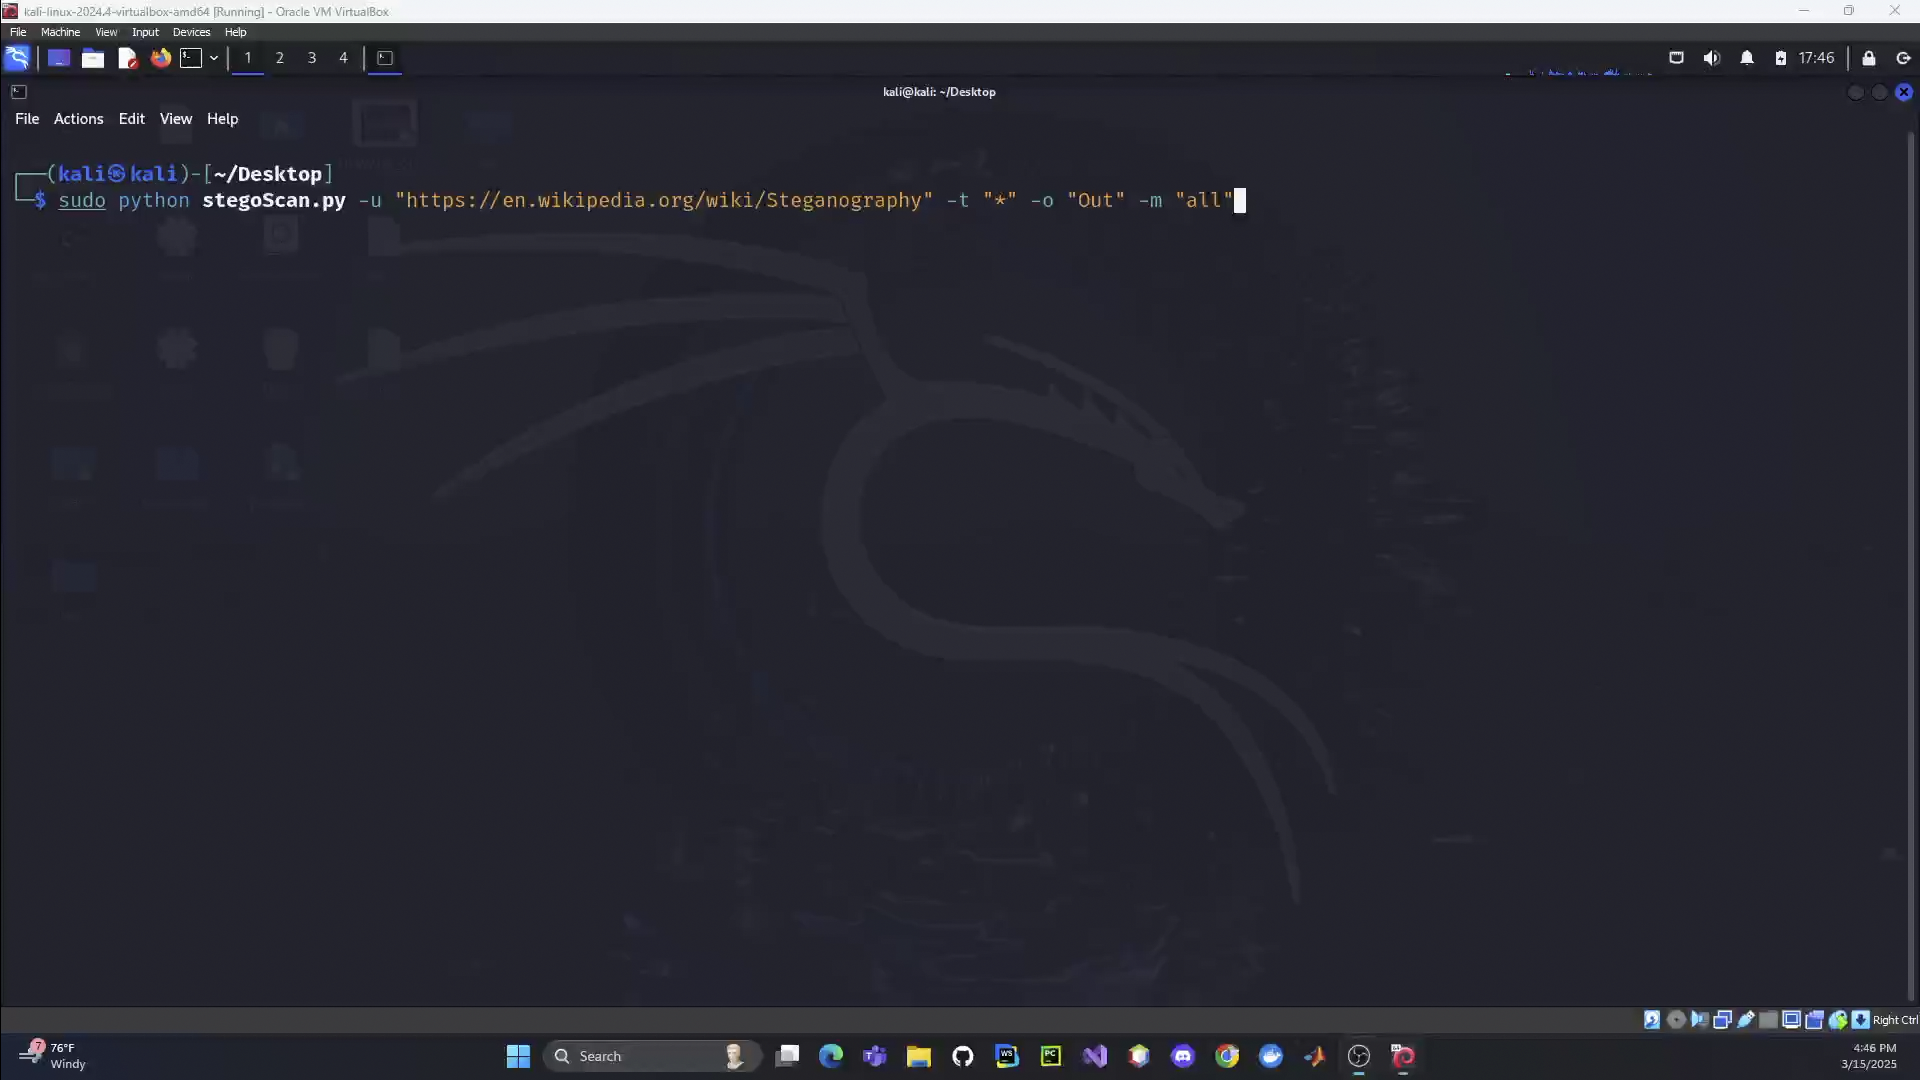 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering