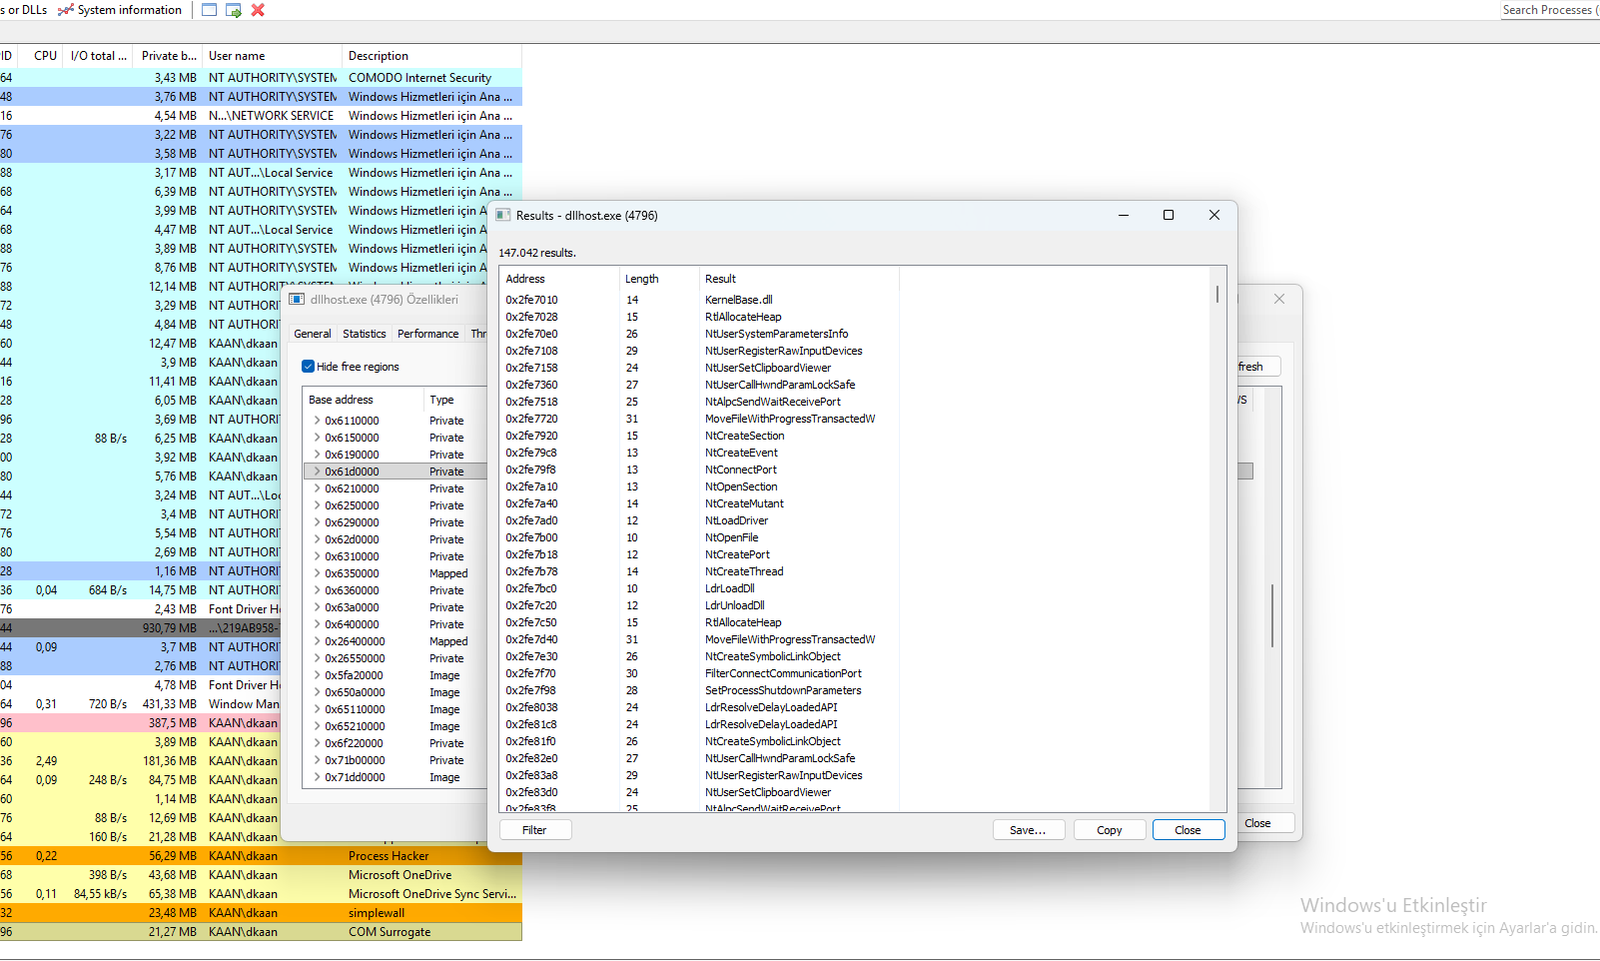
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

The next stage of CyberMeowfil (CVE-2026-43499 and 43074),Possibly biased toward vivo devices?

CVE-2026-43813: CloudAttestation enforceEnvironment bypass

Coefficient-Based Reconstruction of Arithmetic — a Mixed Boolean-Arithmetic (MBA) expression simplifier for deobfuscation

autonomous red teaming platform; multi-agent offensive-security meta-harness

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

Patched version of dnstracer fixing CVE-2017-9430 stack-based buffer overflow via argv[0] length validation. Traces DNS server chains for hostname…

N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…

cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…

a systems programming language prioritizing verifiable correctness, determinism, and performance

Injects code into ELF executables post-build

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…