
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
65 results
CVE-2026-96515 preview

CVE-2026-96515

GitHubwhoami-012/cve-2026-96515

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

binary-analysisembedded-systems-securityexploitation+7
11 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

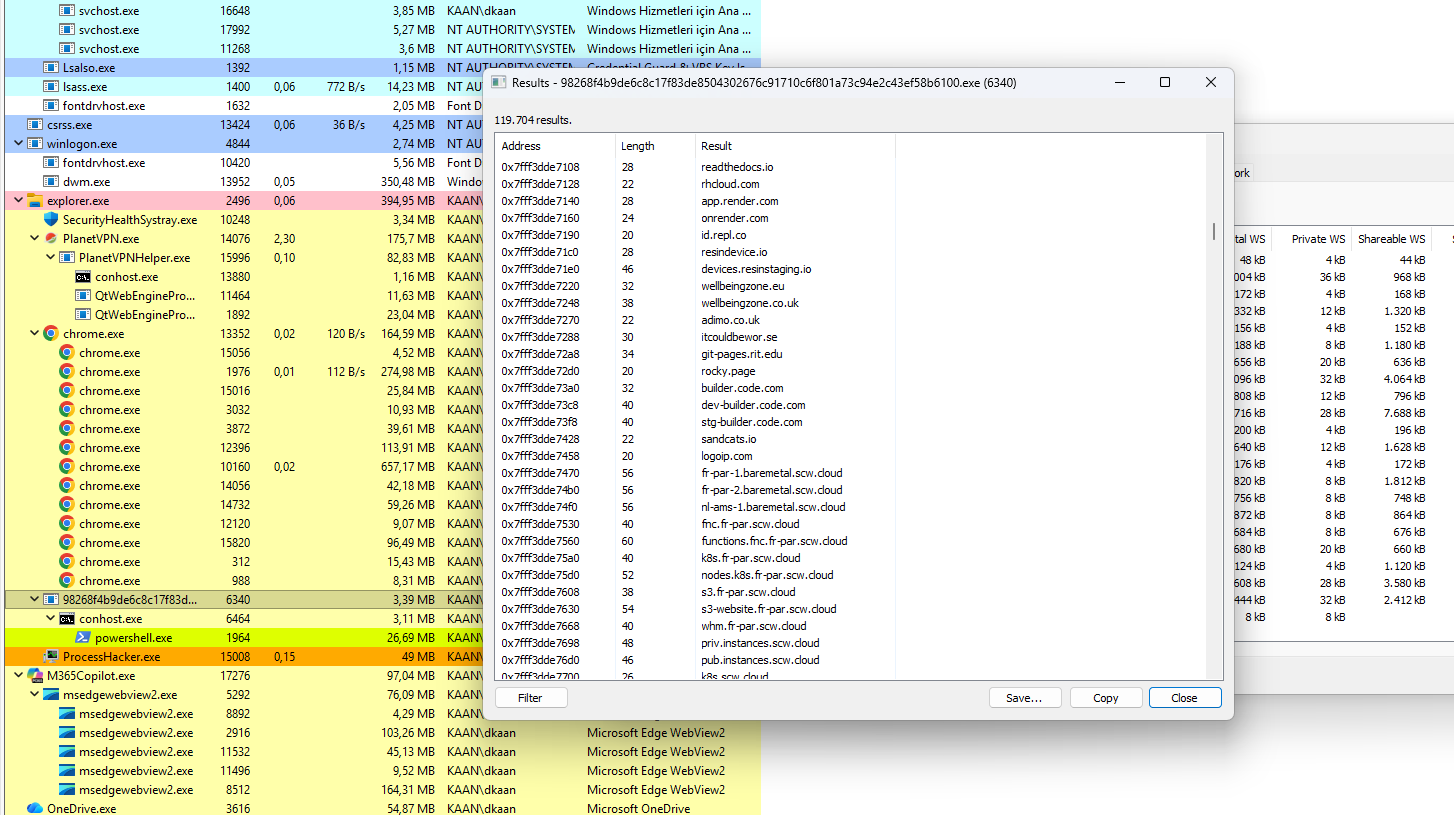
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1614 days ago
discord-crasher preview

discord-crasher

GitHubaftermathlabs/discord-crasher

Some bugs found via binary instrumentation and fuzzing
binary-analysisdynamic-analysis-sandboxingexploitation+5
2320 days ago
ipaforge preview

ipaforge

GitHubvighnesh91/ipaforge

Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…

binary-analysiscode-analysisios-security+6
119 days ago
CyberStrikeAI preview

CyberStrikeAI

GitHubaipentest/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+8
7.2k21h 43m ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
binary-analysiscommand-and-controldata-exfiltration+4
111 month ago
CVE-2026-31431 preview

CVE-2026-31431

GitHubexploiteoom/cve-2026-31431

Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
binary-analysisexploitationexploit-frameworks+2
25 months ago
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
binary-analysiscommand-and-controlexploitation+4
461 month ago
AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis preview

AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis

GitHubkaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis

Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
binary-analysiscommand-and-controldata-exfiltration+2
31 month ago
ghostdebug preview

ghostdebug

GitHubvollragm/ghostdebug

Debugger utilizing stealth hooks to hide from debugger detection
binary-analysisdebuggersdefensive-tools+1
231 month ago
class-dump preview

class-dump

GitHubnygard/class-dump

Generate Objective-C headers from Mach-O files.

binary-analysisios-securityreverse-engineering+1
3.6k7 years ago
ipsw preview

ipsw

GitHubblacktop/ipsw

iOS/macOS Research Swiss Army Knife

ai-assisted-reversingbinary-analysisdebuggers+9
3.8k6h 29m ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
binary-analysiscommand-and-controldata-exfiltration+6
51 month ago
bochs_linux_kernel_debugging preview

bochs_linux_kernel_debugging

GitHubtherealdreg/bochs_linux_kernel_debugging

Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)

binary-analysisdebuggerseducation+1
333 years ago
dissect.cobaltstrike preview

dissect.cobaltstrike

GitHubfox-it/dissect.cobaltstrike

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

binary-analysiscommand-and-controldigital-forensics+4
1984 days ago
scare preview

scare

GitHubnetspooky/scare

A multi-arch assembly REPL and emulator for your command line.
binary-analysisdebuggersdynamic-analysis-sandboxing+4
3121 year ago
ghidrecomp preview

ghidrecomp

GitHubclearbluejar/ghidrecomp

Python Command-Line Ghidra Decompiler

binary-analysisreverse-engineeringstatic-code-analysis+1
1599 months ago
AgentTesla-Config-Extractor preview

AgentTesla-Config-Extractor

GitHubembee-research/agenttesla-config-extractor

Config extractor for AgentTesla - Discord/Telegram Variant

binary-analysiscommand-and-controlioc-management+4
33 years ago
Previous1234Next