Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

CTF framework and exploit development library

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

.NET, PE, & Raw Shellcode Packer/Loader Written in Nim

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…

PE loader with various shellcode injection techniques

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.

Python based tool for generating Shellcode from PIC C

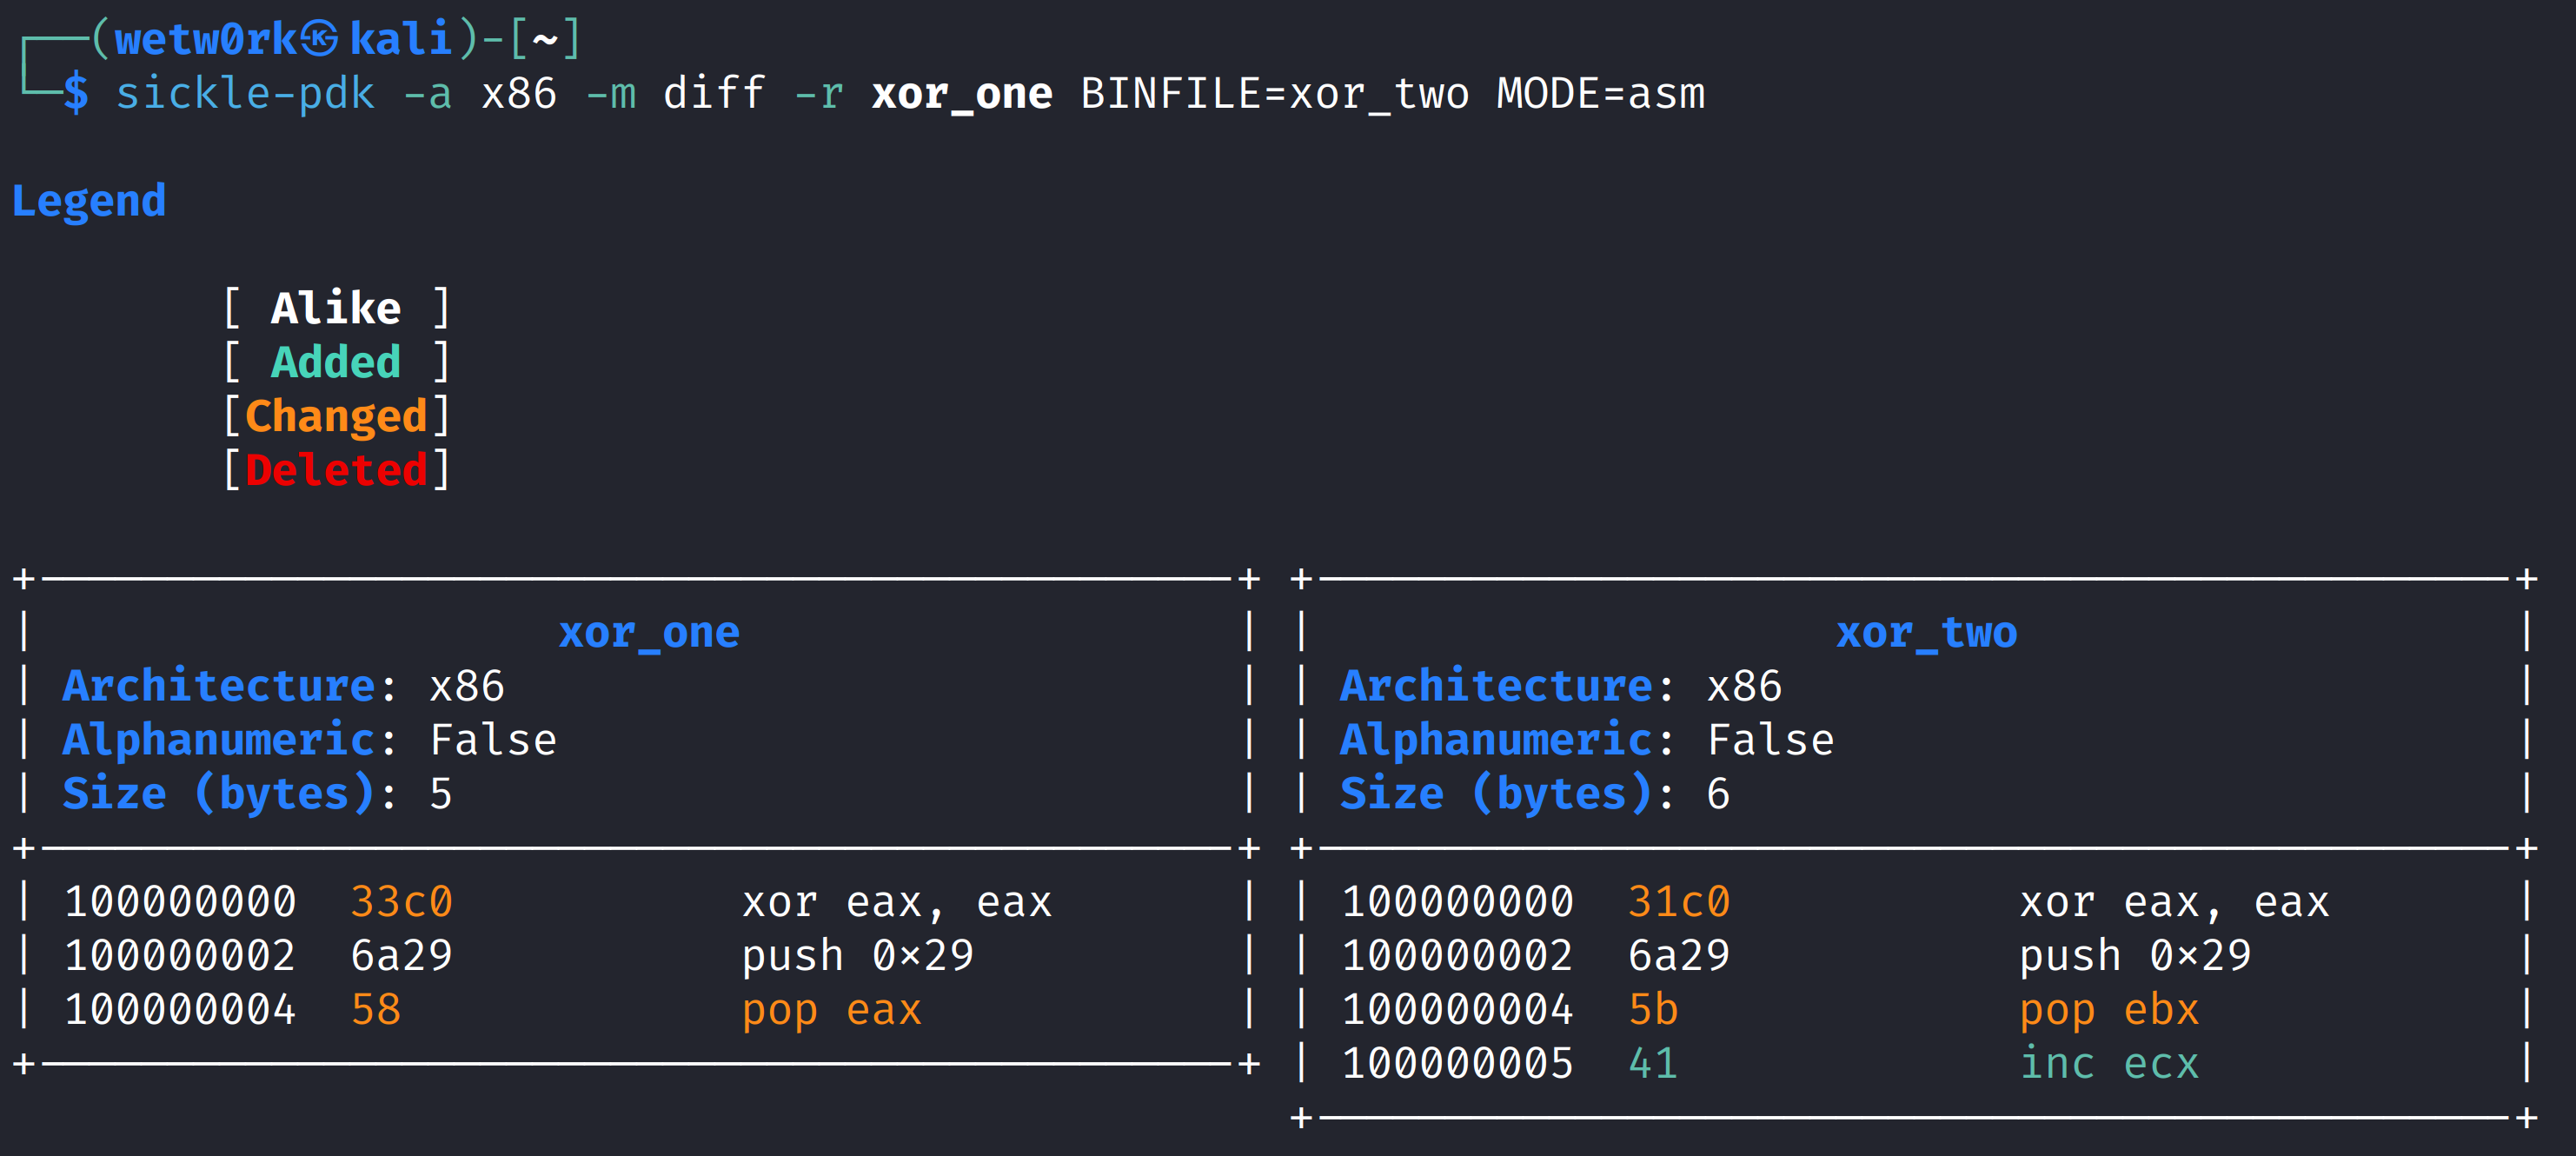
Sickle - Payload Development Kit

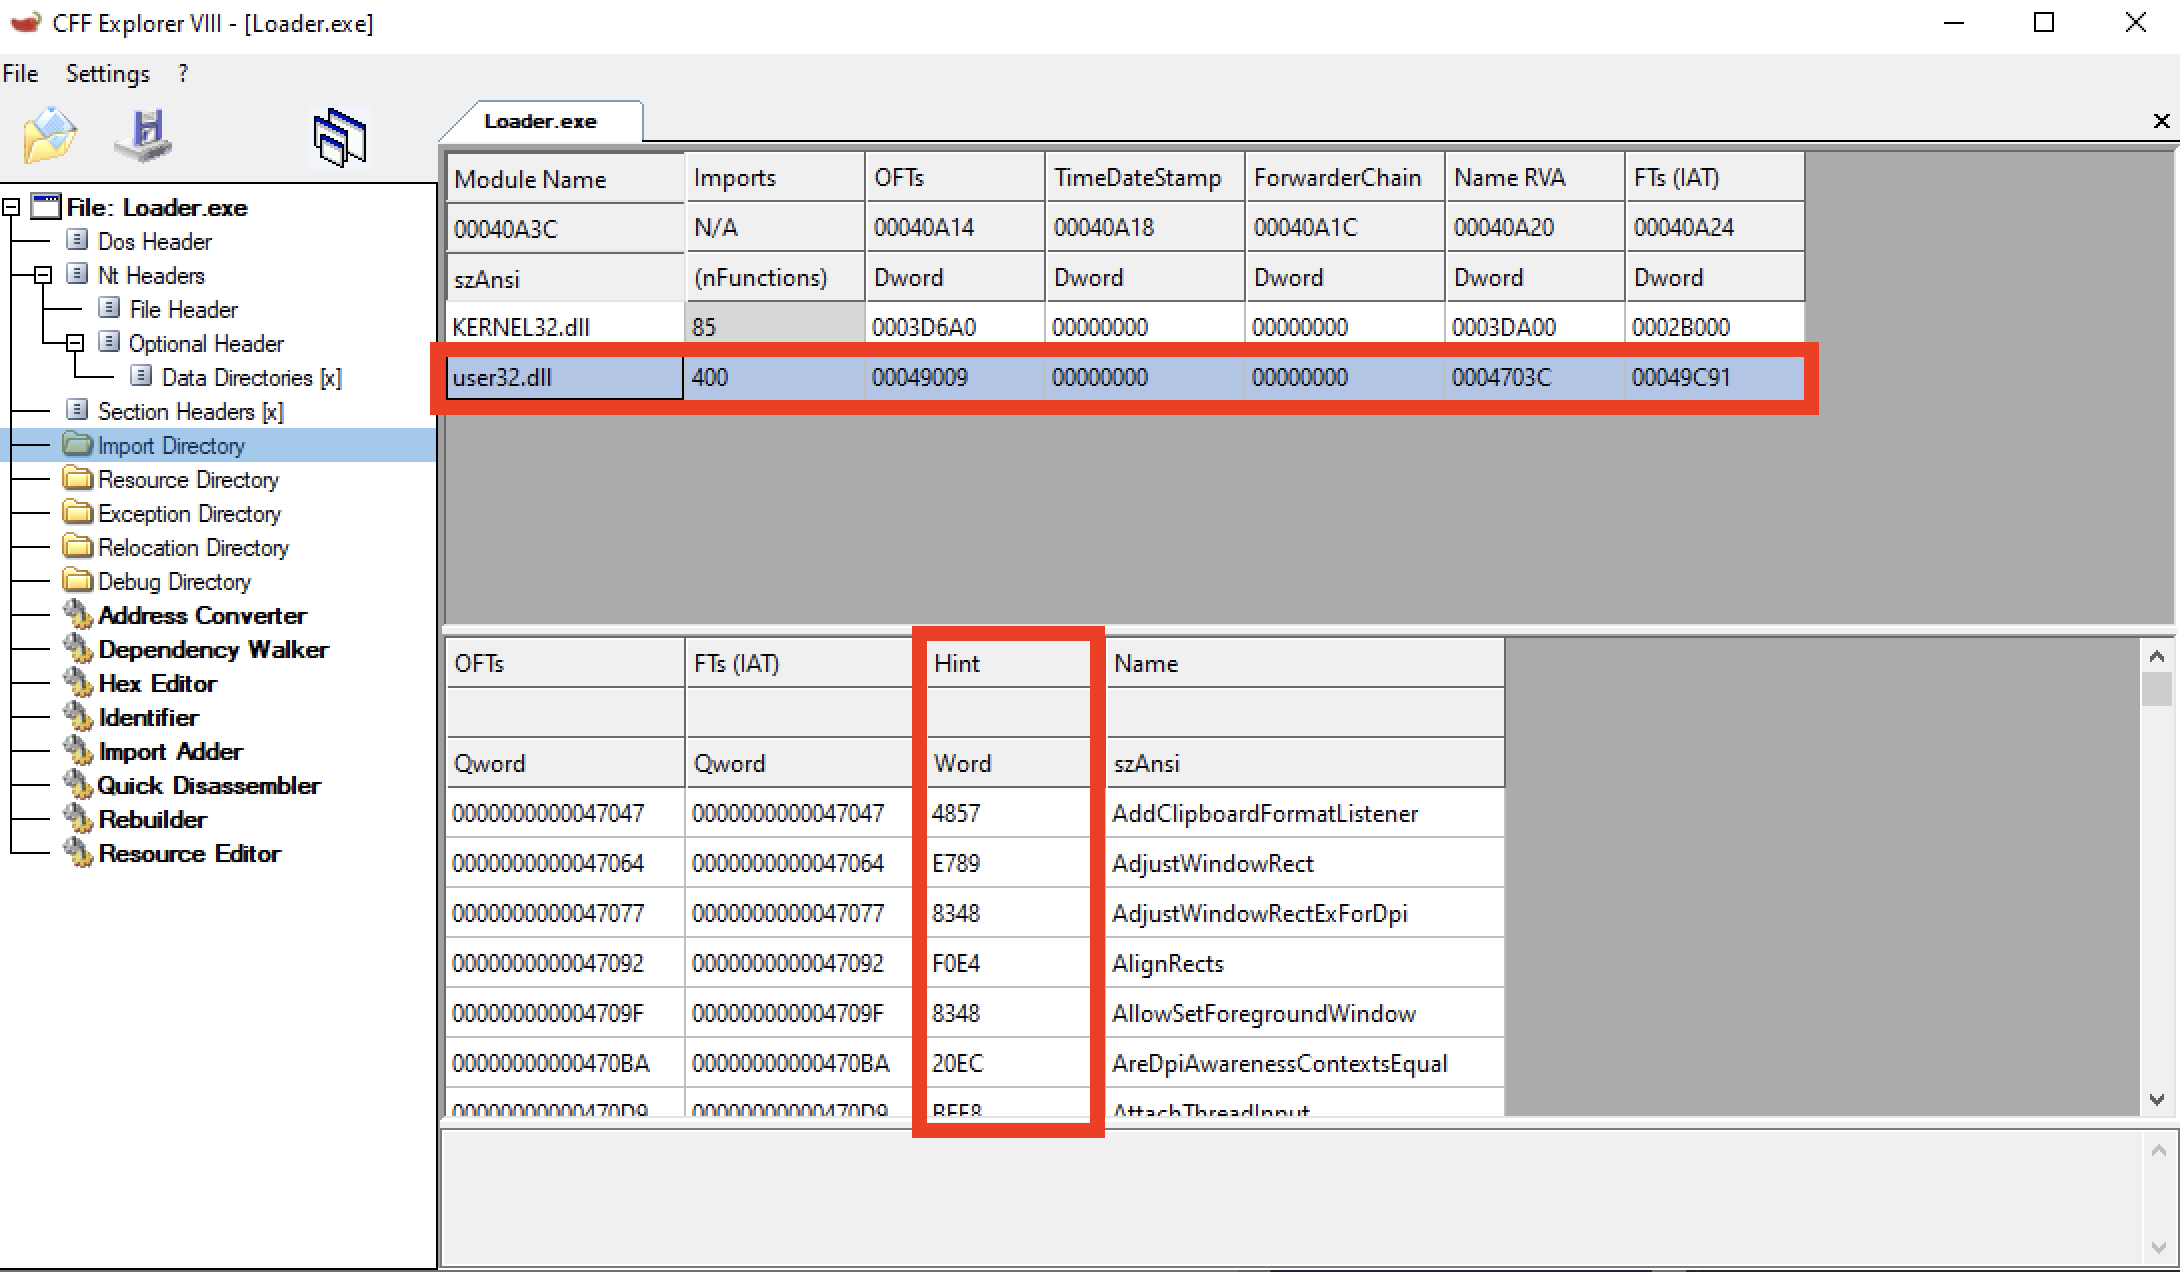
A PoC project for embedding shellcode to Hint/Name Table

An architecture-agnostic ELF file flattener for shellcode

Proxies sensitive API calls from shellcode to artifacts for CET-compatible clean call stacks, enabling stealthy payload execution and call stack…