
ReparcelBug2
 michalbednarski/reparcelbug2
Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…
android-securitybinary-analysisexploitation+3
125
michalbednarski/reparcelbug2Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…
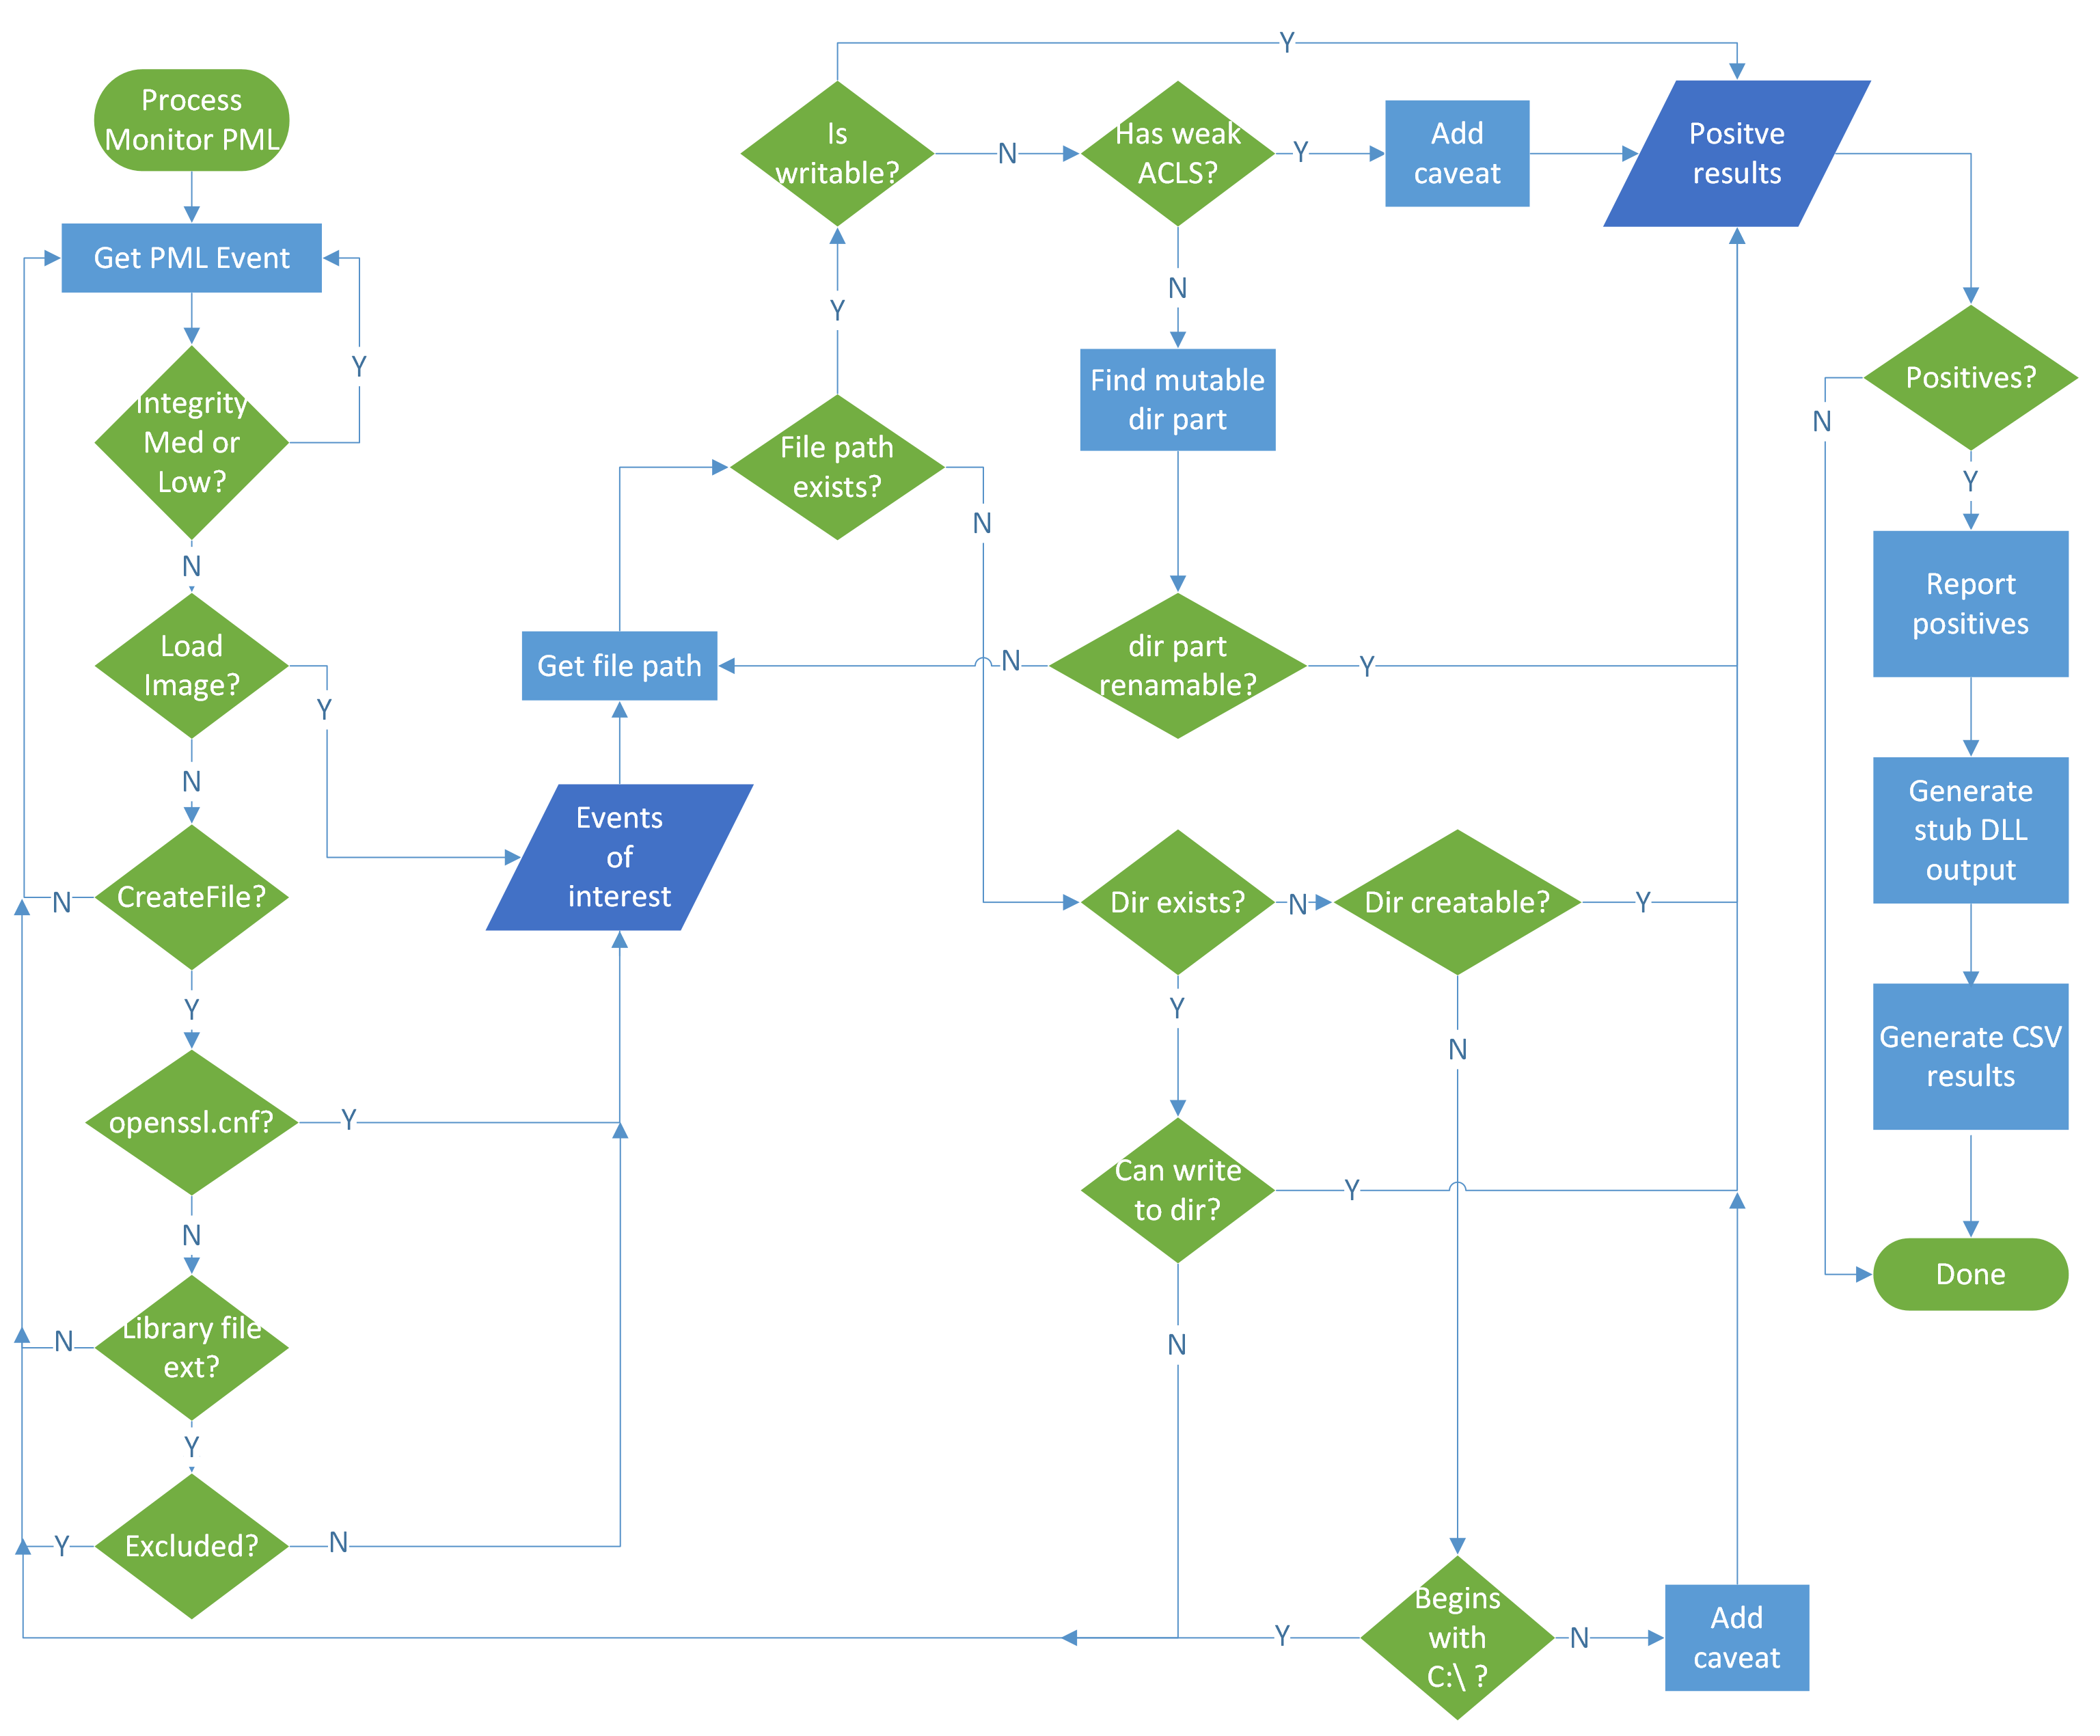 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 fzrsllasher/cve-2026-12166_cve-2026-12167_cve-2026-12168
Technical advisory detailing three local privilege escalation vulnerabilities (CVE-2026-12166/7/8) in the Little Orbit GFAC kernel driver, including…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
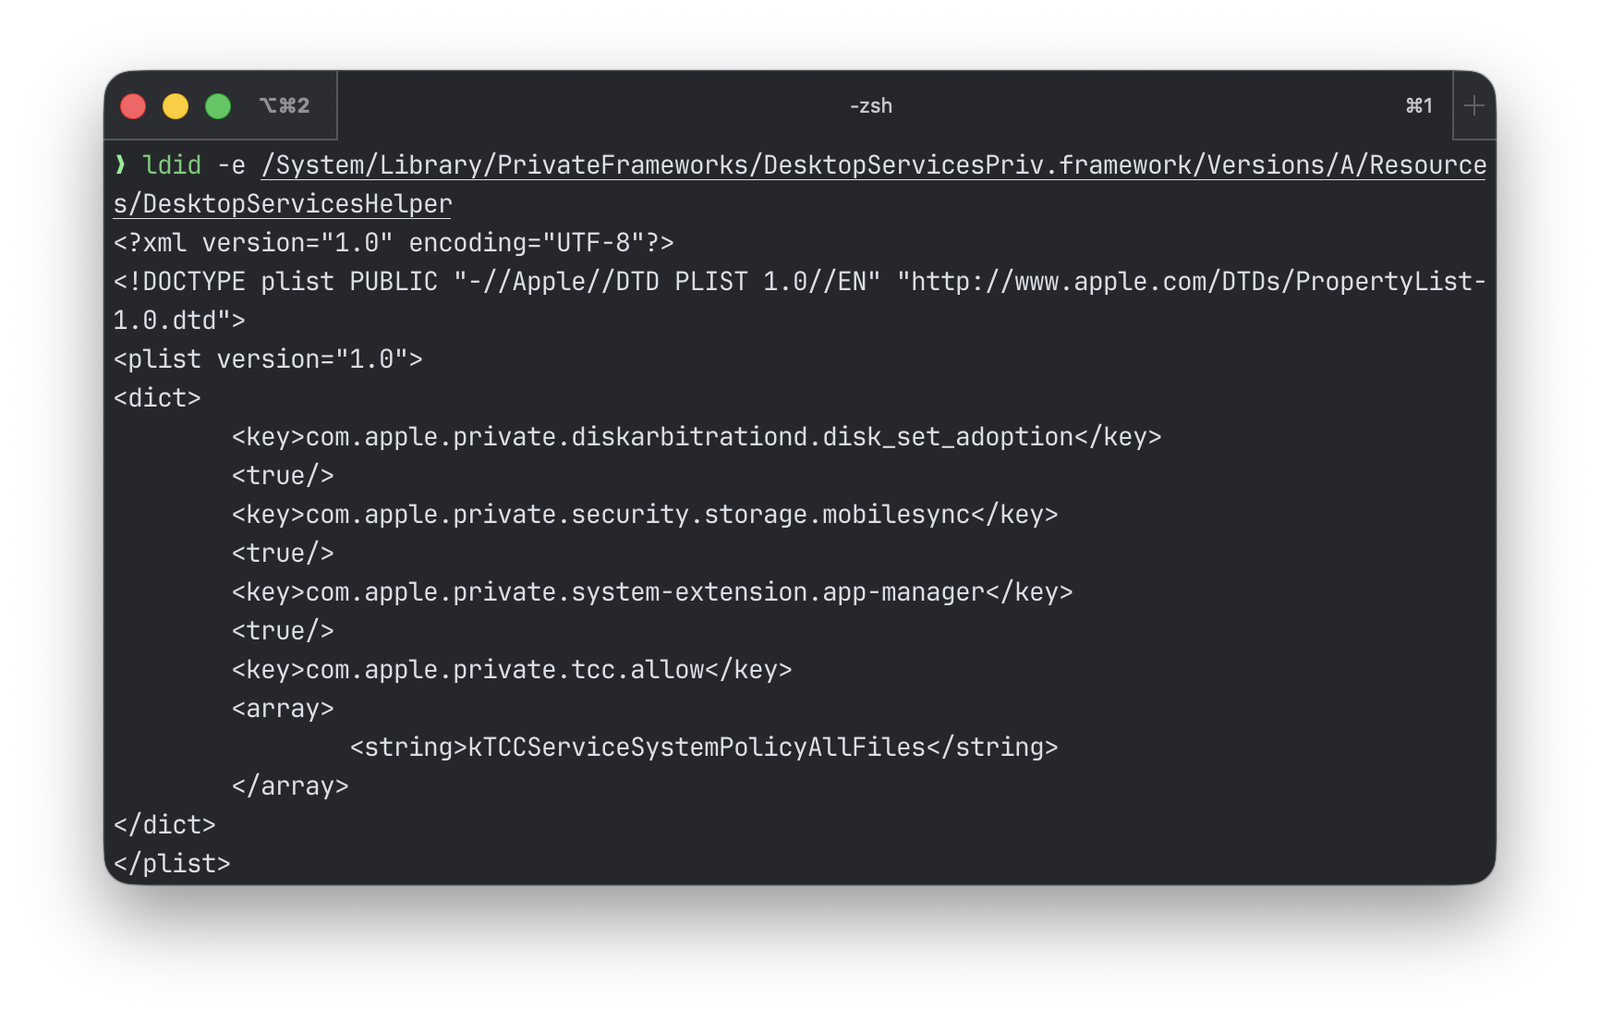 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
 kikiuuw/cve-2025-68921
Analyze and demonstrate the local privilege escalation vulnerability (CVE-2025-68921) in Nahimic audio software on gaming laptops, with automated…
 webraybtl/cve-2022-24934
Technical analysis and proof-of-concept exploit for CVE-2022-24934, a privilege escalation vulnerability in WPS Office's update mechanism allowing…
 abdelkabirouadoukou/cve-2026-31431-analysis-and-fix
In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…
 d7ead/cve-2026-38765
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 perlun/sudo-1.8.3p1-patched
Custom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied
 nam3lum/msi-central_privesc
CVE-2022-38532 - Local Privilege Escalation vulnerability in MSI Center Application
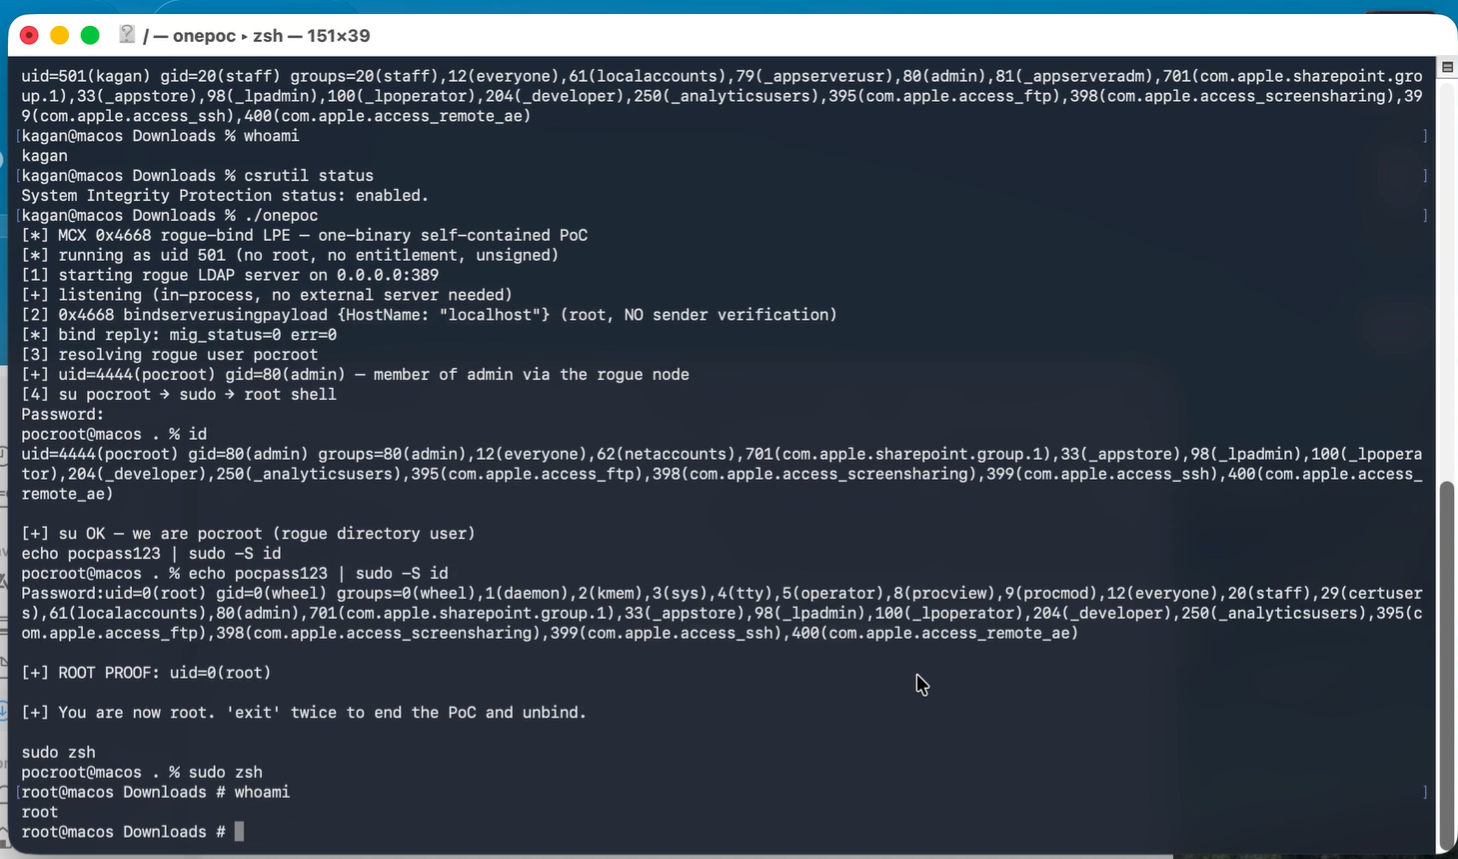 0xblackash/cve-2026-43786
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root…
 tamatahyt/cve-2017-8481
Exploit code for CVE-2017-8481, a Windows privilege escalation vulnerability.