

unblob
 onekey-sec/unblob
Extract files from any kind of container formats
binary-analysisdata-recoveryembedded-systems-security+3
onekey-sec/unblobExtract files from any kind of container formats
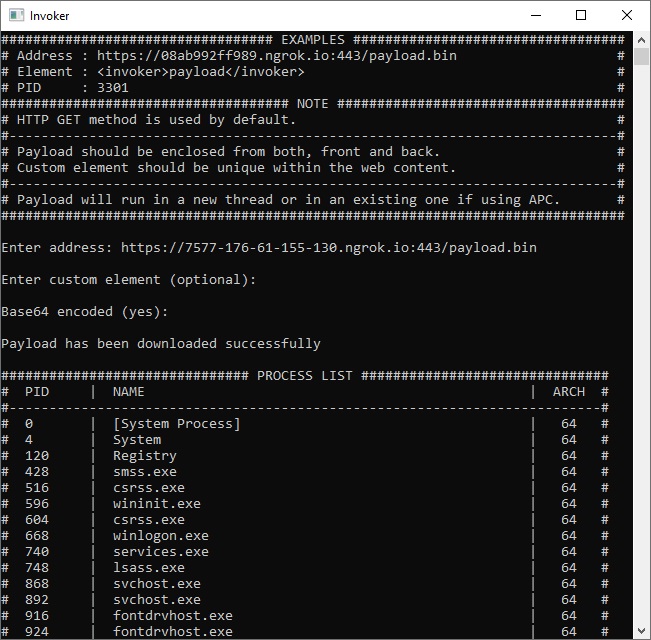 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
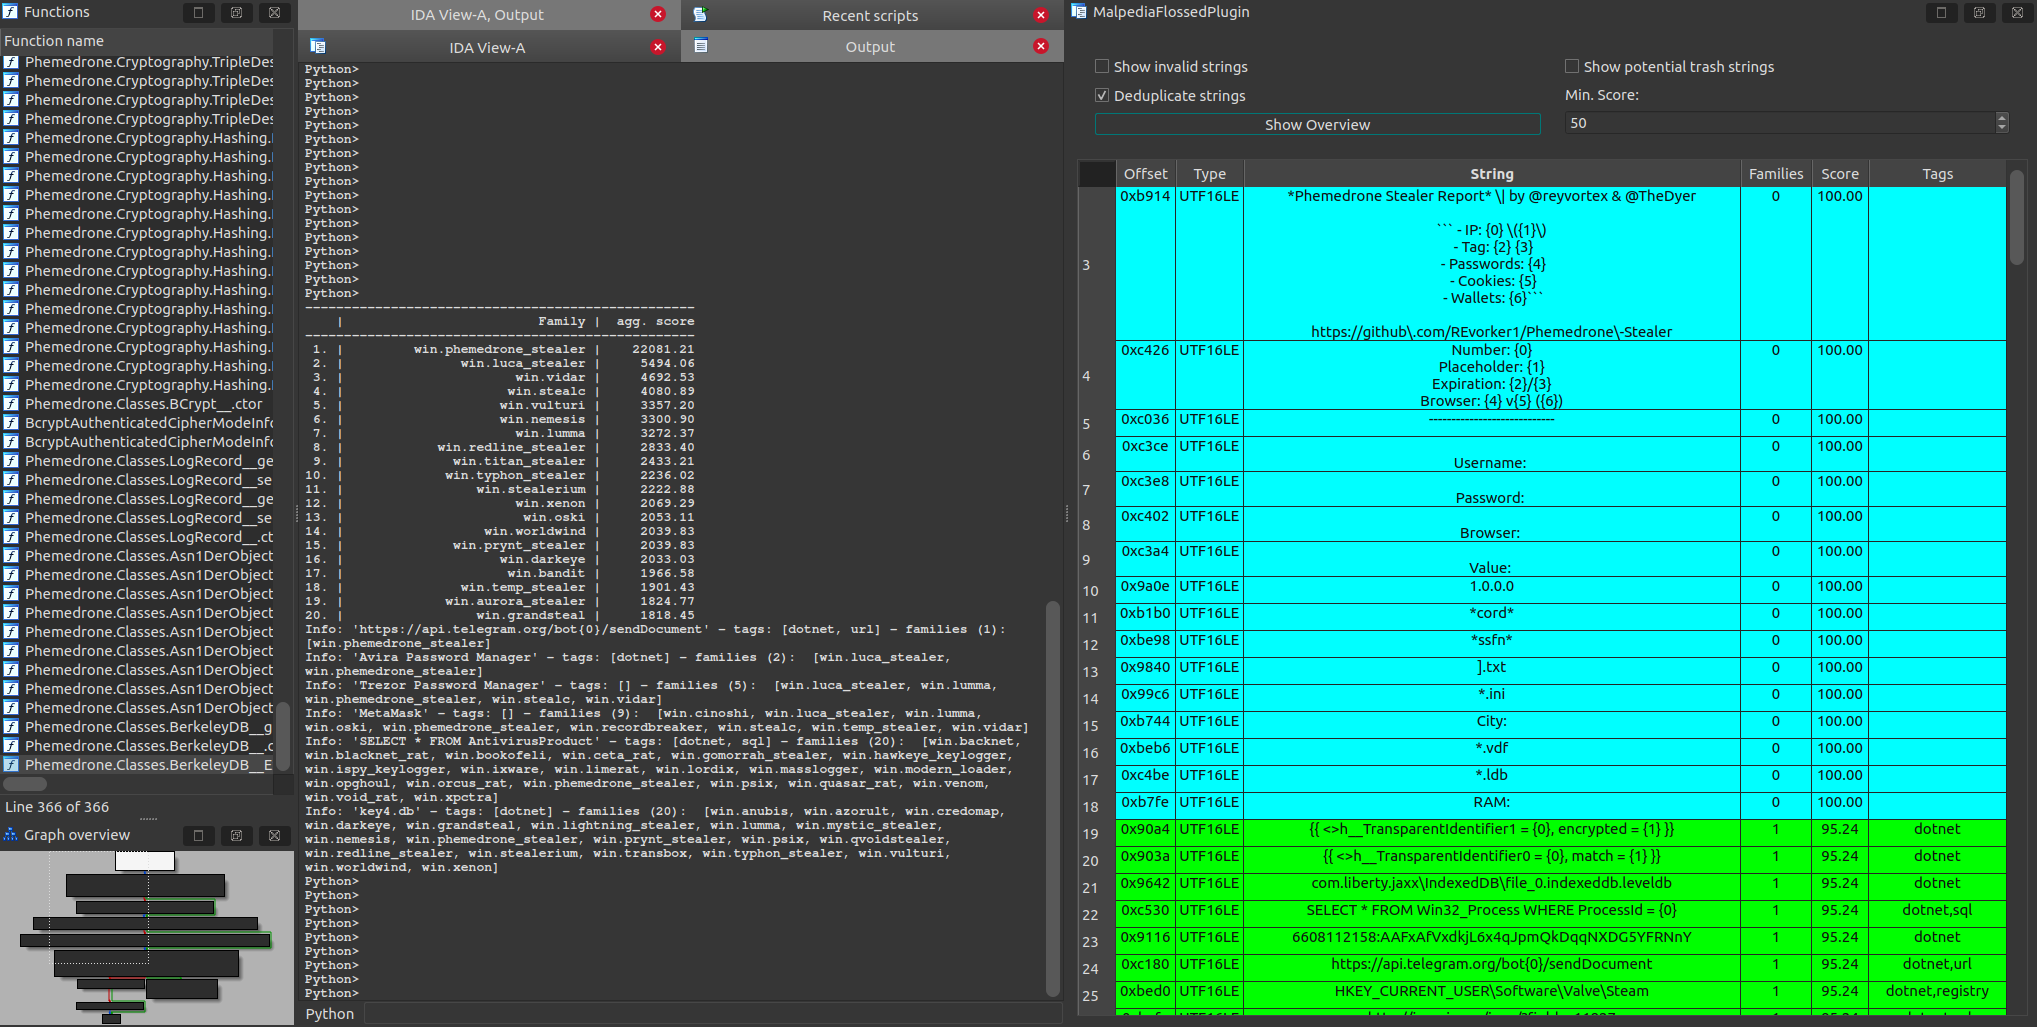 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 sneakynachos/cve-2026-74936-gc-potato
Reproduction of a WebAssembly use-after-free vulnerability in Mozilla's JavaScript engine, demonstrating a deterministic race condition and providing…
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 trailofbits/trailmark
Build and query a graph database representation of source code
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
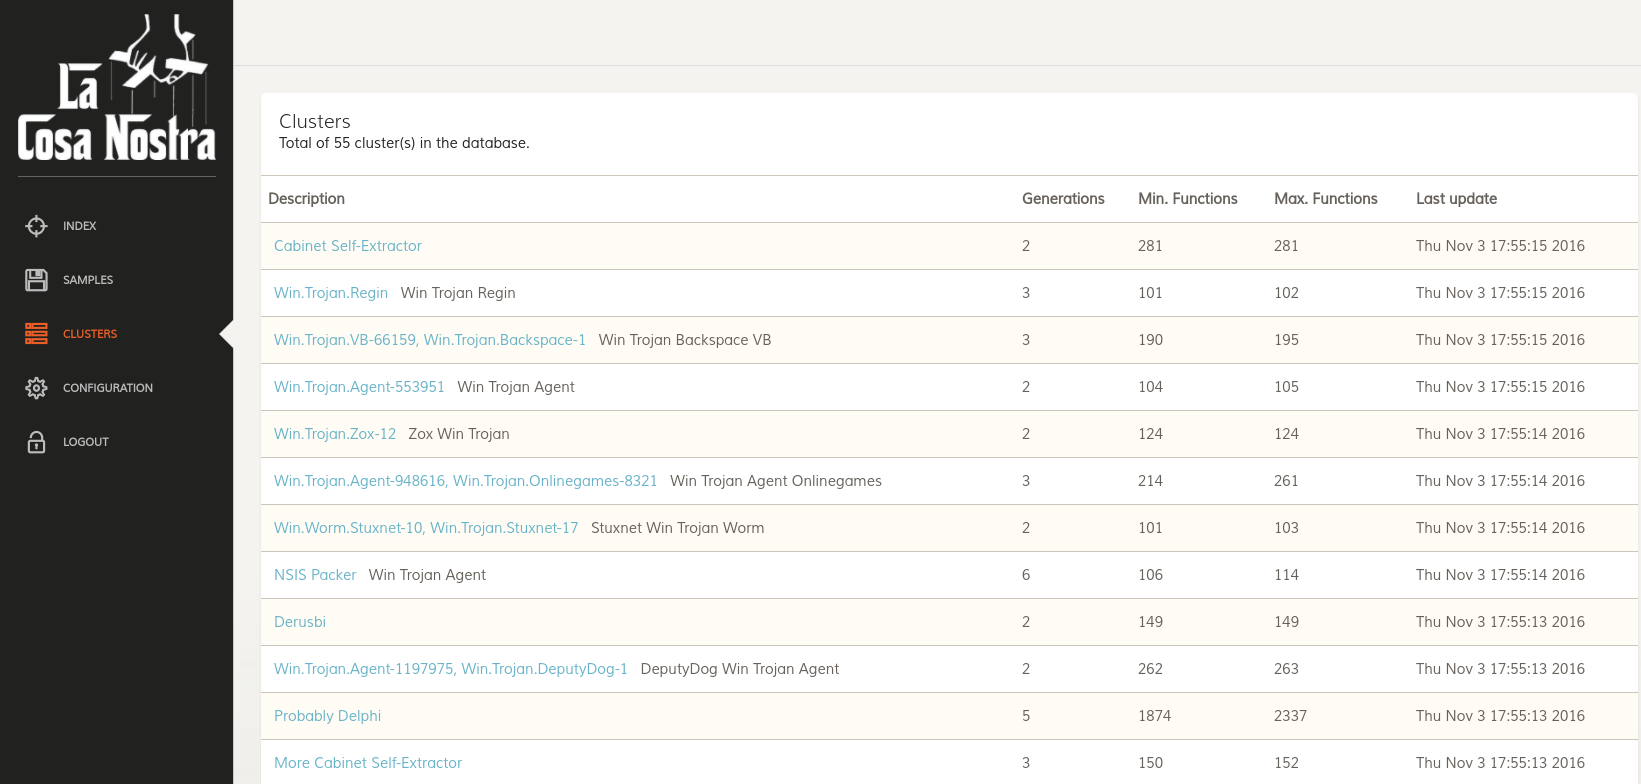 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 nccgroup/asafw
Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]