CVE-2026-42978-PoC-Research

CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…

CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…

Finding CVE-2022-3786 (openssl) with Mayhem

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

Executes at the silicon boundary

An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.

Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…

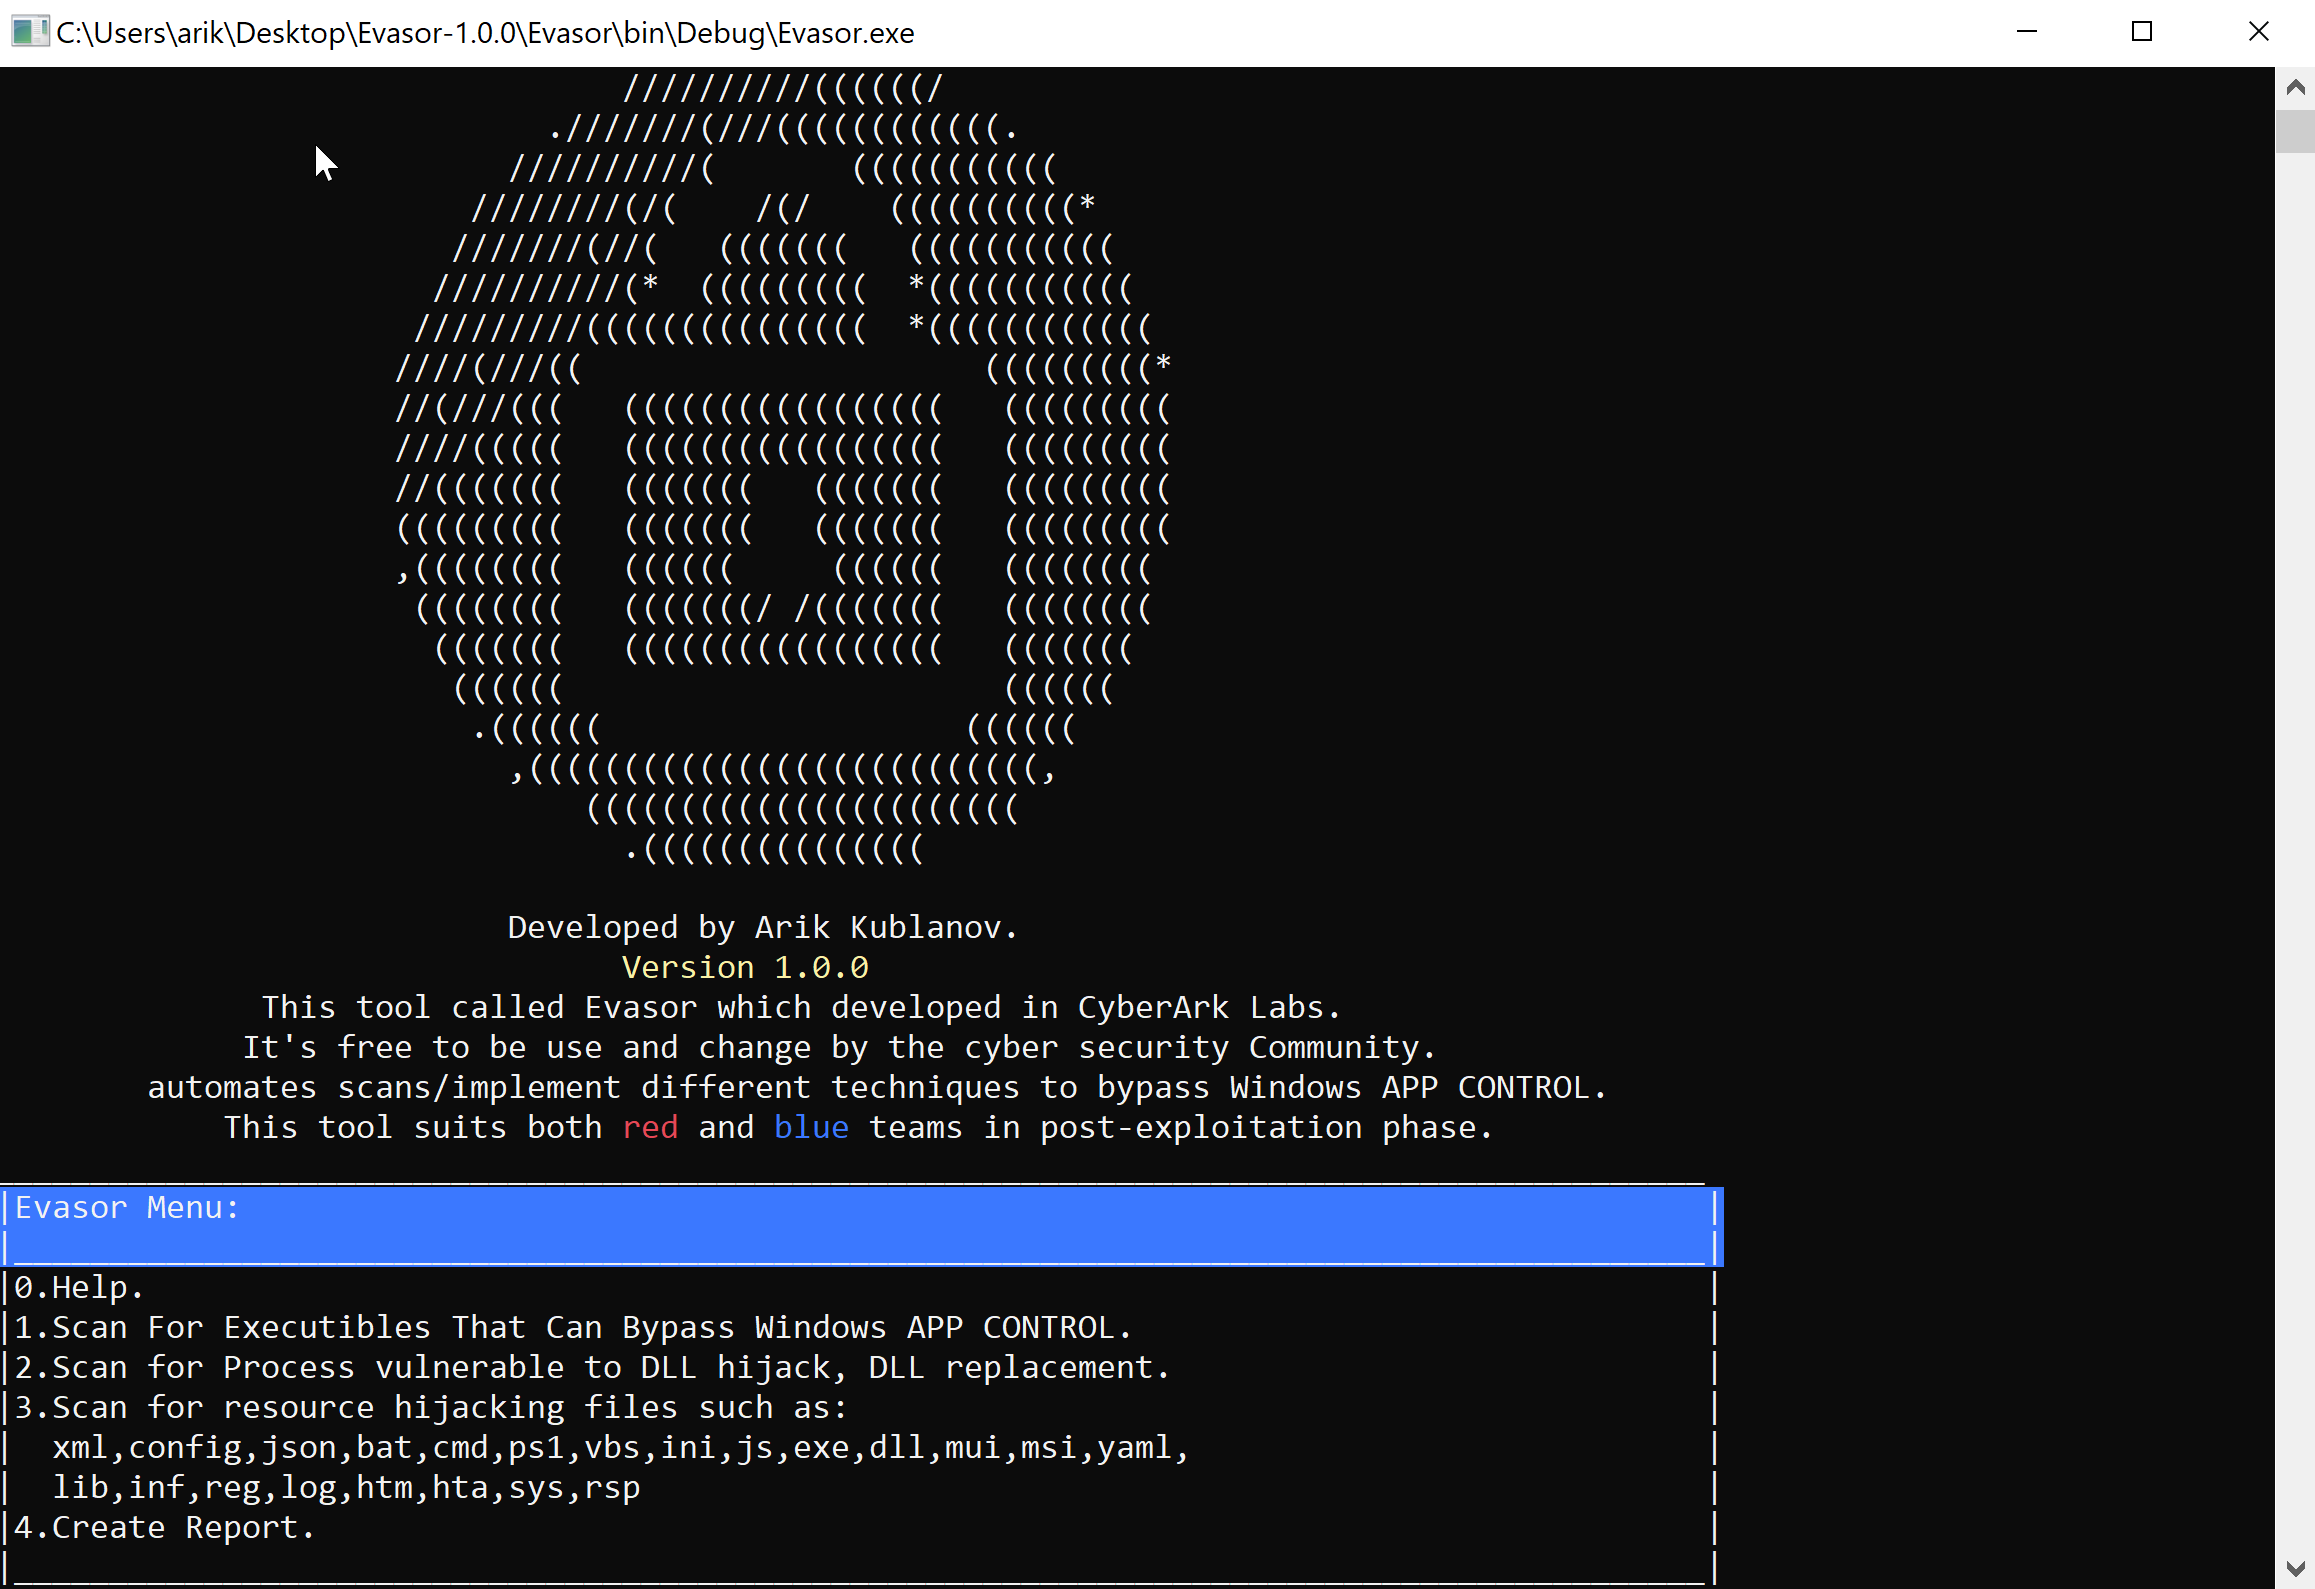
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies

Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…


Post-exploitation and evasion research toolkit for Linux.

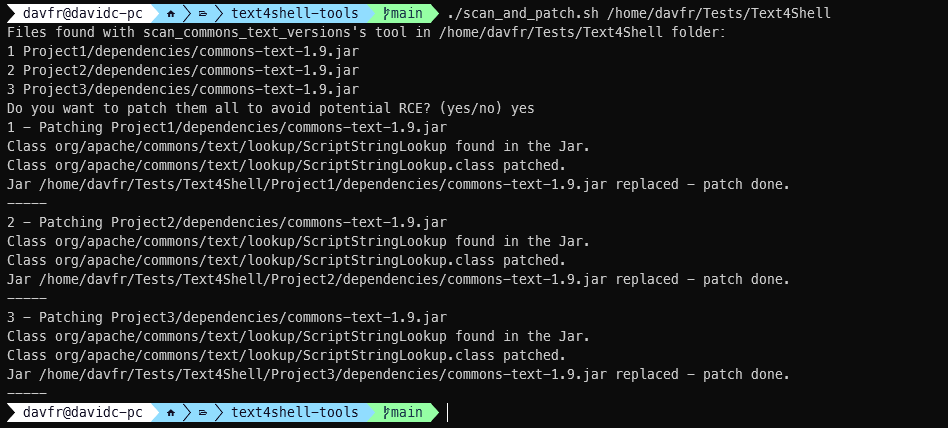
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…

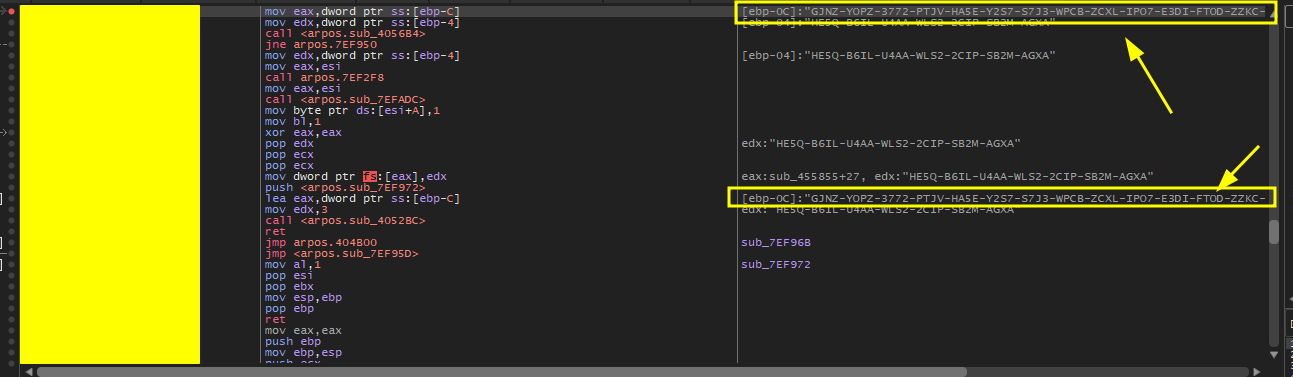
Demonstrates cleartext storage of license keys in memory in Abacre Restaurant POS, enabling license activation bypass via debugger and memory dump…

Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…

This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule

Injects code into ELF executables post-build

CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…

N-DAY VULNERABILITY RESEARCH (FROM PATCH TO EXPLOIT ANALYSIS OF CVE-2021-41081)