

RC4Decryption
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
37
weedhashpeddler/rc4decryptionAbuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 ergrelet/windiff
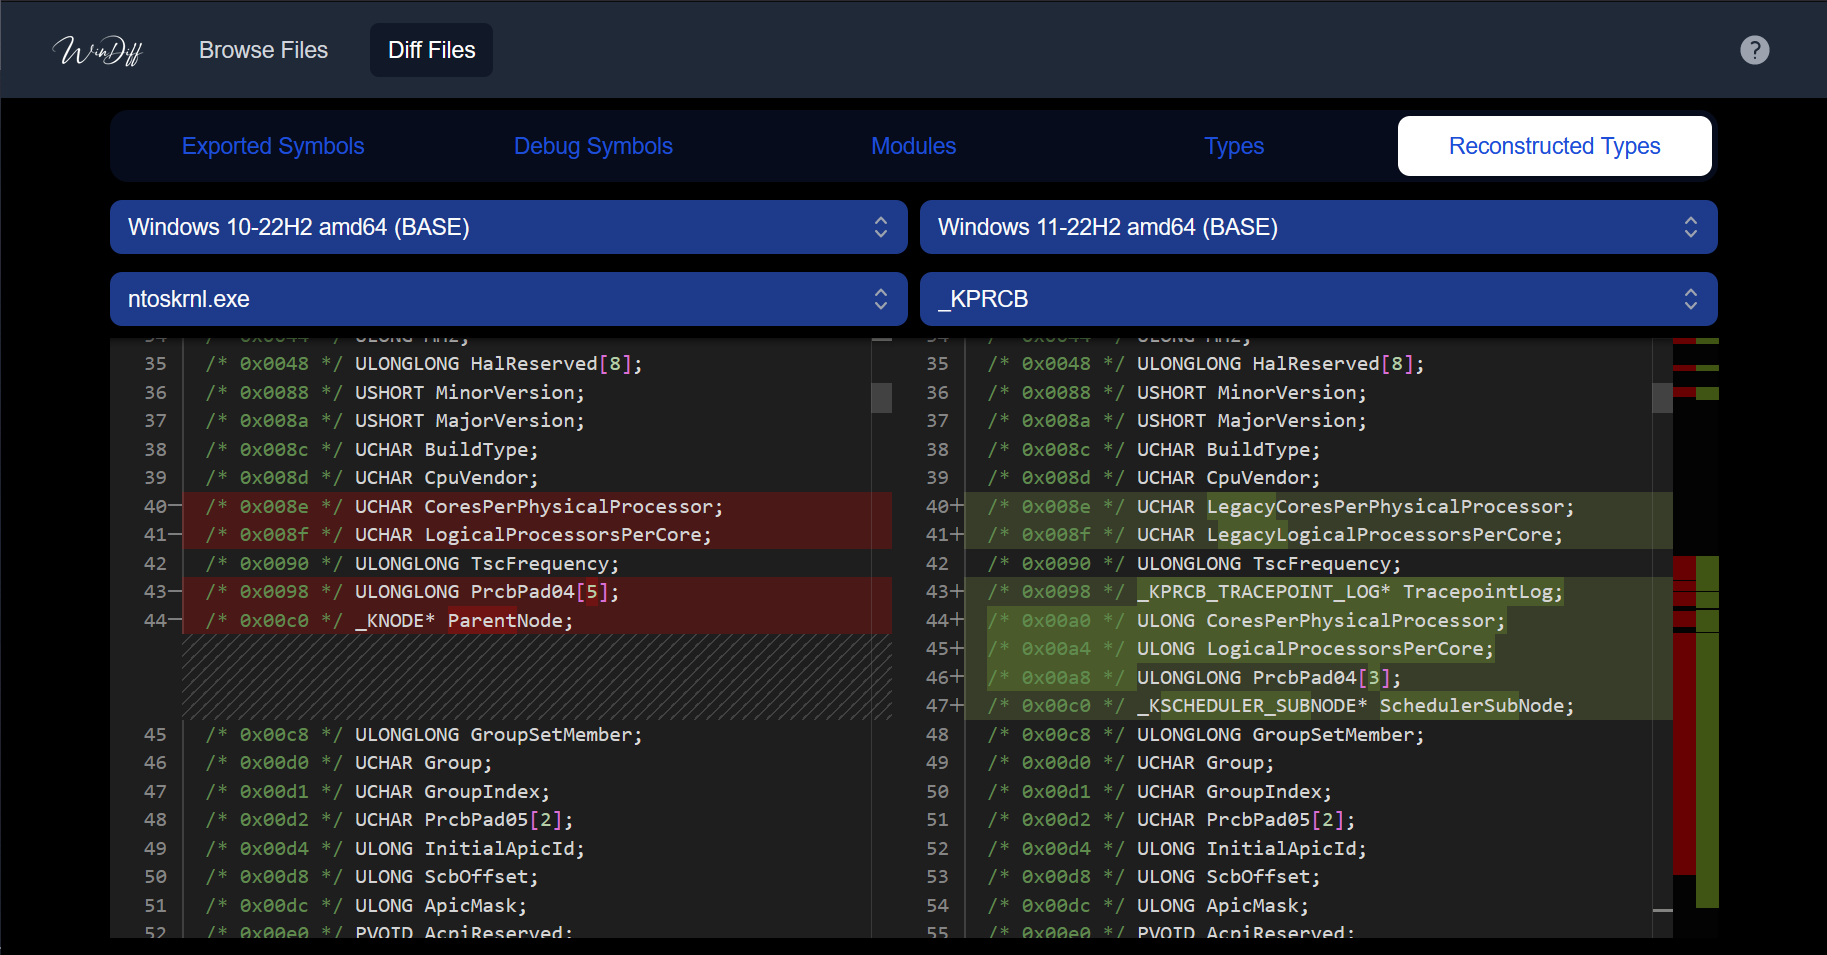
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 0vercl0k/cve-2021-24086
Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.