

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.6k1 day ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 darthton/blackbone
Windows memory hacking library
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
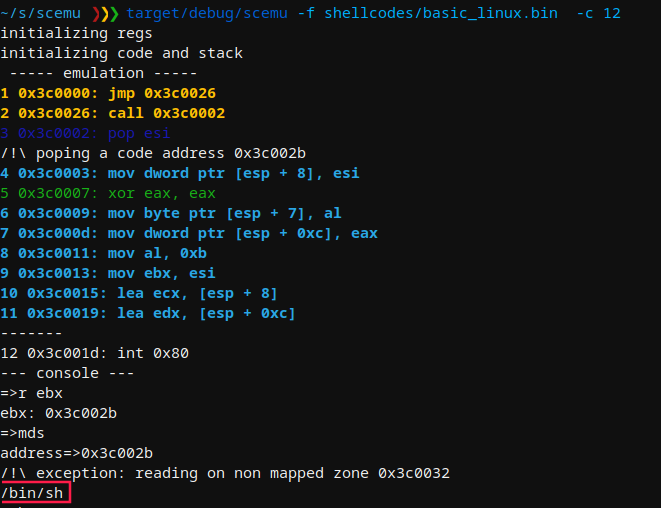 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
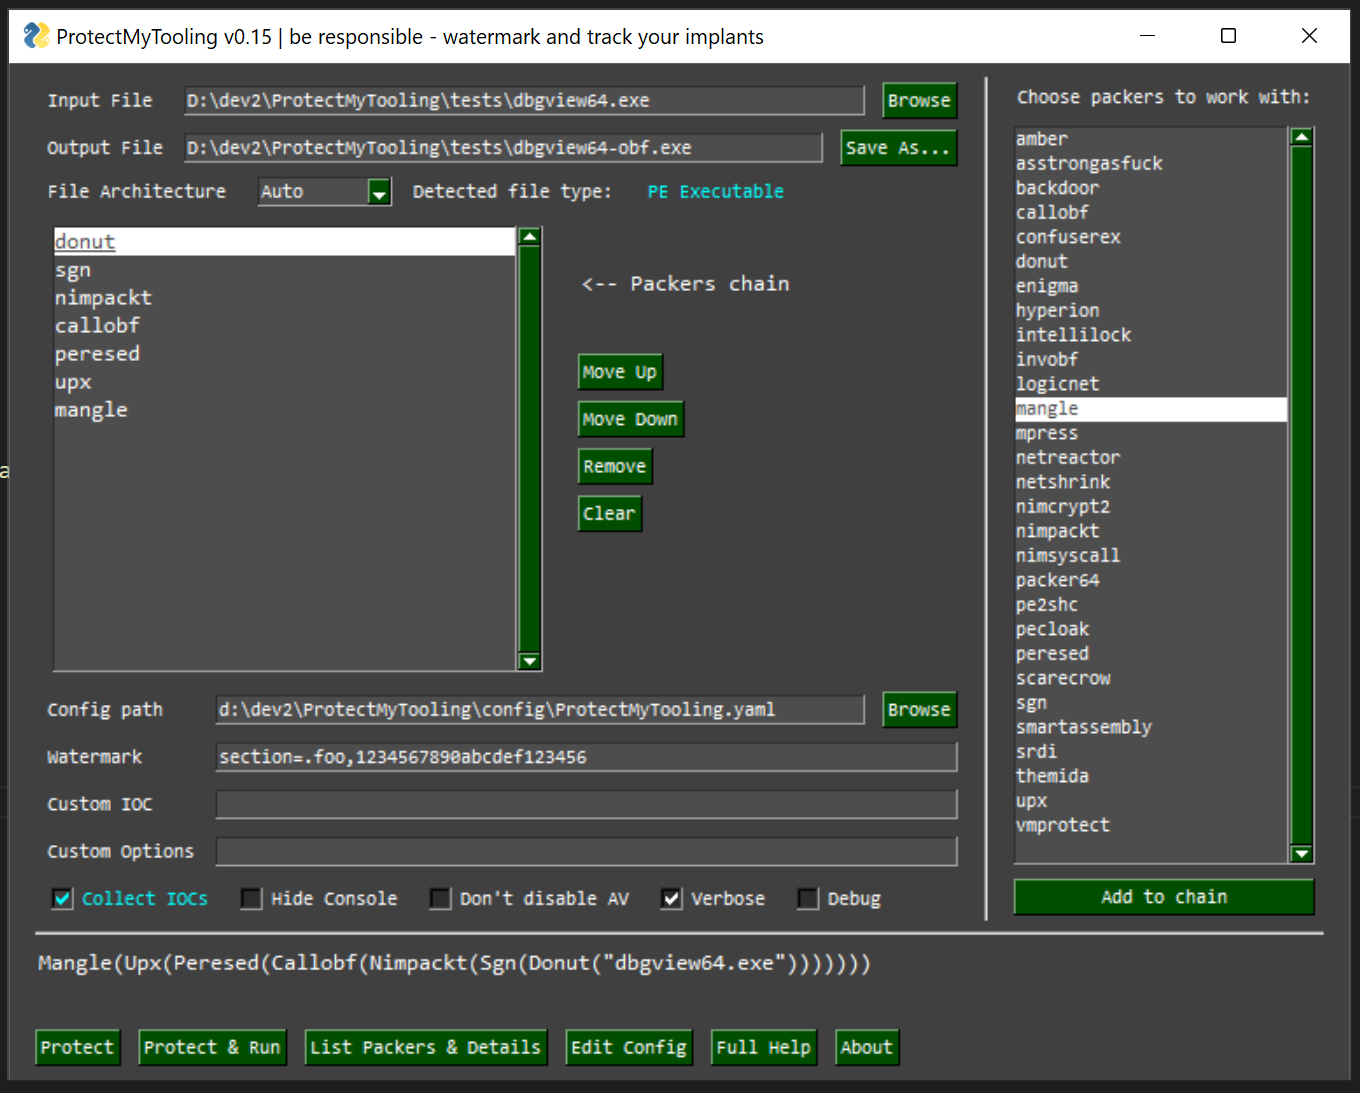 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
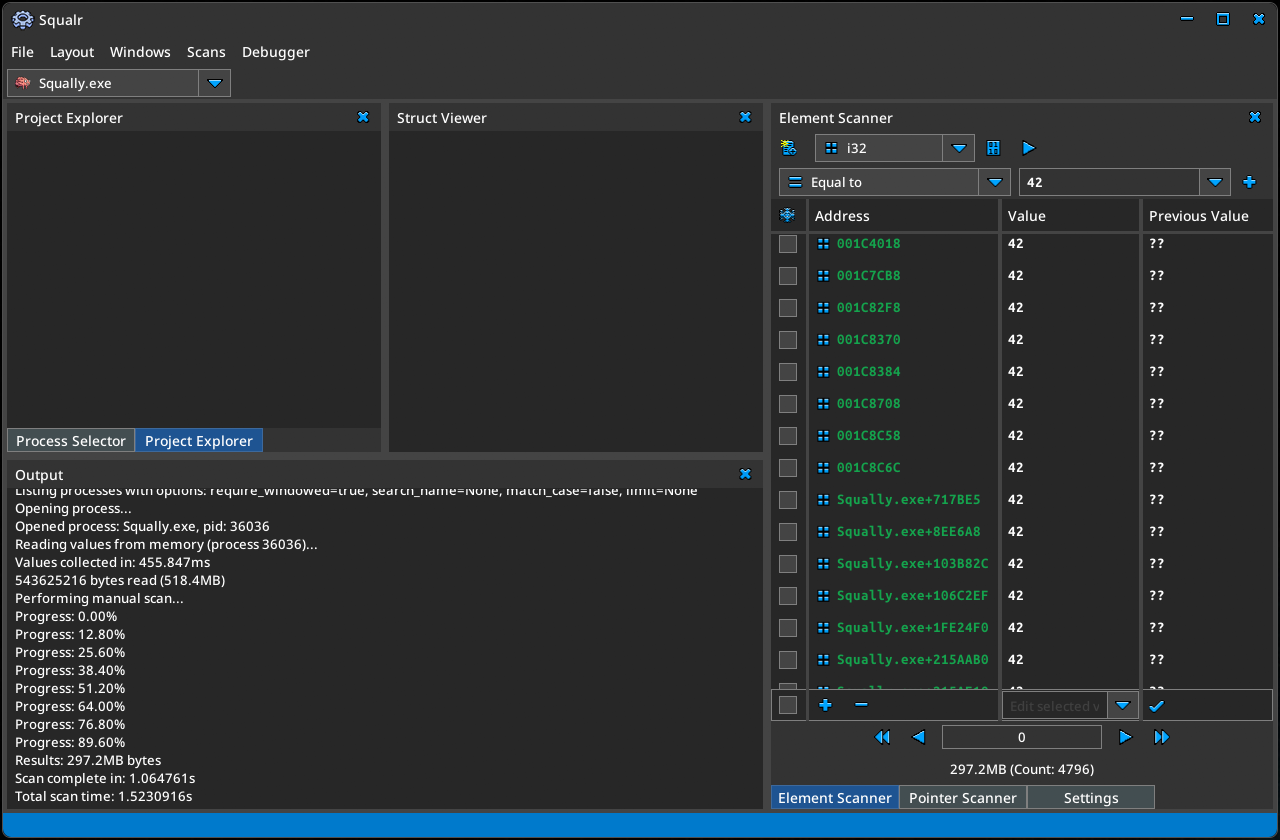 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
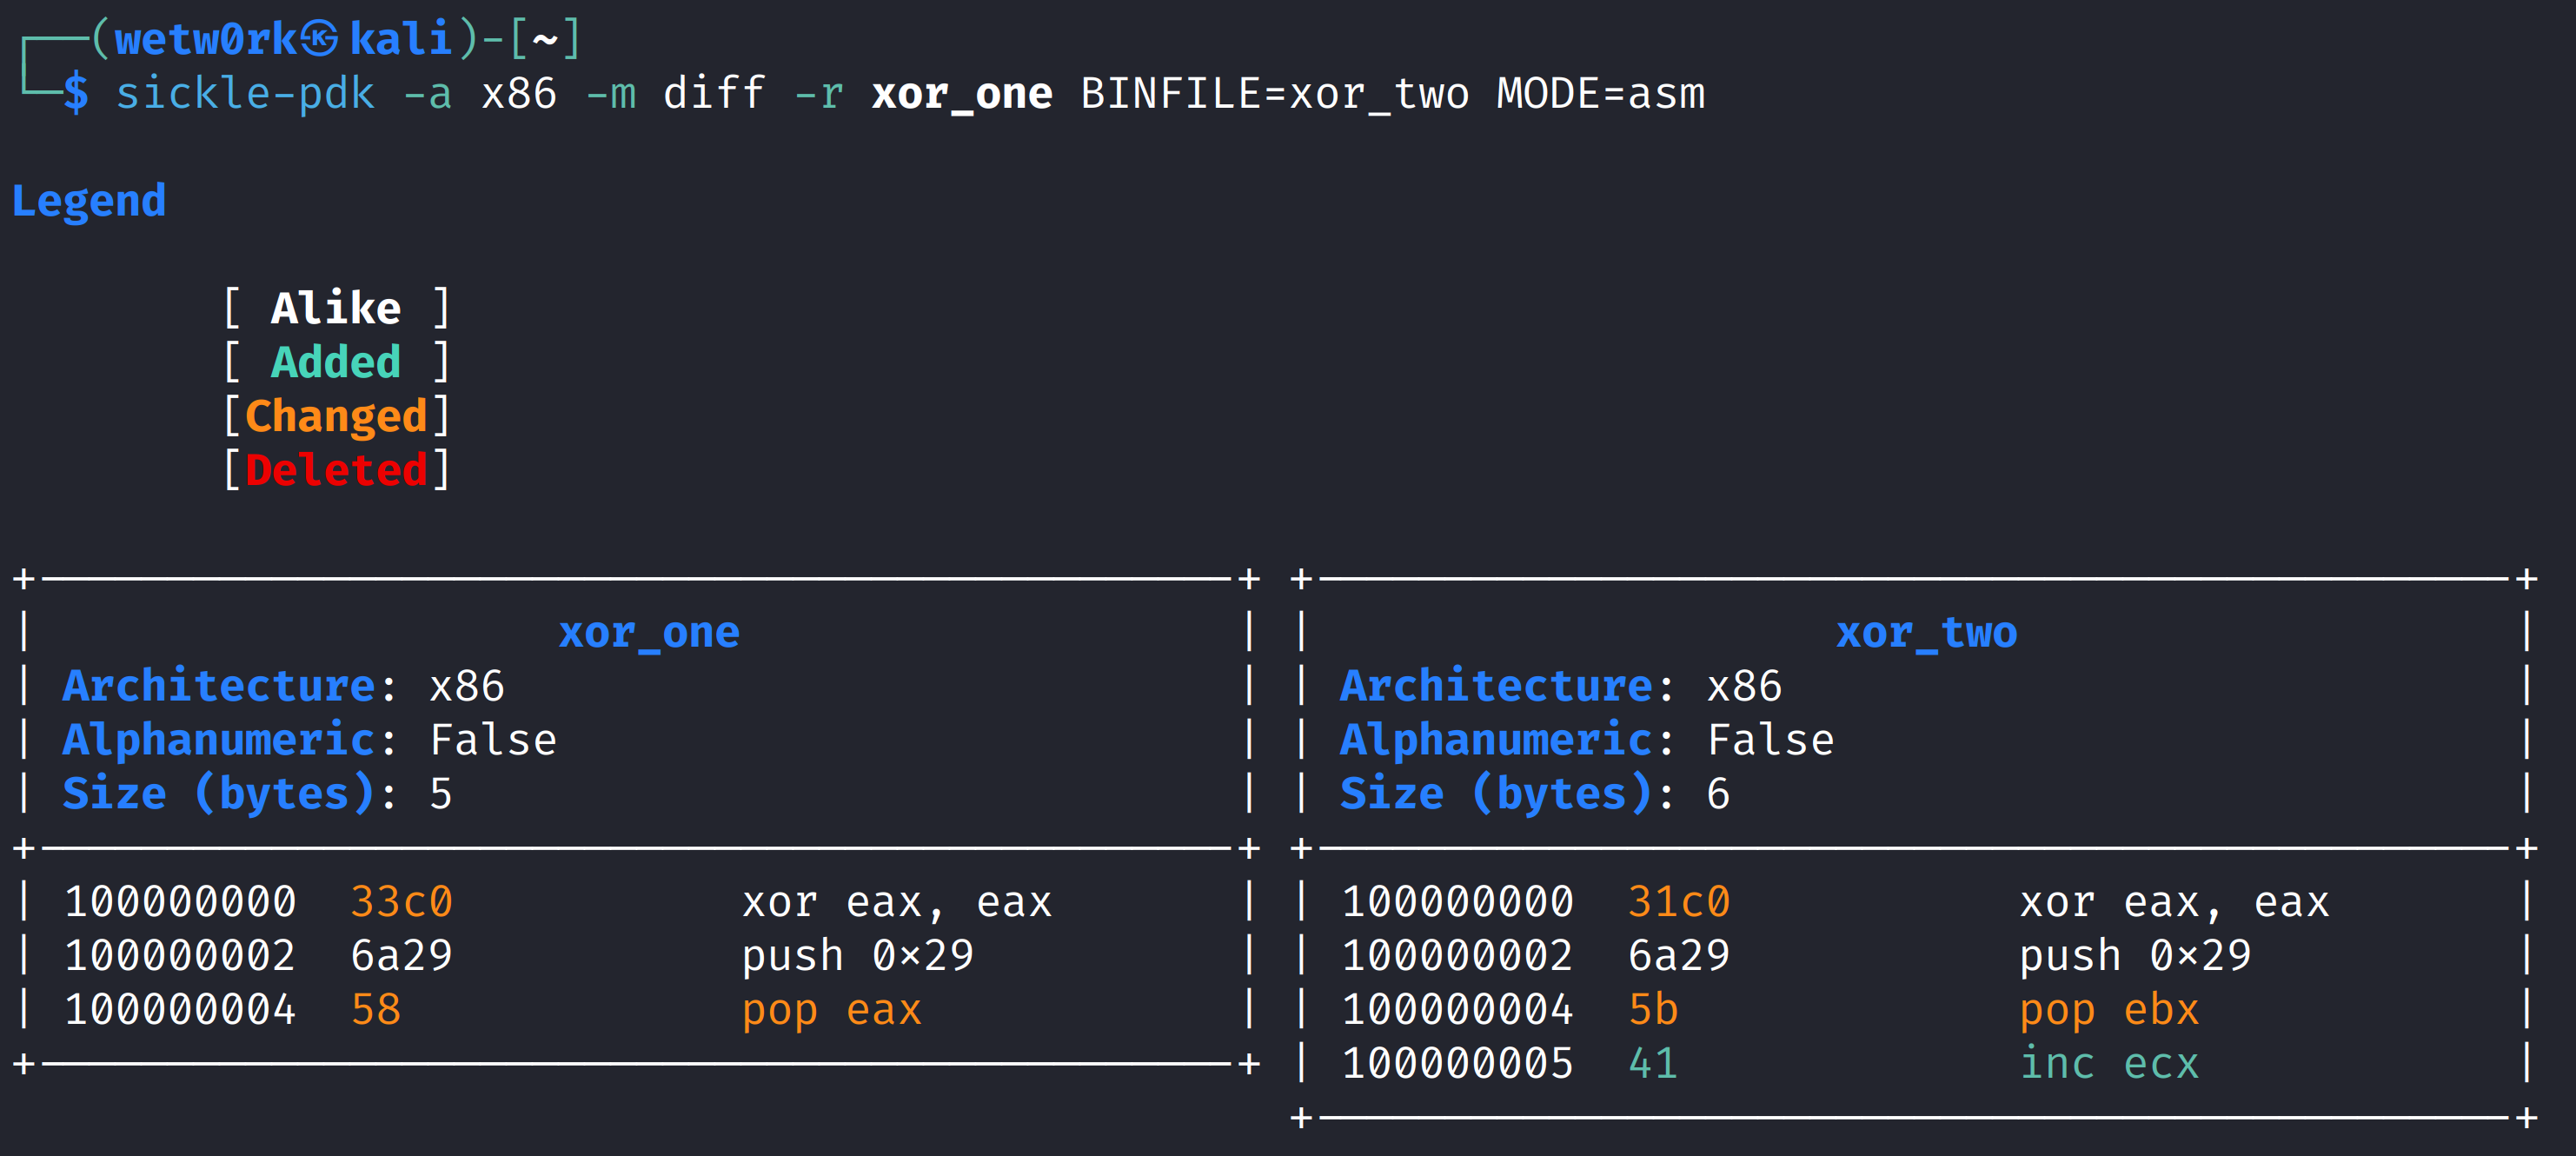 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.