

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
198
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
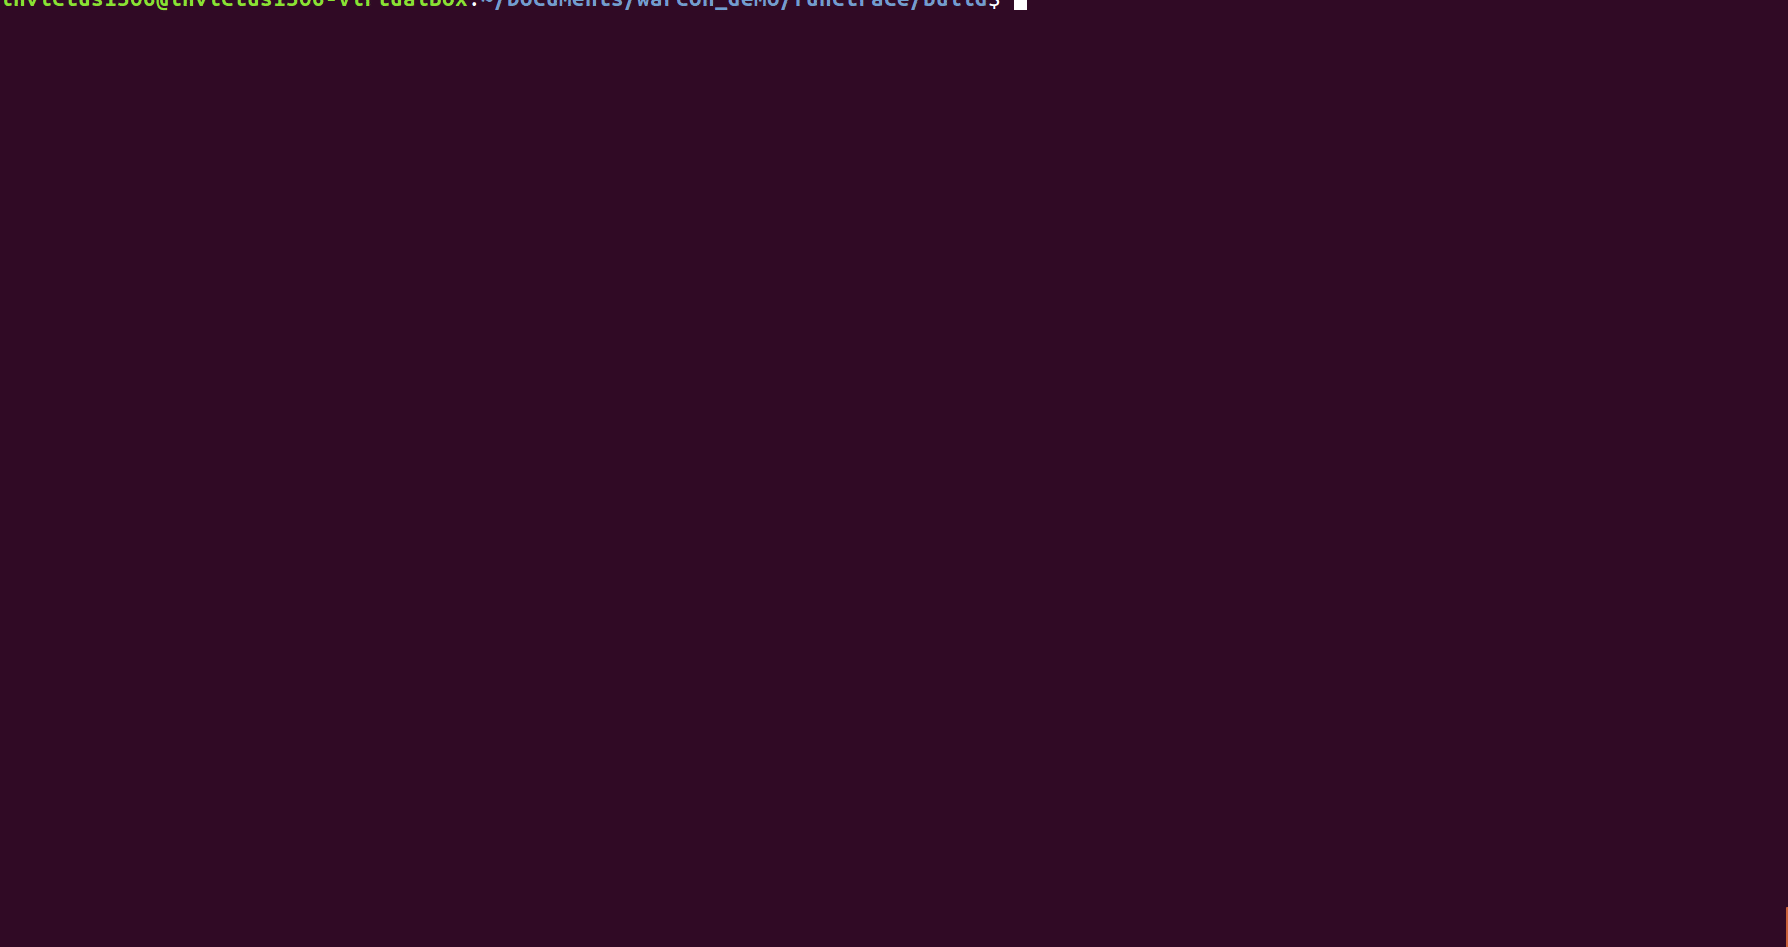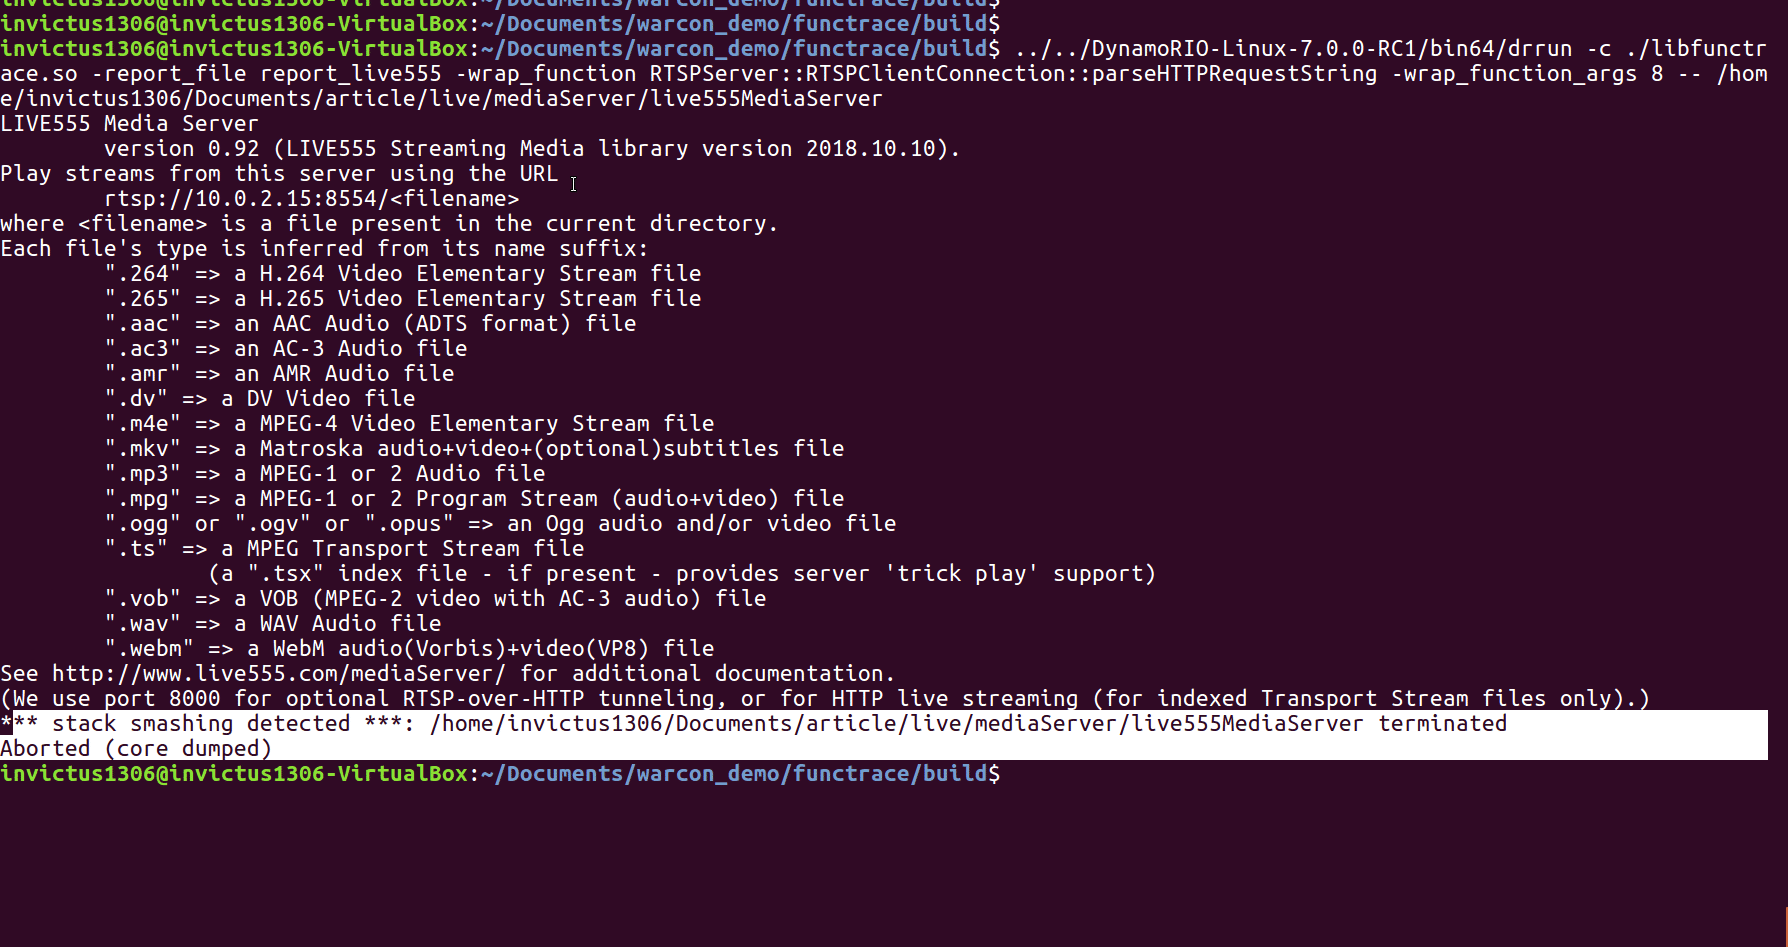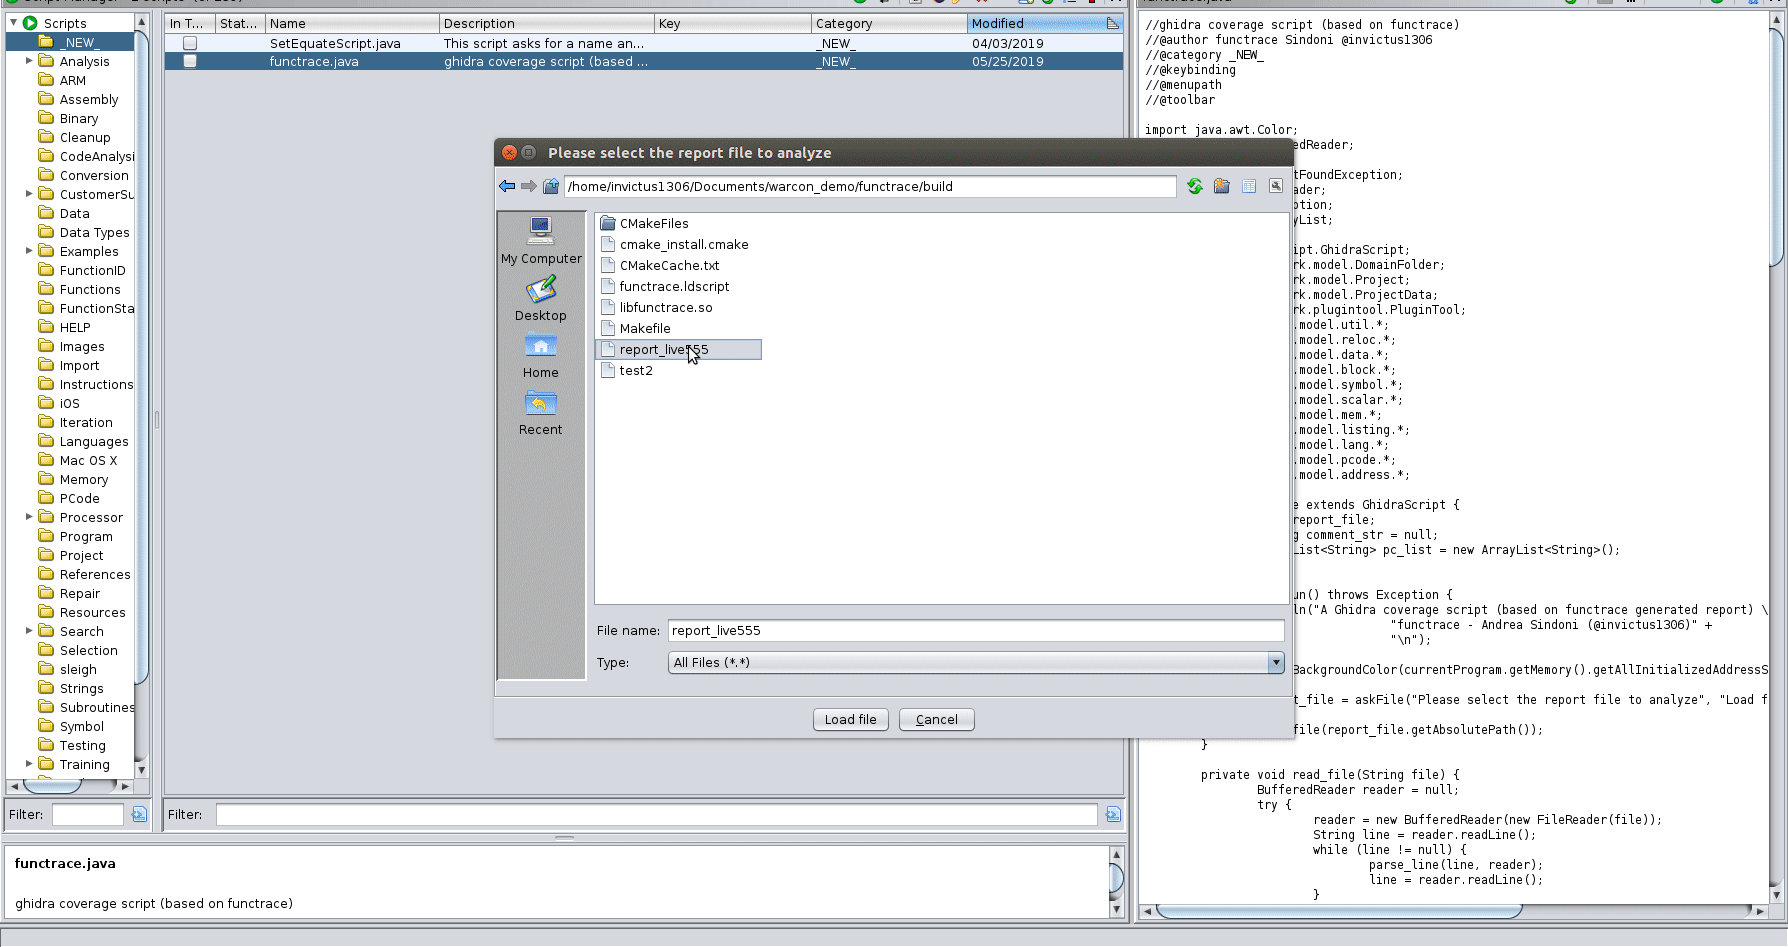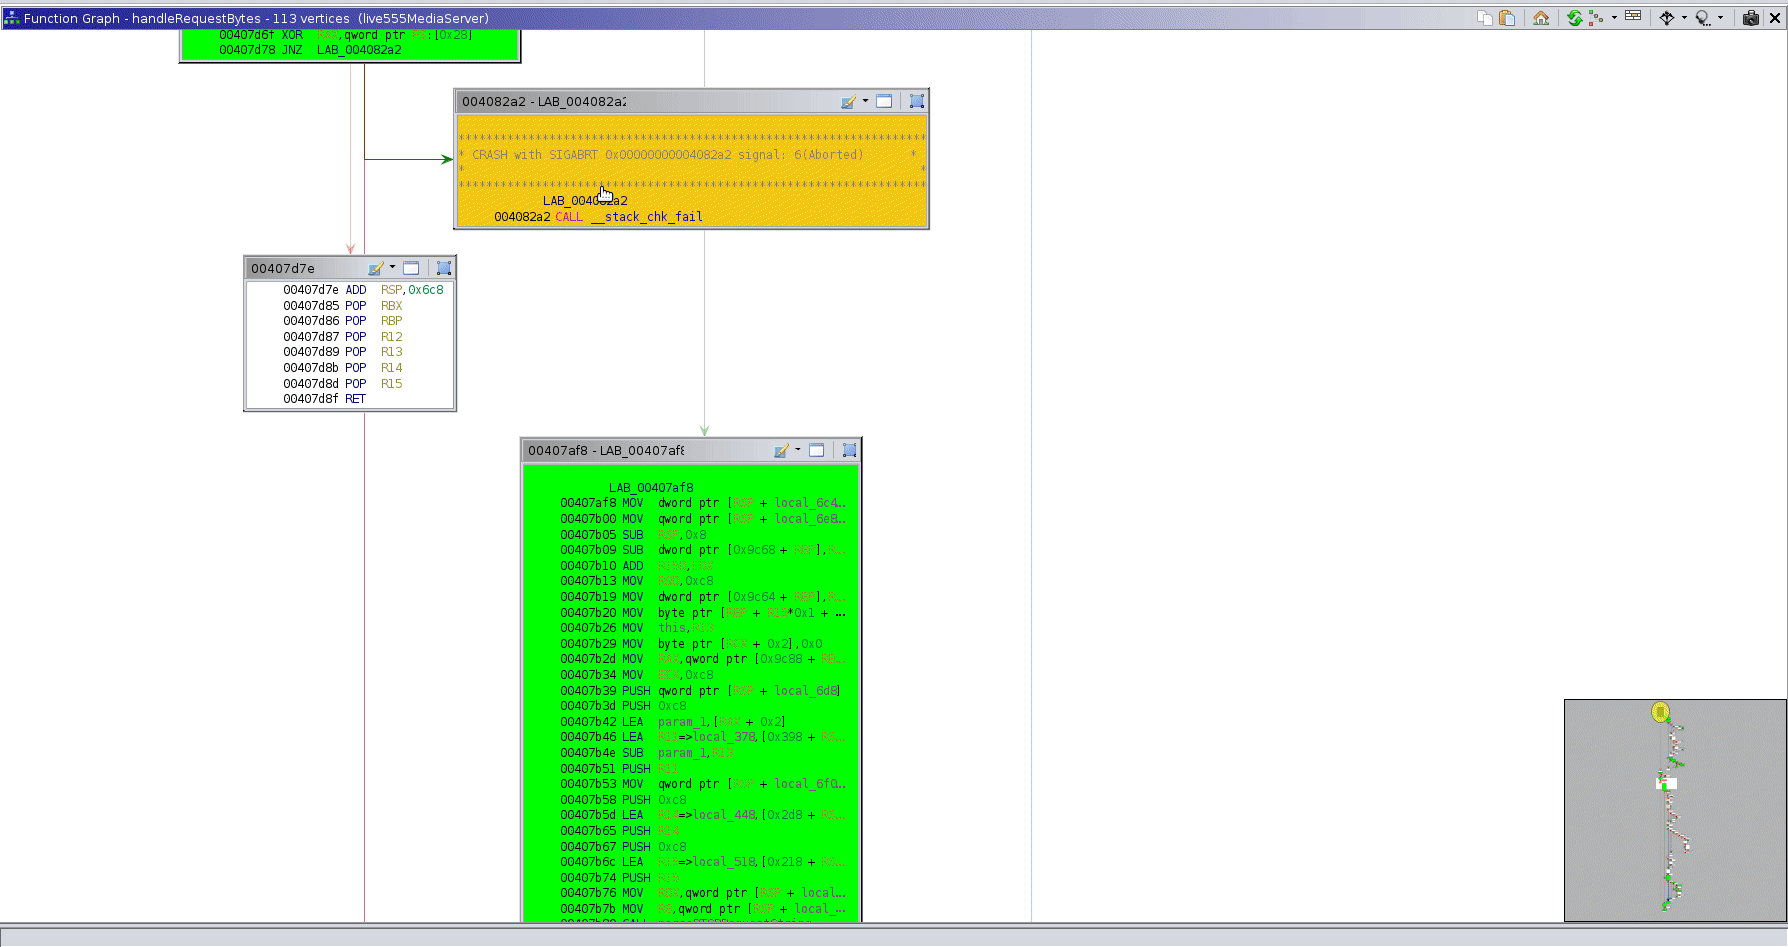 invictus1306/functrace
A function tracer
 yadyvazifeh1oz92/ecdsa-private-key-recovery
Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 zodiacon/alltools
All reasonably stable tools
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
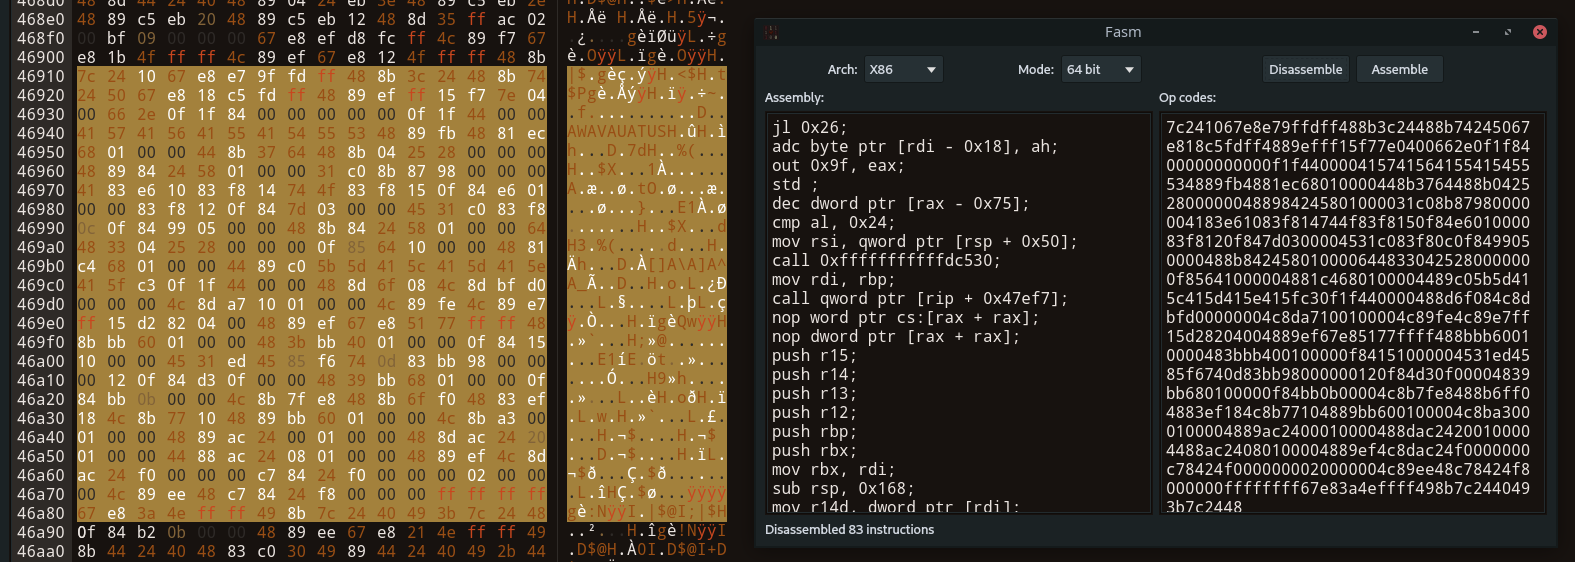 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
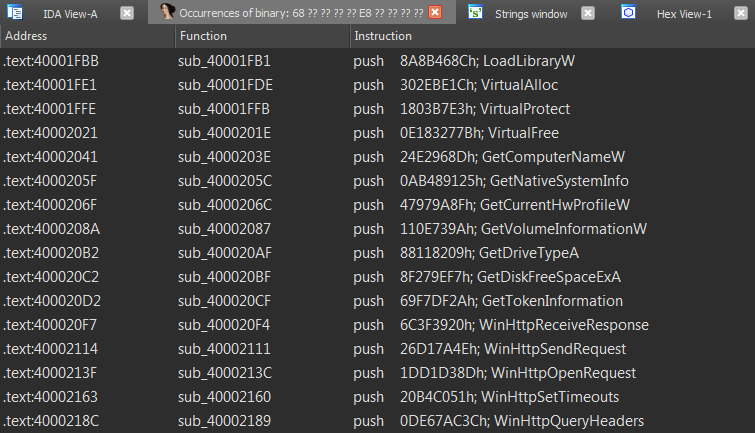 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan