

ablation
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
ai-assisted-reversingandroid-securitybinary-analysis+7
66
ablation-tool/ablationReverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
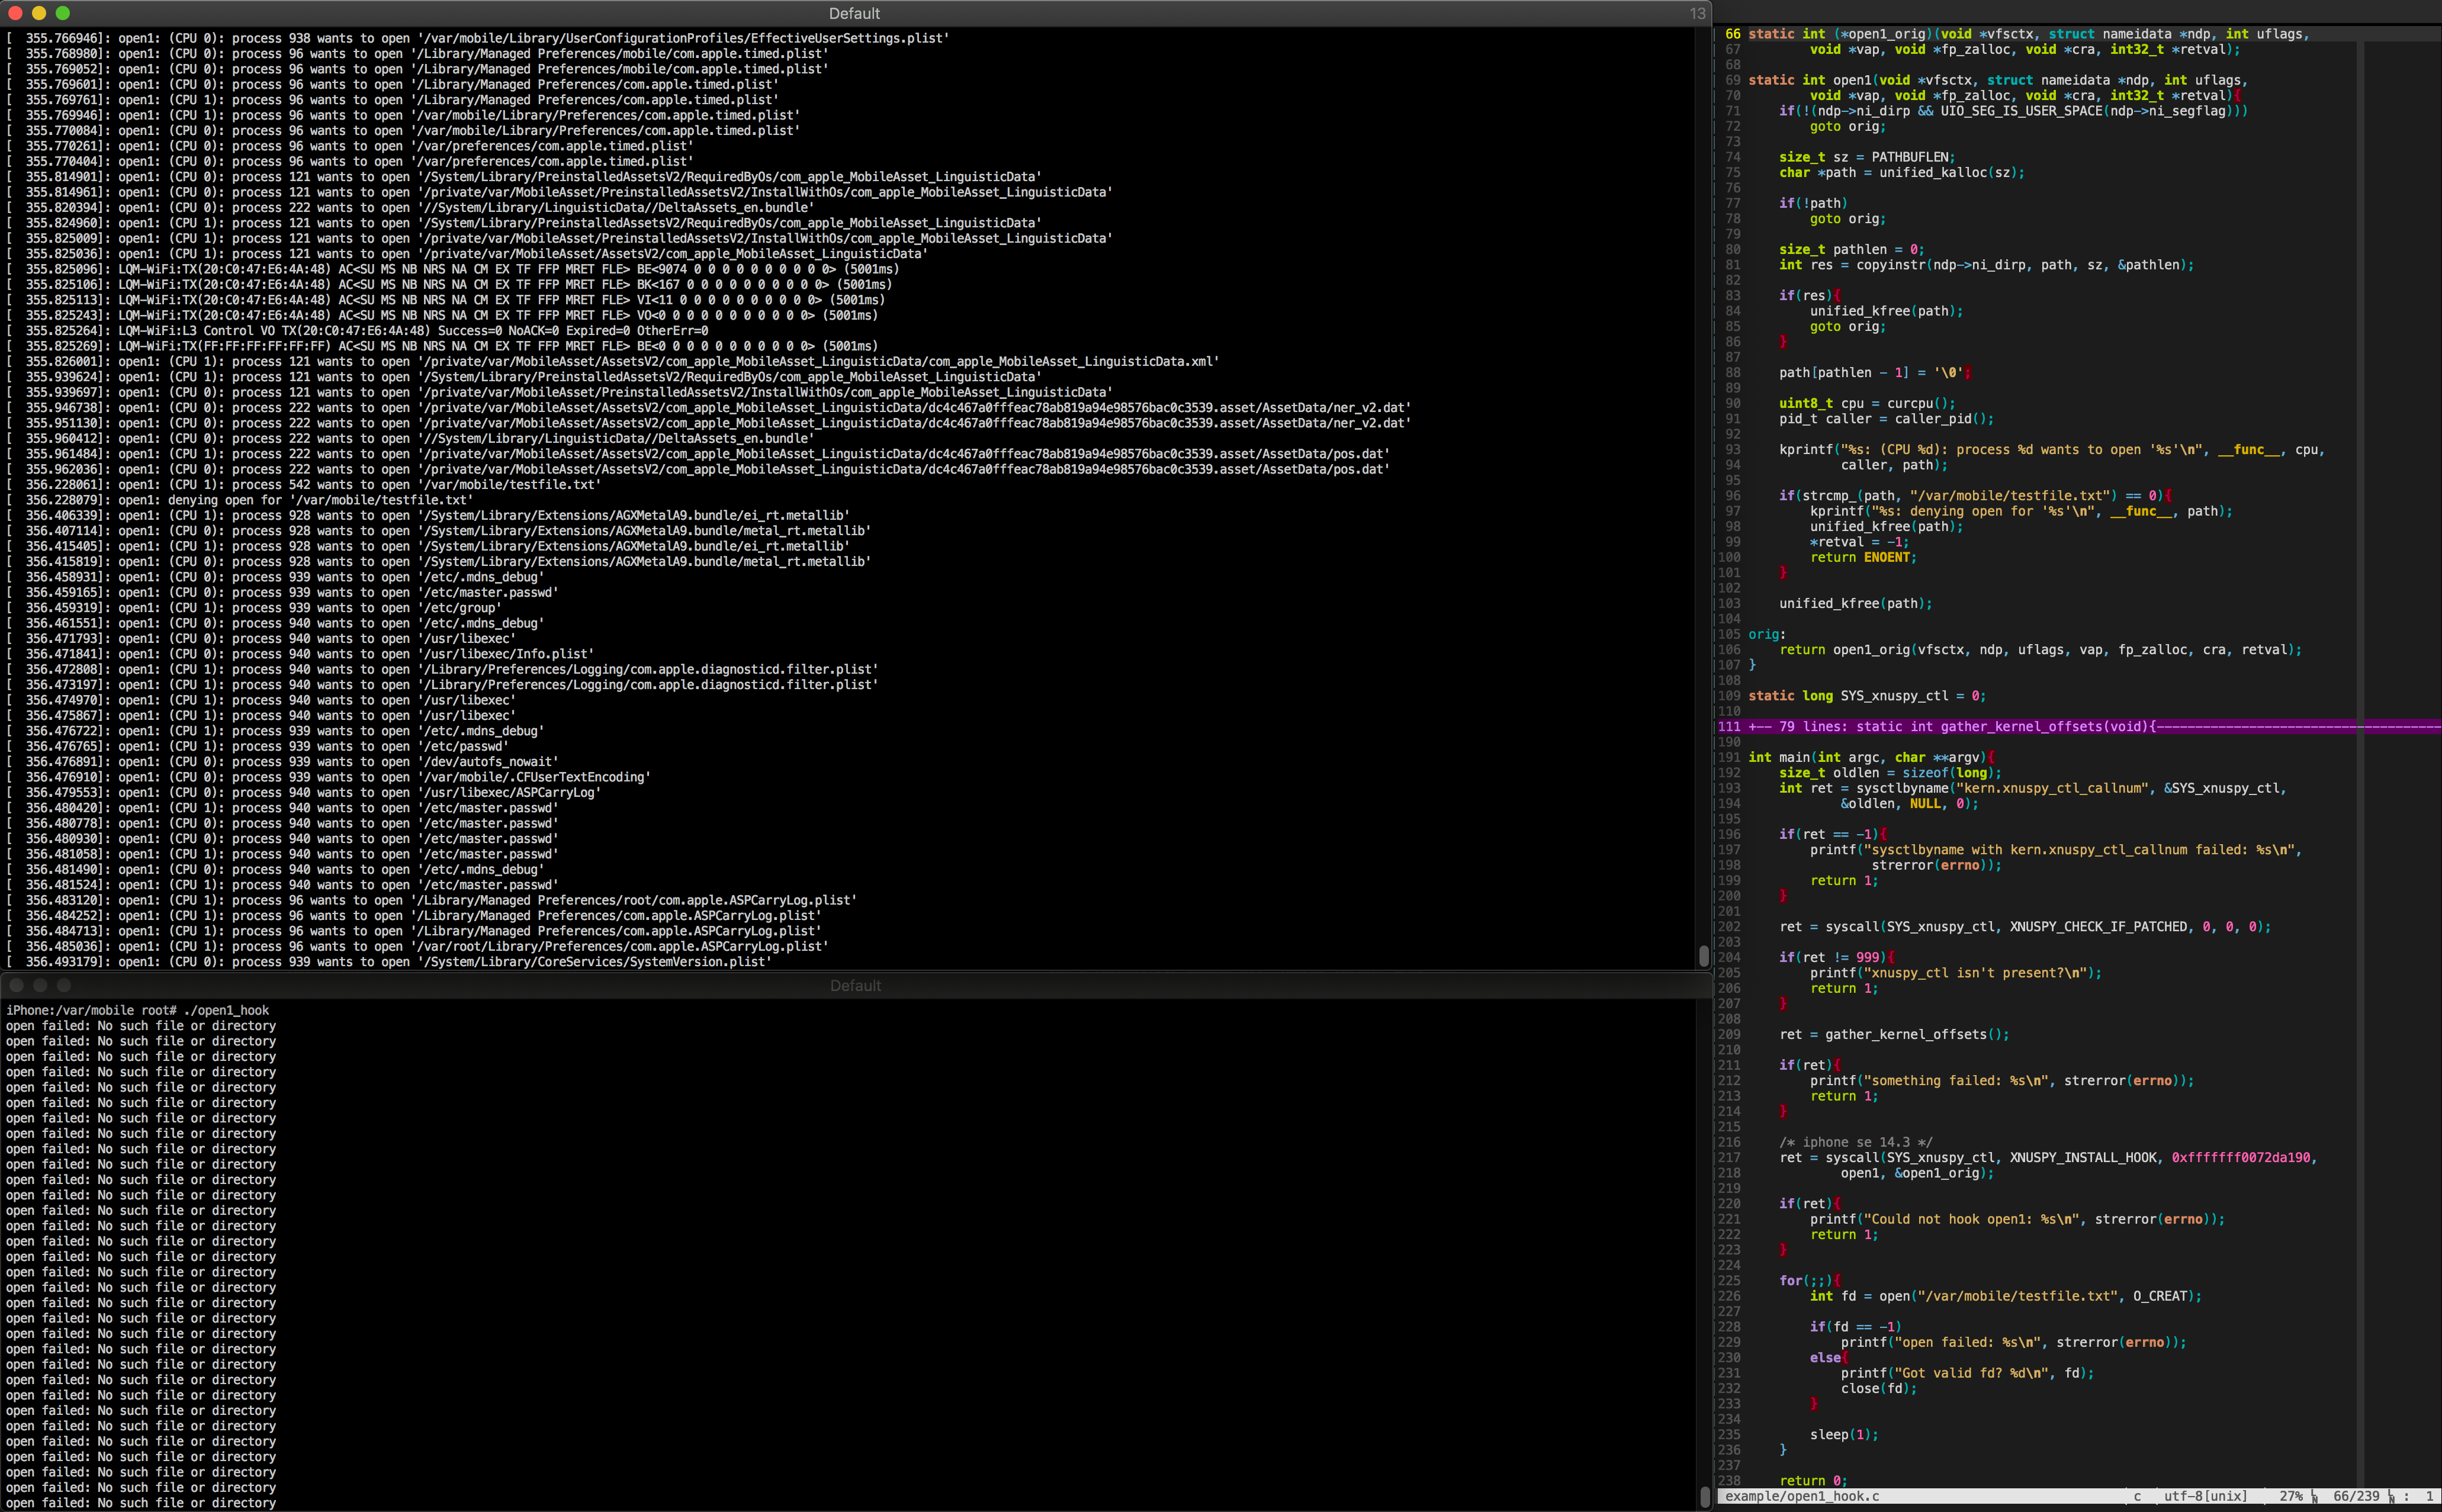 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 angr/angr
A powerful and user-friendly binary analysis platform!