
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
16 results
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
188
24 days ago
sass-king preview

sass-king

GitHubflorianmattana/sass-king

Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
binary-analysiscode-analysiscurated-resources+8
3404 months ago
python-exe-unpacker preview

python-exe-unpacker

GitHubwithsecurelabs/python-exe-unpacker

A helper script for unpacking and decompiling EXEs compiled from python code.
binary-analysisdynamic-analysis-sandboxingforensics+2
1.0k2 years ago
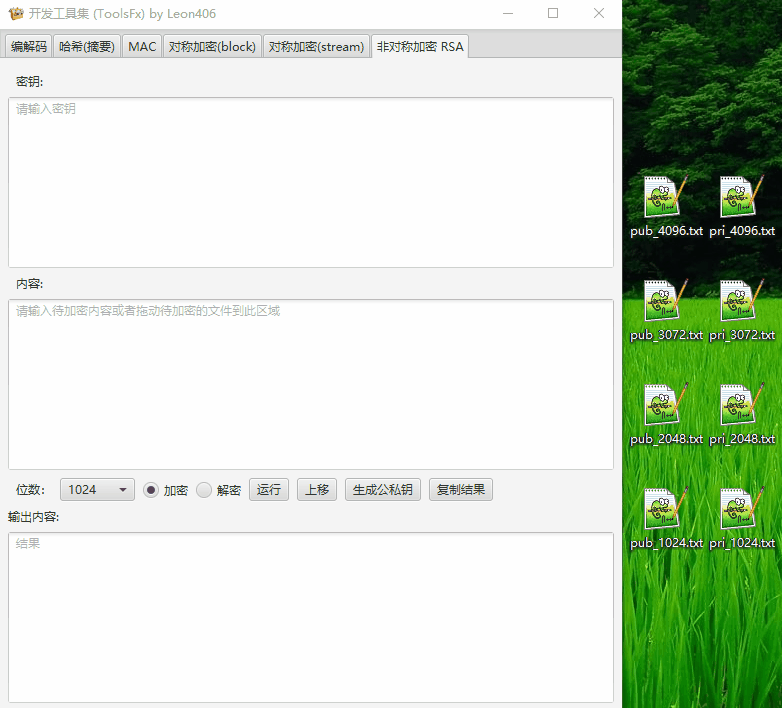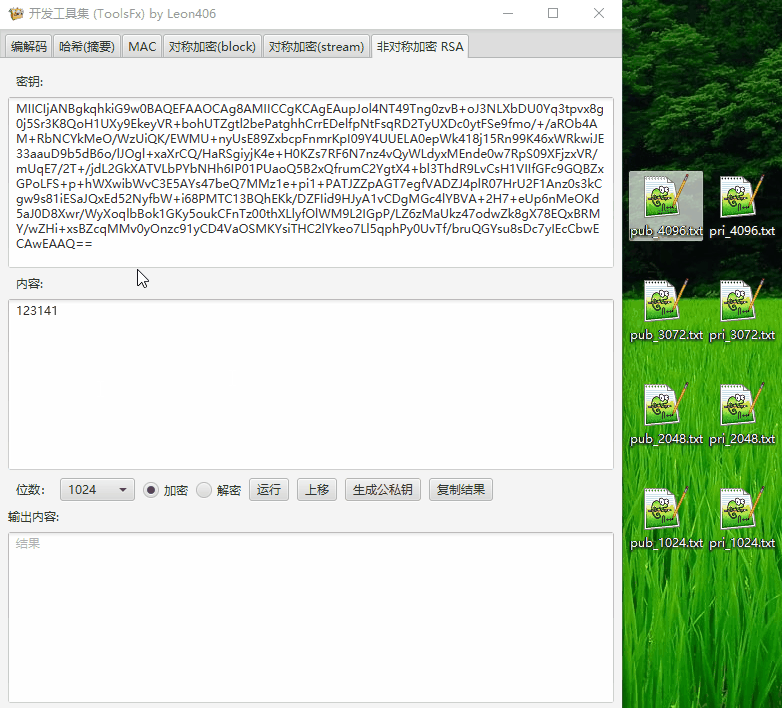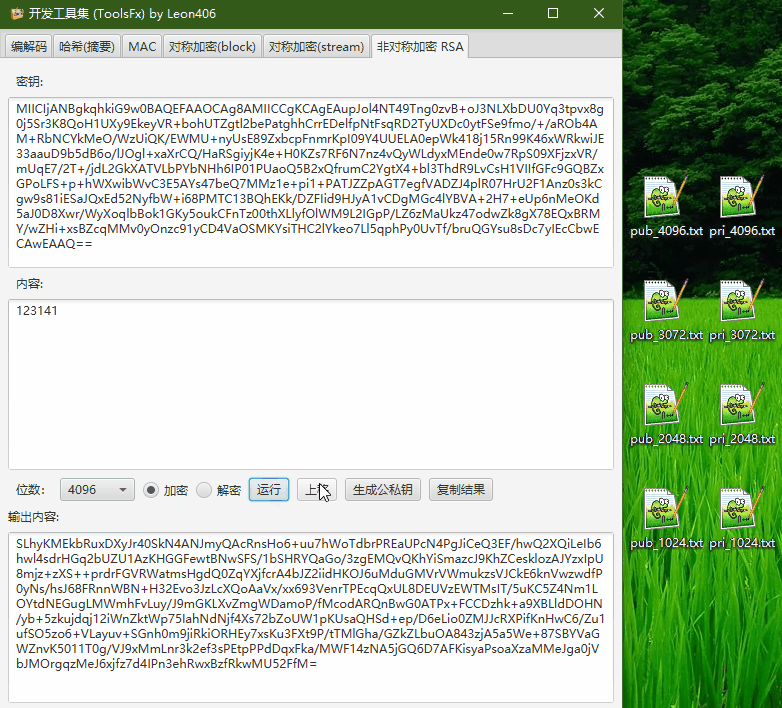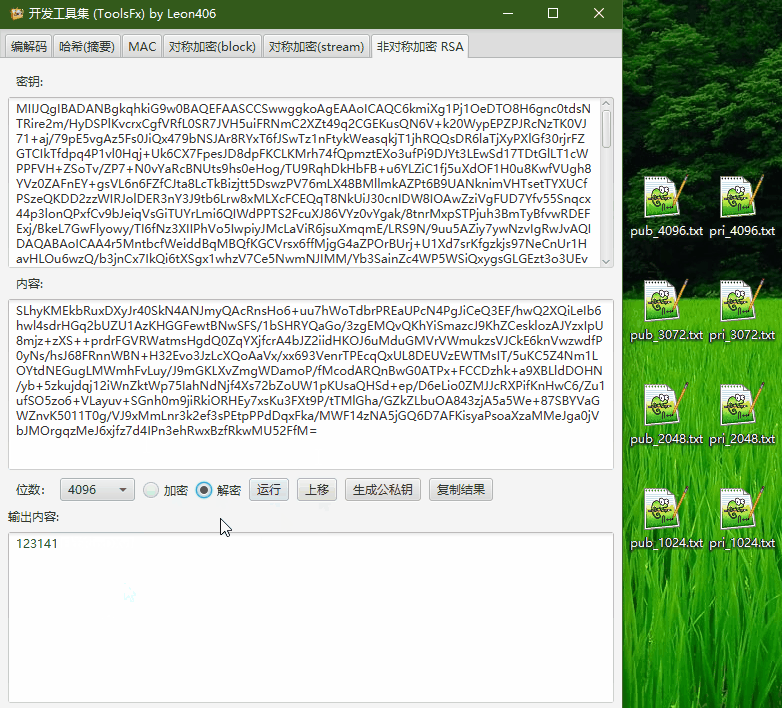
ToolsFx preview

ToolsFx

GitHubleon406/toolsfx

跨平台密码学工具箱。包含编解码,编码转换,加解密, 哈希,MAC,签名,大数运算,压缩,二维码功能,CTF等功能。
binary-analysiscryptographyctf+3
2.1k4 months ago
Transformers-Forged-To-Fight-Offline-Version preview

Transformers-Forged-To-Fight-Offline-Version

GitHubgeamztheangrybirds727/transformers-forged-to-fight-offline-version

TRANSFORMERS: Forged to Fight is a 3D combat game where you take over some of the most charismatic troopers straight out of the Transformers…
binary-analysisbinary-exploitationcurated-resources+5
32 months ago
SPiCa preview

SPiCa

GitHub0xkirisame/spica

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
anomaly-detectionbinary-analysisdefensive-tools+7
1042 months ago
MalwareForge---Advanced-Static-Malware-Analyzer preview

MalwareForge---Advanced-Static-Malware-Analyzer

GitHubkaandemir993/malwareforge---advanced-static-malware-analyzer

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

binary-analysishash-analysismalware-analysis+2
41 month ago
Sekiryu preview
Archived

Sekiryu

GitHub20urc3/sekiryu

Comprehensive toolkit for Ghidra headless.
ai-assisted-reversingbinary-analysiscode-analysis+3
3621 year ago
CVE-2024-42642 preview

CVE-2024-42642

GitHubvl4dr/cve-2024-42642

Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…
binary-analysisembedded-systems-securityexploitation+5
142 years ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4926 months ago
AndroidDriveSignity preview

AndroidDriveSignity

GitHubgmh5225/androiddrivesignity

AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
android-securitybinary-analysisexploitation+1
632 years ago
r0ak preview

r0ak

GitHubown2pwn/r0ak

r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
binary-analysisexploitationpenetration-testing+3
278 years ago
fuzzuf preview

fuzzuf

GitHubfuzzuf/fuzzuf

Modular fuzzing framework with a DSL (HierarFlow) to compose fuzzing loops from reusable primitives. Supports AFL, libFuzzer, VUzzer, and more for…

binary-analysiseducationfuzzing+2
3852 years ago
CVE-2020-15999 preview

CVE-2020-15999

GitHuboxfemale/cve-2020-15999

CVE-2020-15999

binary-analysisexploitationfuzzing+3
35 years ago
VLC_CVE-2021-25801_Analysis preview

VLC_CVE-2021-25801_Analysis

GitHubdshankle/vlc_cve-2021-25801_analysis

Technical analysis of CVE-2021-25801 in VLC's AVI parser, demonstrating an out-of-bounds read via crafted sub-index chunks and providing a…

binary-analysisexploitationfuzzing+1
4 years ago
dotNetPELoader preview

dotNetPELoader

GitHubiss4cf0ng/dotnetpeloader

A C# PE loader for x64 and x86 PE files.

binary-analysisexploitationpayload-development+2
576 months ago