
Shadow-Vault
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
authentication-authorizationemail-securityidentity-access-management+3
jenderal92/shadow-vaultShadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 watchtowrlabs/watchtowr-vs-solarwinds-webhelpdesk-cve-2025-40552-cve-2025-40553
Detection artifact generator for SolarWinds Web Help Desk pre-auth RCE chain (CVE-2025-40552 + CVE-2025-40553). Verifies authentication bypass and…
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 authelia/authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
 ghostpack/certify
C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
 7hepr0fess0r/adcsdevilcom
A C# tool for requesting certificates from ADCS using DCOM over SMB. This tool allows you to remotely request X.509 certificates from CA server using…
 xenoncyber/envy
A terminal based tool for managing secrets with both tui and cli support
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
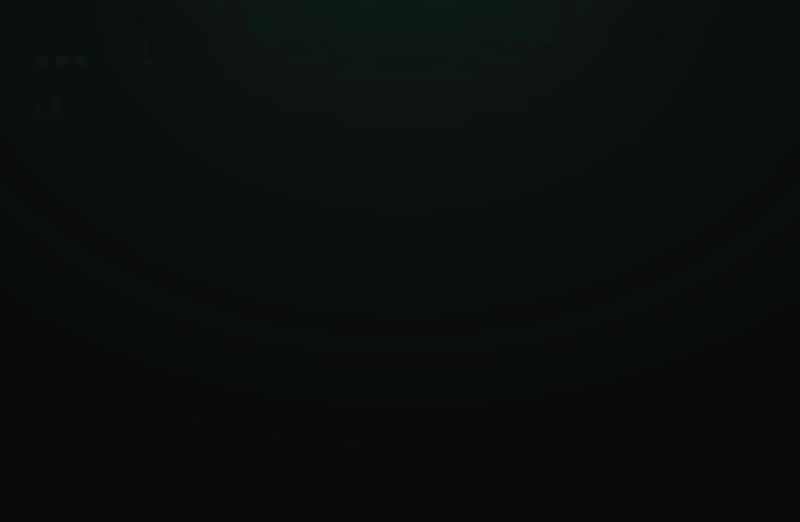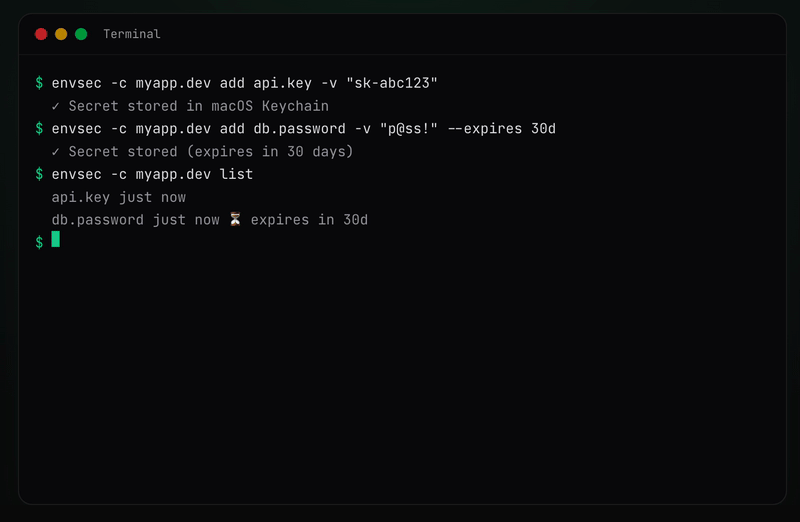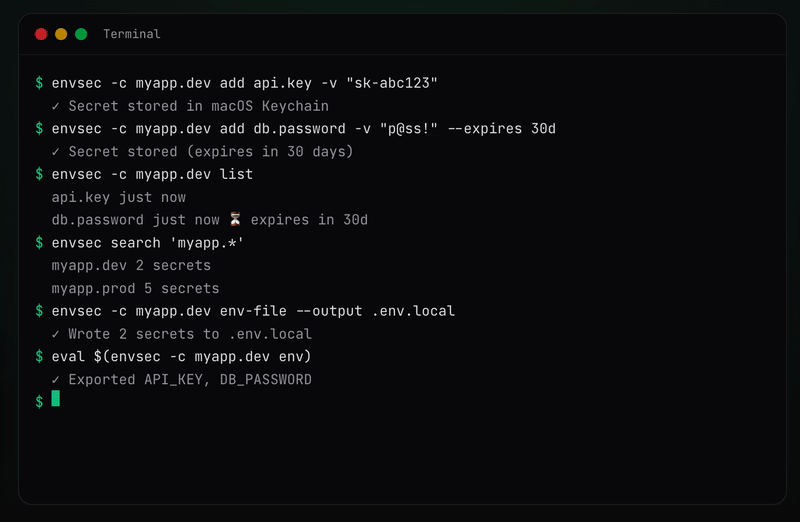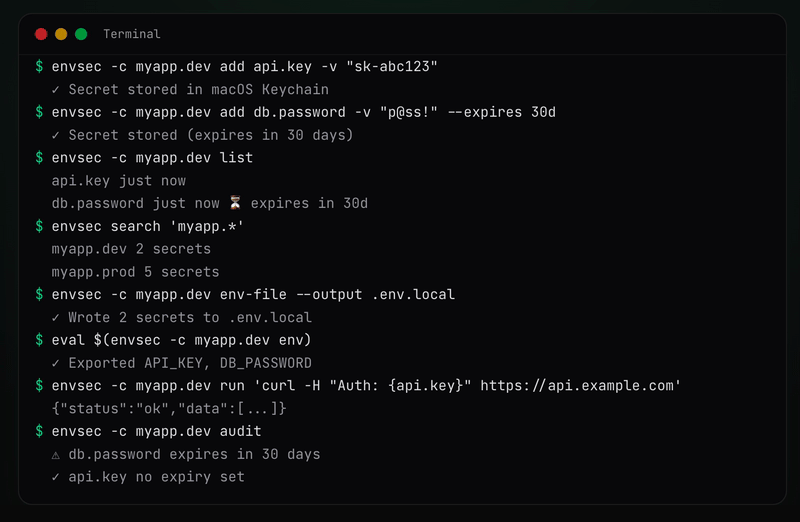 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 sumaiyafathima-code/cve-2023-27524
Exploit tool for CVE-2023-27524, an authentication bypass vulnerability in Apache Superset. Enables unauthorized access to vulnerable instances for…
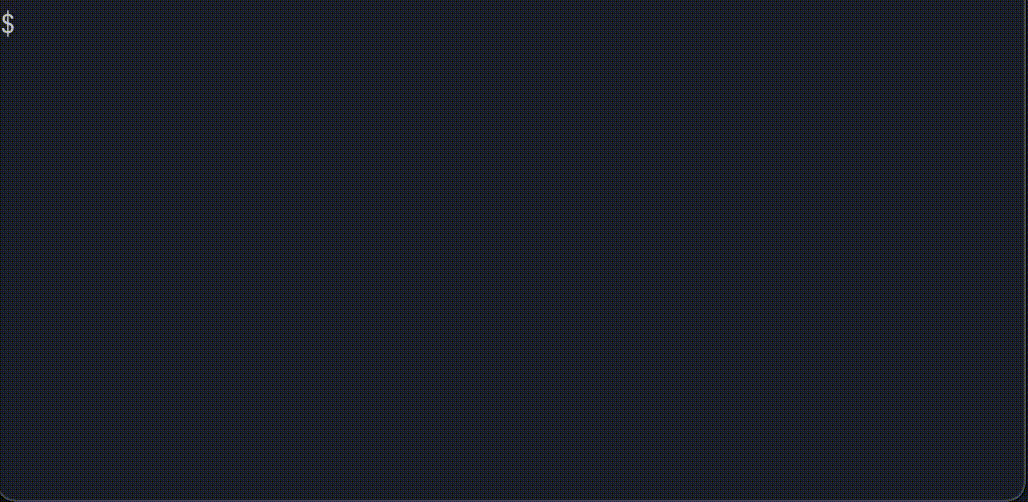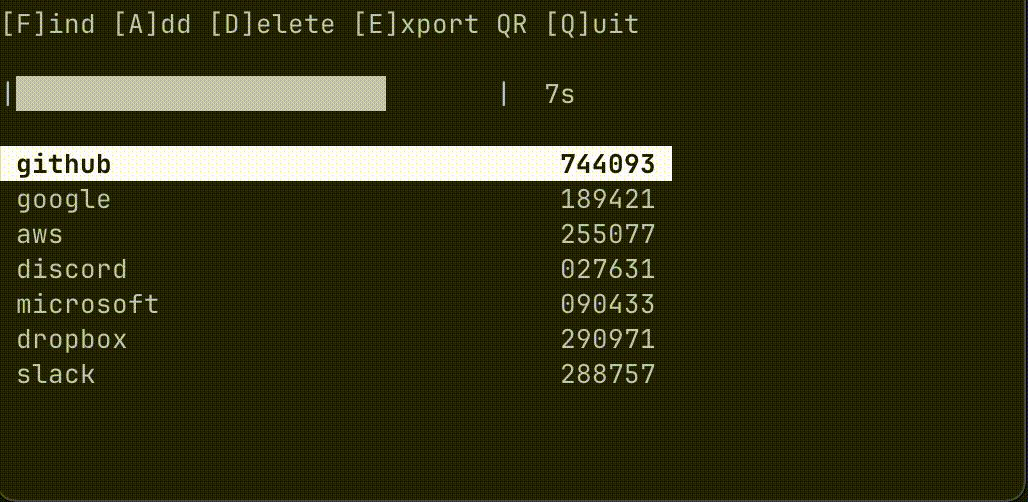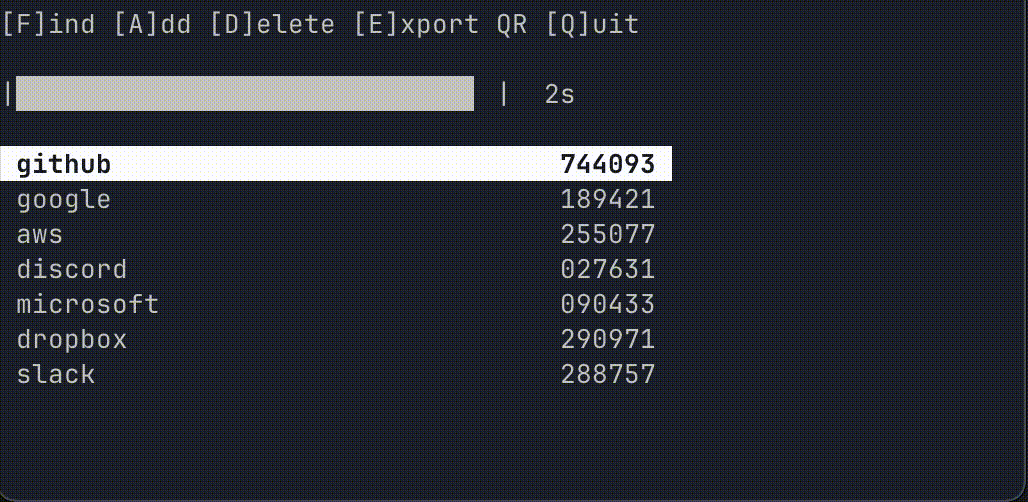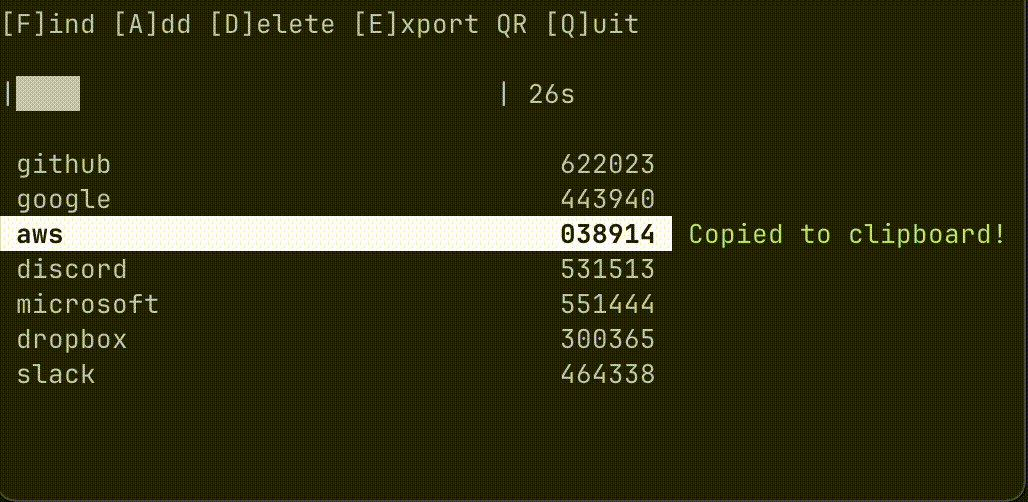 yen223/hotpot
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…