CVE-2026-65013-BOLA-IDOR

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…

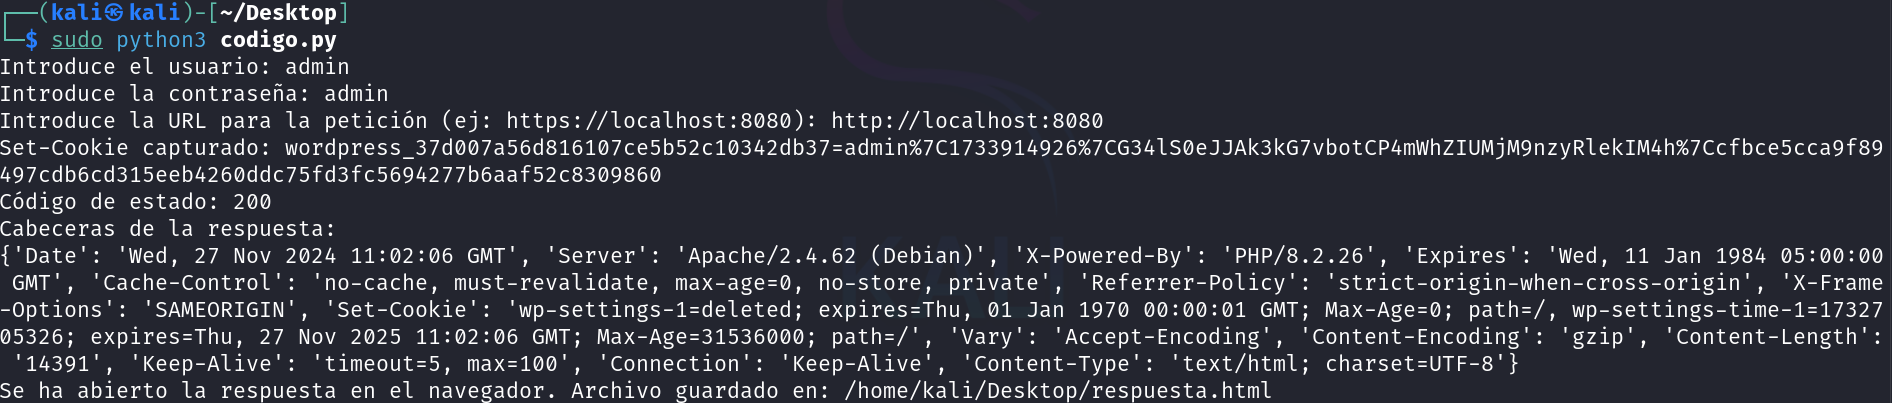
Proof-of-concept exploit for CVE-2024-10924, an authentication bypass vulnerability in the Really Simple Security WordPress plugin, enabling MFA…

Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)

Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.

Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…

The Secure CommsOS™ for mission-critical operations

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…

The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.

🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…

Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

The easiest, and most secure way to access and protect all of your infrastructure.

CVE-2026-23552 - Cross-Realm Token Acceptance in camel-keycloak