

pingap
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
api-securityauthenticationauthentication-authorization+4
vicanso/pingapA reverse proxy like nginx, built on pingora, simple and efficient.
 yen223/hotpot
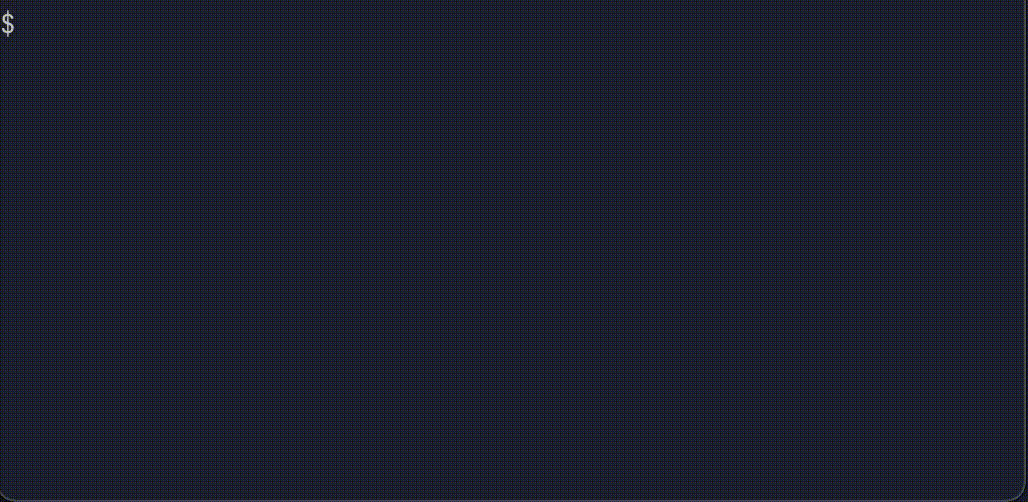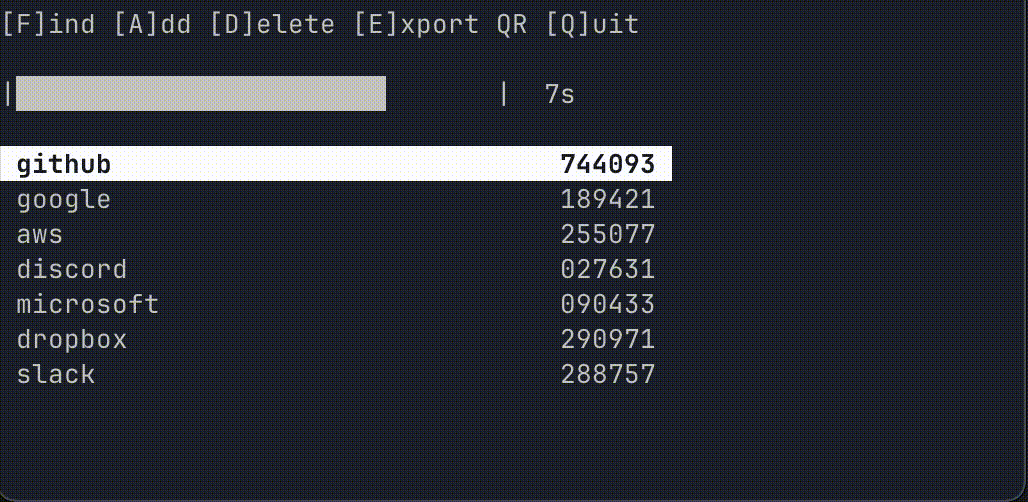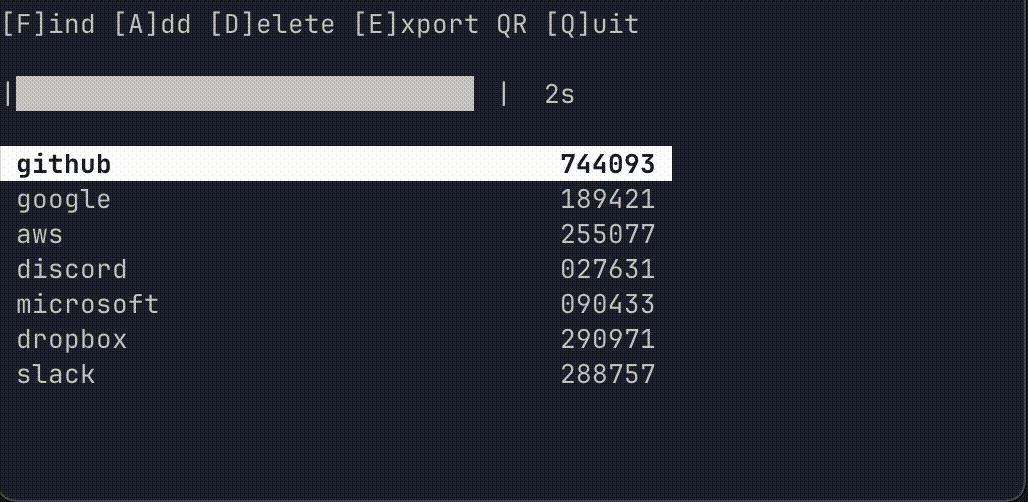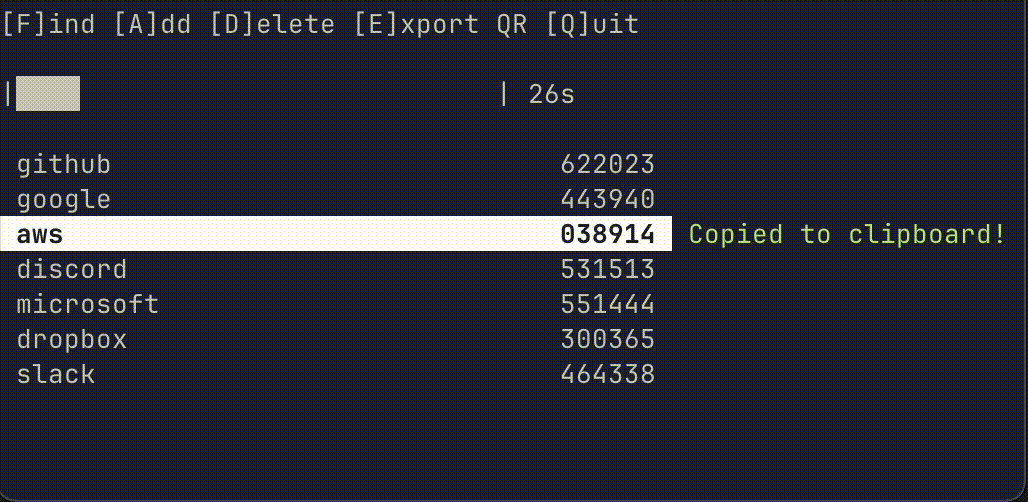
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.
 kanidm/kanidm
Self-hosted identity management platform providing WebAuthn passkeys, OAuth2/OIDC SSO, SSH key distribution, RADIUS and LDAP integration for modern…
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 randomrobbiebf/cve-2024-10924
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 murataydemir/cve-2020-6287
[CVE-2020-6287] SAP NetWeaver AS JAVA (LM Configuration Wizard) Authentication Bypass (Create Simple & Administrator Java User)
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
 agberohq/keeper
Simple Secure Keeper for Secrets
 m3ssap0/wordpress-really-simple-security-authn-bypass-exploit
Python exploit for CVE-2024-10924 authentication bypass in Really Simple Security < 9.1.2. Enables unauthenticated login as any existing WordPress…
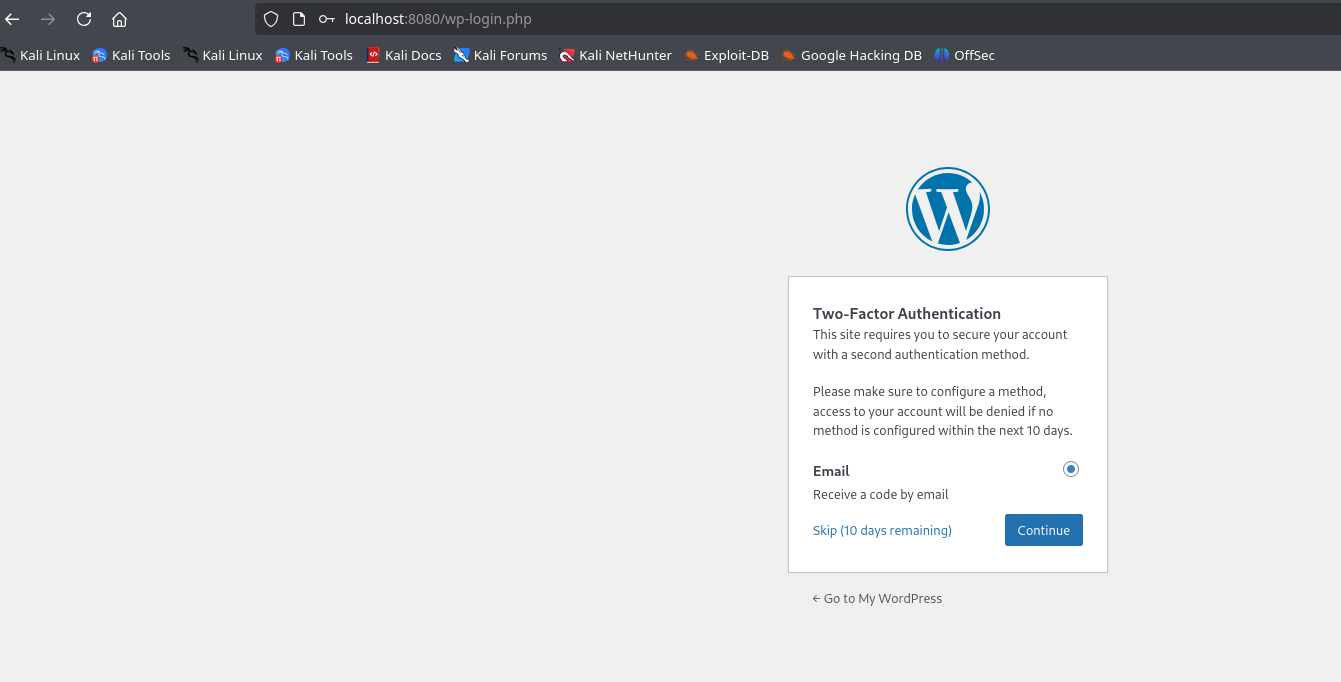 maalfer/cve-2024-10924-poc
Bypass del MFA en WordPress con el plugin Really Simple Security instalado entre las versiones 9.0.0 – 9.1.1.1.
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 izxci/cve-2026-7459
Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…
 maleeshaudan/wordpress-cve-2024-10924--exploit
WordPress CVE-2024-10924 Exploit for Really Simple Security plugin