
CVE-2022-22978-PoC
 ducluongtran9121/cve-2022-22978-poc
PoC of CVE-2022-22978 vulnerability in Spring Security framework
authentication-authorizationeducationexploitation+3
13
ducluongtran9121/cve-2022-22978-pocPoC of CVE-2022-22978 vulnerability in Spring Security framework
 shoucheng3/apache__shiro_cve-2023-34478_1-11-0
Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…
 umakant76705/cve-2022-22978
Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 symfony/symfony
The Symfony PHP framework
 wso2/carbon-identity-framework
Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 shoucheng3/asf__cxf_cve-2019-17573_3-2-11
Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.
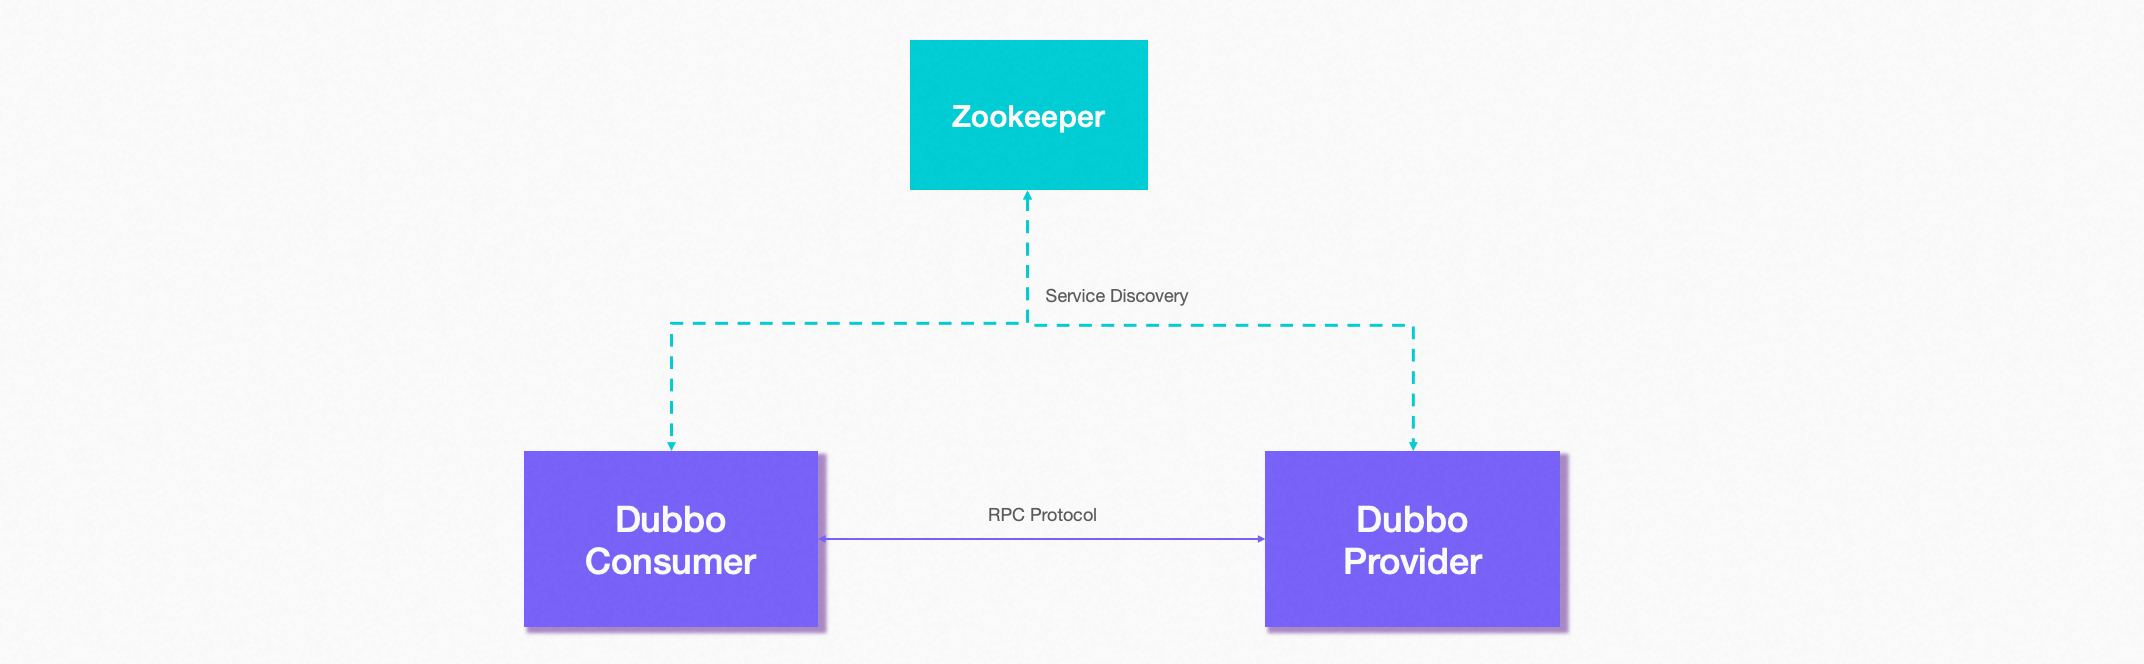 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 shoucheng3/asf__cxf_cve-2016-6812_3-0-11
Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.
 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
 th-secforge/cve-2025-29972
CVE-2025-29927 - Critical Security Vulnerability in Next.js
 ethan-repo-lab4b6/cve-2022-36537
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

 kit-lang/packages/kit-policy
A flexible, composable authorization framework for Kit (inspired by Action Policy)
 nearai/ironclaw
Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…
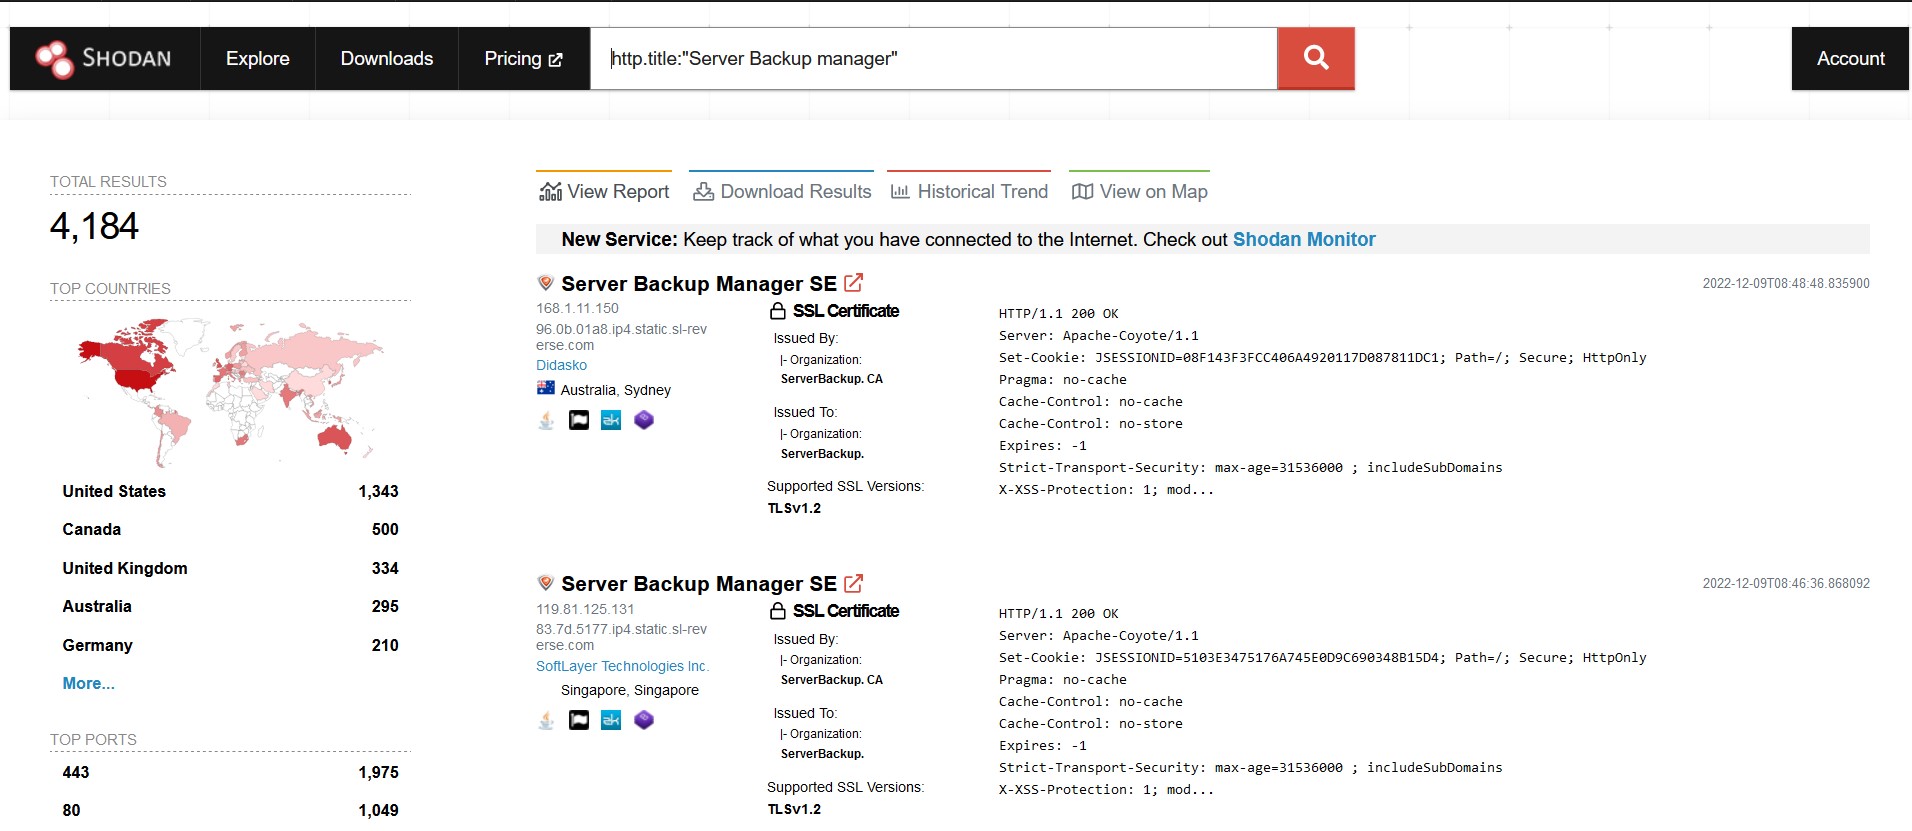 malwareman007/cve-2022-36537
POC of CVE-2022-36537