
CVE-2021-3560
 winmin/cve-2021-3560
PolicyKit CVE-2021-3560 Exploitation (Authentication Agent)
authentication-authorizationexploitationpenetration-testing+2
25
winmin/cve-2021-3560PolicyKit CVE-2021-3560 Exploitation (Authentication Agent)
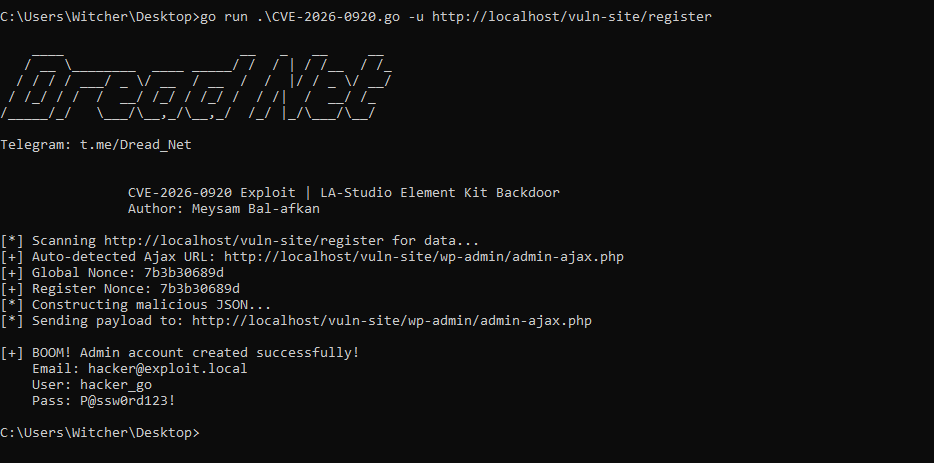 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…
 rohitberiwala/cve-2026-28372-telnetd-privilege-escalation
This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…
 xrzmodz444/cve-2026-41940-poc-linux
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports custom payloads and verbose logging, compatible with…
 okkotsu1/cve-2024-47533
Exploit for CVE-2024-47533, a critical authentication bypass in Cobbler XML-RPC API, granting unauthenticated admin access for educational security…
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 turtlearm/ksmbrace
ksmbd CVEs: CVE-2026-31717, CVE-2026-68083
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 hakivvi/cve-2021-3560
C exploit for CVE-2021-3560, an authentication bypass in polkit enabling unprivileged users to create a privileged account via DBus, with a detailed…
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
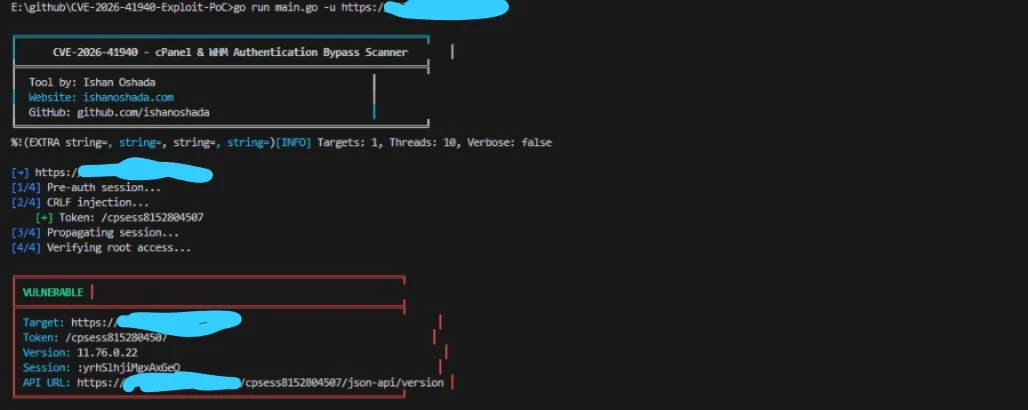 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
 ignis-sec/cve-2019-10008
ManageEngine Service Desk Plus 10.0 Privilaged account Hijacking
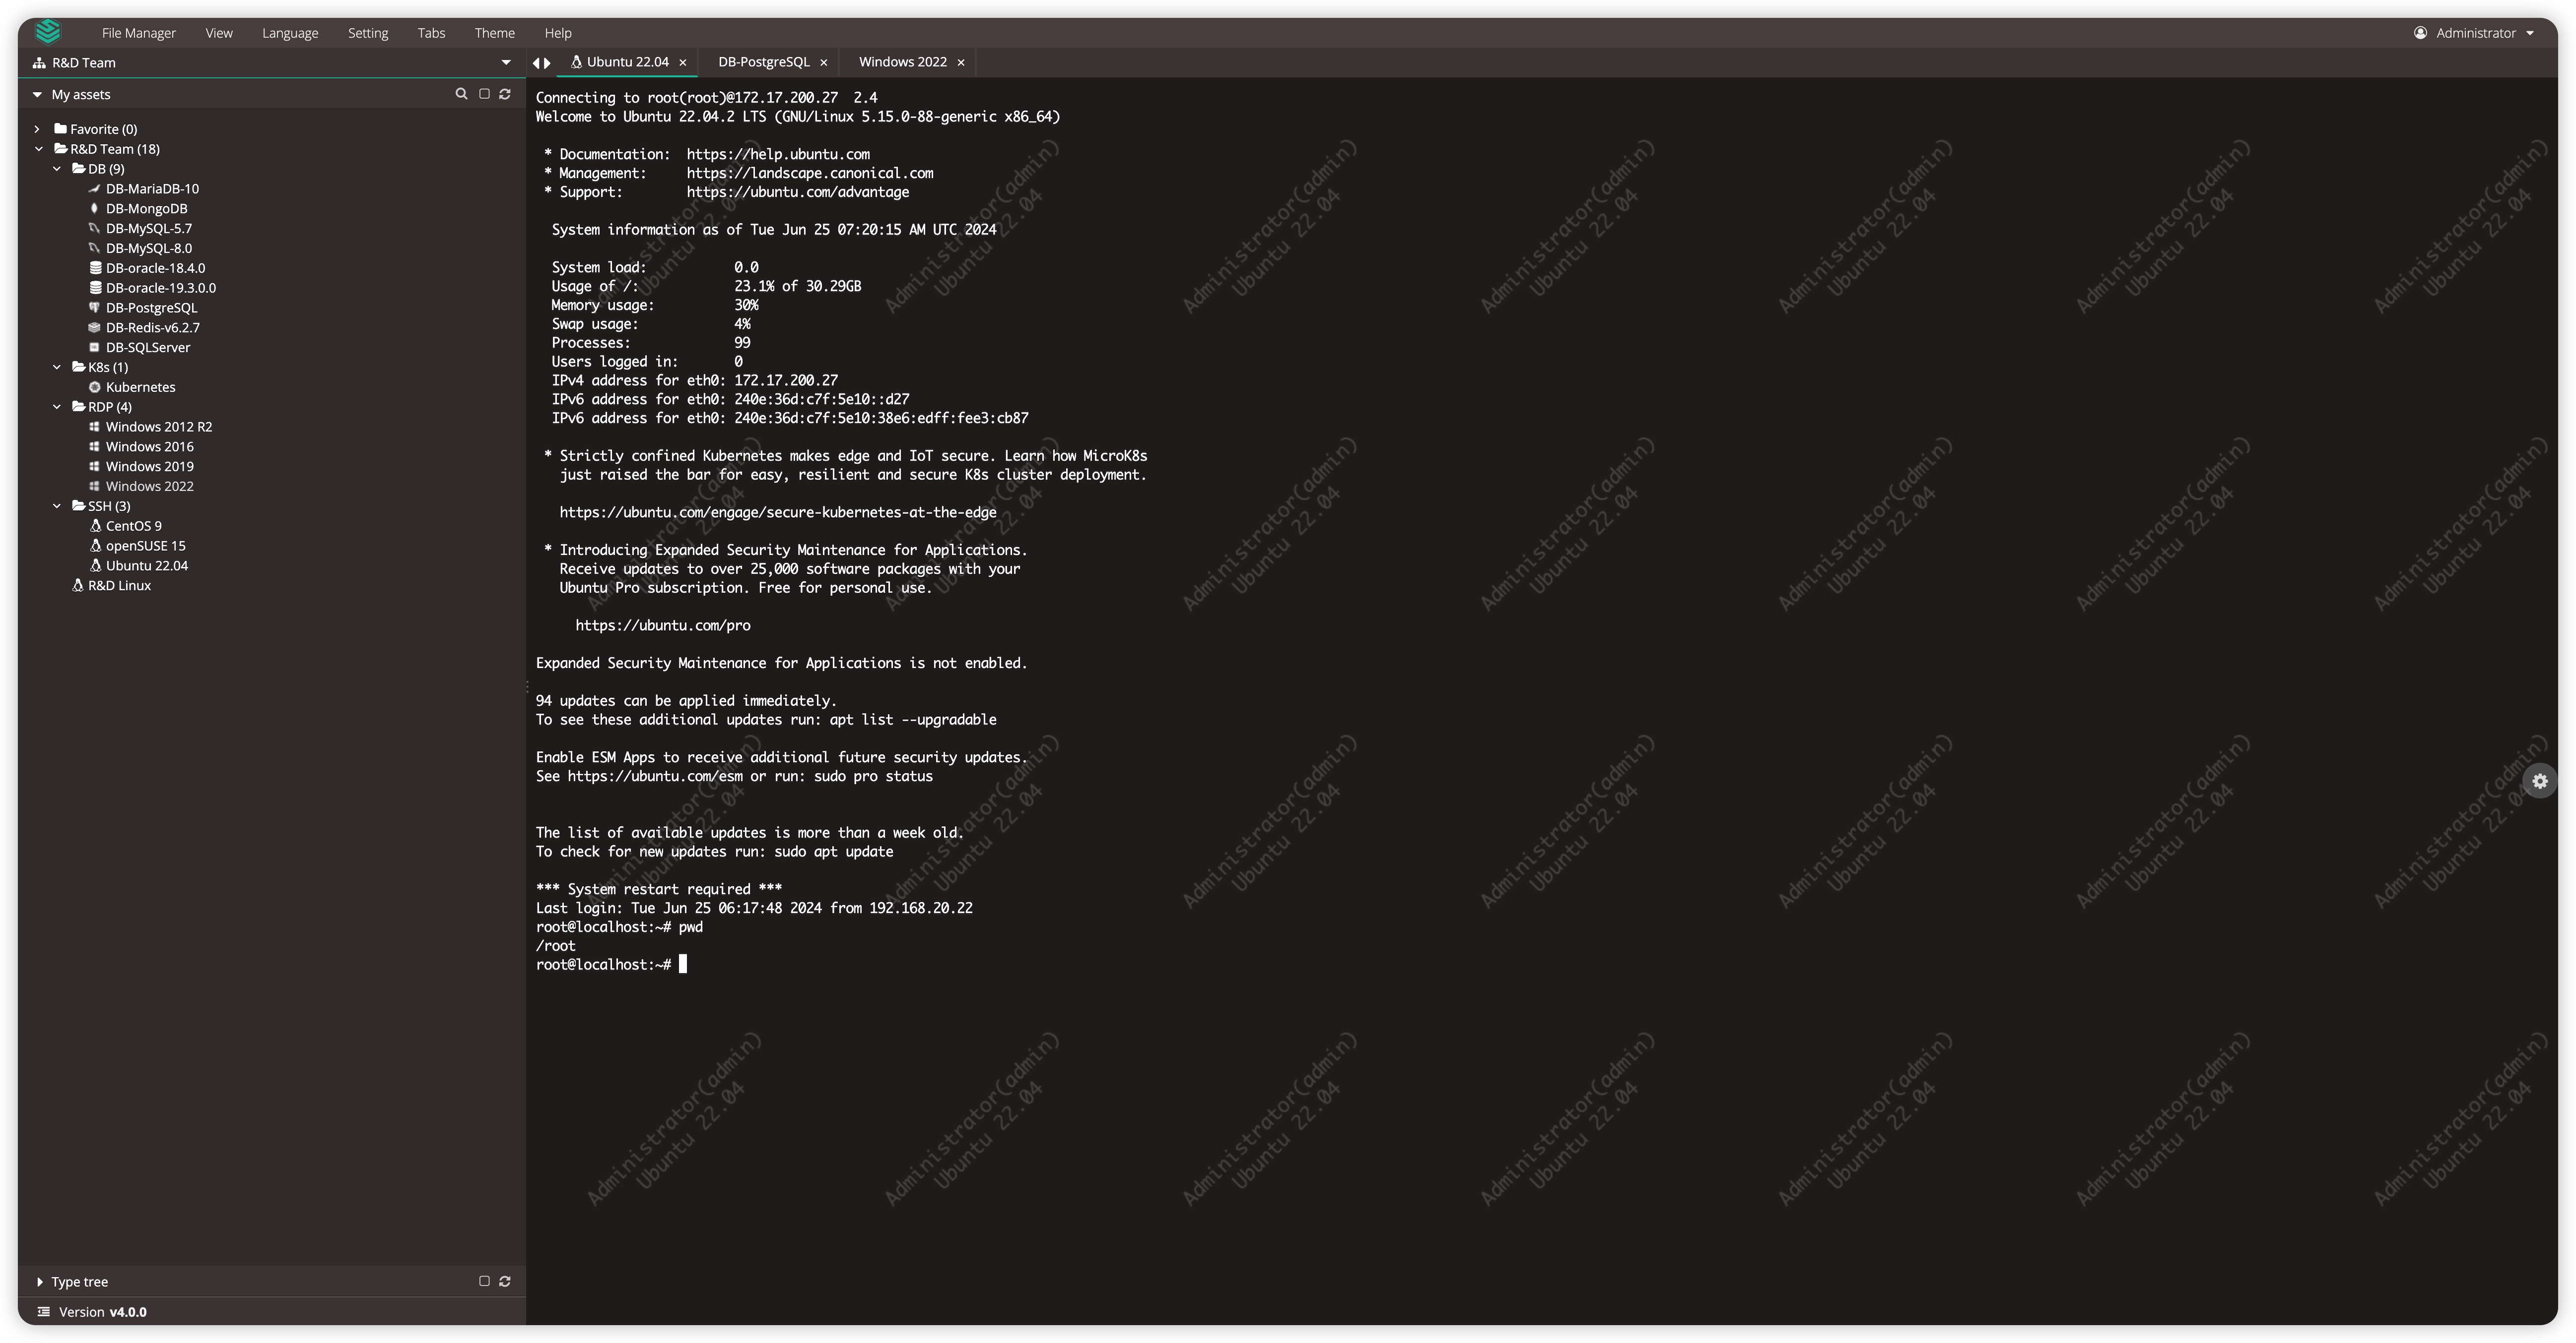 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer