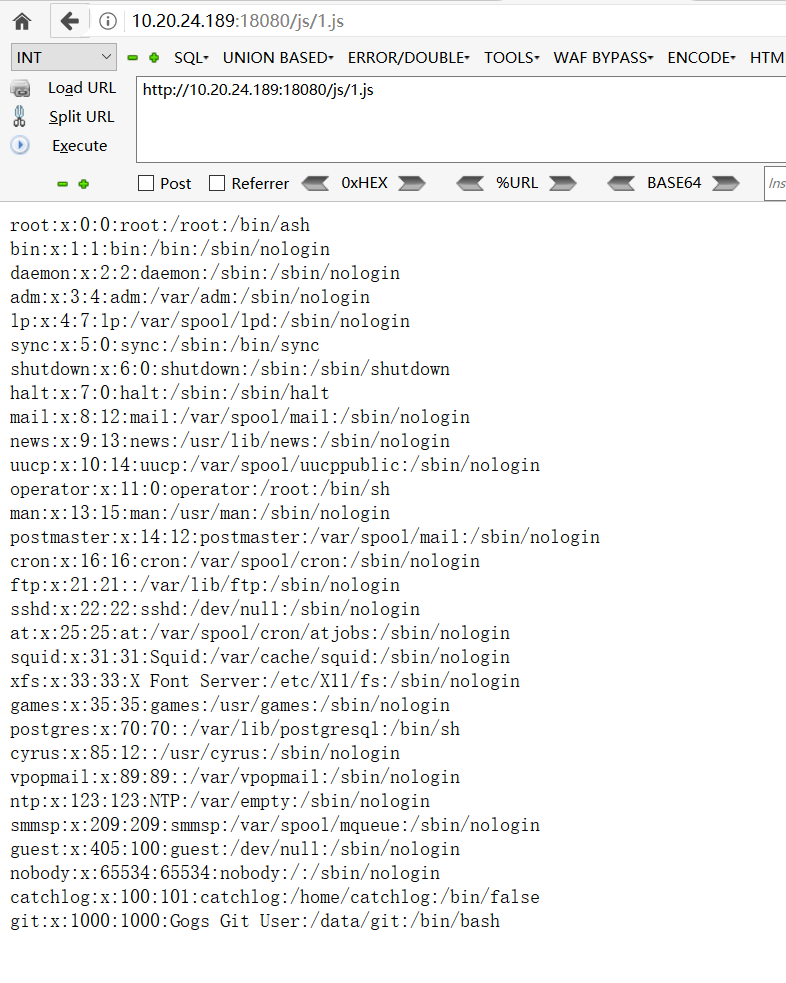
spring-cloud__spring-cloud-config_CVE-2020-5405_2-1-6-RELEASE

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

A flexible, composable authorization framework for Kit (inspired by Action Policy)

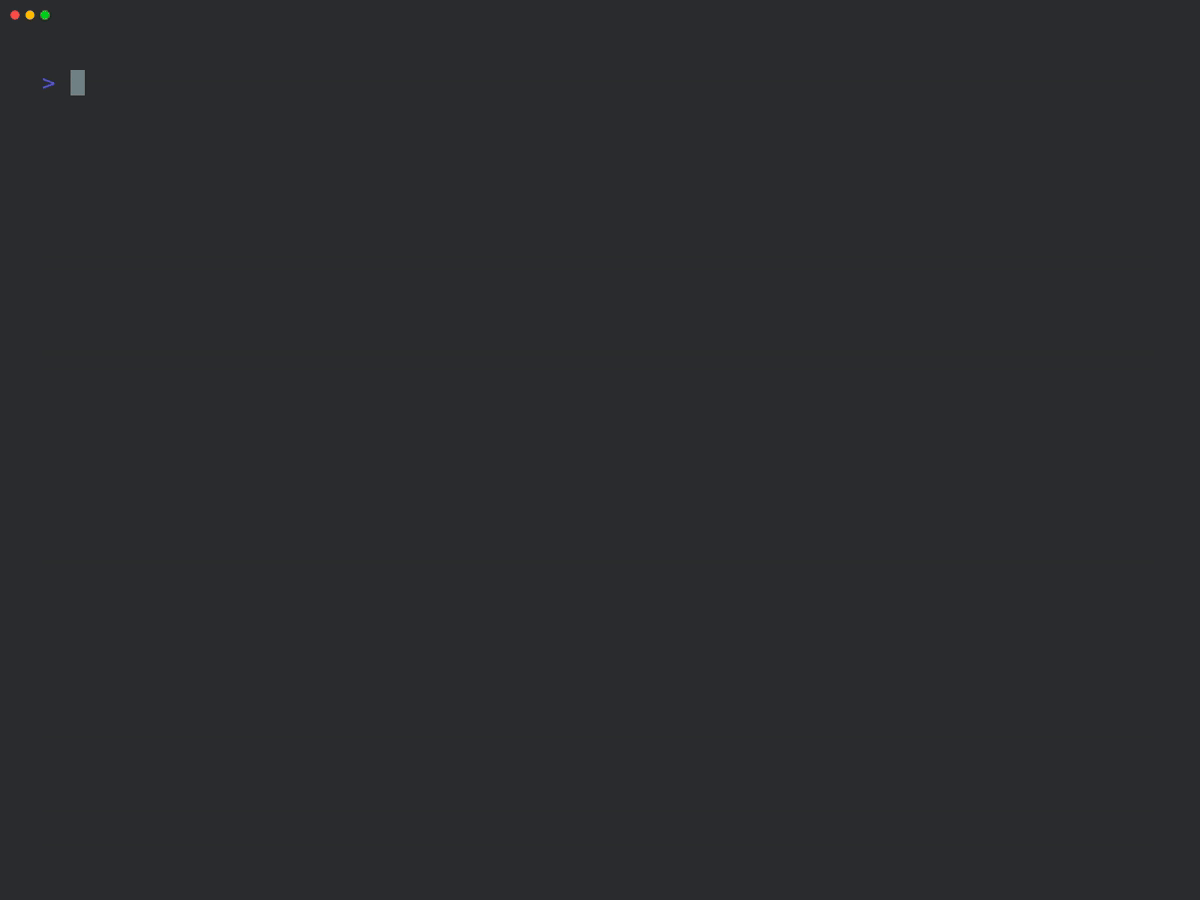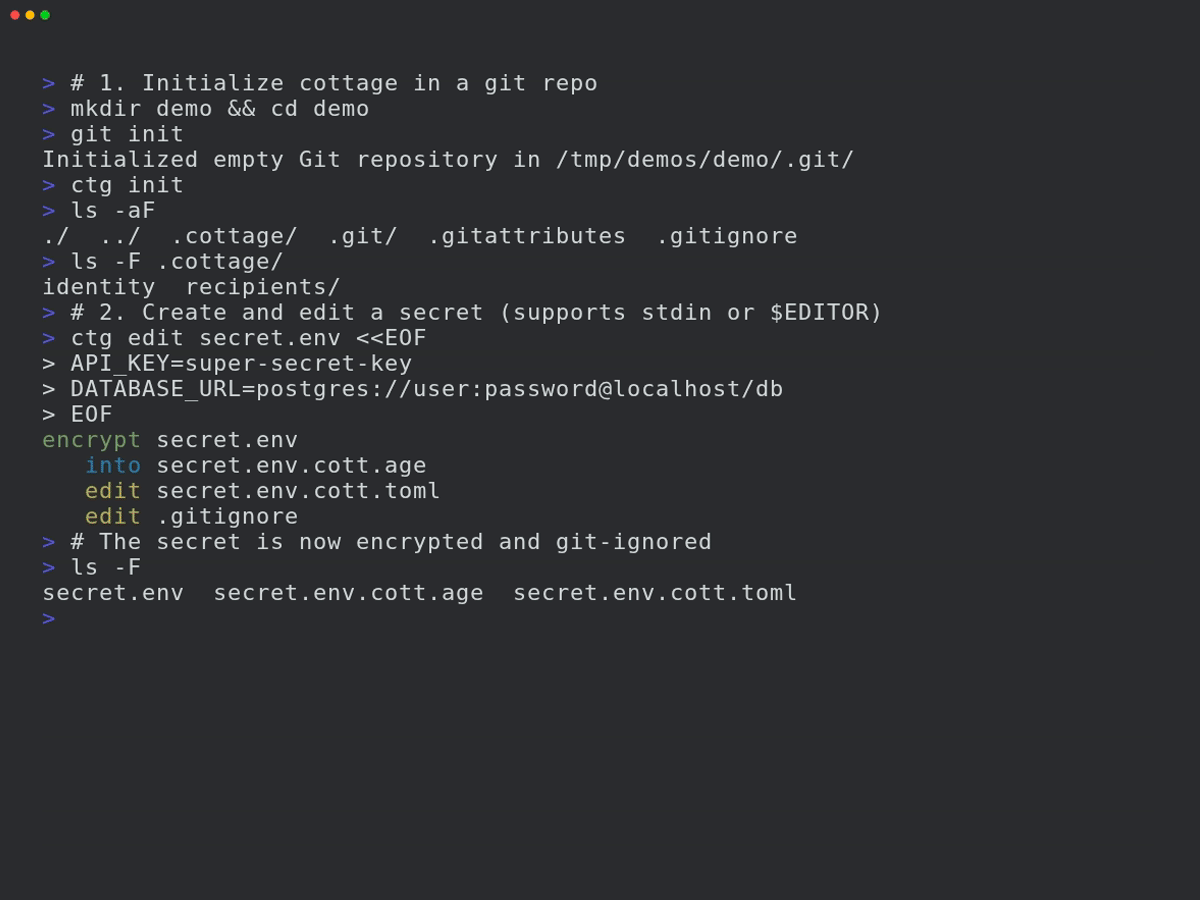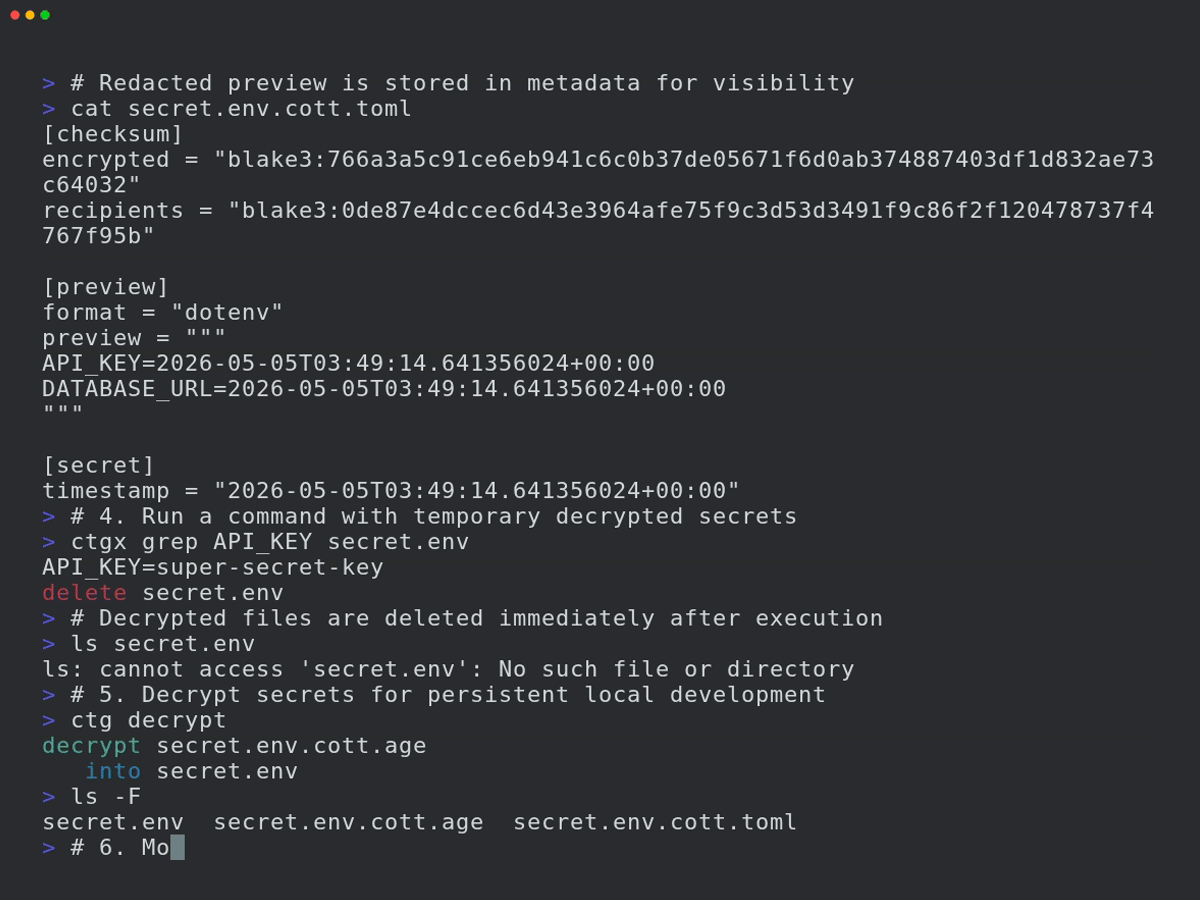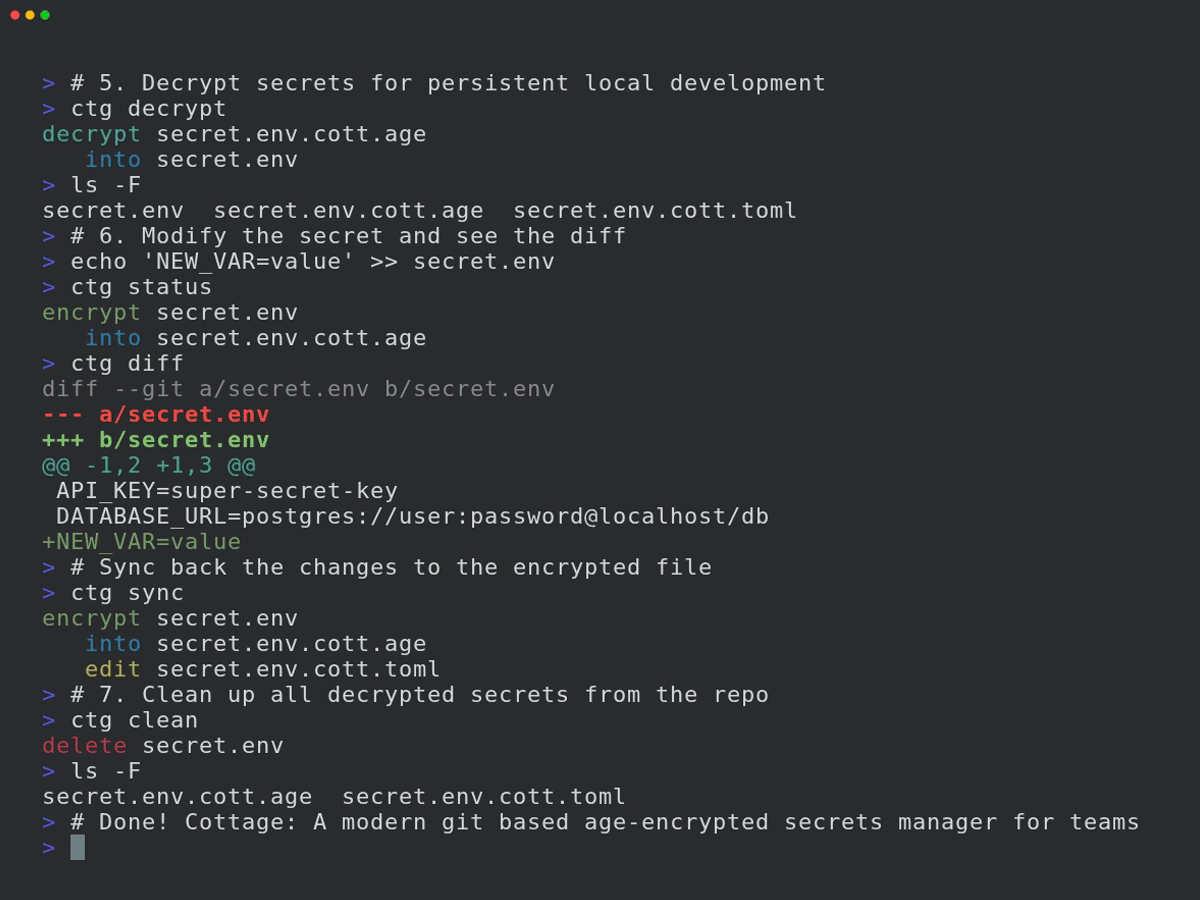
A modern git based age-encrypted secrets manager for teams.

Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…

Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.

A tool for secrets management, encryption as a service, and privileged access management

OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…

Transparent file encryption in git

A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…

CVE-2016-4468