
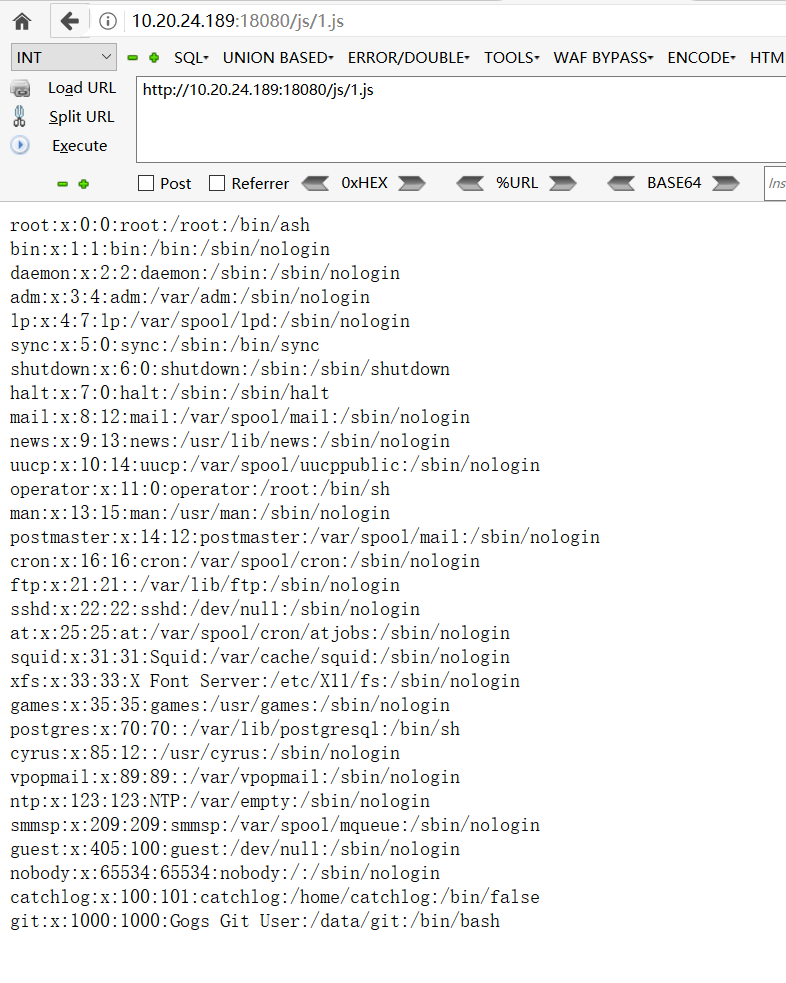
Gogs_RCE
 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
authentication-authorizationexploitationpayload-development+4
16
jas502n/gogs_rceExploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 bogdanrotariu/cve-2026-29204-whmcs-clientarea-addonid
Provides community notes and an optional temporary hook to guard against CVE-2026-29204, a WHMCS client area addonId ownership vulnerability, with…
 bombobombone/cve-2026-102973
Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…