CVE-2022-46169_unauth_remote_code_execution

Unauthenticated Remote Code Execution through authentication bypass and command injection in Cacti < 1.2.23 and < 1.3.0

Unauthenticated Remote Code Execution through authentication bypass and command injection in Cacti < 1.2.23 and < 1.3.0

Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…

PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

Python script for CVE-2024-0012 / CVE-2024-9474 exploit

PoC exploit for FortiWeb CVE-2025-64446 (authentication bypass via path traversal) and CVE-2025-58034 (OS command injection) with detailed analysis…

PoC exploit for FortiWeb CVEs: authentication bypass via path traversal and authenticated OS command injection. Includes detailed analysis, payloads,…

Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…

Catch what's lurking in your Kafka clusters.

Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.

ScriptCase Pre-Authenticated Remote Command Execution exploitation script (CVE-2025-47227, CVE-2025-47228).

Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…

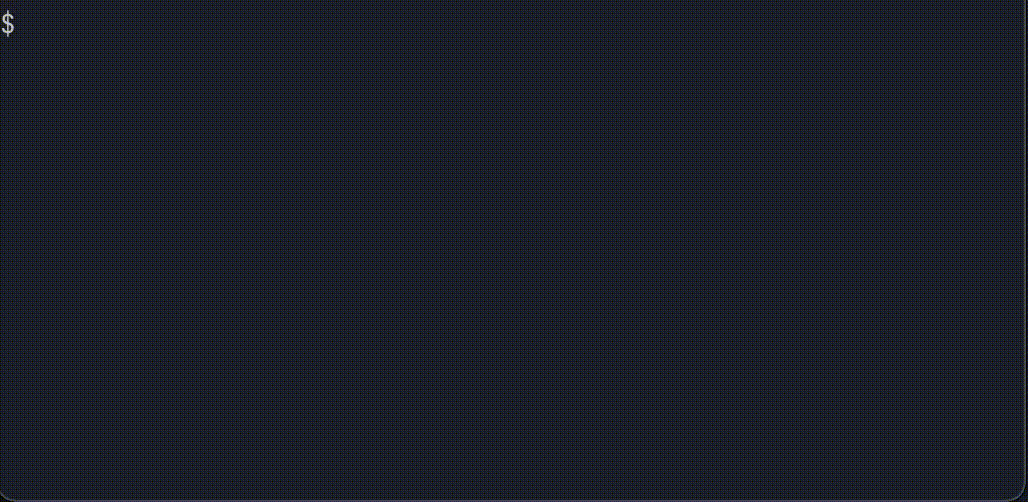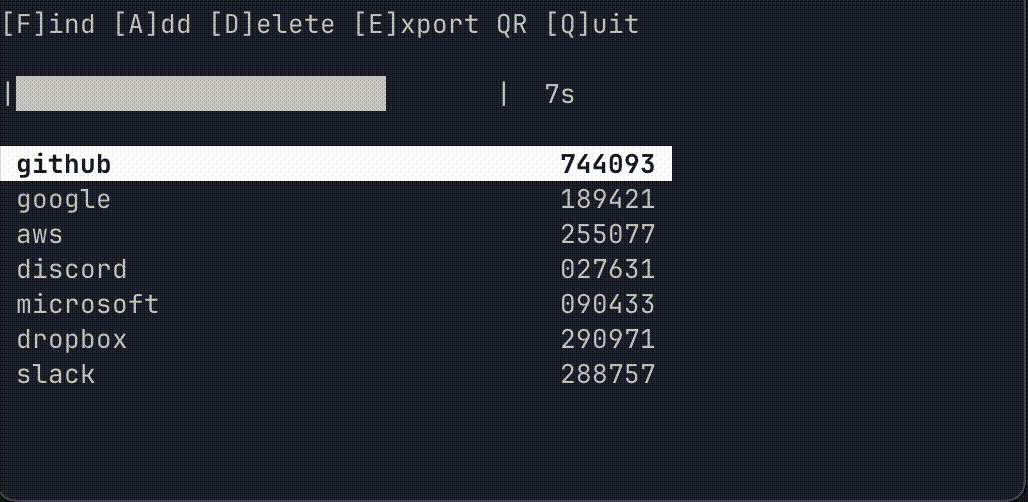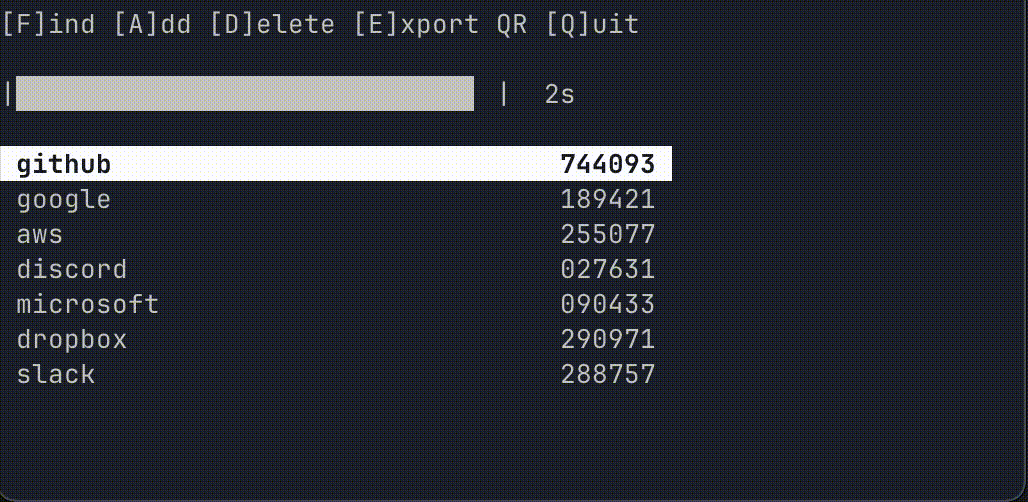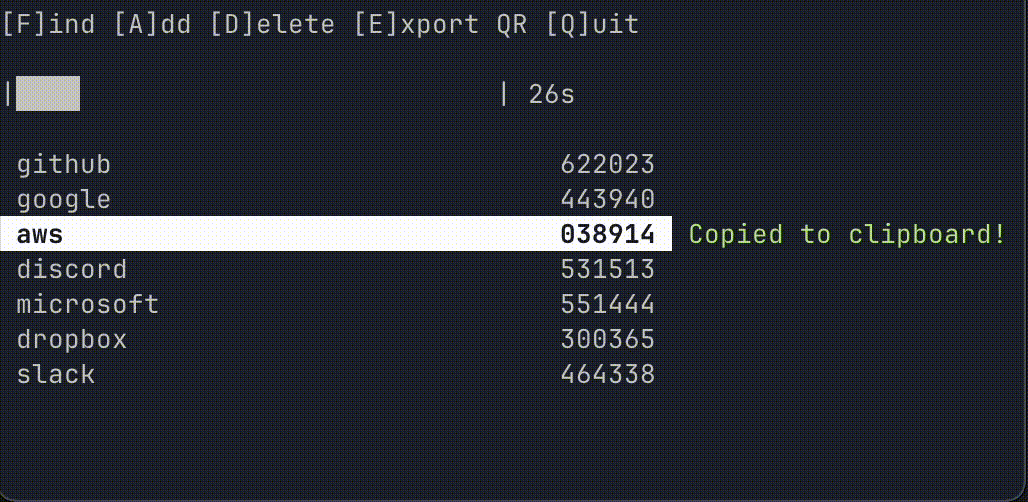
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.

CVE-2018-10933 very simple POC

Proof-of-concept exploit for authentication bypass in ConnectWise ScreenConnect, enabling addition of administrative user as first step to Remote…

Proof-of-concept exploit for CVE-2019-10915 targeting an authentication bypass in Siemens TIA Administrator, enabling remote command execution via…

Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…