
heartwood
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
authentication-authorizationcode-analysisnetwork-security+2
267
radicle-dev/heartwoodPeer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 realalexandergeorgiev/artifactory-cve-2026-82329-poc.py
CVE-2026-82329 — JFrog Artifactory unauthenticated authentication bypass ("phantom join key" -> forged service admin token)
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (🔥 CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
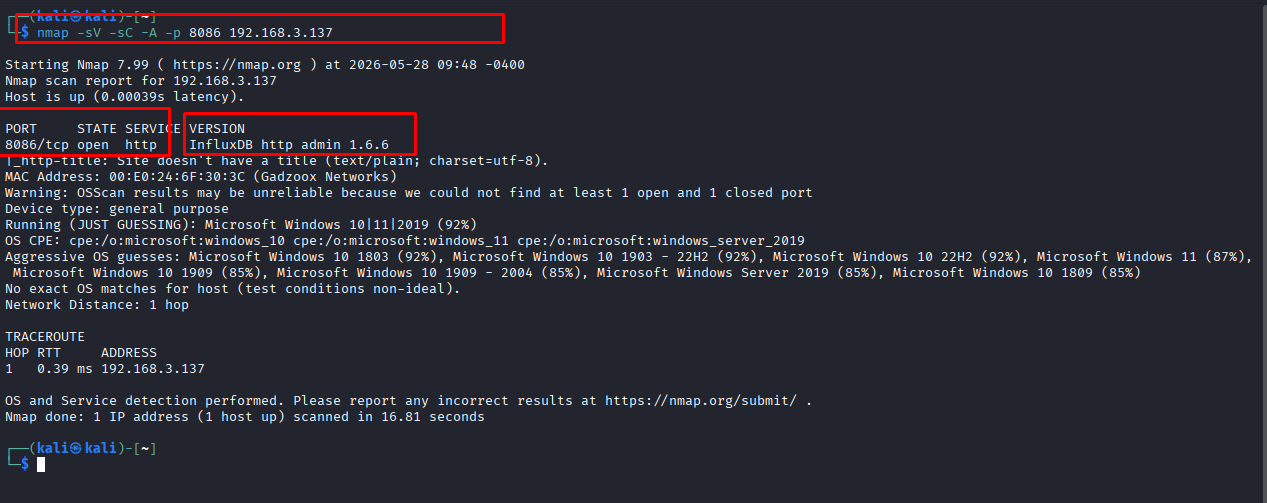 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 manbahadurthapa1248/cve-2026-29000---pac4j-jwt-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt. Forges JWT tokens to gain admin access to protected endpoints.
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
 sdrtba/cve-2025-29927
Proof-of-concept and mass scanning toolkit for CVE-2025-29927, a Next.js middleware authorization bypass via forged x-middleware-subrequest header.…
 absholi7ly/poc-cve-2024-32962-xml-crypto
Simulates an attack exploiting CVE-2024-32962 to forge SAML messages and gain unauthorized permissions, demonstrating the vulnerability's impact.
 mandiant/adfsdump
Dumps AD FS signing keys, token certificates, and relying-party configuration, enabling forged federated authentication tokens for red-team…
 synacktiv/cve-2024-45409
Ruby-SAML / GitLab Authentication Bypass (CVE-2024-45409) exploit
 c0gnit00/cve-2026-29000
Python POC, Exploit for CVE-2026-29000
 maanvader/cve-2023-27524-poc
A POC for the all new CVE-2023-27524 which allows for authentication bypass and gaining access to the admin dashboard.