

cs-token-vault
 henkru/cs-token-vault
In-memory token vault BOF for Cobalt Strike
authentication-authorizationpenetration-testing-frameworkspost-exploitation+2
151
henkru/cs-token-vaultIn-memory token vault BOF for Cobalt Strike
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
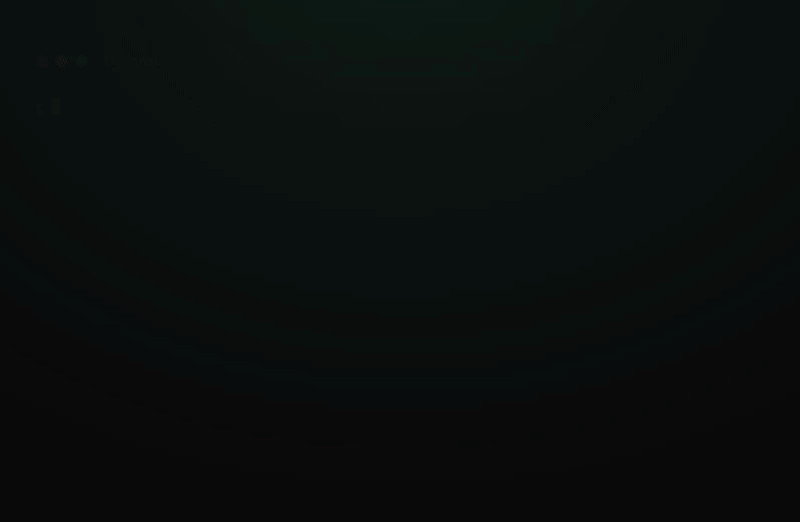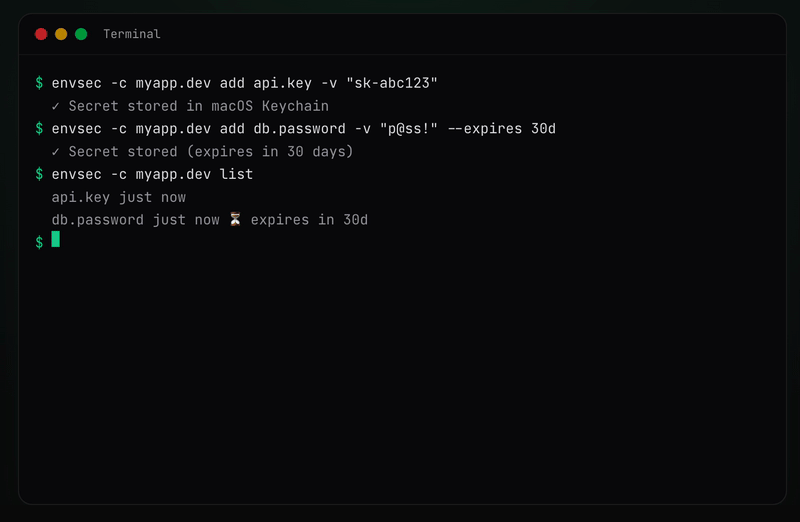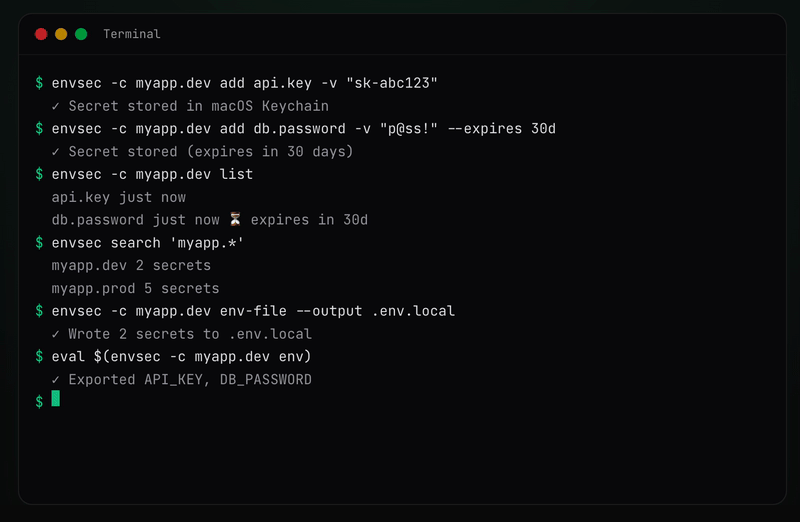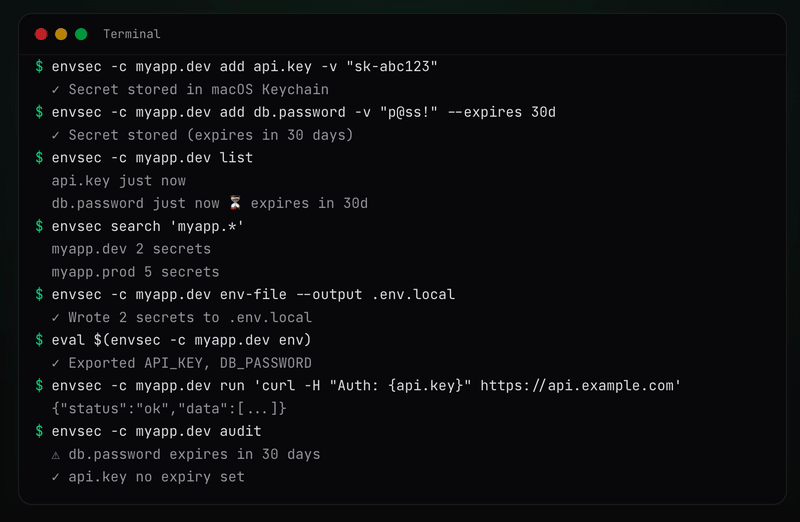 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 vidvansh/cve-2021-41511
Proof-of-concept exploit for SQL injection and authentication bypass in Lodging Reservation Management System 1.0, enabling unauthorized admin access…
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 openvpn/openvpn
Secure tunneling daemon implementing VPN protocols with TLS encryption, certificate authentication, and routing/firewall configuration for private…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
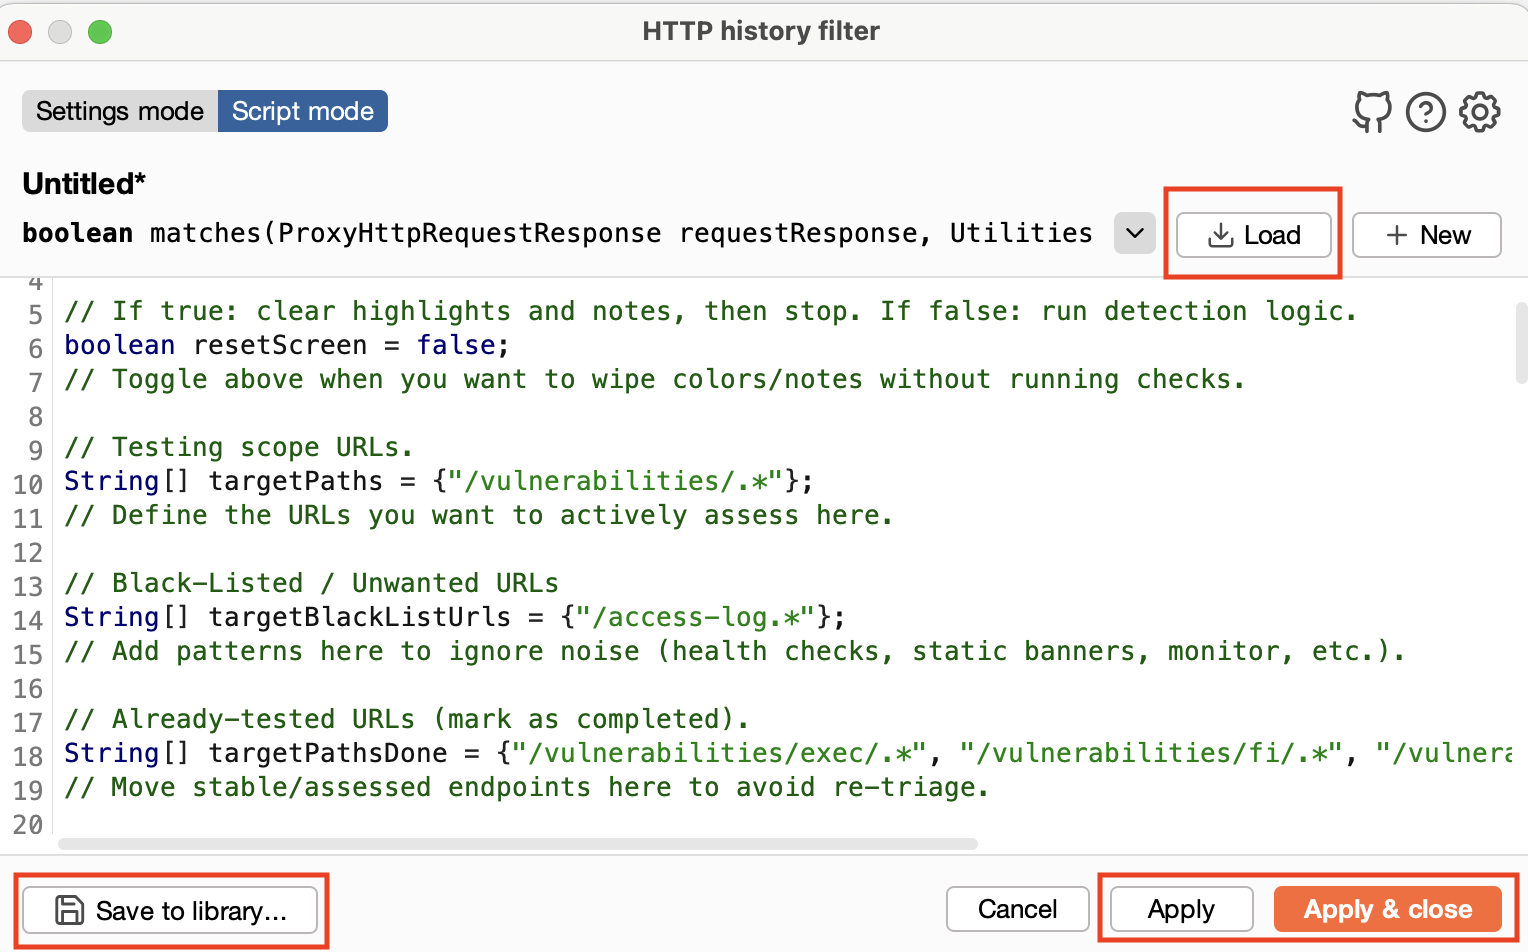 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
 dsccommunity/certificatedsc
DSC resources to simplify administration of certificates on a Windows Server.
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 sourceincite/randy
A pre-authenticated RCE exploit for Inductive Automation Ignition
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…