

hydra
 ory/hydra
OpenID Certified OAuth 2.0 and OpenID Connect provider for token issuance, client management, JWKS, and login/consent flow orchestration via headless…
api-securityauthenticationauthentication-authorization+3
17.6k
ory/hydraOpenID Certified OAuth 2.0 and OpenID Connect provider for token issuance, client management, JWKS, and login/consent flow orchestration via headless…
 juanfont/headscale
An open source, self-hosted implementation of the Tailscale control server
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 freeradius/freeradius-server
High-performance multi-protocol AAA server for RADIUS, DHCPv4/v6, DNS, TACACS+, and VMPS, centralizing network authentication, authorization, and…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…
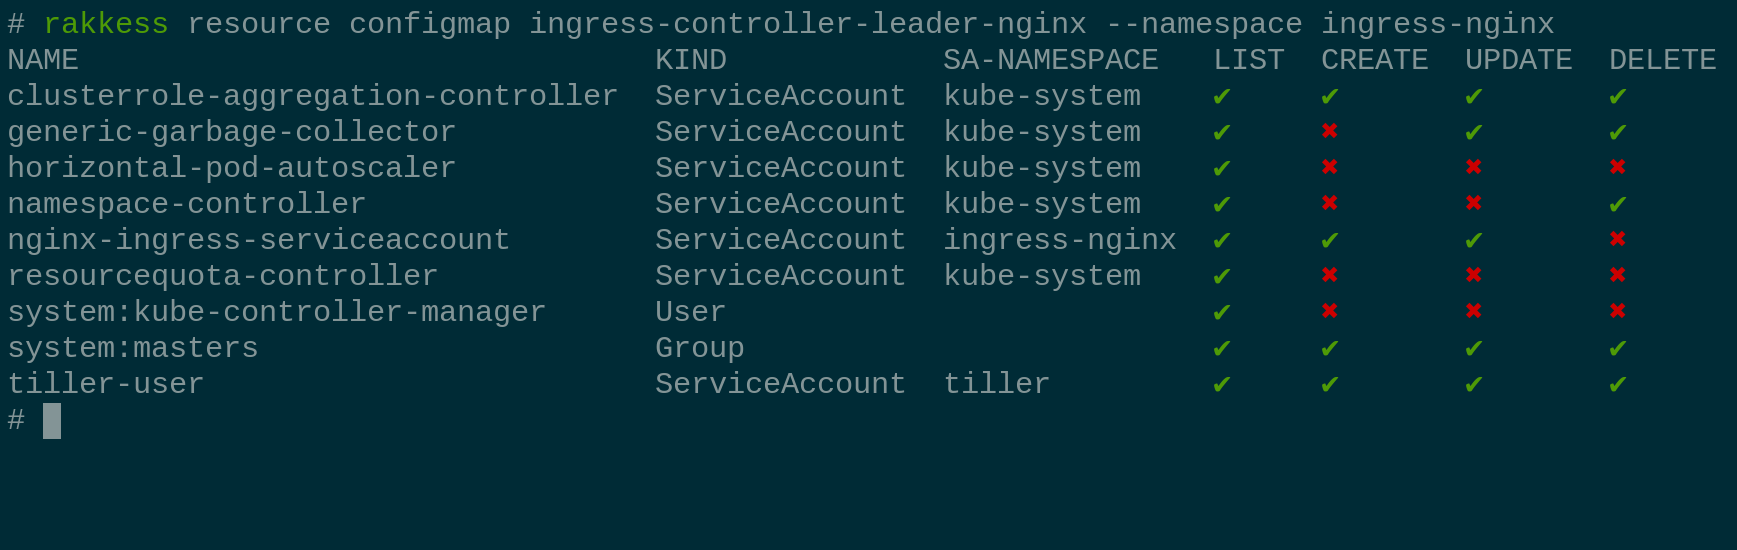 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources
 dsccommunity/certificatedsc
DSC resources to simplify administration of certificates on a Windows Server.
 ory/talos
Scalable API key server for issuing, verifying, and revoking credentials with token derivation for fine-grained capability tokens. Supports…
 7hepr0fess0r/adcsdevilcom
A C# tool for requesting certificates from ADCS using DCOM over SMB. This tool allows you to remotely request X.509 certificates from CA server using…
 ymsniper/noeyes
Secure terminal chat. E2E encrypted, zero-metadata blind-forwarder server. PyNaCl XSalsa20-Poly1305 + Ed25519 + forward secrecy. Cross-platform…
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 sourceincite/cve-2021-24085
Proof-of-concept exploit for CVE-2021-24085: CSRF-based elevation of privilege in Microsoft Exchange Server via msExchEcpCanary token forgery,…
 bhdresh/cve-2021-33766
ProxyToken (CVE-2021-33766) : An Authentication Bypass in Microsoft Exchange Server POC exploit
 yoryio/cve-2024-27198
Exploit for CVE-2024-27198 - TeamCity Server
 stuub/rcity-cve-2024-27198
CVE-2024-27198 & CVE-2024-27199 PoC - RCE, Admin Account Creation, Enum Users, Server Information
 hakivvi/cve-2025-23369
Exploit for CVE-2025-23369: SAML authentication bypass in GitHub Enterprise Server via libxml2 quirks, enabling unauthorized access.