
pared
 renich/pared
Lightweight, secure control plane & real-time web dashboard in Crystal for Linux firewalld and NetworkManager host security.
authentication-authorizationdefensive-toolsidentity-access-management+2
renich/paredLightweight, secure control plane & real-time web dashboard in Crystal for Linux firewalld and NetworkManager host security.
 xrzmodz444/cve-2026-41940-poc-linux
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports custom payloads and verbose logging, compatible with…
 winmin/cve-2021-3560
PolicyKit CVE-2021-3560 Exploitation (Authentication Agent)
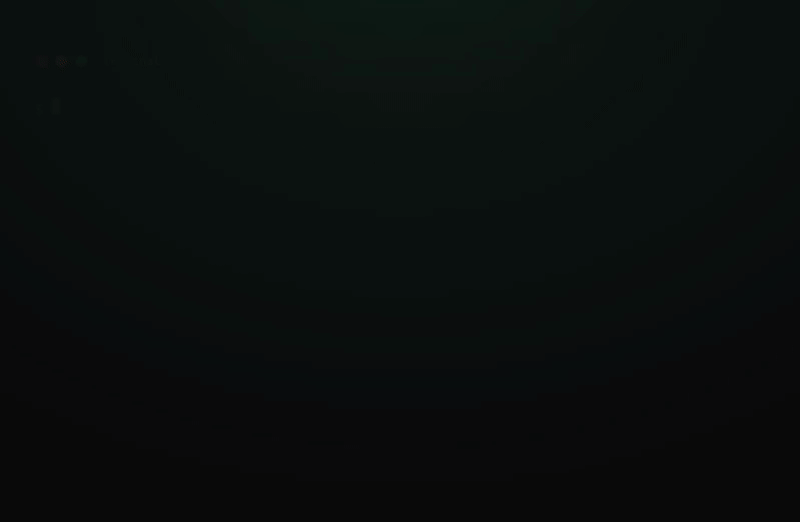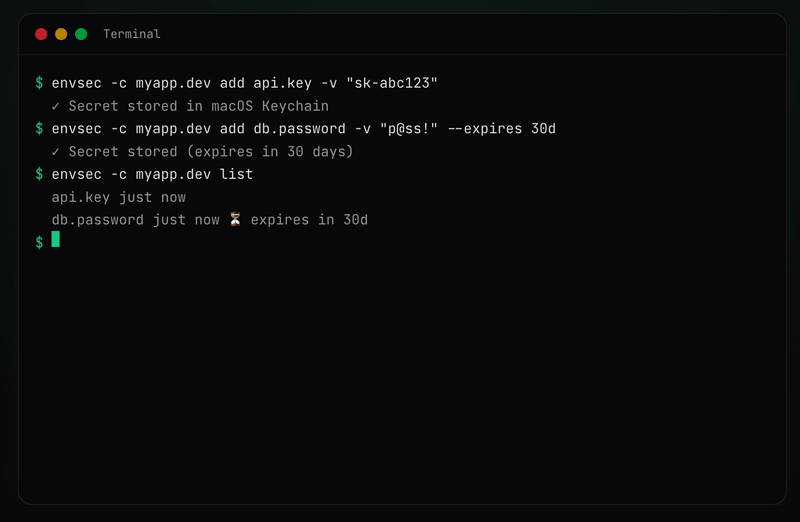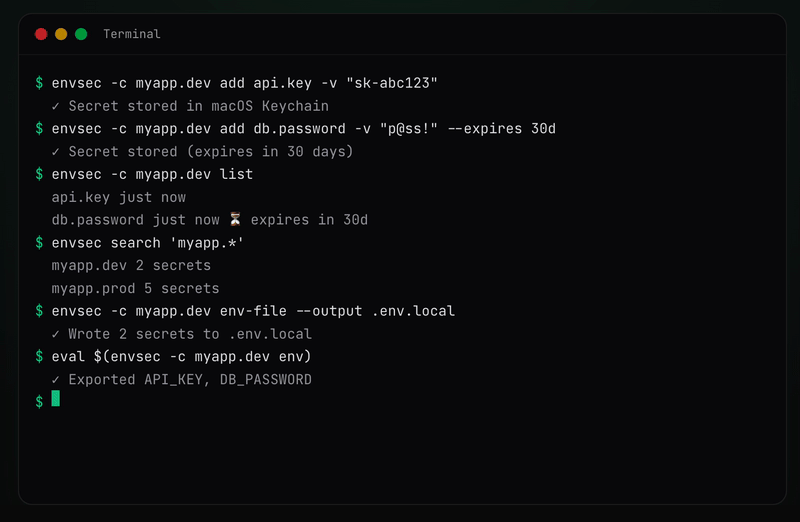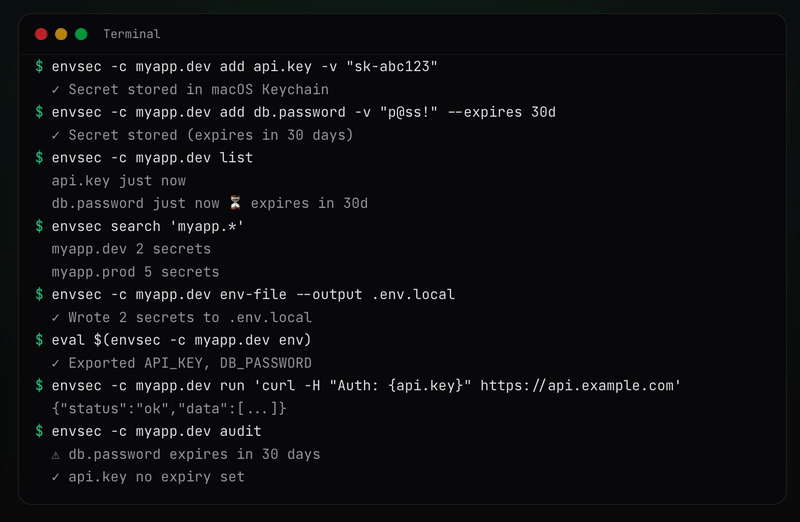 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 okkotsu1/cve-2024-47533
Exploit for CVE-2024-47533, a critical authentication bypass in Cobbler XML-RPC API, granting unauthenticated admin access for educational security…
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 aker-gateway/aker
SSH bastion/jump host/jumpserver
 turtlearm/ksmbrace
ksmbd CVEs: CVE-2026-31717, CVE-2026-68083
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 hakivvi/cve-2021-3560
C exploit for CVE-2021-3560, an authentication bypass in polkit enabling unprivileged users to create a privileged account via DBus, with a detailed…
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 aancw/polkit-auto-exploit
Automatic Explotation PoC for Polkit CVE-2021-3560