
CVE-2019-17662
 muirlandoracle/cve-2019-17662
Exploit code for CVE-2019-17662
authentication-authorizationexploitationpenetration-testing+2
19
muirlandoracle/cve-2019-17662Exploit code for CVE-2019-17662
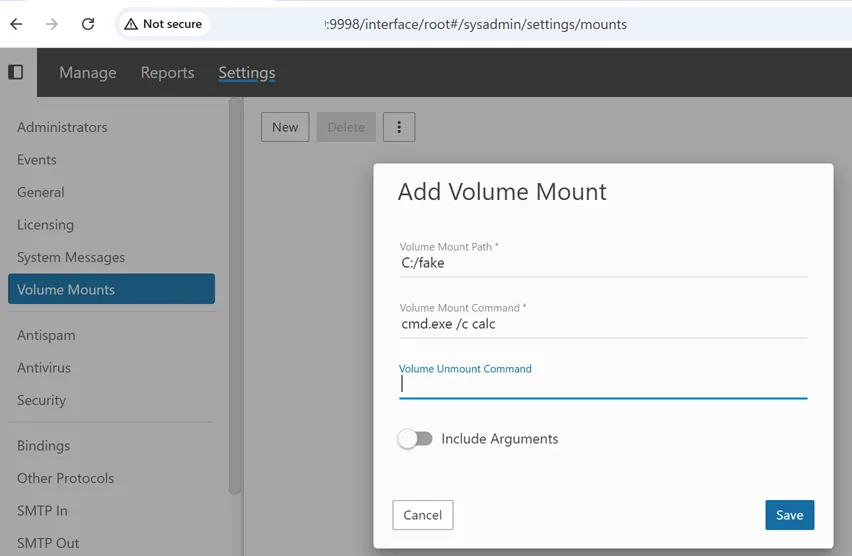 maxmnml/smartermail-cve-2026-23760-poc
CVE-2026-23760 - An authentication bypass via password reset API in SmarterMail.
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
 oscerd/cve-2026-23552
CVE-2026-23552 - Cross-Realm Token Acceptance in camel-keycloak
 bidaoui4905/cve-2018-10933
LibSSH authentification bypass
 hypnguyen1209/cve-2026-63520
Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…
 a17-ba/cve-2026-51119
Technical analysis and advisory for CVE-2026-51119, a privilege escalation in Invixium IXM WEB allowing authenticated low-privilege users to create…
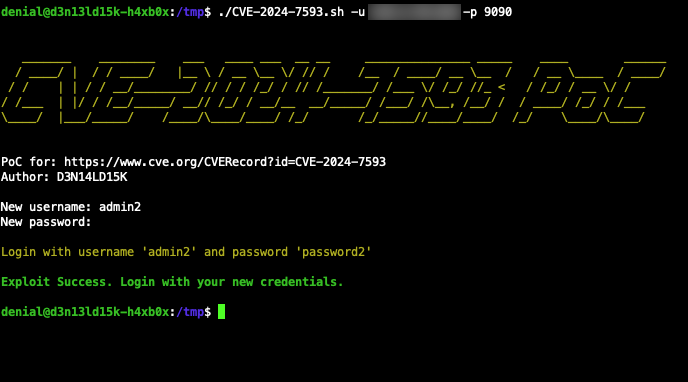 d3n14ld15k/cve-2024-7593_poc_exploit
CVE-2024-7593 Ivanti Virtual Traffic Manager 22.2R1 / 22.7R2 Admin Panel Authentication Bypass PoC [EXPLOIT]
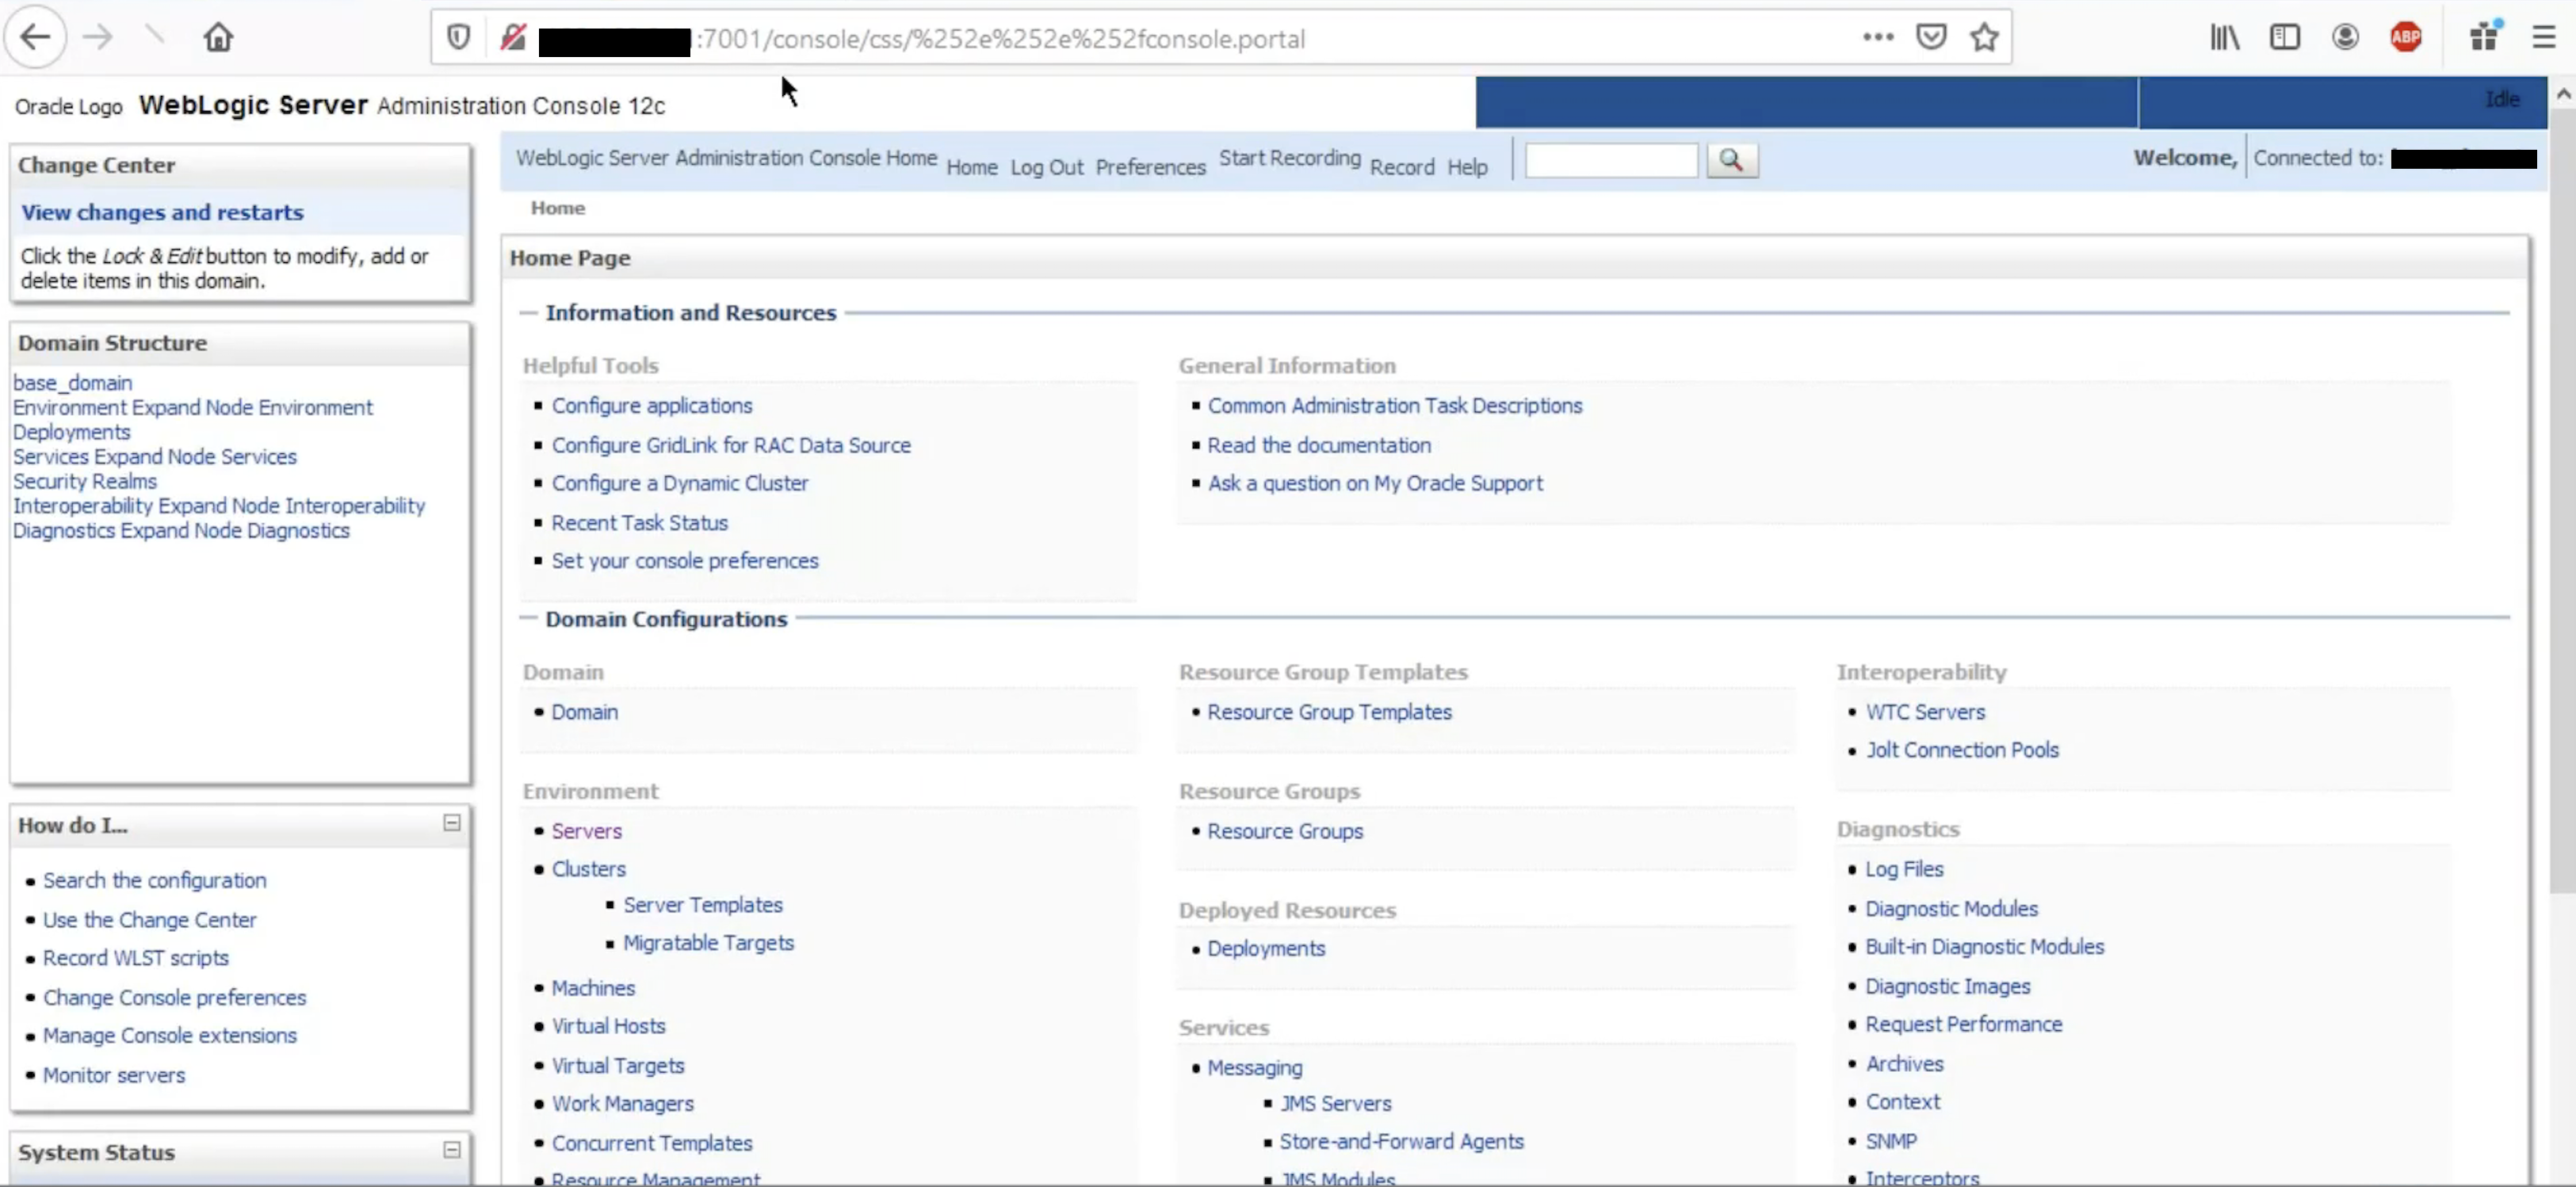 murataydemir/cve-2020-14882
[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
 5amu/cve-2021-29156
Exploit for CVE-2021-29156
 trqt/cve-2024-48322
Exploit for CVE-2024-48322 targeting RunCodes instances. Retrieves user passwords via email inbox after authentication bypass, requiring only any…
 shoucheng3/kubernetes-client__java_cve-2020-8570_client-java-parent-9_0_2_fixed
Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 john-jung/cve-2026-25604-poc
A PoC for demonstrating CVE-2026-25604
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…