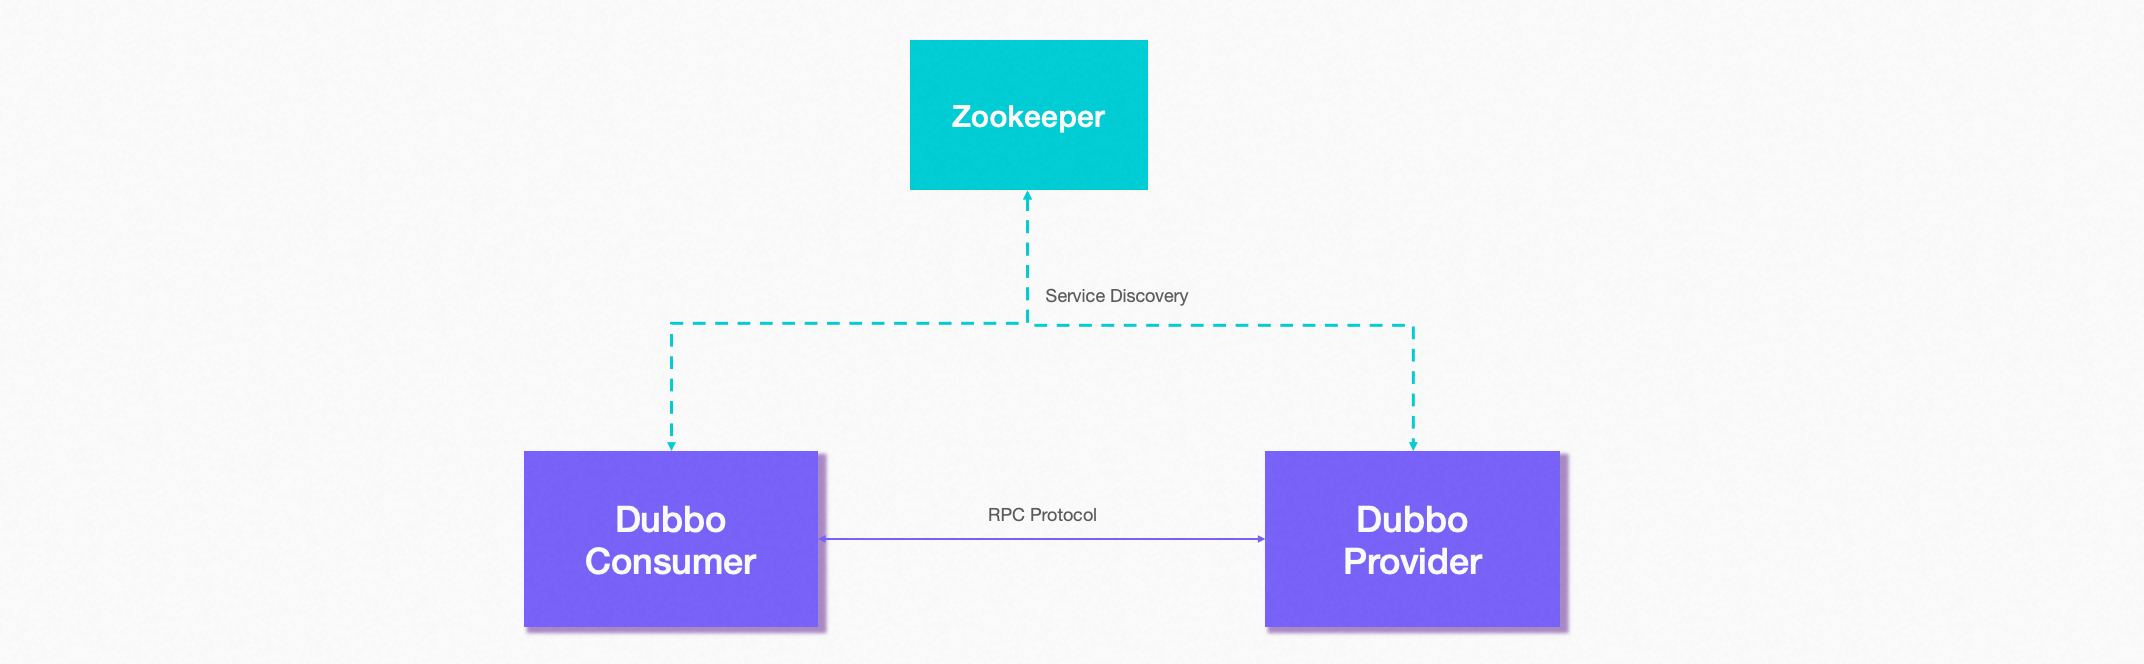
apache__incubator-dubbo_CVE-2021-30181_2-6-8

High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…

High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…

This is a simple Shiro-basic project .Just for pentest env

Macally WIFISD2

Robust toolkit implementing TLS/SSL protocols and a full-strength cryptographic library for encryption, decryption, certificate creation, and secure…

Exploit for CVE-2023-46747, a critical authentication bypass vulnerability in F5 BIG-IP, enabling unauthenticated remote code execution.

Proof-of-concept exploit for CVE-2017-8295, demonstrating unauthorized password reset in WordPress 4.7.4 by intercepting the reset link without prior…

SureTriggers <= 1.0.78 - Authorization Bypass Exploit

Exploit for CVE-2025-27580: A predictable token vulnerability in NIH BRICS through 14.0.0-67 allows unauthenticated users with a Common Access Card…

Open source identity and access management platform providing single sign-on, user federation, and centralized authentication for modern applications…

Open source identity and access management solution providing single sign-on, user federation, and centralized authentication for modern applications…

Open source identity and access management solution providing single sign-on, user federation, and centralized authentication for modern applications…

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…

This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)

Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Demonstrates CVE-2022-31692 Spring Security authorization bypass with a minimal Java exploit, enabling security researchers to test and understand…

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…