
in-toto
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
authentication-authorizationcryptographydefensive-tools+2
1.1k
in-toto/in-totoProtects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 cyberark/conjur
CyberArk Conjur automatically secures secrets used by privileged users and machine identities
 corneliusweig/rakkess
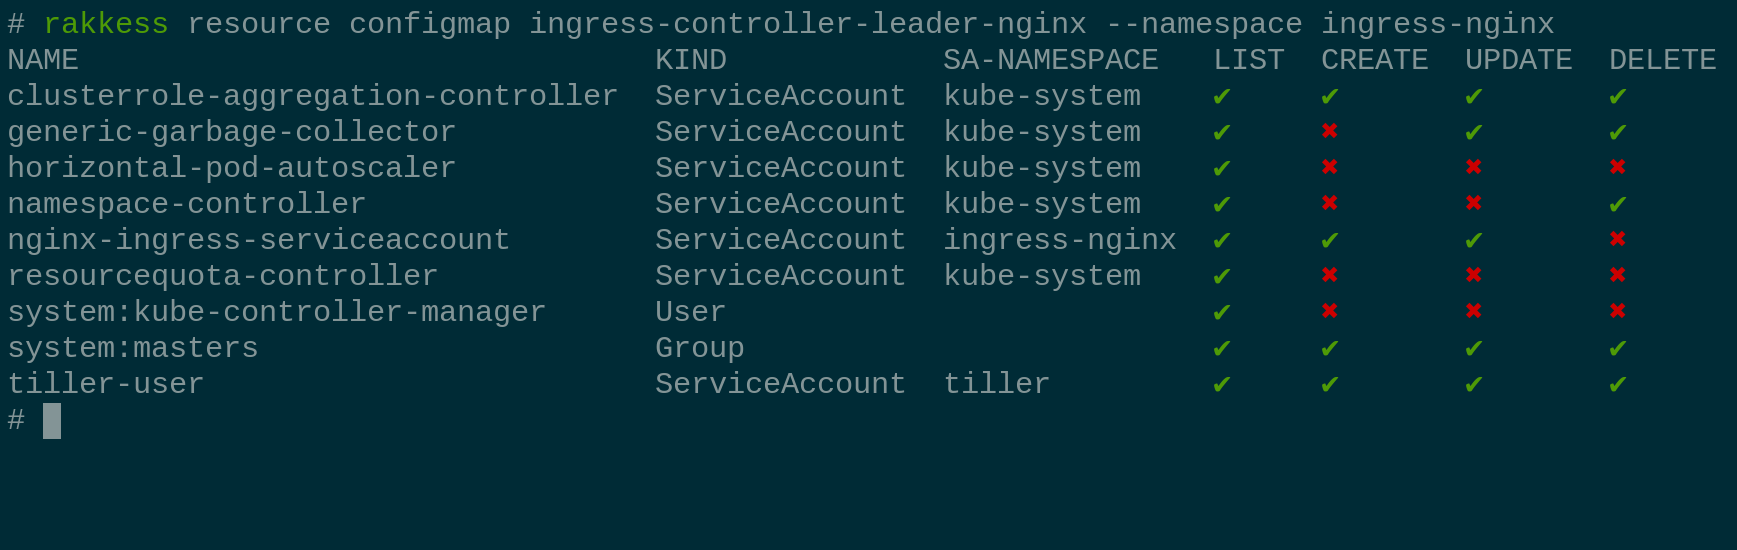
Review Access - kubectl plugin to show an access matrix for k8s server resources
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 synacktiv/cve-2024-45409
Ruby-SAML / GitLab Authentication Bypass (CVE-2024-45409) exploit
 agberohq/keeper
Simple Secure Keeper for Secrets
 l0ading-x/cve-2022-23131
cve-2022-23131
 qarait/ephemera
Zero-Trust SSH CA
 chocapikk/cve-2026-24061
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) with Docker lab setup and Go PoC. Exploits NEW-ENVIRON…
 nxploited/cve-2025-3102
Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation
 ignis-sec/cve-2019-10008
ManageEngine Service Desk Plus 10.0 Privilaged account Hijacking
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
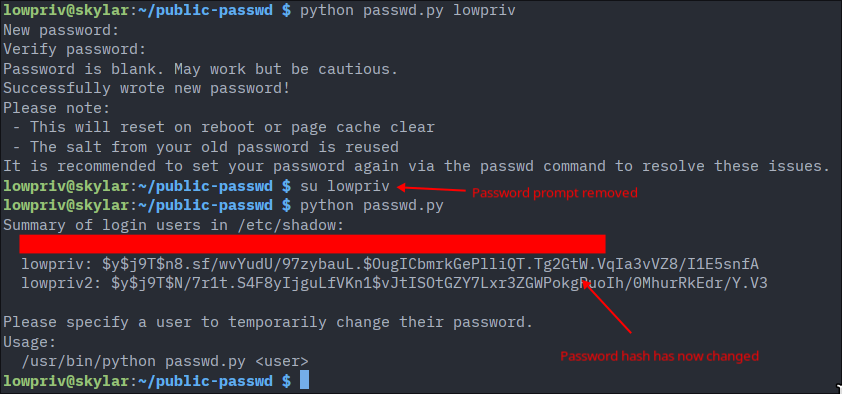 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
 razureink/cve-2024-0012_9474-panos_authbypass_reproduction
CVE Reproduction: cve-2024-0012_9474-panos_authbypass_reproduction