

CVE-2023-43154-PoC
 ally-petitt/cve-2023-43154-poc
PoC for the type confusion vulnerability in Mac's CMS that results in authentication bypass and administrator account takeover.
authentication-authorizationexploitationpassword-attacks+3
ally-petitt/cve-2023-43154-pocPoC for the type confusion vulnerability in Mac's CMS that results in authentication bypass and administrator account takeover.
 geraldoalcantara/cve-2023-49547
Customer Support System 1.0 - SQL Injection Login Bypass
 vulnz/cve-2021-40903
CVE-2021-40903
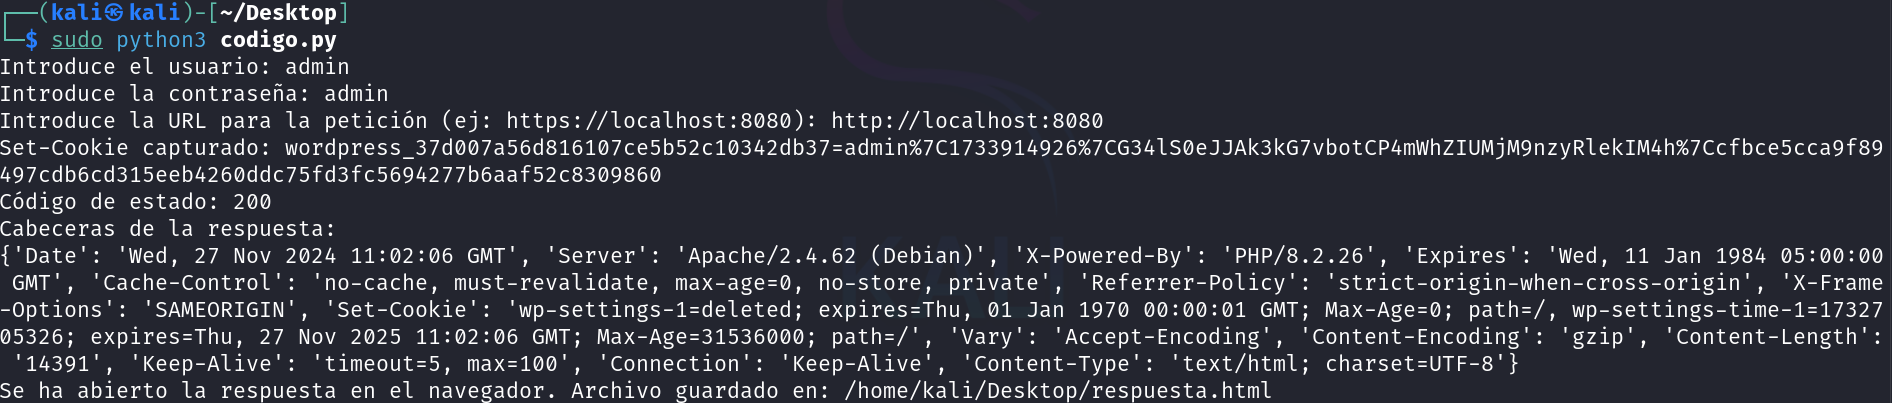 hunt3r850/cve-2024-10924-poc
Proof-of-concept exploit for CVE-2024-10924, an authentication bypass vulnerability in the Really Simple Security WordPress plugin, enabling MFA…
 underprotection/cve-2020-24030
Proof-of-concept for CVE-2020-24030: weak token expiration in ForLogic Qualiex v1/v3 enabling remote unauthenticated privilege escalation and…
 c411e/cve-2023-47564
CVE-2023-47564
 asg-castle/cve-2023-27350
Proof-of-concept exploit for CVE-2023-27350 in PaperCut NG; exploits SetupCompleted access-control flaw to bypass authentication and execute code as…
 rampantspark/cve-2024-27198
A PoC for CVE-2024-27198 written in Go
 shoucheng3/asf__cxf_cve-2016-6812_3-0-11
Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 amjadali-110/cve-2023-43317
Vertical Privilege Escalation via Session Storage by Amjad Ali (CVE-2023-43317)
 pinpinsec/cve-2021-44270
CVE-2021-44270
 rxrcoder/cve-2023-2437
Exploit tool for CVE-2023-2437 targeting UserPro <= 5.1.1 authentication bypass, allowing attackers to gain admin access and create new…
 randomrobbiebf/cve-2024-54378
Quietly Insights <= 1.2.2 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Options Update
 randomrobbiebf/cve-2024-50488
Token Login <= 1.0.3 - Authenticated (Subscriber+) Privilege Escalation
 randomrobbiebf/cve-2024-9890
User Toolkit <= 1.2.3 - Authenticated (Subscriber+) Authentication Bypass
 randomrobbiebf/cve-2024-50477
Stacks Mobile App Builder <= 5.2.3 - Authentication Bypass via Account Takeover
 ubaydev/cve-2025-2594
User Registration & Membership <= 4.1.2 - Authentication Bypass